
A branch has BFD up to every ordinary site and BFD down only to the cloud gateway. Control connections are up. The firewall permits the other sites and blocks the gateway's public address. What is blocked?
Select an answer to reveal the explanation.
Short Explanation
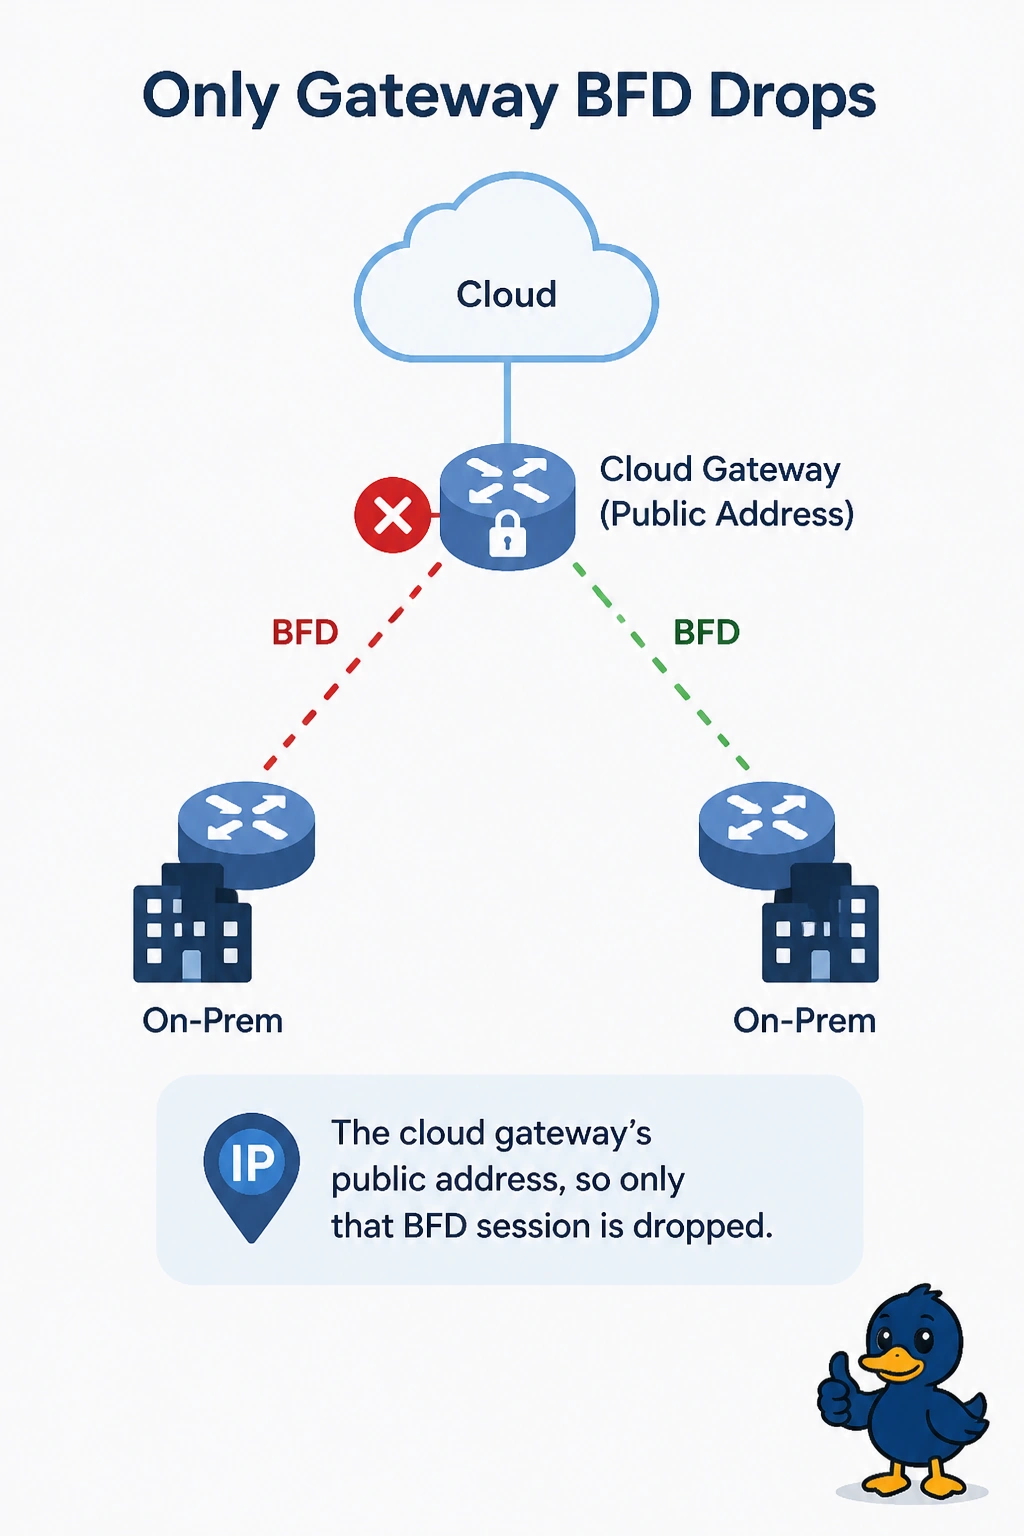
Every other site answers, and one address on the firewall does not. You permit the cloud gateway's public address. The controllers are already up, so the certificate is not what singled out this gateway.
Full Explanation
BFD to a cloud gateway is ordinary underlay traffic to that gateway's public address. This firewall allows the other sites and blocks only that address, which matches BFD up everywhere else and down to the gateway. Control connections are up, so the controller path and the certificate are working. A certificate failure would not leave ordinary BFD up while targeting one gateway address. OMP is not down. Control being up is the opposite of an OMP transport failure, and the selective BFD loss is explained by the address filter. VPN 512 does not have to be up for cloud-gateway BFD. That BFD uses the transport VPN. Exam caveat: permitting the address is not the same as permitting the UDP ports BFD needs. If the address is allowed and the port is still denied, open the port too. Operational check: after the gateway address is permitted, show sdwan bfd sessions should list that gateway up, with the other sites unchanged.