
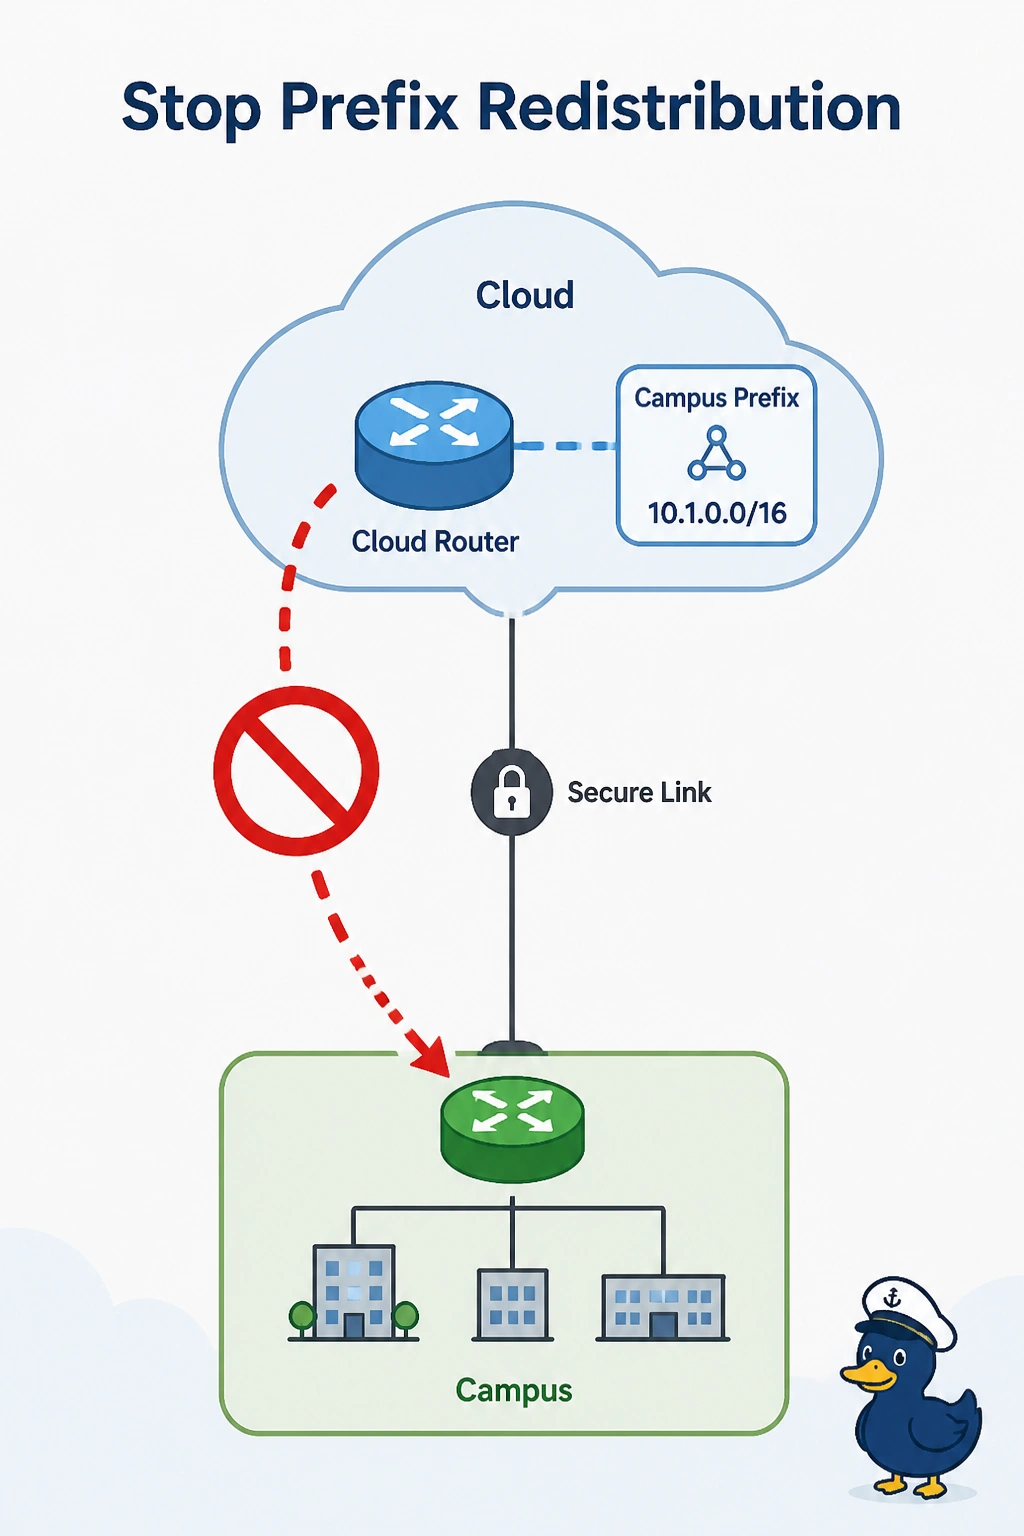
Campus and cloud IOS XE routers have a Full OSPF adjacency. The campus then prefers a path for its own prefix that points back at the cloud router. The cloud router is redistributing that prefix with no filter. What should be stopped?
Select an answer to reveal the explanation.
Short Explanation
The cloud router learned your prefix and offered it back as a better way home. You stop it from redistributing that campus prefix toward the campus. A Full adjacency only means OSPF is working, which is not a reason to keep the loop.
Full Explanation
A cloud IOS XE router that redistributes a learned campus prefix back toward the campus can become the campus router's best path for its own network. Traffic then walks to the cloud router and is sent toward the campus again. Filter that prefix, or tag it and deny the tag, on the way back out. The Full adjacency is healthy and is not something to tear down to hide the loop. IKE is up enough for OSPF to be Full. A duplicated pre-shared key is not what created the route. The virtual private gateway is not the OSPF peer in this design. The cloud IOS XE router is the one advertising the prefix back. Exam caveat: keep advertising the VPC prefixes the campus does not already own. The filter should match the campus prefix, not the whole OSPF table. Operational check: show ip route on the campus router for its own prefix should point at a local interface again, not at the cloud router.