
A campus IOS XE router aims its tunnel destination at an address inside the VPC. IKE never reaches AWS. The VPN connection page shows a different outside public address. What should the destination be?
Select an answer to reveal the explanation.
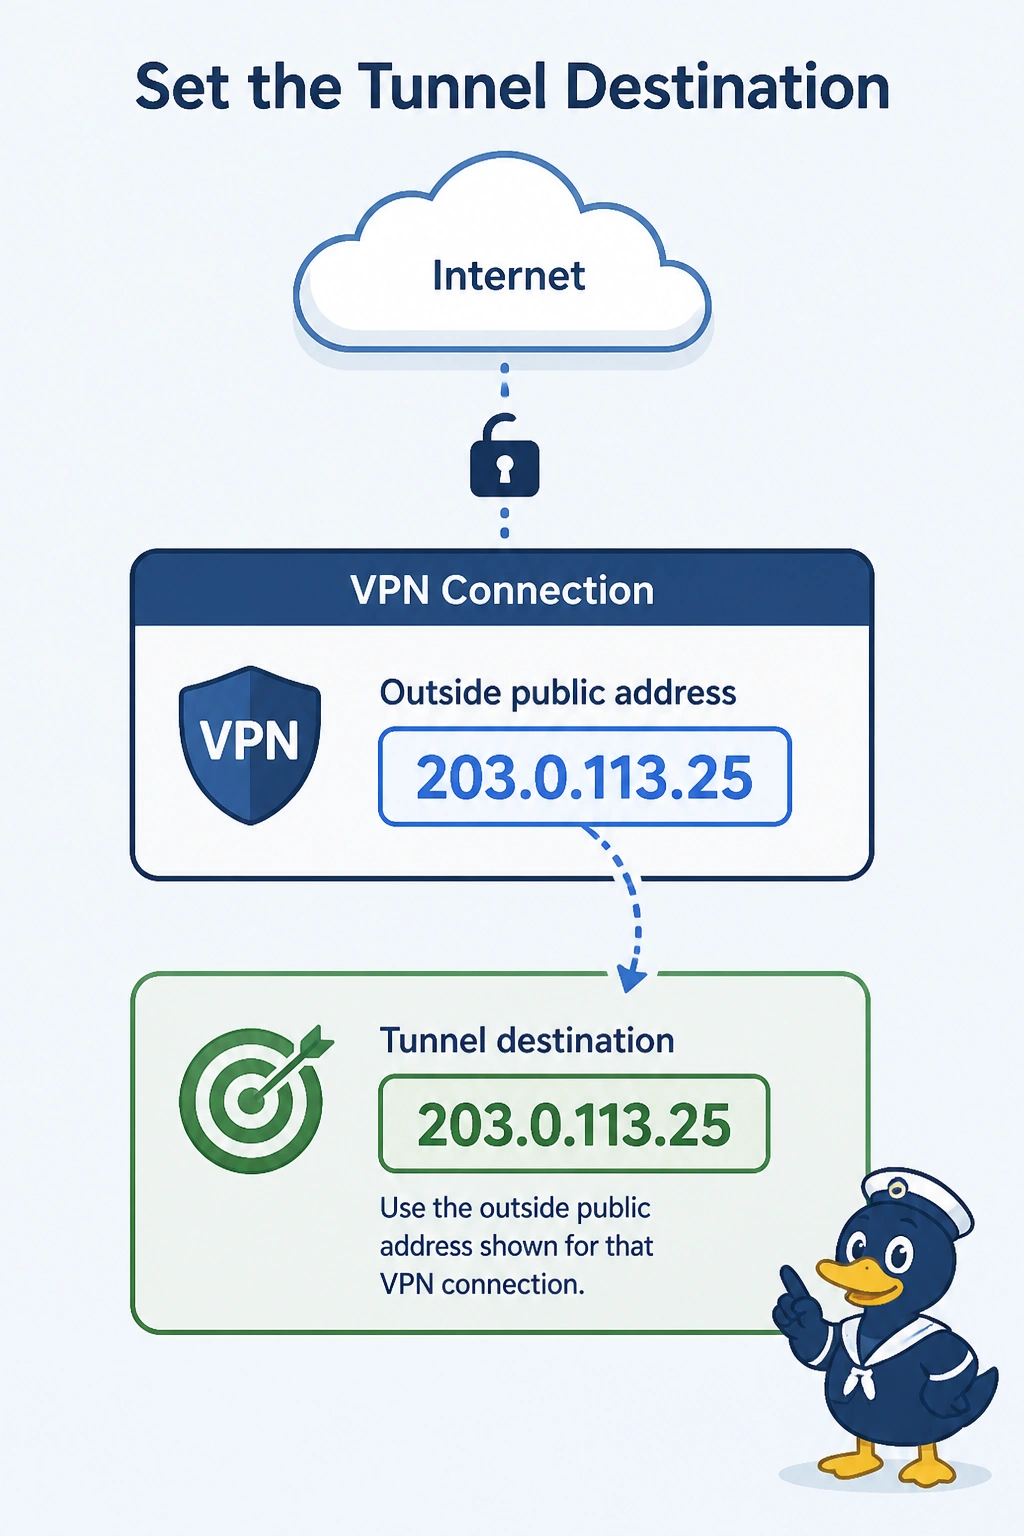
Short Explanation
You are knocking on a door that is not on the public street. You set the tunnel destination to the outside public address from the VPN connection. The address inside the VPC is not the IKE peer, and the router cannot finish IKE by aiming at itself.
Full Explanation
AWS Site-to-Site VPN expects IKE at the outside public address of the connection. This router is aimed at an address inside the VPC, which is not reachable as the IKE peer on the internet, so the exchange never arrives. Change the destination to the outside address the connection page shows. The VPC DNS resolver is not the IKE peer. The tunnel's own inside address makes the router try to build IKE to itself. An Azure gateway address is a different cloud and is not an alternate AWS peer. Exam caveat: each tunnel on the connection has its own outside address. Point tunnel 1 at the first outside address and tunnel 2 at the second, not both at one of them. Operational check: the tunnel destination should match the outside address, and a capture on the internet interface should show IKE toward that address.