
A clinic retired a campus prefix and is using a new one. AWS still sends return traffic toward the old prefix. BGP is not in use. The VPN connection still has a static route for the old prefix. What should be edited?
Select an answer to reveal the explanation.
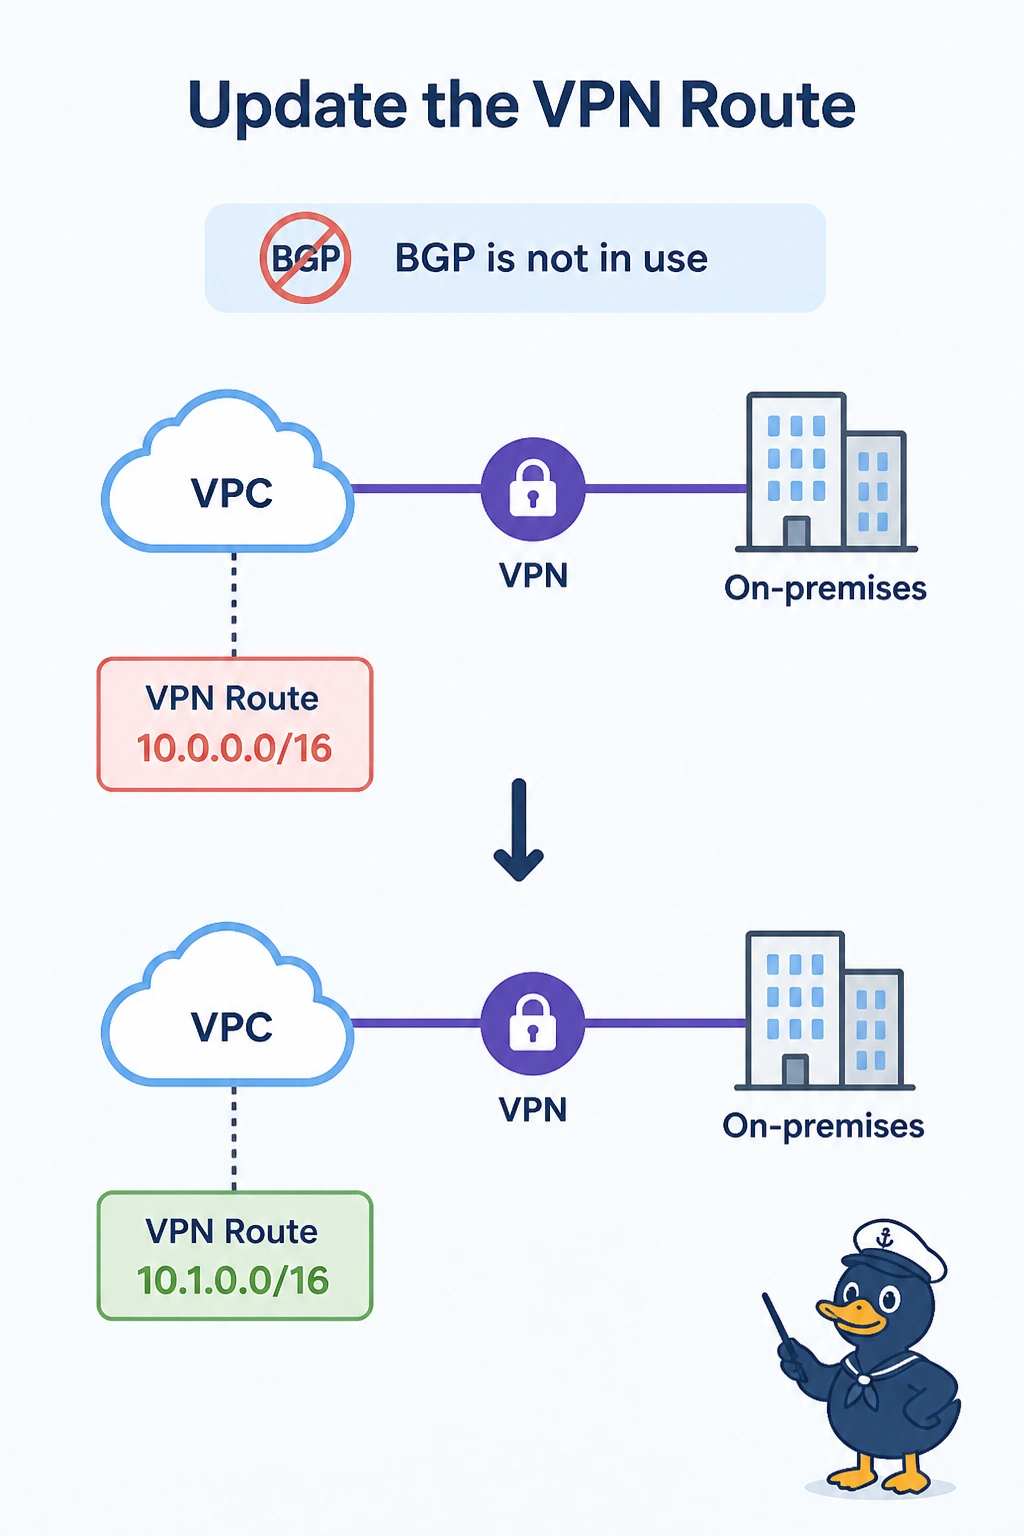
Short Explanation
AWS is still following the route note you left on the VPN connection. You can replace the old prefix with the new one in that static route; with no BGP session, nothing will withdraw the old route for you. The IKE identity affects authentication, not which prefix AWS routes.
Full Explanation
Without BGP, AWS learns campus prefixes from the static routes configured on the VPN connection. The clinic has retired its old prefix but left that static route in place, so AWS continues sending return traffic toward a range the clinic no longer uses. Edit the static route on the VPN connection, replacing the old prefix with the new one. An OSPF cost on the virtual private gateway is not the fix: the gateway does not run OSPF or own this static route as an OSPF cost. The IKE identity is used for authentication, not for selecting which campus prefix AWS installs. The anti-replay window helps reject reordered packets on a security association; it does not keep a withdrawn routing prefix installed. Exam caveat: remove the old route rather than merely adding the new one. If both routes remain, hosts still sourcing traffic from the old range may retain a path the clinic intended to retire. Practical check: confirm the VPN connection’s static routes list the new prefix and no longer list the old one, then verify that a VPC instance can reach a host in the new range.