
A regional retailer has 40 WAN Edge routers with enterprise CA certificates, and overnight three stores lost OMP routes while DTLS to the SD-WAN Controller stays down after a certificate renewal window. Valid serials still appear in SD-WAN Manager but one device shows an expired validity date. Which certificate lifecycle condition should the engineer validate first to explain the failed control connections?
Select an answer to reveal the explanation.
Short Explanation
You nailed the tricky part — dates matter more than allowlists here. A stale validity window is like an expired passport that blocks boarding despite a valid ticket, so focus on validity first.
Full Explanation
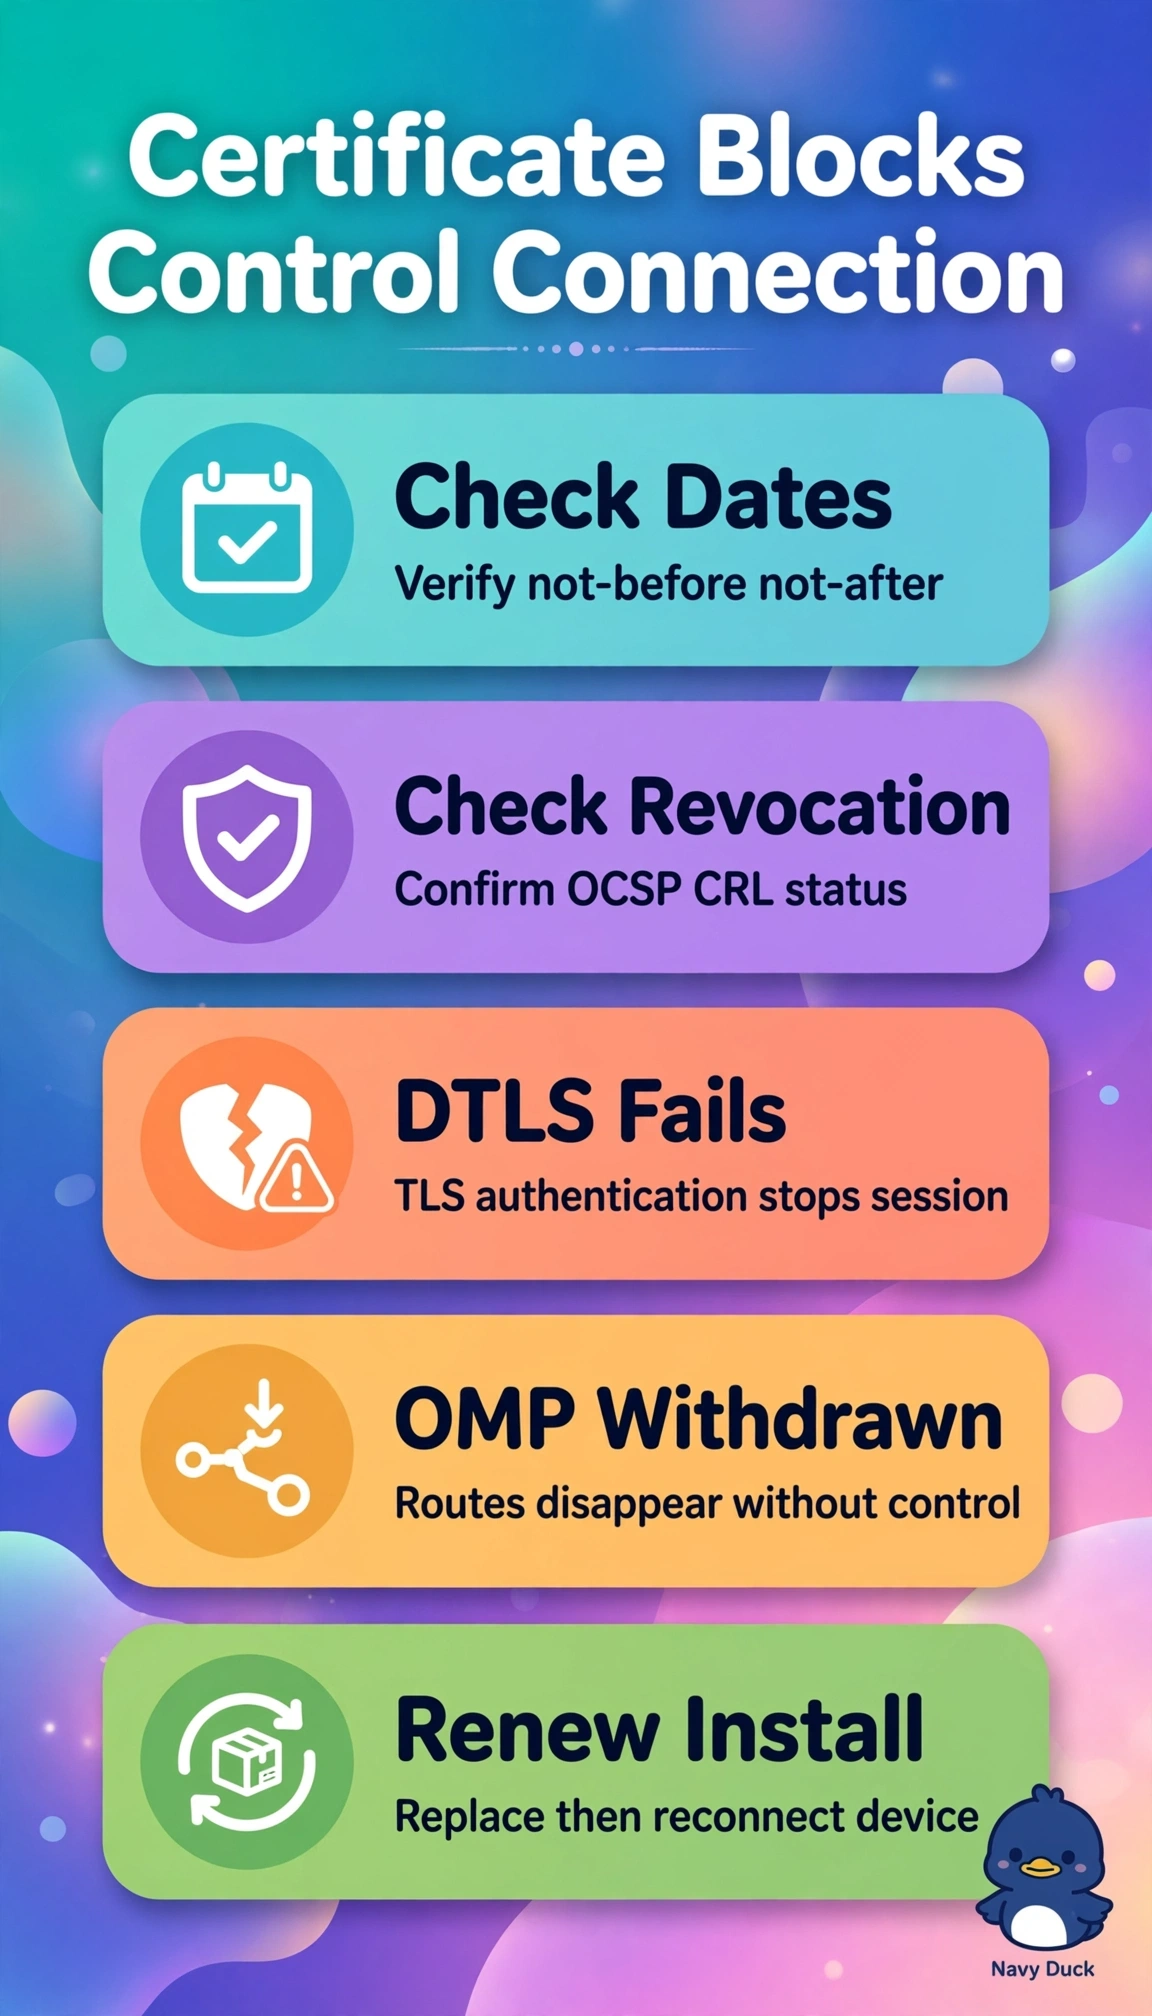
Control connections require the WAN Edge to establish DTLS (or TLS, if configured) to the SD-WAN Controller (formerly vSmart) and DTLS to the SD-WAN Validator after certificate authentication, and both sides check the not-before/not-after dates and reject certificates that are revoked or on the invalid list before the session is allowed to carry OMP and TLOC state. When validity has lapsed or the certificate was revoked during renewal, authentication fails and DTLS remains down, which withdraws OMP routes even if the serial is still listed in SD-WAN Manager. Checking allowlist authorization explains Validator redirect for unknown chassis but does not explain an expired date with a listed serial. Checking the root CA bundle explains trust chain issues for all devices, not selective expiry after renewal. Checking organization-name consistency explains controller rejection across the fabric, not isolated expiry tied to renewal timing. Exam caveat: distinguish authorized serial versus valid certificate, as both are required but tested separately. Practical check: compare the validity dates in show control local-properties against the Manager certificate inventory.