
A new deployment has SD-WAN Manager, two controllers and fifty WAN Edges that show certificate errors and fail to establish DTLS/TLS sessions despite reachability to the Validator. The root CA chain was recently renewed. Which certificate-chain installation step restores trusted control connections for controllers and edges?
Select an answer to reveal the explanation.
Short Explanation
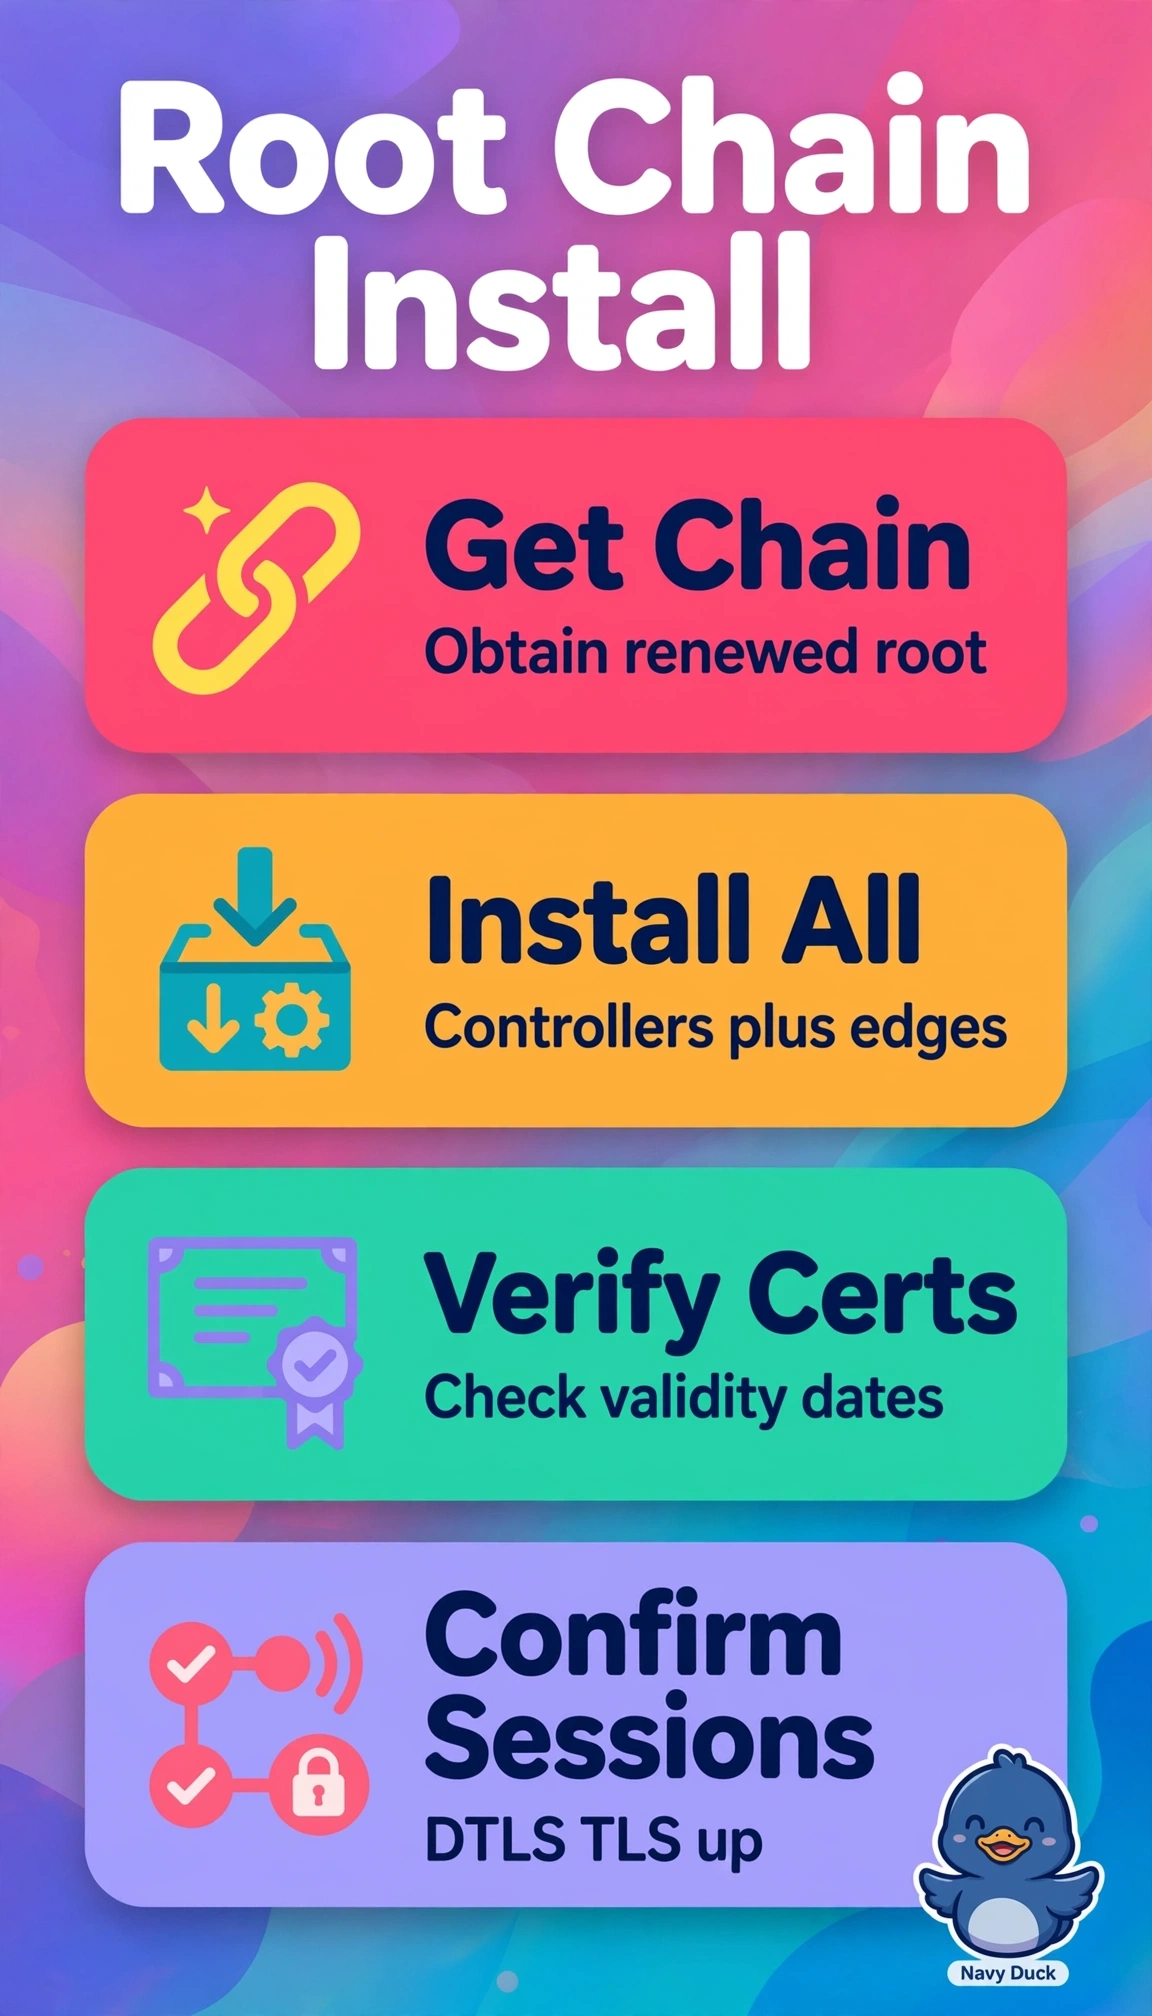
You fix trust fast when every device sees the same root. Installing the renewed chain everywhere lets DTLS and TLS sessions authenticate again.
Full Explanation
The correct step restores trust because DTLS/TLS control connections require each controller and WAN Edge to validate peer certificates against the same renewed root anchor, so after root CA renewal the new chain must be installed where validation is performed, on the controllers and all edges, with show certificate verification of issuer, chain and expiry to prove the trust store changed and negotiation can succeed. Installing the renewed chain only on SD-WAN Manager and the Validator fails by scope because Validator reachability does not confer trust, and the devices actually building the failing sessions still retain the old anchor and continue to reject peers. Reissuing identity certificates without updating the root trust chain fails by anchor concept because even correctly enrolled device certificates cannot be validated when the peer lacks the renewed root needed to build the chain, so errors persist despite fresh identities. Installing only the intermediate bundle fails by completeness because validation requires the full chain to the self-signed renewed root, and an intermediate alone leaves the anchor mismatch unresolved. An exam caveat is to separate reachability, organization assignment and device enrollment from root replacement, since only consistent renewed roots on both ends of every DTLS/TLS session clear post-renewal certificate failures. As a practical check, run show certificate plus show control connections on a controller and sample edges, confirm matching issuer and validity against the renewed bundle, then confirm error state clears to active connections.