
A regional planning commission wants to stop a BGP↔OSPF redistribution feedback loop toward city hall without depending only on tags. Which mechanism directly supports that loop-prevention goal?
Select an answer to reveal the explanation.
Short Explanation
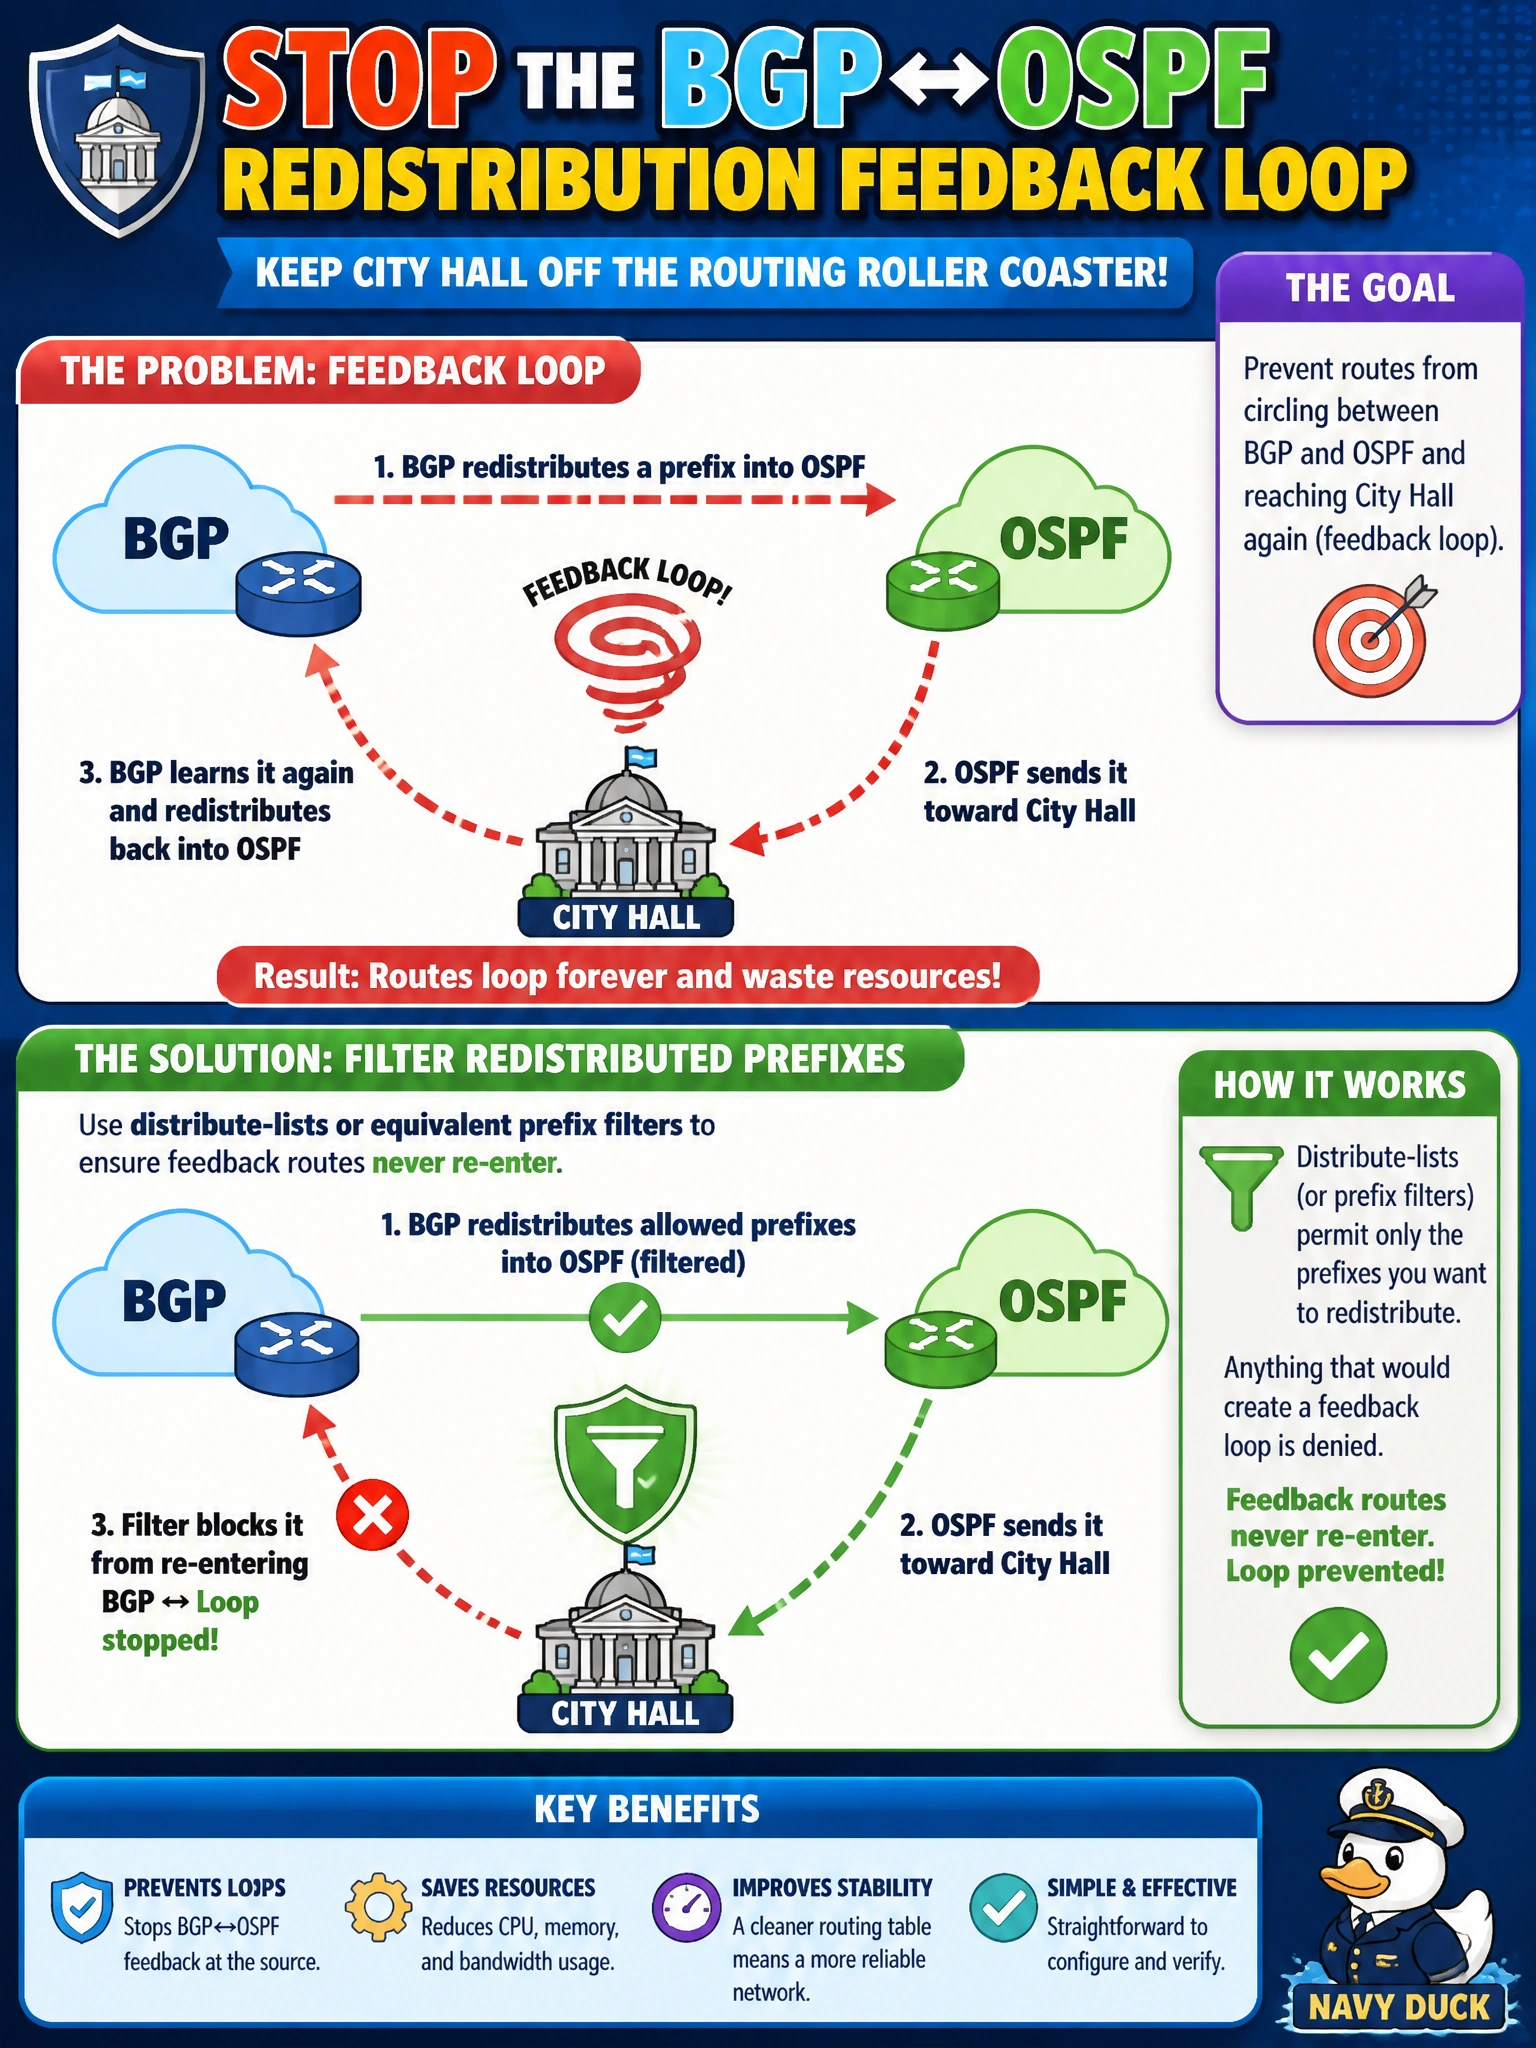
If tags aren't your only tool, slam a filter on redistribution. Distribute-lists or prefix filters keep the bouncing city-hall prefixes from crossing back into the other protocol.
Full Explanation
Loop prevention for BGP↔OSPF redistribution toward city hall can be done with tags, but it can also be done by filtering which prefixes are allowed to cross the redistribution boundary. Filtering redistributed prefixes with distribute-lists or equivalent prefix filters so feedback routes never re-enter is the direct mechanism: distribute-lists, prefix-lists, or route-maps that deny feedback candidate prefixes stop those routes from re-entering the other protocol, breaking the redistribution loop without relying only on tags. For a regional planning commission that wants that direct control, applying distribute-list or equivalent prefix filters on redistribution is a valid primary mechanism.
Increasing OSPF hello multipliers so loops time out faster affects failure detection timers, not redistribution feedback. Enabling BGP synchronization in modern IOS as the sole fix is obsolete; as a modern sole fix it does not address OSPF↔BGP re-injection loops in current designs. Setting all interface priorities to 0 to prevent DR election loops manipulates DR/BDR election and has no bearing on redistribution loops to city hall.
Exam caveat: filters require knowing which prefixes, or prefix sets, constitute feedback risk—often the exact city-hall blocks being redistributed. Tags scale better when many dynamic prefixes need a common mark; prefix filters excel when the set is known and should never cross back. Using both, tag plus prefix deny, is common in hardened municipal designs. Always apply filters in the direction that stops re-entry, not only on initial export.
Operational check: identify a looping city-hall prefix with unstable next hops across show ip route and show ip bgp / show ip ospf database external. Apply a distribute-list/prefix-list deny for that prefix on the redistribution path, then verify the prefix no longer reappears as an external in the opposite protocol. show ip protocols and show route-map / show ip prefix-list confirm the filter attachment and hit counts.