
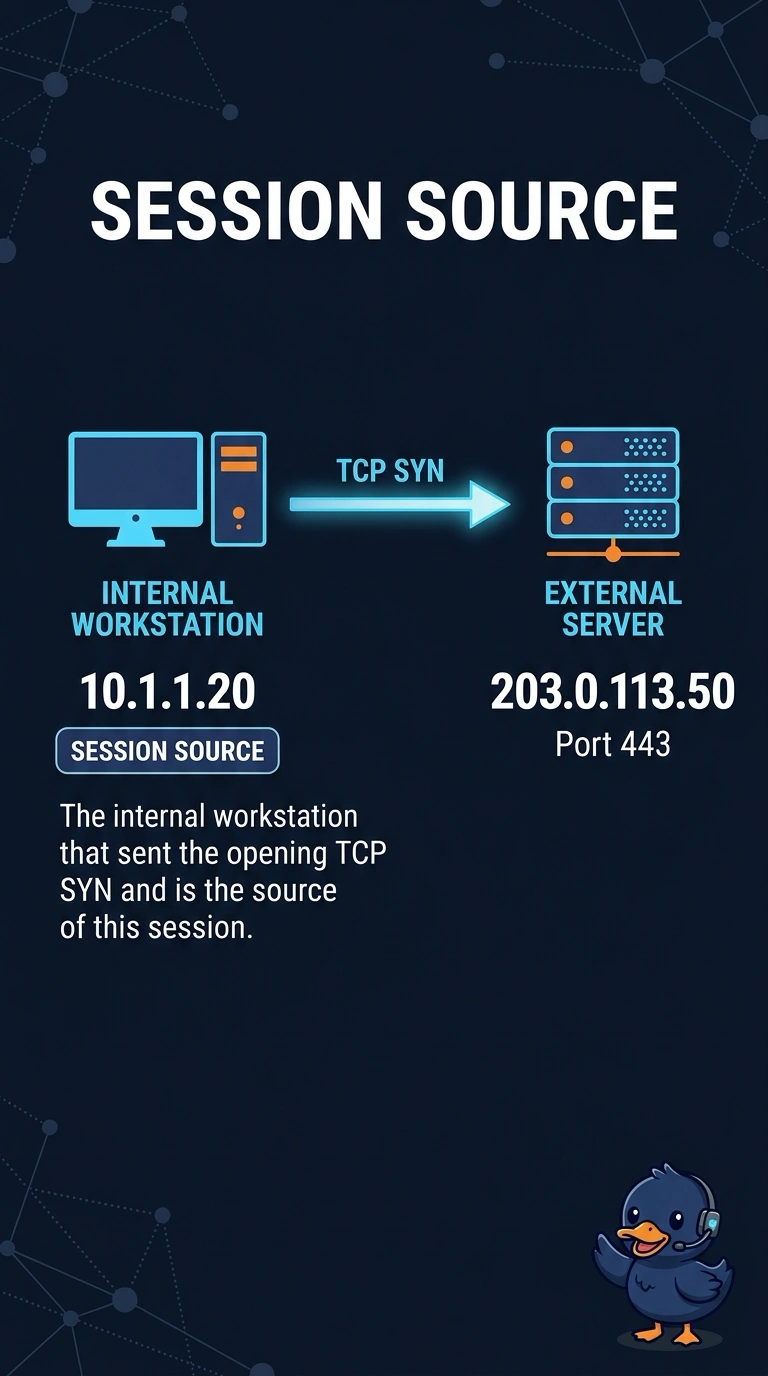
A bank packet capture shows 10.1.1.20 sending a TCP SYN to 203.0.113.50 on port 443, and no reply has arrived yet. What is the source address of this session?
Select an answer to reveal the explanation.
Short Explanation
The person who knocks is the visitor, and the house number is the destination. You take 10.1.1.20, the host that sent the SYN, as the source of the session. The trap is answering with the far address, port 443, or a DNS server that sent nothing.
Full Explanation
The right selection is "10.1.1.20, the internal workstation that sent the opening SYN and is the source address of this session". In the TCP handshake the host that sends the SYN is the side opening the session, and the capture shows 10.1.1.20 sending that SYN toward 203.0.113.50. No reply has arrived, so there is not even a return packet whose source field could be misread as the session source. The statement "203.0.113.50, the address that received the SYN and is the destination of this bank session" is the address that was the target of the SYN, so it is the destination. The statement "Port 443 on the far host, a service port shown in the capture and not an IP source address" is a port number, and the question asks for an address. The statement "The bank DNS resolver, a name server that is not the host shown sending this SYN in the capture" names a server that did not send this SYN, and the capture shows no name lookup. Exam caveat: after a handshake completes, return packets use the server as their packet source, and the session source remains the host that sent the SYN. Operational check: select the SYN packet and read the IP source field on that packet.