
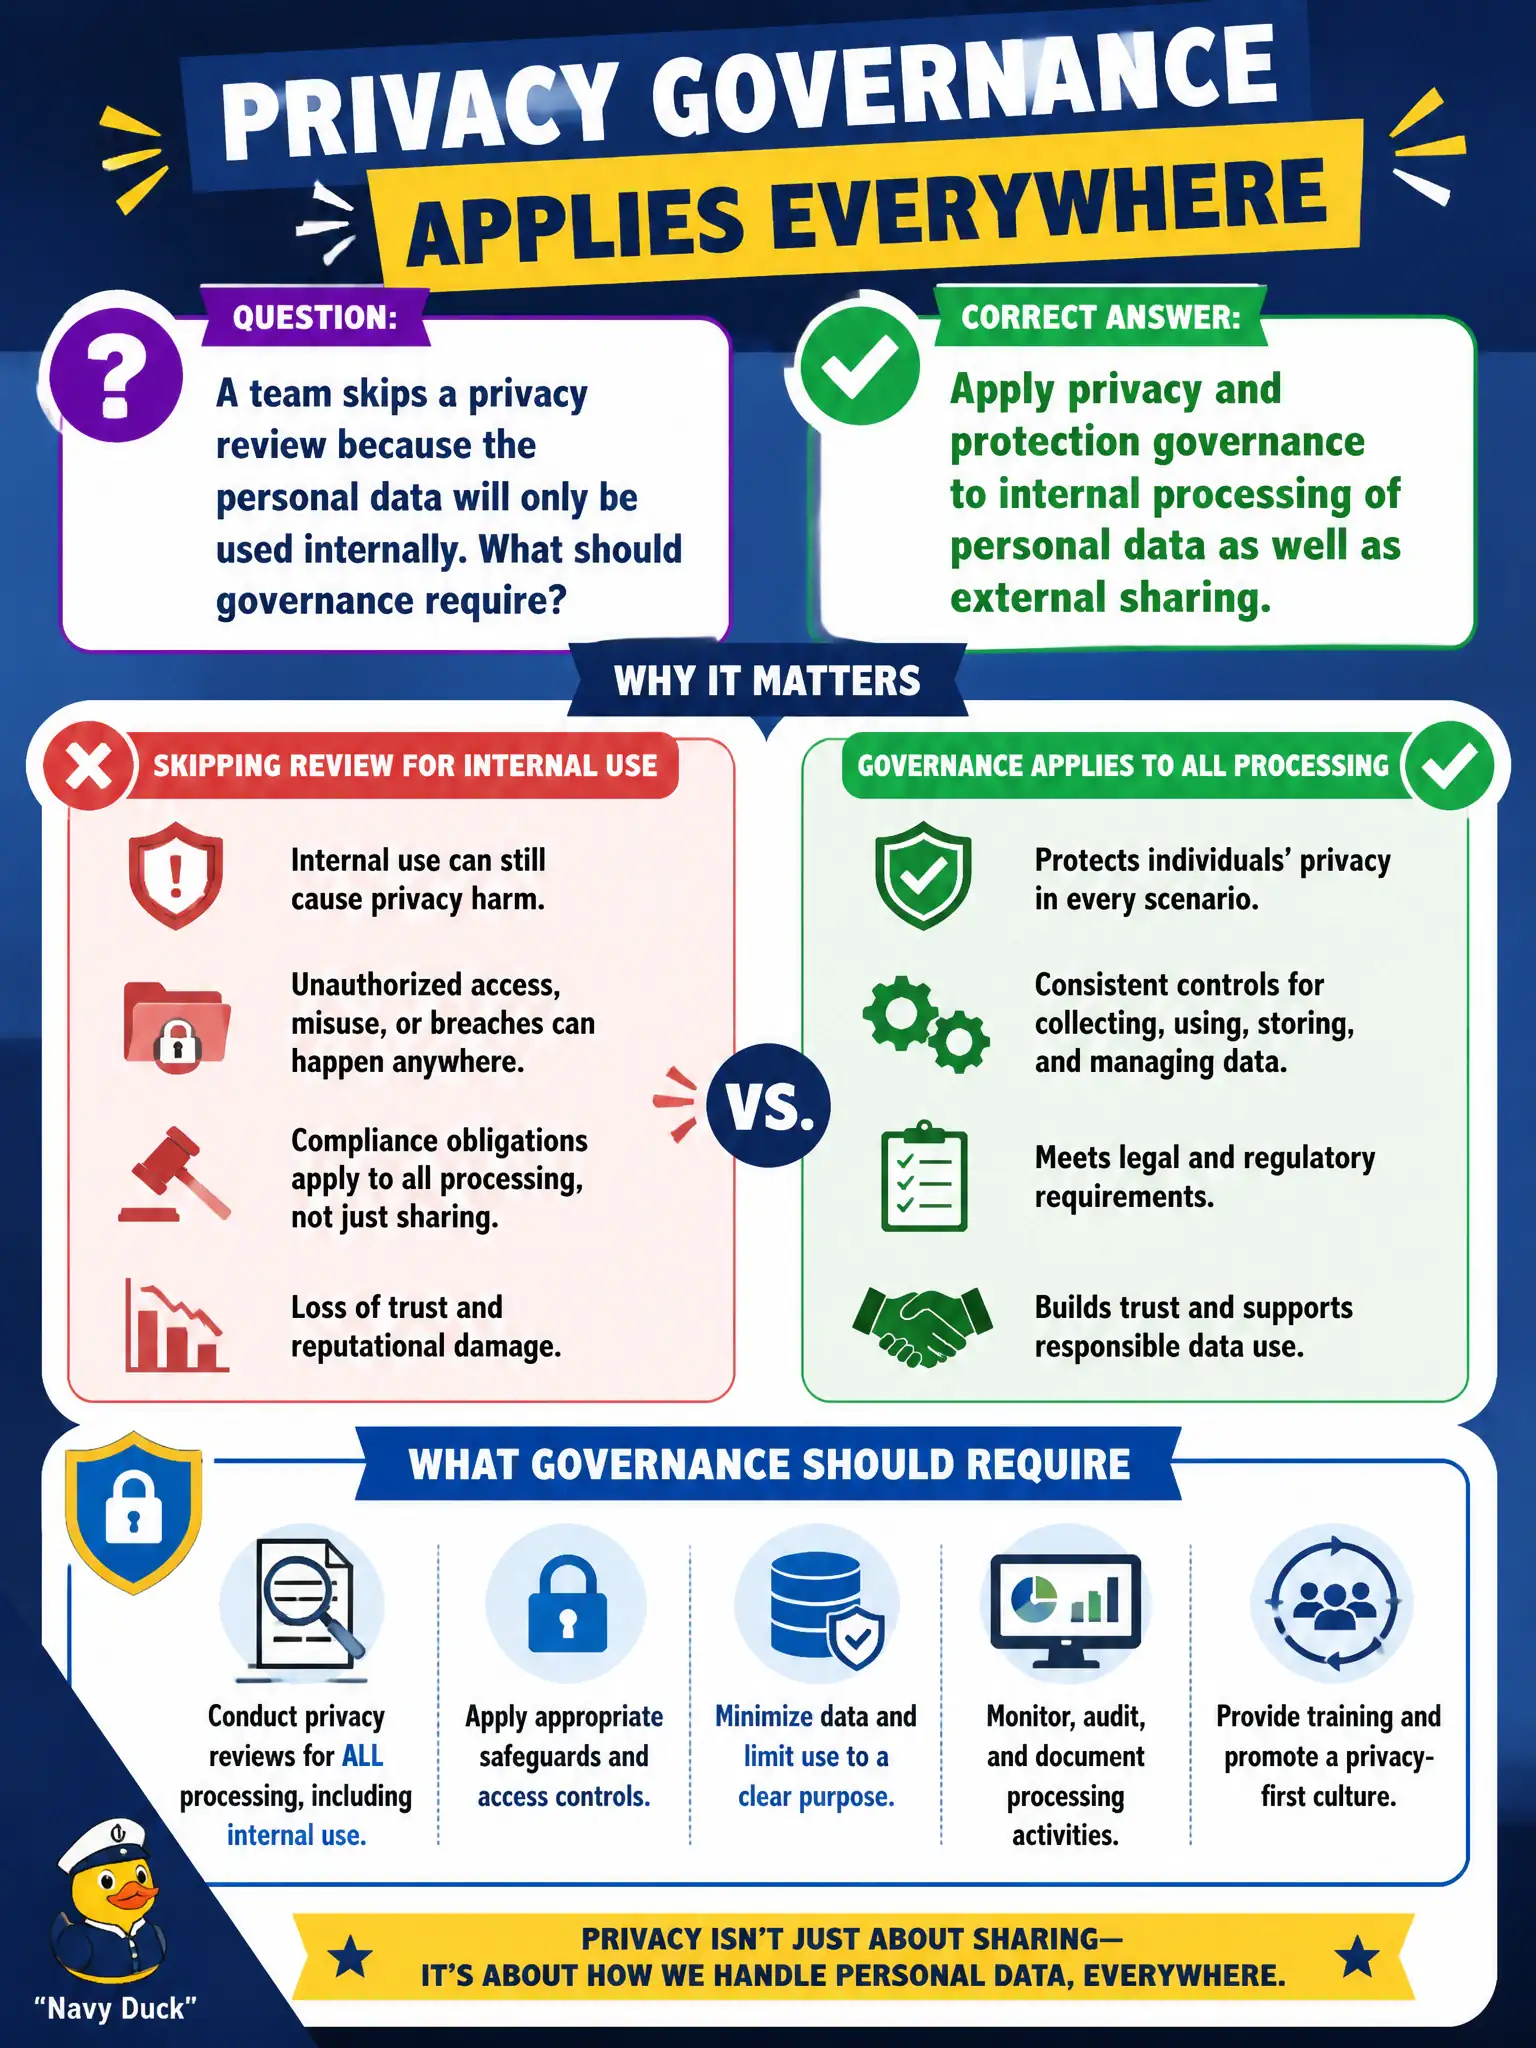
A team skips a privacy review because the personal data will only be used internally. What should governance require?
Select an answer to reveal the explanation.
Short Explanation
Keeping it 'inside the building' does not magically anonymize a resident's file. Internal dashboards, shared drives, and staff lookups still process personal data—so privacy rules still apply. Inside is not a free pass.
Full Explanation
Privacy and protection governance apply to internal processing of personal data as well as external sharing in civic organizations. When a team skips a privacy review because personal data will only be used inside the city, governance should still require review of purpose, minimization, access, and retention. Claiming internal use automatically exempts all personal data from privacy controls is a dangerous misconception for resident and employee information. Limiting privacy reviews to cases where data is sold to external marketers ignores personal data processed daily inside agencies for services and HR. Skipping reviews if the dataset fits on a single shared drive confuses storage size with risk and individual rights. Exam caveat: legal bases and policies vary by jurisdiction, but internal-only is not a universal free pass; document the analysis and approvals. Operational check: route internal personal-data projects through the same privacy triage as external shares, record purpose and access lists, and sample shared drives for unmanaged personal data. City privacy officers and DG should jointly refuse production use of new personal-data stores lacking a completed internal review record.