
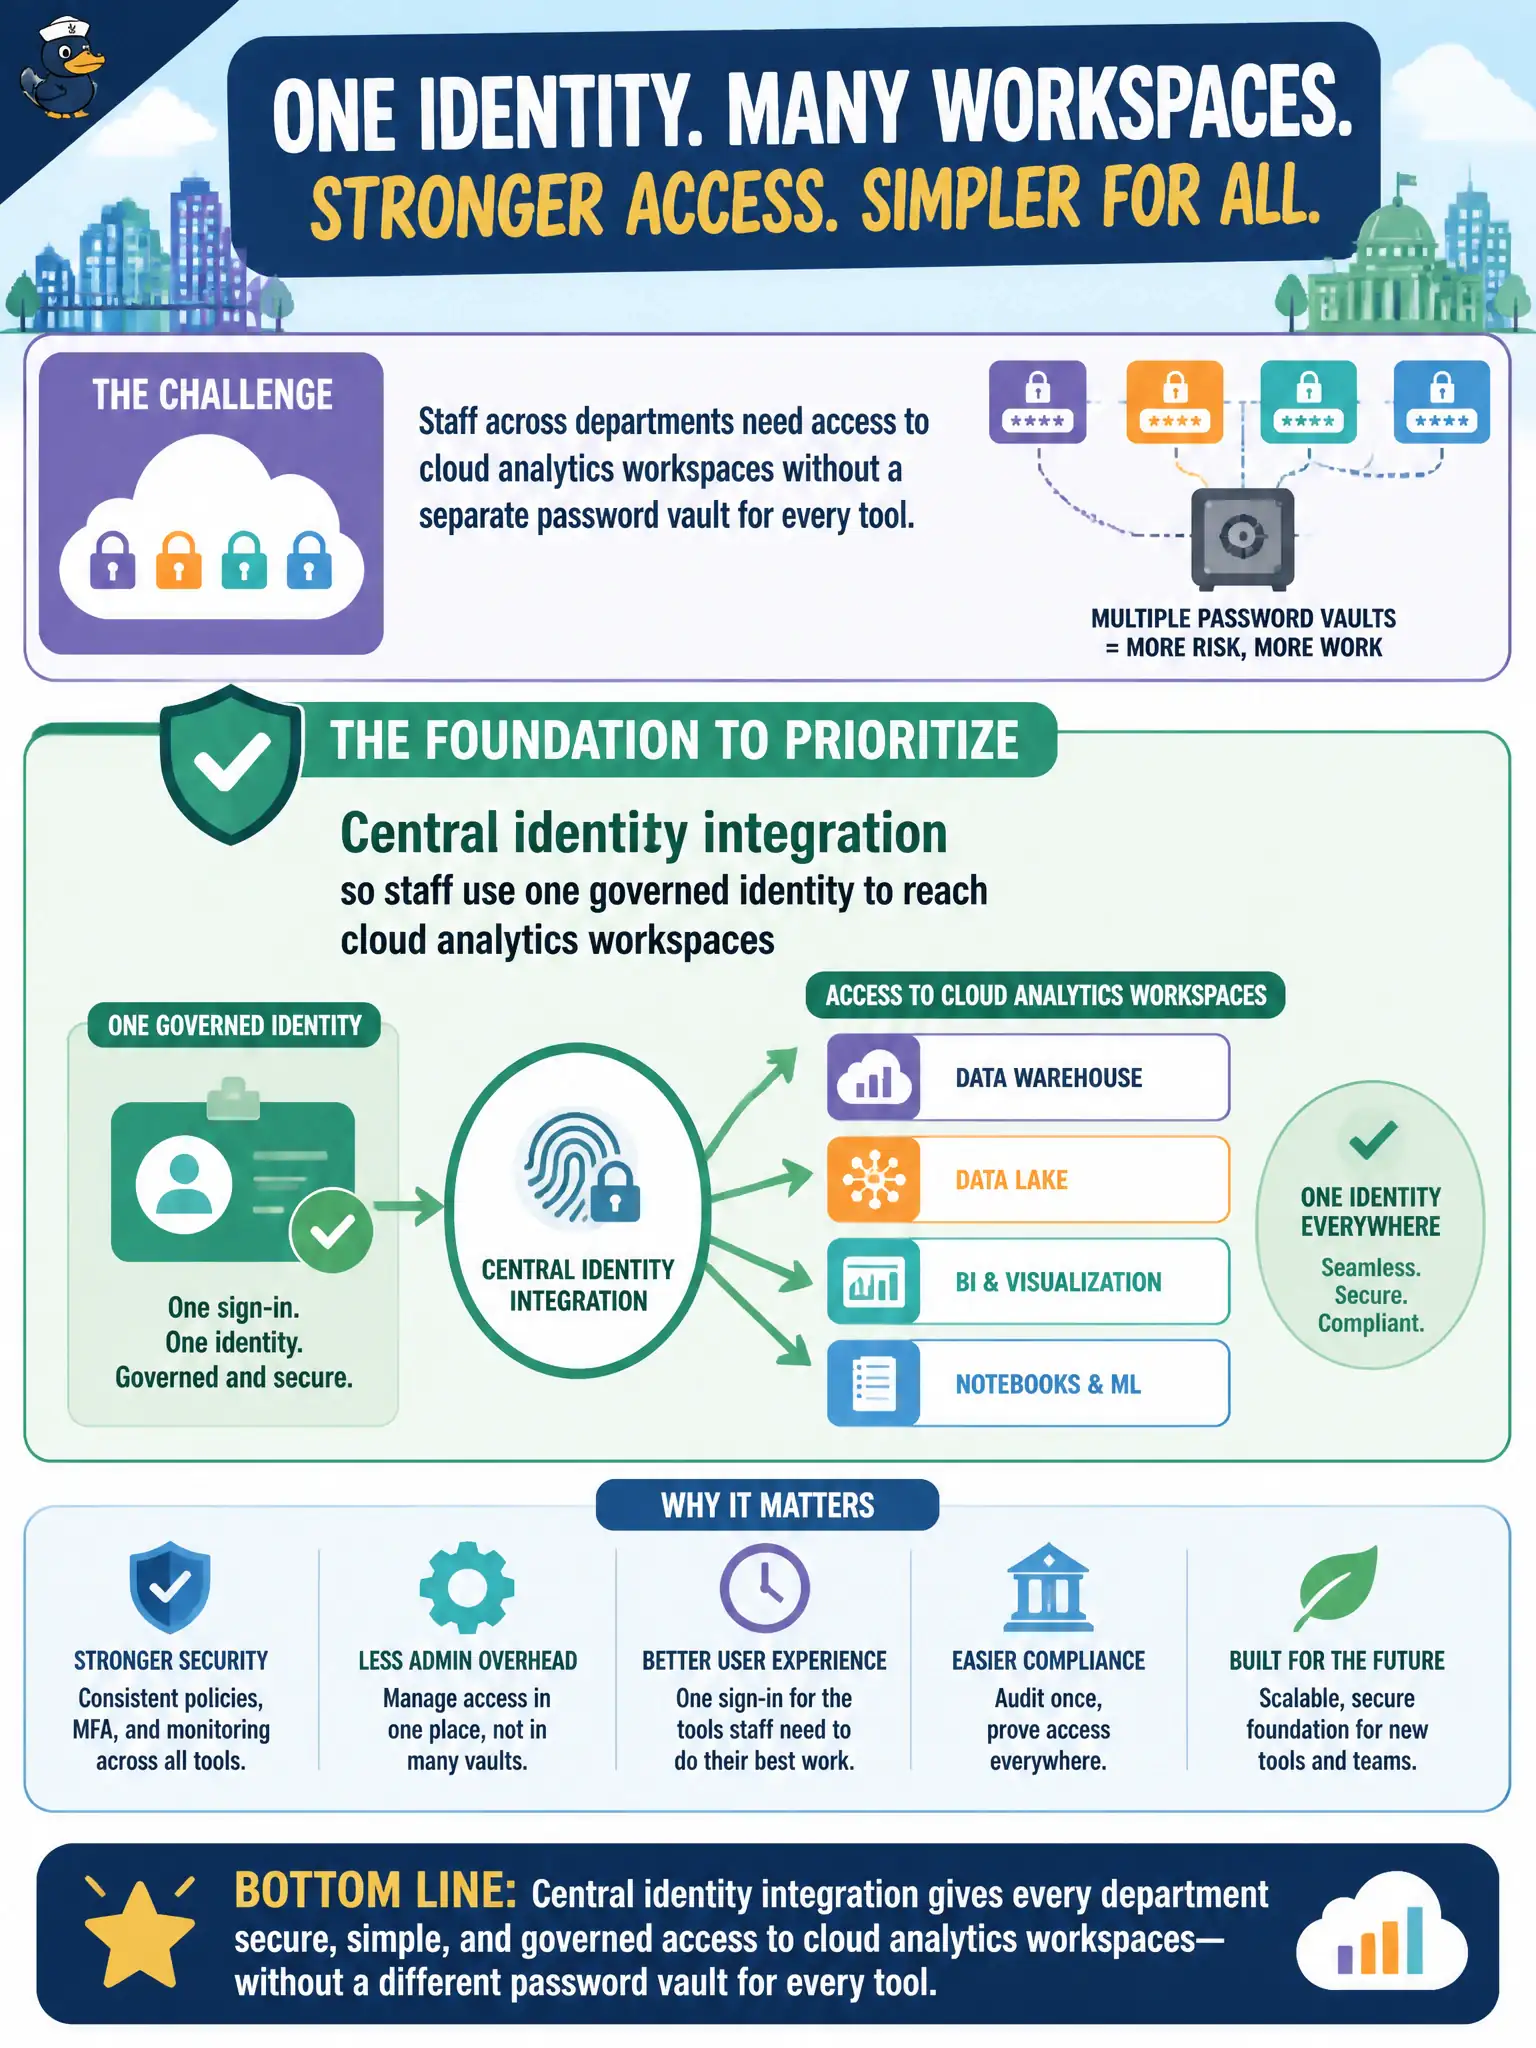
Staff across departments need access to cloud analytics workspaces without a separate password vault for every tool. What foundation should the city prioritize?
Select an answer to reveal the explanation.
Short Explanation
One badge that opens the right doors beats a pocket full of mystery keys. Central identity integration lets staff reach cloud analytics with governed access. Shared passwords and anonymous guest links are governance disasters.
Full Explanation
Central identity integration so staff use one governed identity to reach cloud analytics workspaces is the foundation cities should prioritize across departments. Federated or centralized IAM reduces password sprawl, improves joiners/movers/leavers handling, and supports consistent MFA and audit for municipal analytics. Chapter 9 security and access awareness for civic cloud platforms starts with identity as the control plane.
Shared generic logins taped under keyboards destroy accountability and fail audits when something goes wrong on a weekend. Local-only accounts created independently inside each analytics product recreate password vaults and orphaned access after staff change roles. Anonymous guest links for every internal Spark notebook open uncontrolled sharing paths inappropriate for municipal analytics containing resident-adjacent data.
Exam caveat: central identity must be paired with group-based authorization and periodic access reviews; SSO alone does not remove excess entitlements accumulated over years. Operational check: provision a new analyst via the central identity source only, confirm access to approved analytics workspaces without separate product passwords, then disable the identity and verify access ends across those tools.