
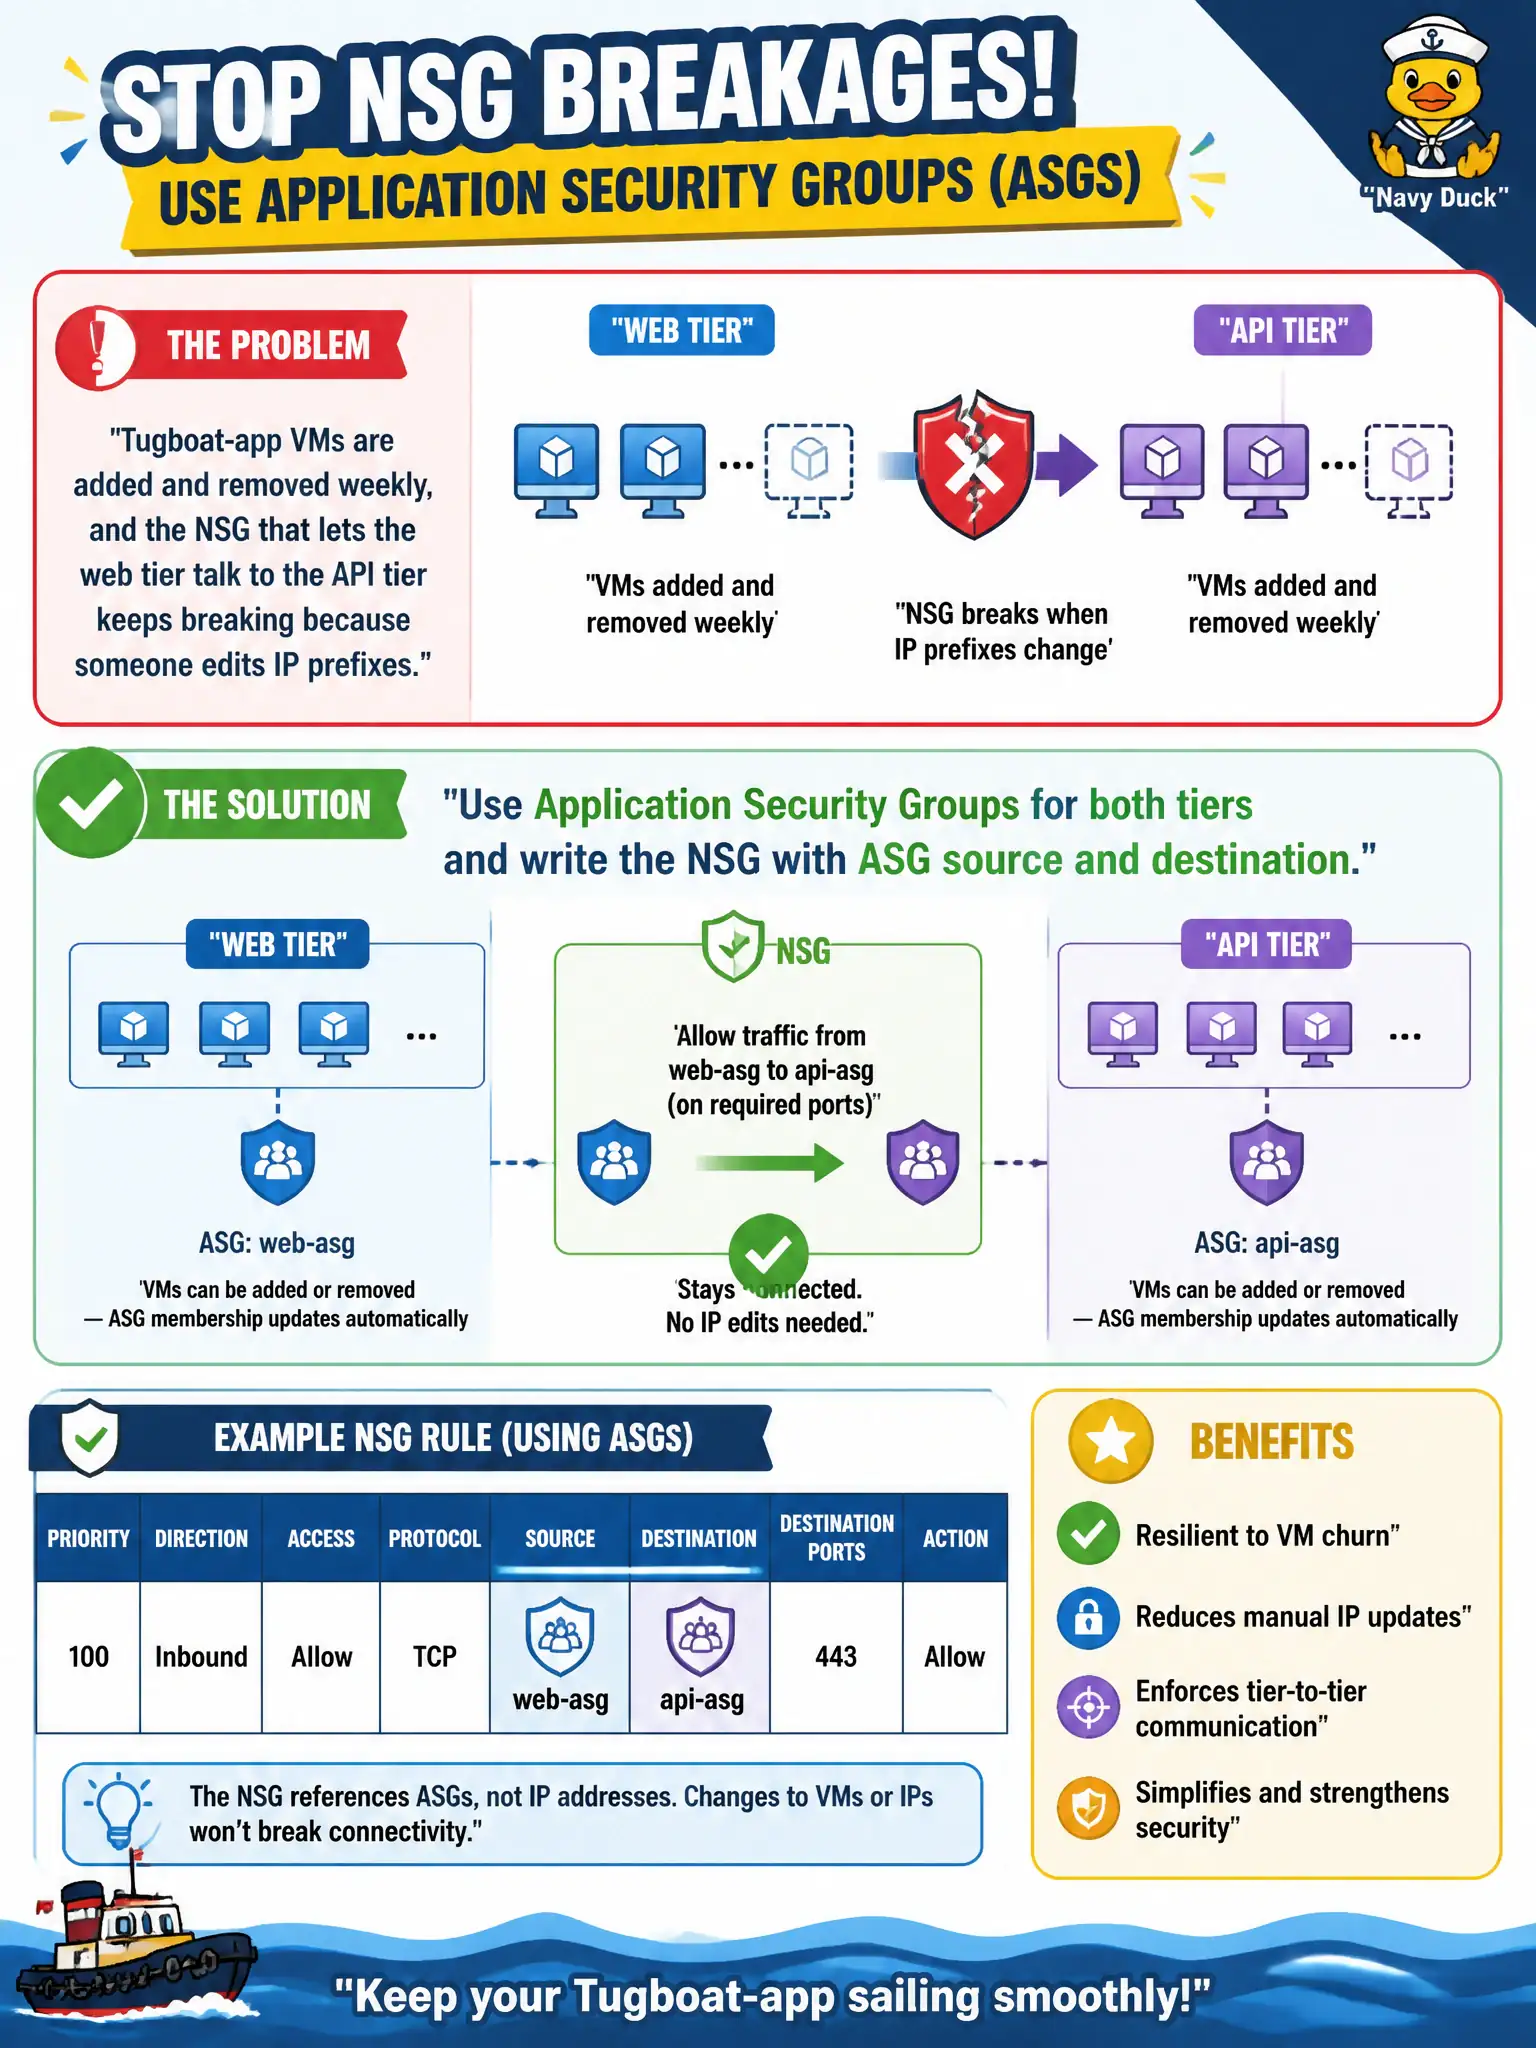
Tugboat-app VMs are added and removed weekly, and the NSG that lets the web tier talk to the API tier keeps breaking because someone edits IP prefixes. What should the security engineer use instead?
Select an answer to reveal the explanation.
Short Explanation
Stop rewriting IP prefixes every time a tugboat VM docks. Drop both tiers into Application Security Groups and let the NSG talk ASG-to-ASG.
Full Explanation
Application Security Groups group NICs by workload role inside a virtual network so NSG rules can use ASG source and destination instead of brittle IP prefixes. For tugboat-app VMs that churn weekly and break NSGs when someone edits IPs, put web and API NICs into ASGs and write the NSG with ASG references so membership changes update targeting without rewriting prefixes each week.
Using Azure Firewall IP Groups only without changing how the subnet NSG names workloads fails the NSG maintainability problem. Using Entra ID security groups as NSG source and destination fails by concept: NSGs do not take Entra groups as five-tuple fields. Static public IP allow lists on every NIC fail architecture for private east-west traffic.
Exam caveat: ASGs are scoped to a virtual network and simplify east-west micro-segmentation. Operational check: create ASG-web and ASG-api, associate NICs, rewrite NSG rules to ASG source and destination, add or remove a VM from an ASG, and confirm connectivity tracks membership without IP edits. In municipal Azure estates, document the decision in the change record, validate with a nonproduction rehearsal, and confirm monitoring still pages the on-call operator when the control fails closed during an incident drill.