
Compost-lab front-end VMs must reach only the mid-tier VMs on TCP 8443, not every NIC covered by the VirtualNetwork service tag. What NSG design should the security engineer apply?
Select an answer to reveal the explanation.
Short Explanation
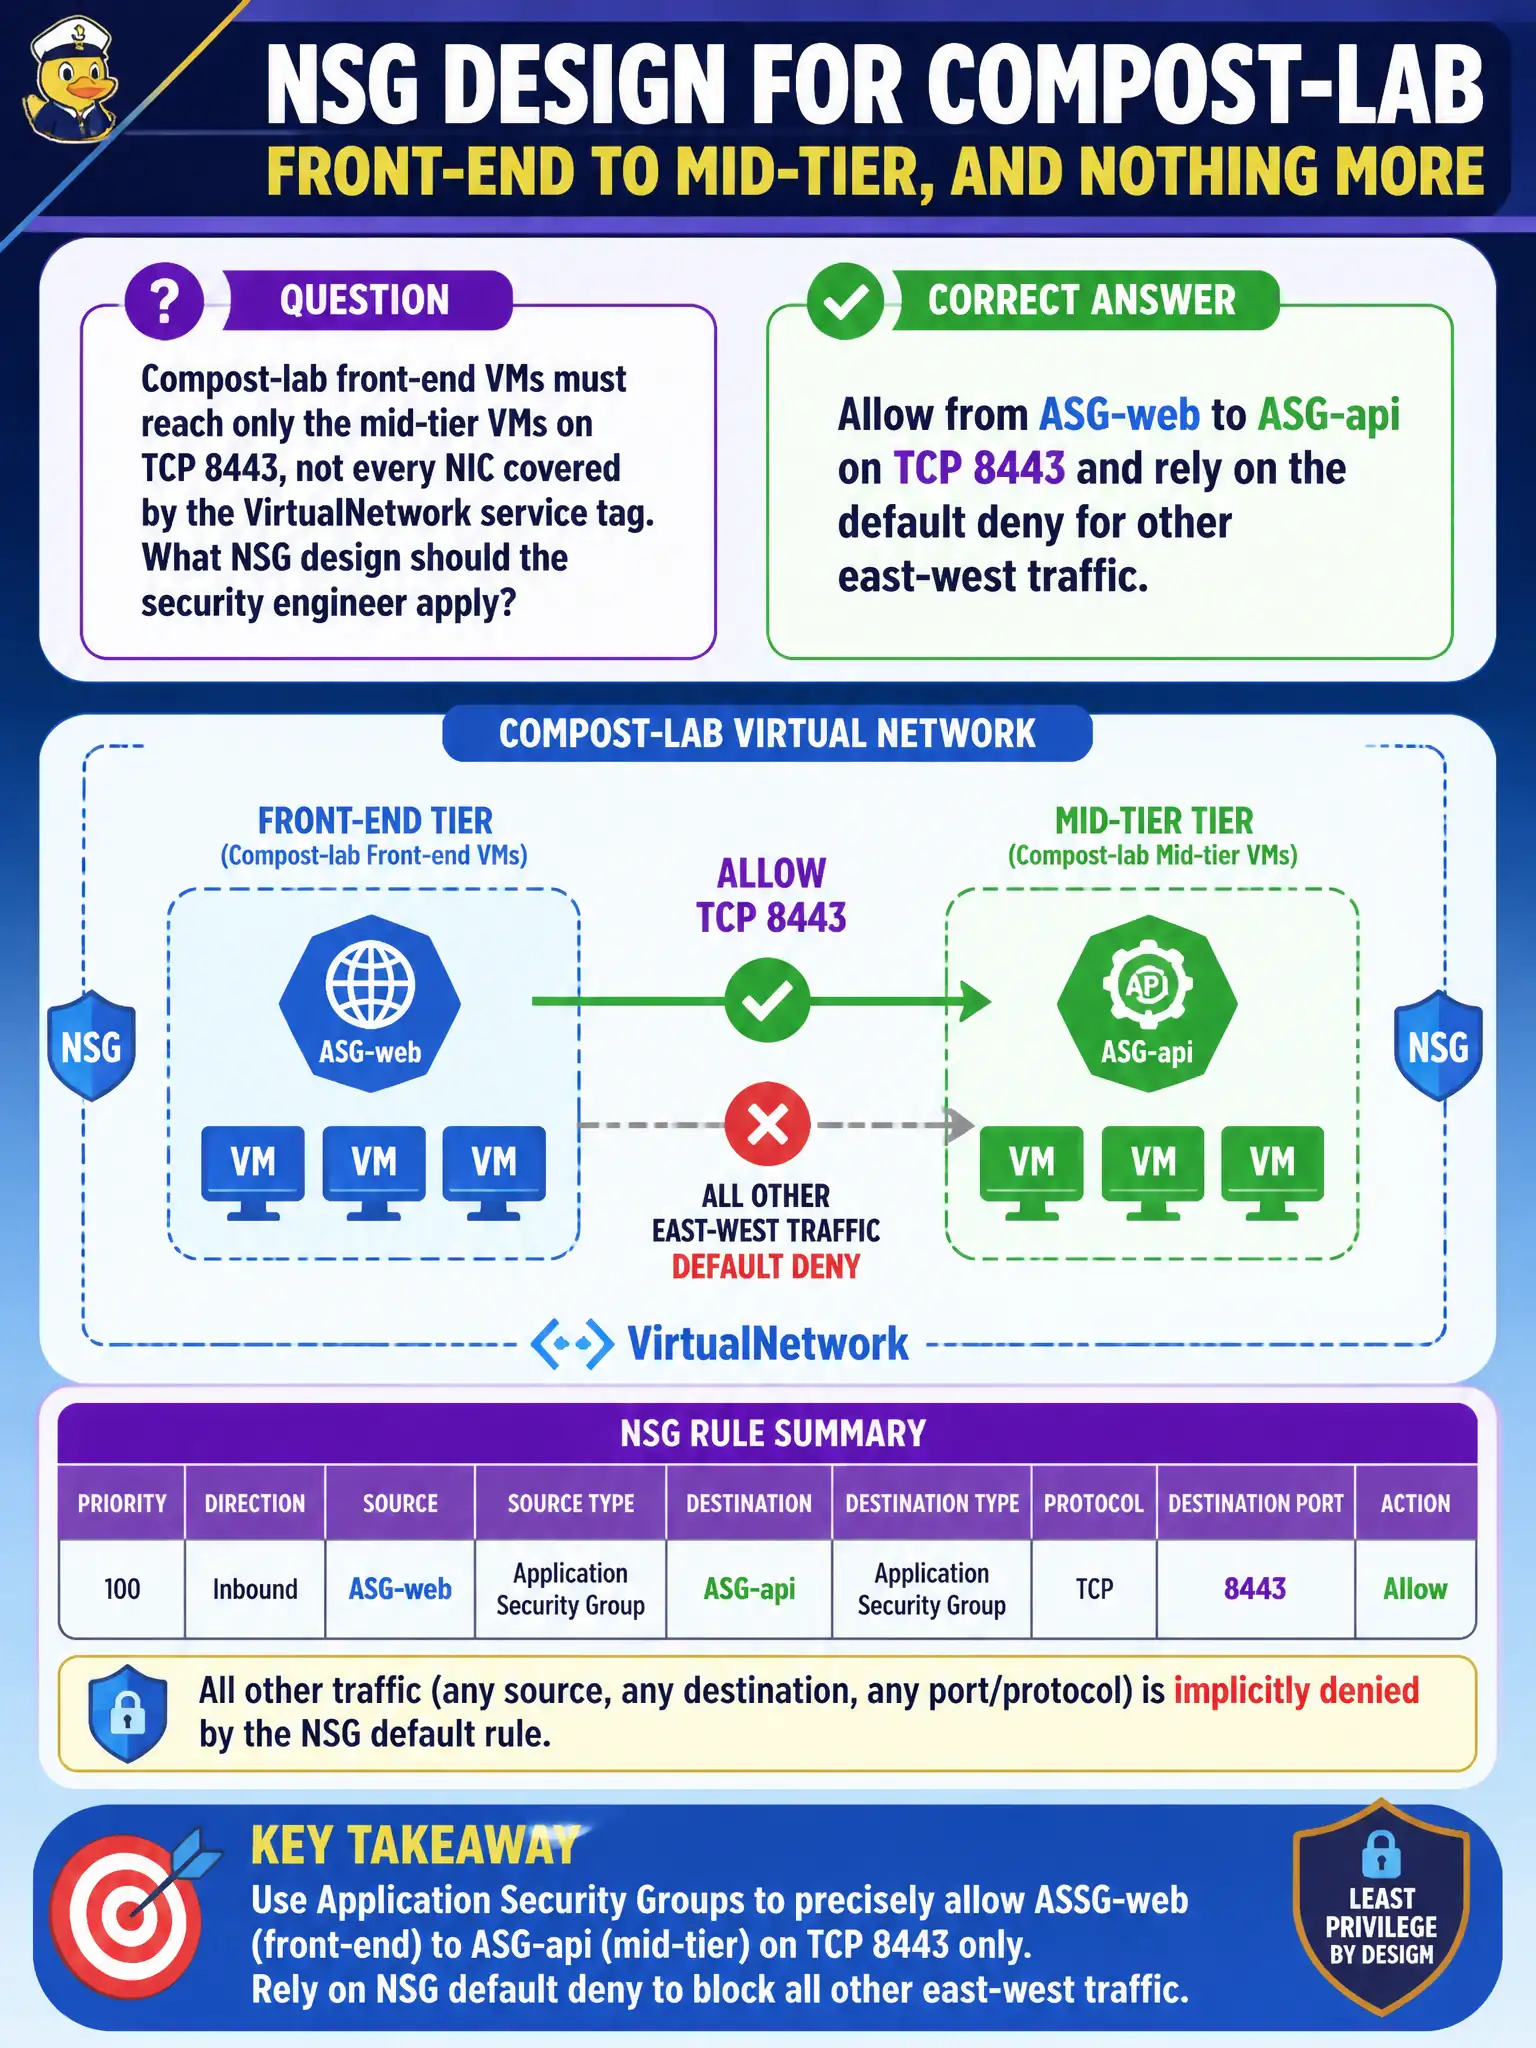
Don’t throw VirtualNetwork wide open like a barn door. Allow ASG-web to ASG-api on 8443 and let the default deny muzzle the rest of east-west.
Full Explanation
Least-privilege east-west design uses Application Security Groups so only intended tiers talk on required ports, relying on default deny for other flows. For compost-lab front-end VMs that must reach only mid-tier VMs on TCP 8443—not every NIC covered by VirtualNetwork—allow from ASG-web to ASG-api on TCP 8443 and let default Deny stop other east-west paths.
Allowing VirtualNetwork to VirtualNetwork on Any fails micro-segmentation. Removing all NSGs and depending solely on Azure Firewall application rules for every east-west flow fails as the only design here—the question asks for NSG and ASG least privilege between tiers. Opening TCP 8443 from Internet to ASG-api fails by exposing the mid-tier publicly.
Exam caveat: the VirtualNetwork service tag is convenient and often too broad for tier isolation. Operational check: implement the ASG allow on 8443, verify front-end to API works, verify front-end cannot reach unrelated NICs on other ports, and review that default rules still deny residual traffic. In municipal Azure estates, document the decision in the change record, validate with a nonproduction rehearsal, and confirm monitoring still pages the on-call operator when the control fails closed during an incident drill.