
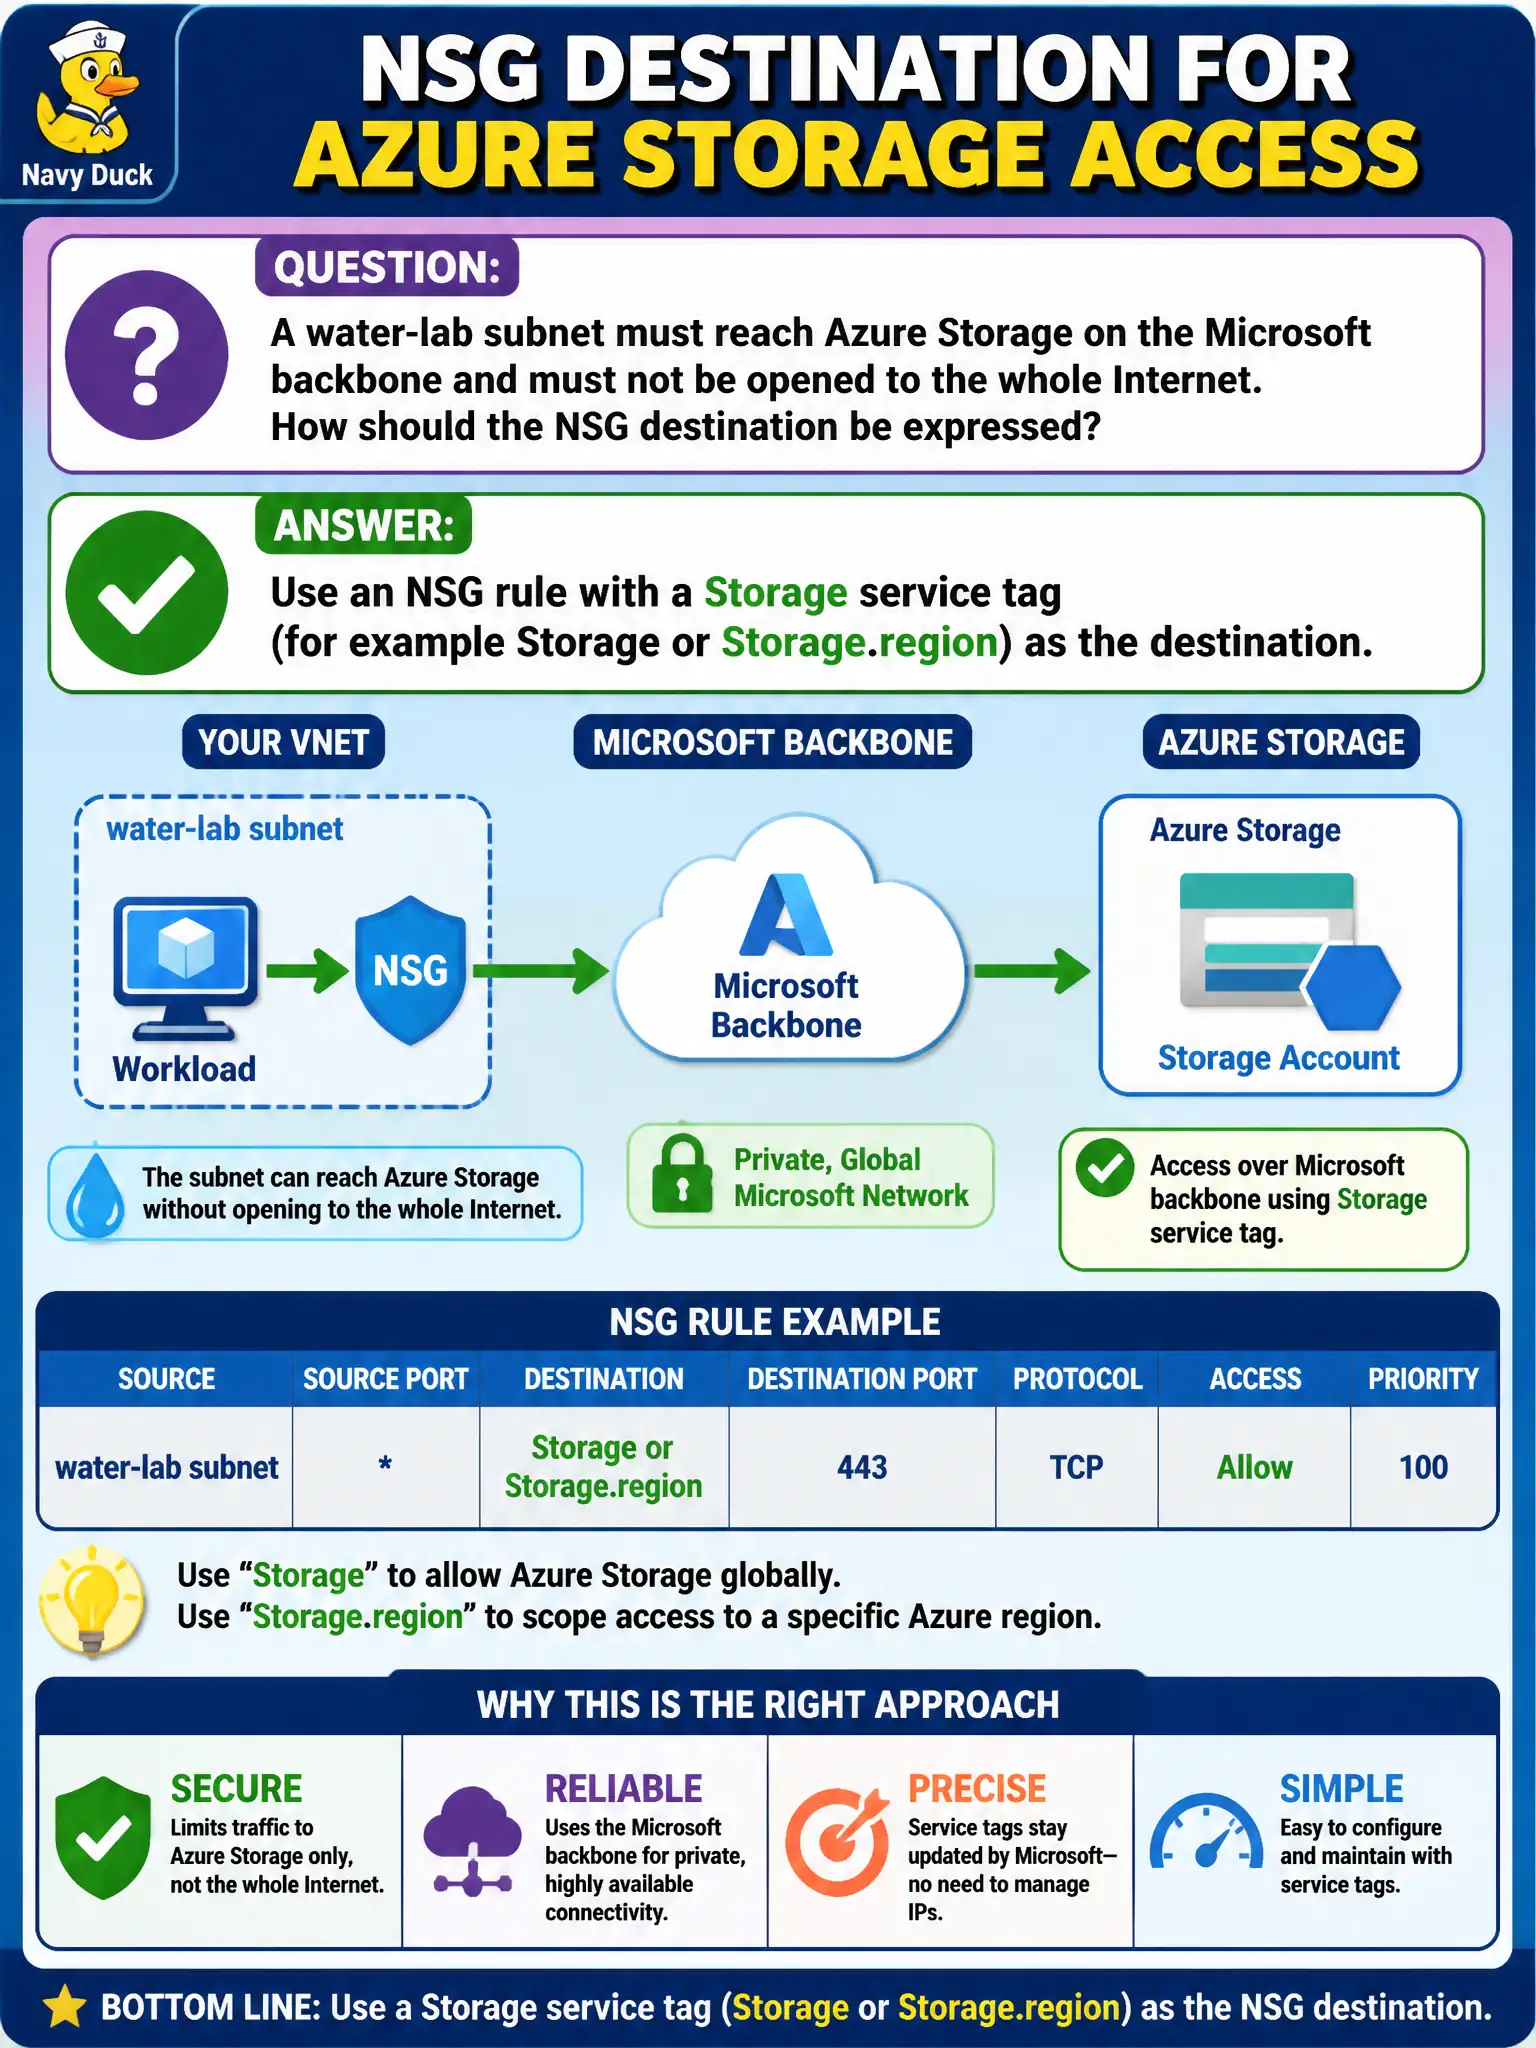
A water-lab subnet must reach Azure Storage on the Microsoft backbone and must not be opened to the whole Internet. How should the NSG destination be expressed?
Select an answer to reveal the explanation.
Short Explanation
Don’t babysit Storage’s public IP phone book. Point the NSG at the Storage service tag and let Microsoft keep the list honest while you stay off wide-open Internet.
Full Explanation
Service tags represent groups of Microsoft-managed IP prefixes for Azure services and regions. For a water-lab subnet that must reach Azure Storage without opening the NSG to the whole Internet, express the destination with a Storage service tag (Storage or Storage.REGION as appropriate) in the NSG rule so Microsoft-managed prefix updates remain aligned.
Allowing destination Any fails least privilege. Pasting a handwritten list of every Storage public IP fails operations because Microsoft prefix lists change. Assigning Contributor on the storage account to every NIC fails by concept: RBAC is not a substitute for NSG destination design and over-privileges every NIC.
Exam caveat: service tags help identify Azure services in NSGs and Firewall; they are not a replacement for Private Link when private connectivity is required. Operational check: add an NSG allow to the Storage service tag for needed ports, deny broader Internet where policy requires, test connectivity, and review service-tag changes in maintenance windows. In municipal Azure estates, document the decision in the change record, validate with a nonproduction rehearsal, and confirm monitoring still pages the on-call operator when the control fails closed during an incident drill.