
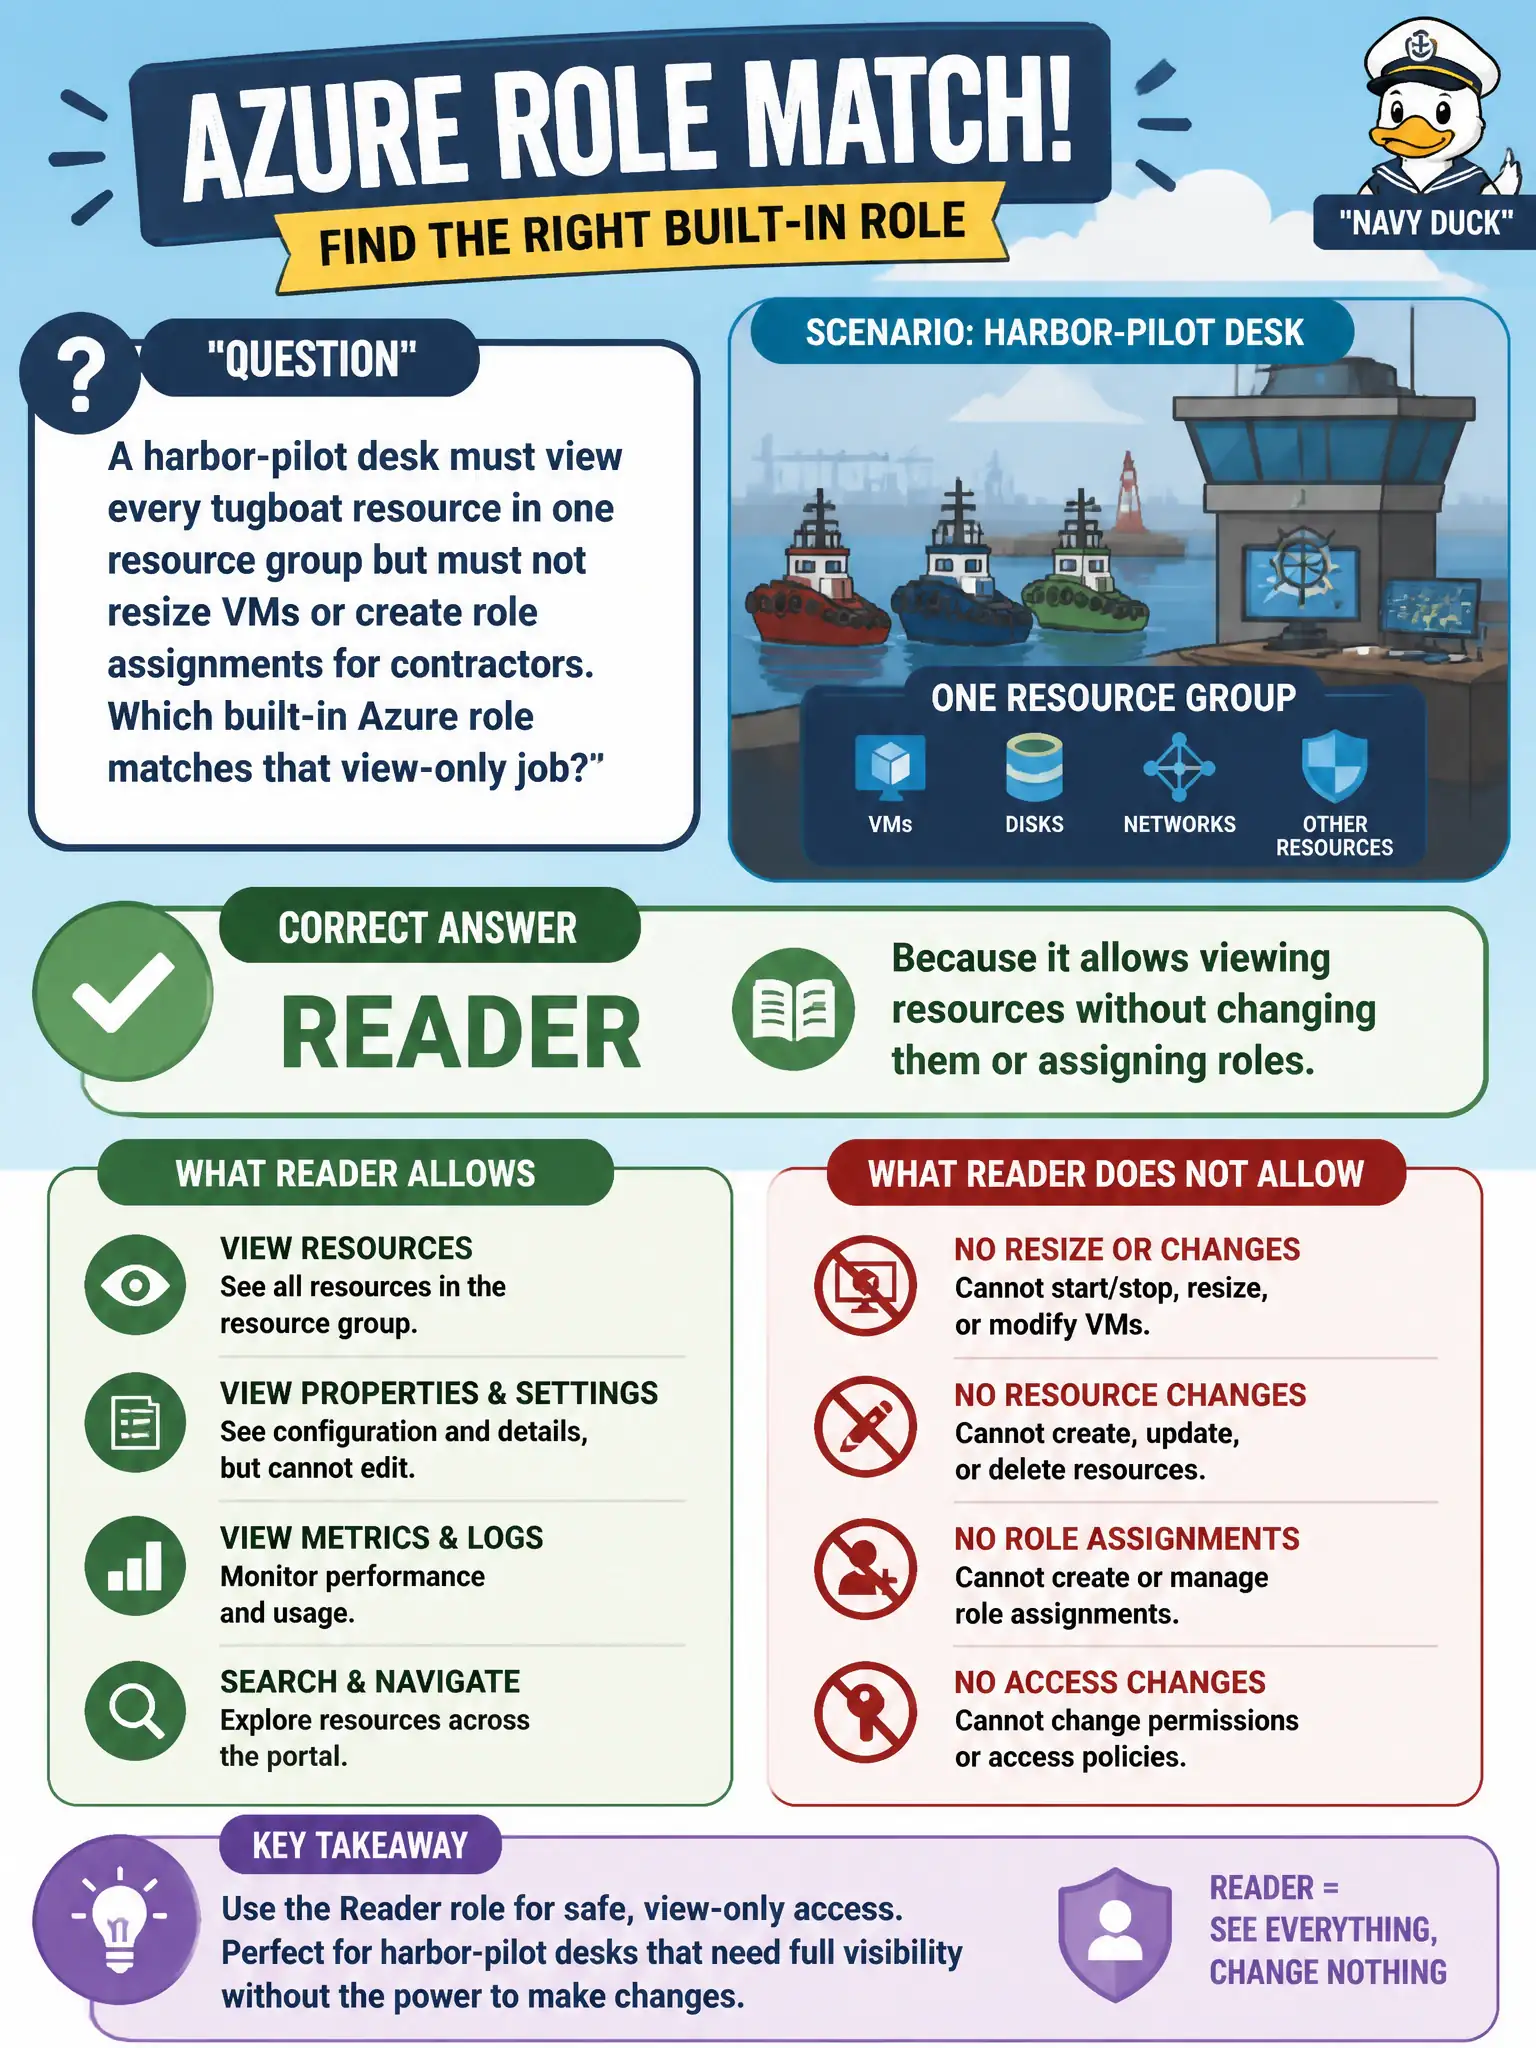
A harbor-pilot desk must view every tugboat resource in one resource group but must not resize VMs or create role assignments for contractors. Which built-in Azure role matches that view-only job?
Select an answer to reveal the explanation.
Short Explanation
Reader is the tourist pass: you can look at every tug in the harbor map, but you cannot move a boat or hand out keys. Contributor changes resources; Owner also hands out role assignments—neither is what the pilot desk asked for.
Full Explanation
Reader is the built-in Azure role that grants read access to resources without permitting writes, deletes, or Microsoft.Authorization role-assignment actions. For the harbor-pilot desk that must view every tugboat resource in one resource group while staying barred from resizing VMs or handing contractors new rights, Reader at that resource group matches the view-only job: operators can inventory and inspect without changing compute size or identity grants.
Contributor fails by concept because it can manage nearly all resource types except assign roles; resizing VMs and deleting networking are in scope, which violates the “must not resize” requirement even though role assignment is excluded. Owner fails because Owner is not required merely to list resources—Reader already lists—and Owner adds full management plus the ability to assign roles, the opposite of least privilege. User Access Administrator fails because that role is centered on managing access (creating and removing role assignments); it is not the general-purpose read role for viewing tugboat resources and does not substitute for Reader’s resource-read permissions.
Exam caveat: Owner, Contributor, Reader, and User Access Administrator are foundational built-ins; AZ-500 commonly tests that listing resources needs Reader (or a job-function read role), not Owner. Operational check: assign Reader on the resource group, sign in as a desk user, confirm resources are visible in the portal, attempt a VM resize and a role assignment, and verify both are denied.