
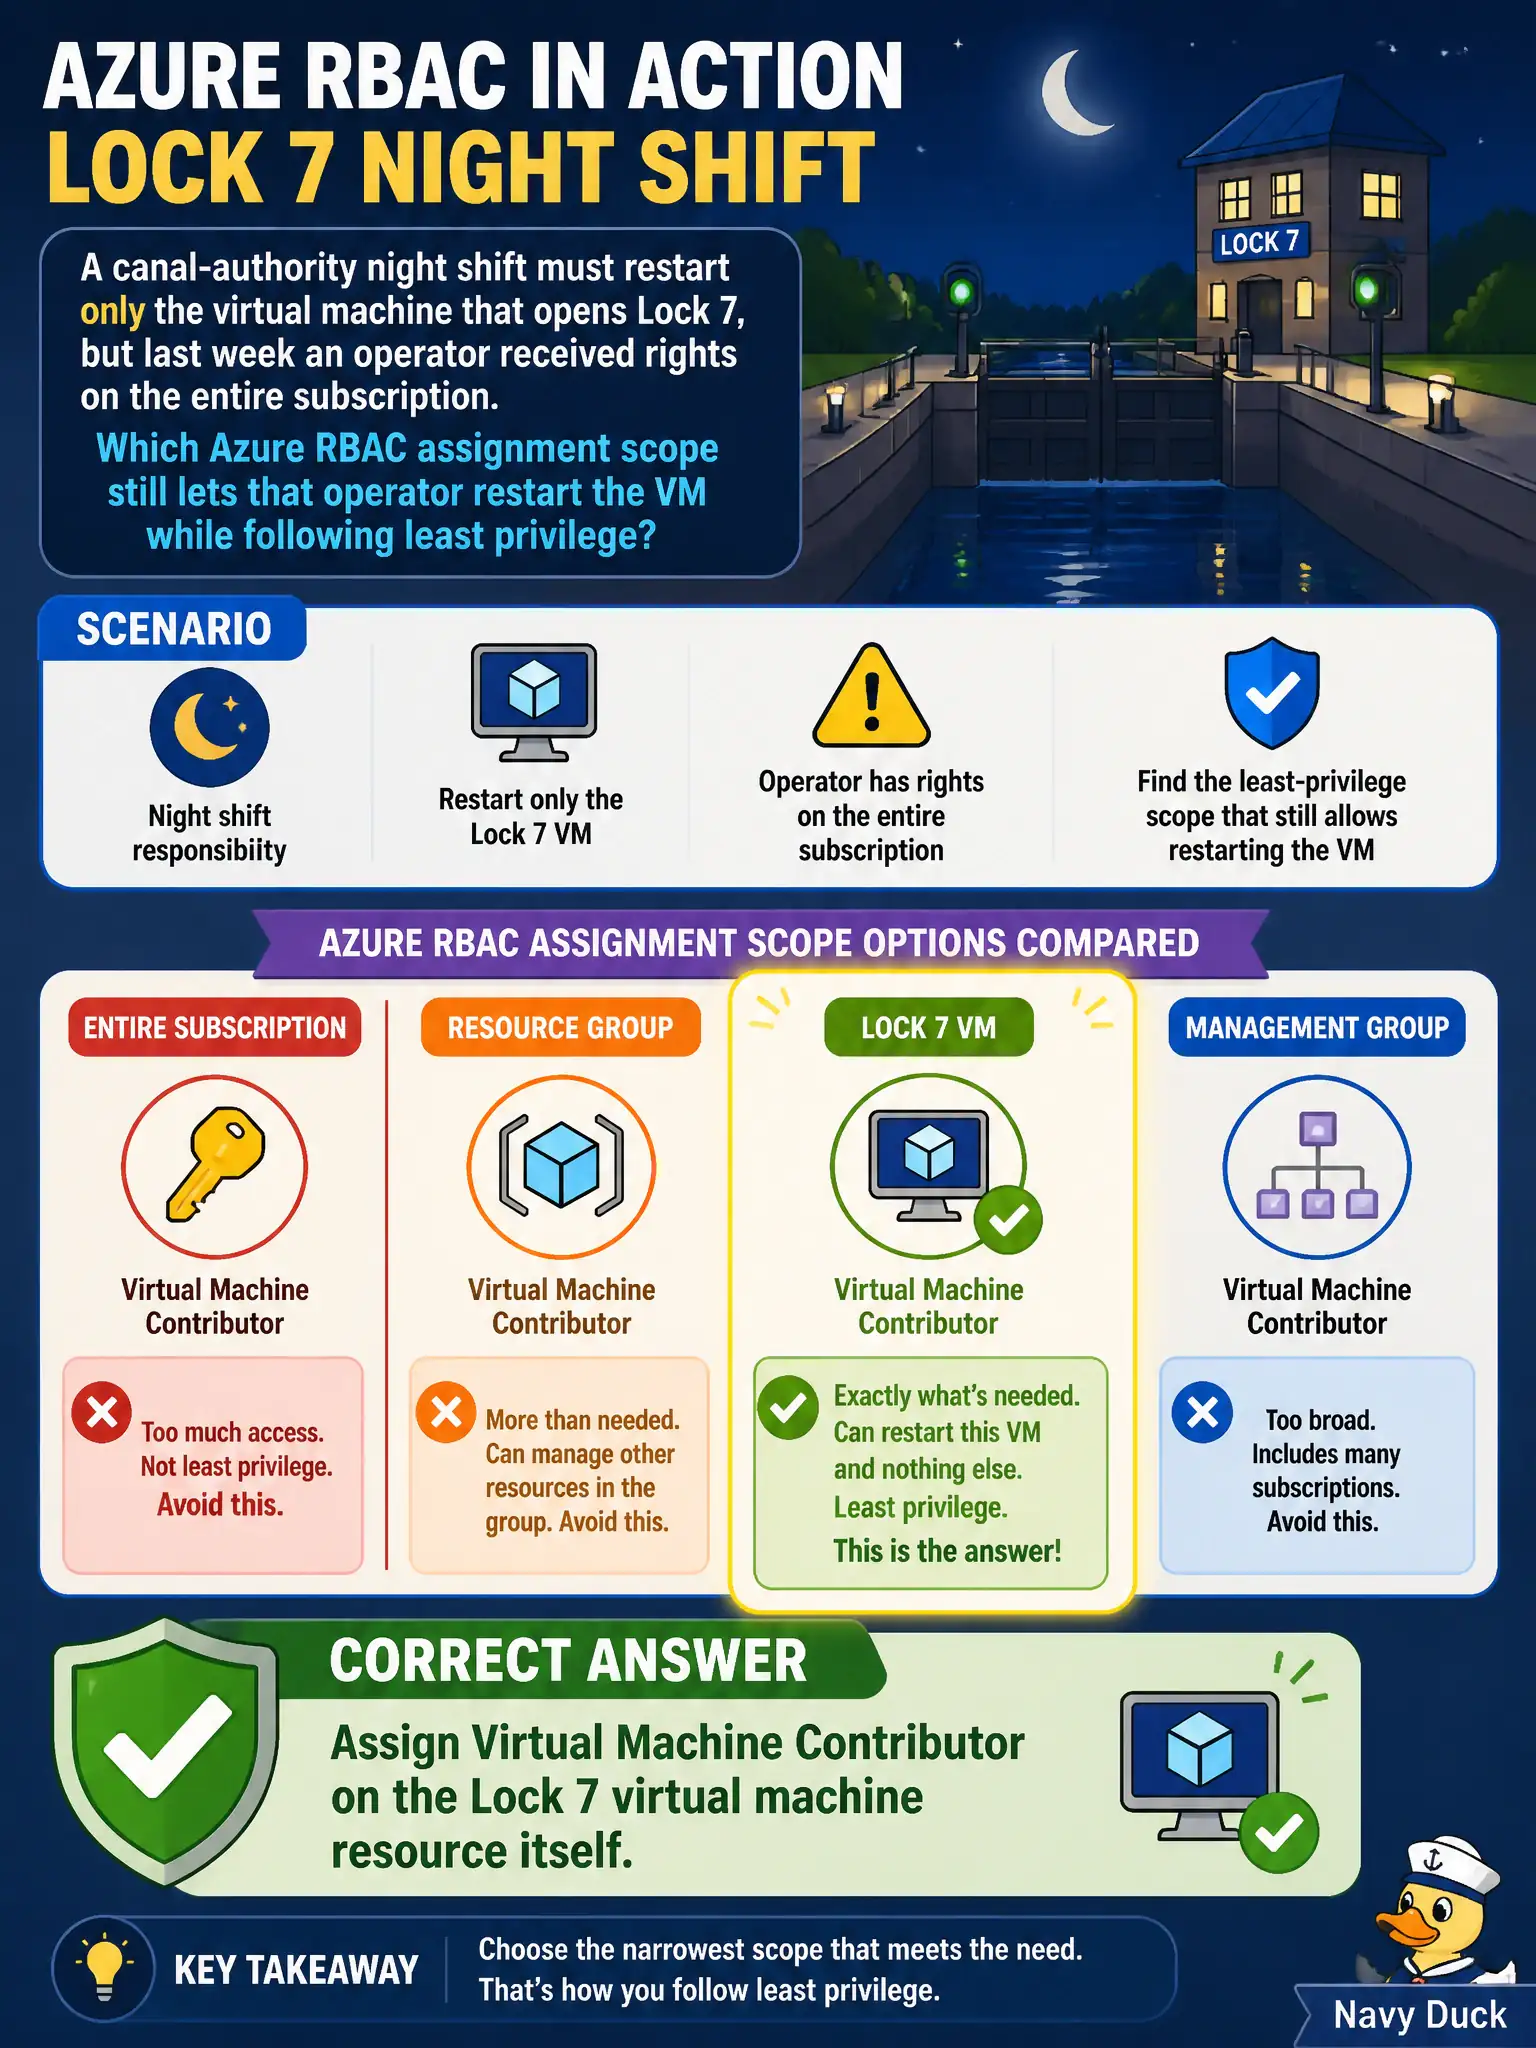
A canal-authority night shift must restart only the virtual machine that opens Lock 7, but last week an operator received rights on the entire subscription. Which Azure RBAC assignment scope still lets that operator restart the VM while following least privilege?
Select an answer to reveal the explanation.
Short Explanation
Think of the canal as nested boxes: management group, subscription, resource group, then the single lock VM. Hand the night shift the key to that one VM box—Virtual Machine Contributor on the Lock 7 resource—so they can restart it without opening every other lock on the waterway.
Full Explanation
Azure RBAC scopes nest from management group to subscription to resource group to the individual resource. Assigning Virtual Machine Contributor directly on the Lock 7 virtual machine grants restart and related compute actions on that one canal asset only, which is the least-privilege answer when night shift must open a single lock without touching every other VM in the subscription. Inheritance flows downward, so a narrow resource-scoped assignment does not expand into sibling locks or unrelated canal workloads.
Assigning Virtual Machine Contributor at the subscription fails by concept because every child resource inherits that role, recreating last week’s over-broad grant across the entire waterway. Assigning Owner at the management group fails even more severely: Owner includes full resource control plus the ability to create role assignments across all subscriptions under that group, far beyond a restart. Assigning Contributor at the resource group and relying on Azure Policy to “block other VMs” fails because Policy evaluates compliance and can deny certain writes, but it is not a substitute for choosing the correct RBAC scope; Contributor at RG scope still authorizes broad resource changes on every resource in that group.
Exam caveat: AZ-500 expects you to distinguish scope selection from role selection—picking Virtual Machine Contributor at the wrong scope is still a least-privilege failure. Operational check: after assigning at the VM resource, verify Effective access / Access control (IAM) on Lock 7 shows the principal, confirm a sibling lock VM does not list the same assignment via inheritance, and have night shift restart only Lock 7 successfully.