
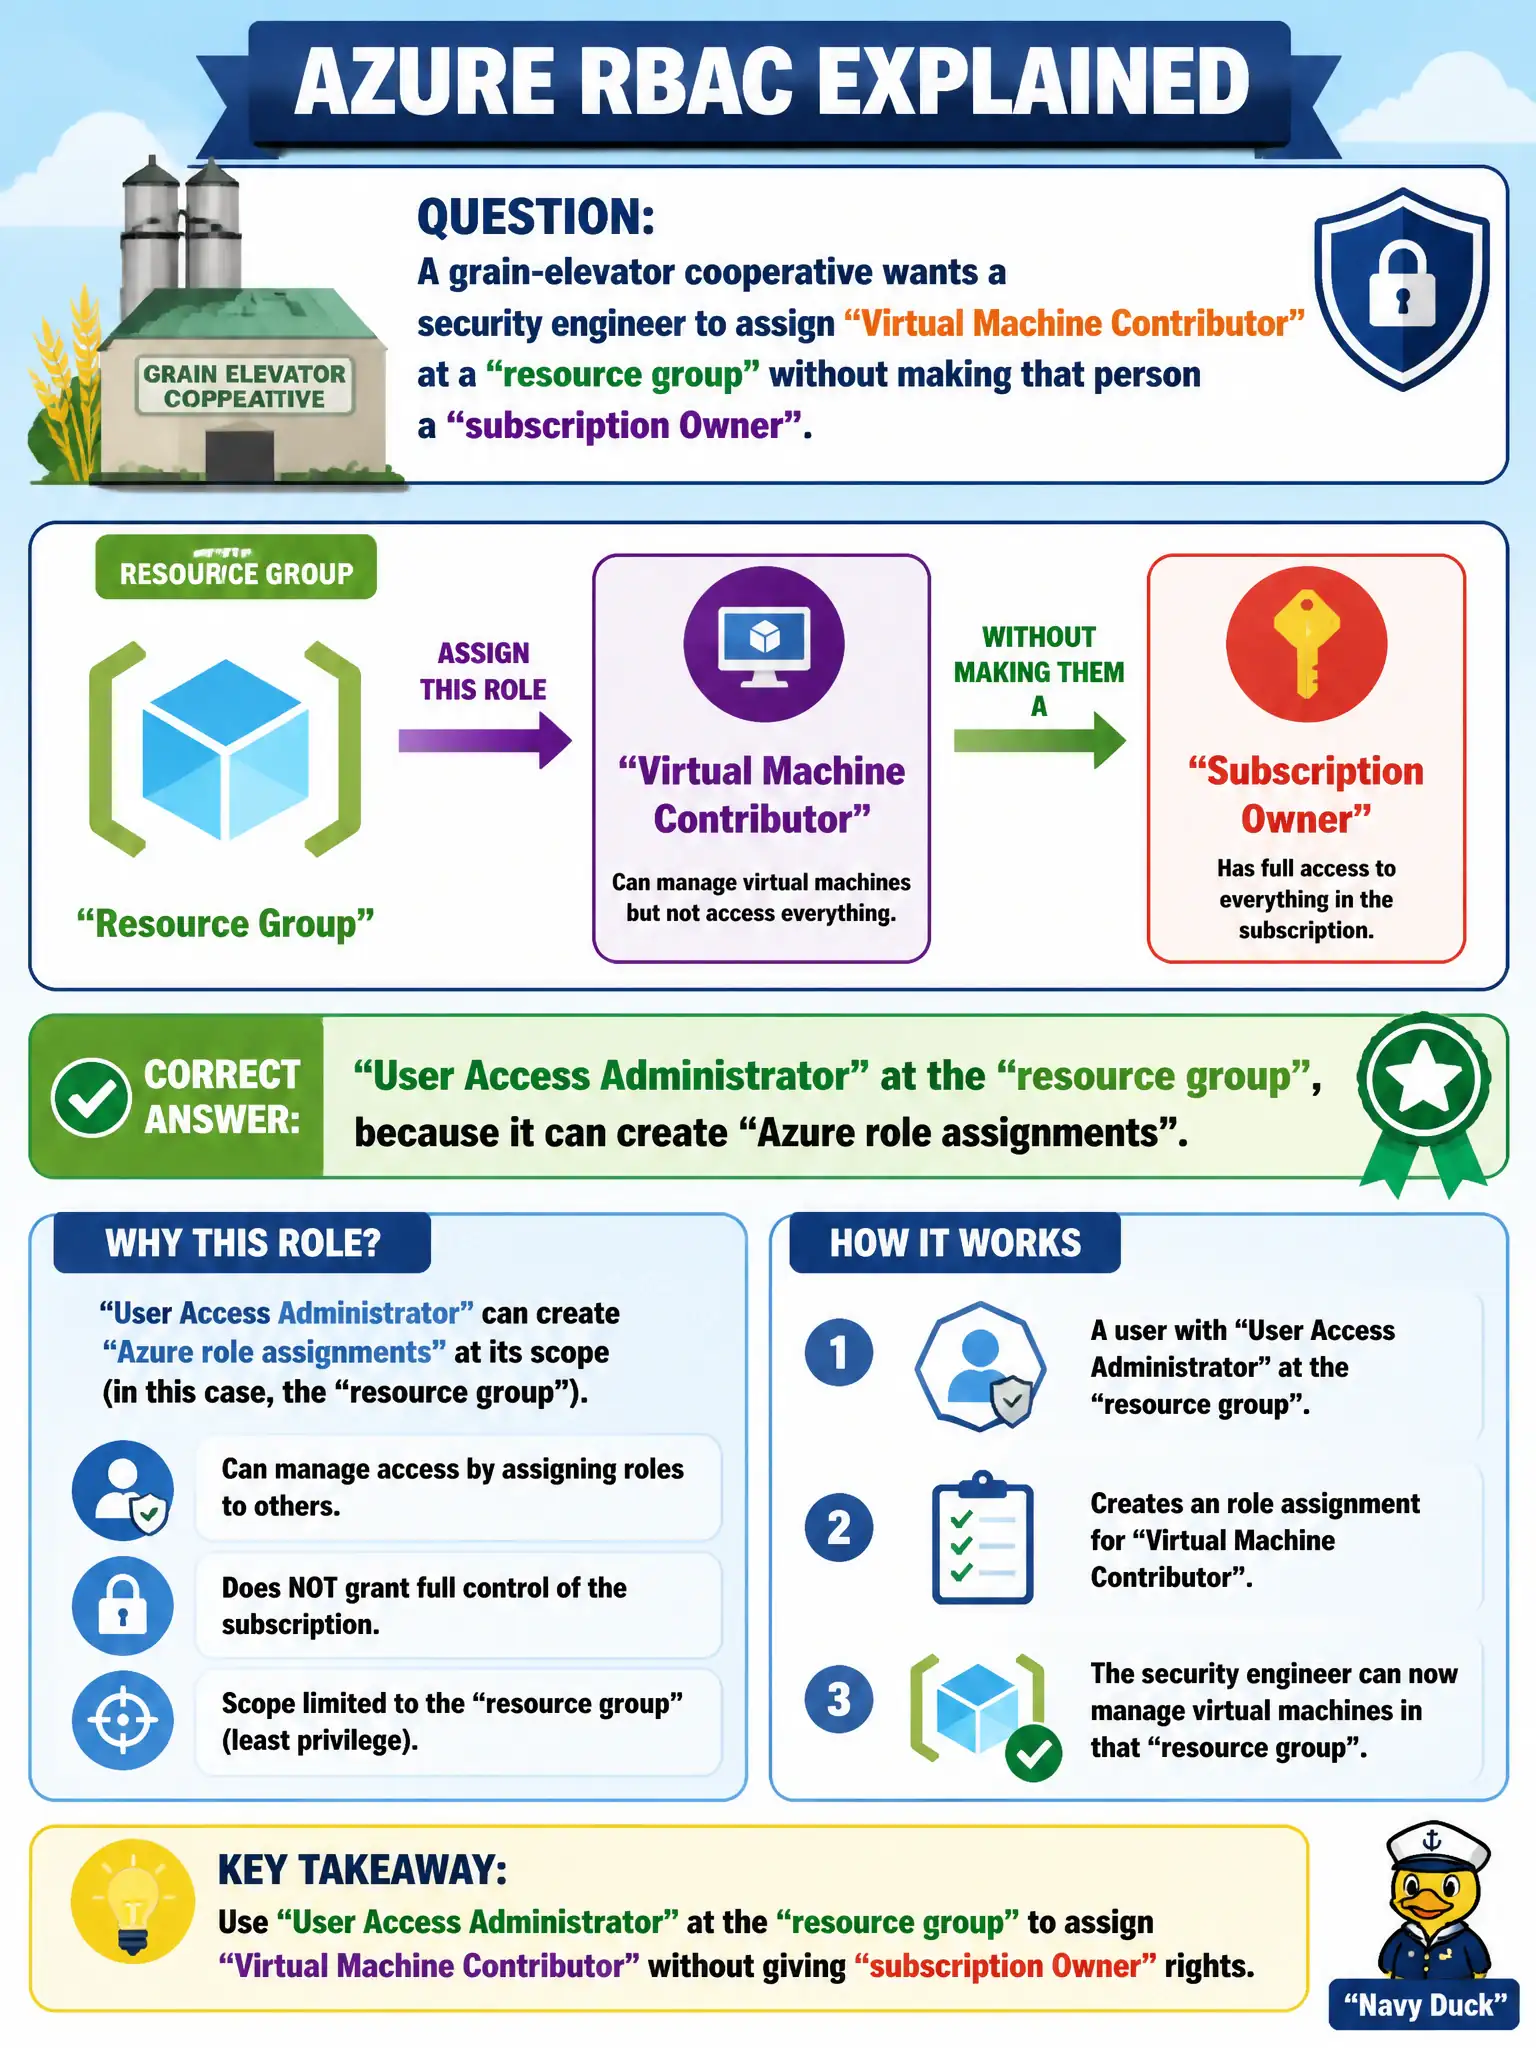
A grain-elevator cooperative wants a security engineer to assign Virtual Machine Contributor at a resource group without making that person a subscription Owner. Which built-in Azure role can create that role assignment?
Select an answer to reveal the explanation.
Short Explanation
Contributor can wrench on resources all day and still cannot hand out badges. User Access Administrator (or Owner, or Role Based Access Control Administrator) is the badge printer—assign that at the resource group so the engineer can grant Virtual Machine Contributor without becoming subscription Owner.
Full Explanation
Creating Azure role assignments requires Microsoft.Authorization/roleAssignments/write (or equivalent elevated authorization rights). User Access Administrator at the resource group includes those authorization actions without granting full Owner on every resource, so a security engineer can assign Virtual Machine Contributor at that resource group for the grain-elevator cooperative without becoming a subscription Owner. That separates “who may manage access” from “who may manage all workloads.”
Contributor at the resource group fails by concept: Contributor can manage resources but explicitly does not include role-assignment permissions, so the engineer still cannot create the Virtual Machine Contributor assignment. Virtual Machine Contributor at the subscription fails because that job-function role manages compute resources; it does not authorize delegating roles to others. Security Reader at the management group fails because Security Reader is a read-oriented security posture role for recommendations and findings—it does not grant the authorization write actions needed to create Azure RBAC assignments.
Exam caveat: remember the classic trio—Owner and User Access Administrator (and custom roles with roleAssignments/write) can assign roles; Contributor cannot, despite sounding powerful. Operational check: grant User Access Administrator only at the target resource group, create the Virtual Machine Contributor assignment there, confirm the engineer cannot assign roles at subscription scope, and remove any temporary Owner grants used during testing.