
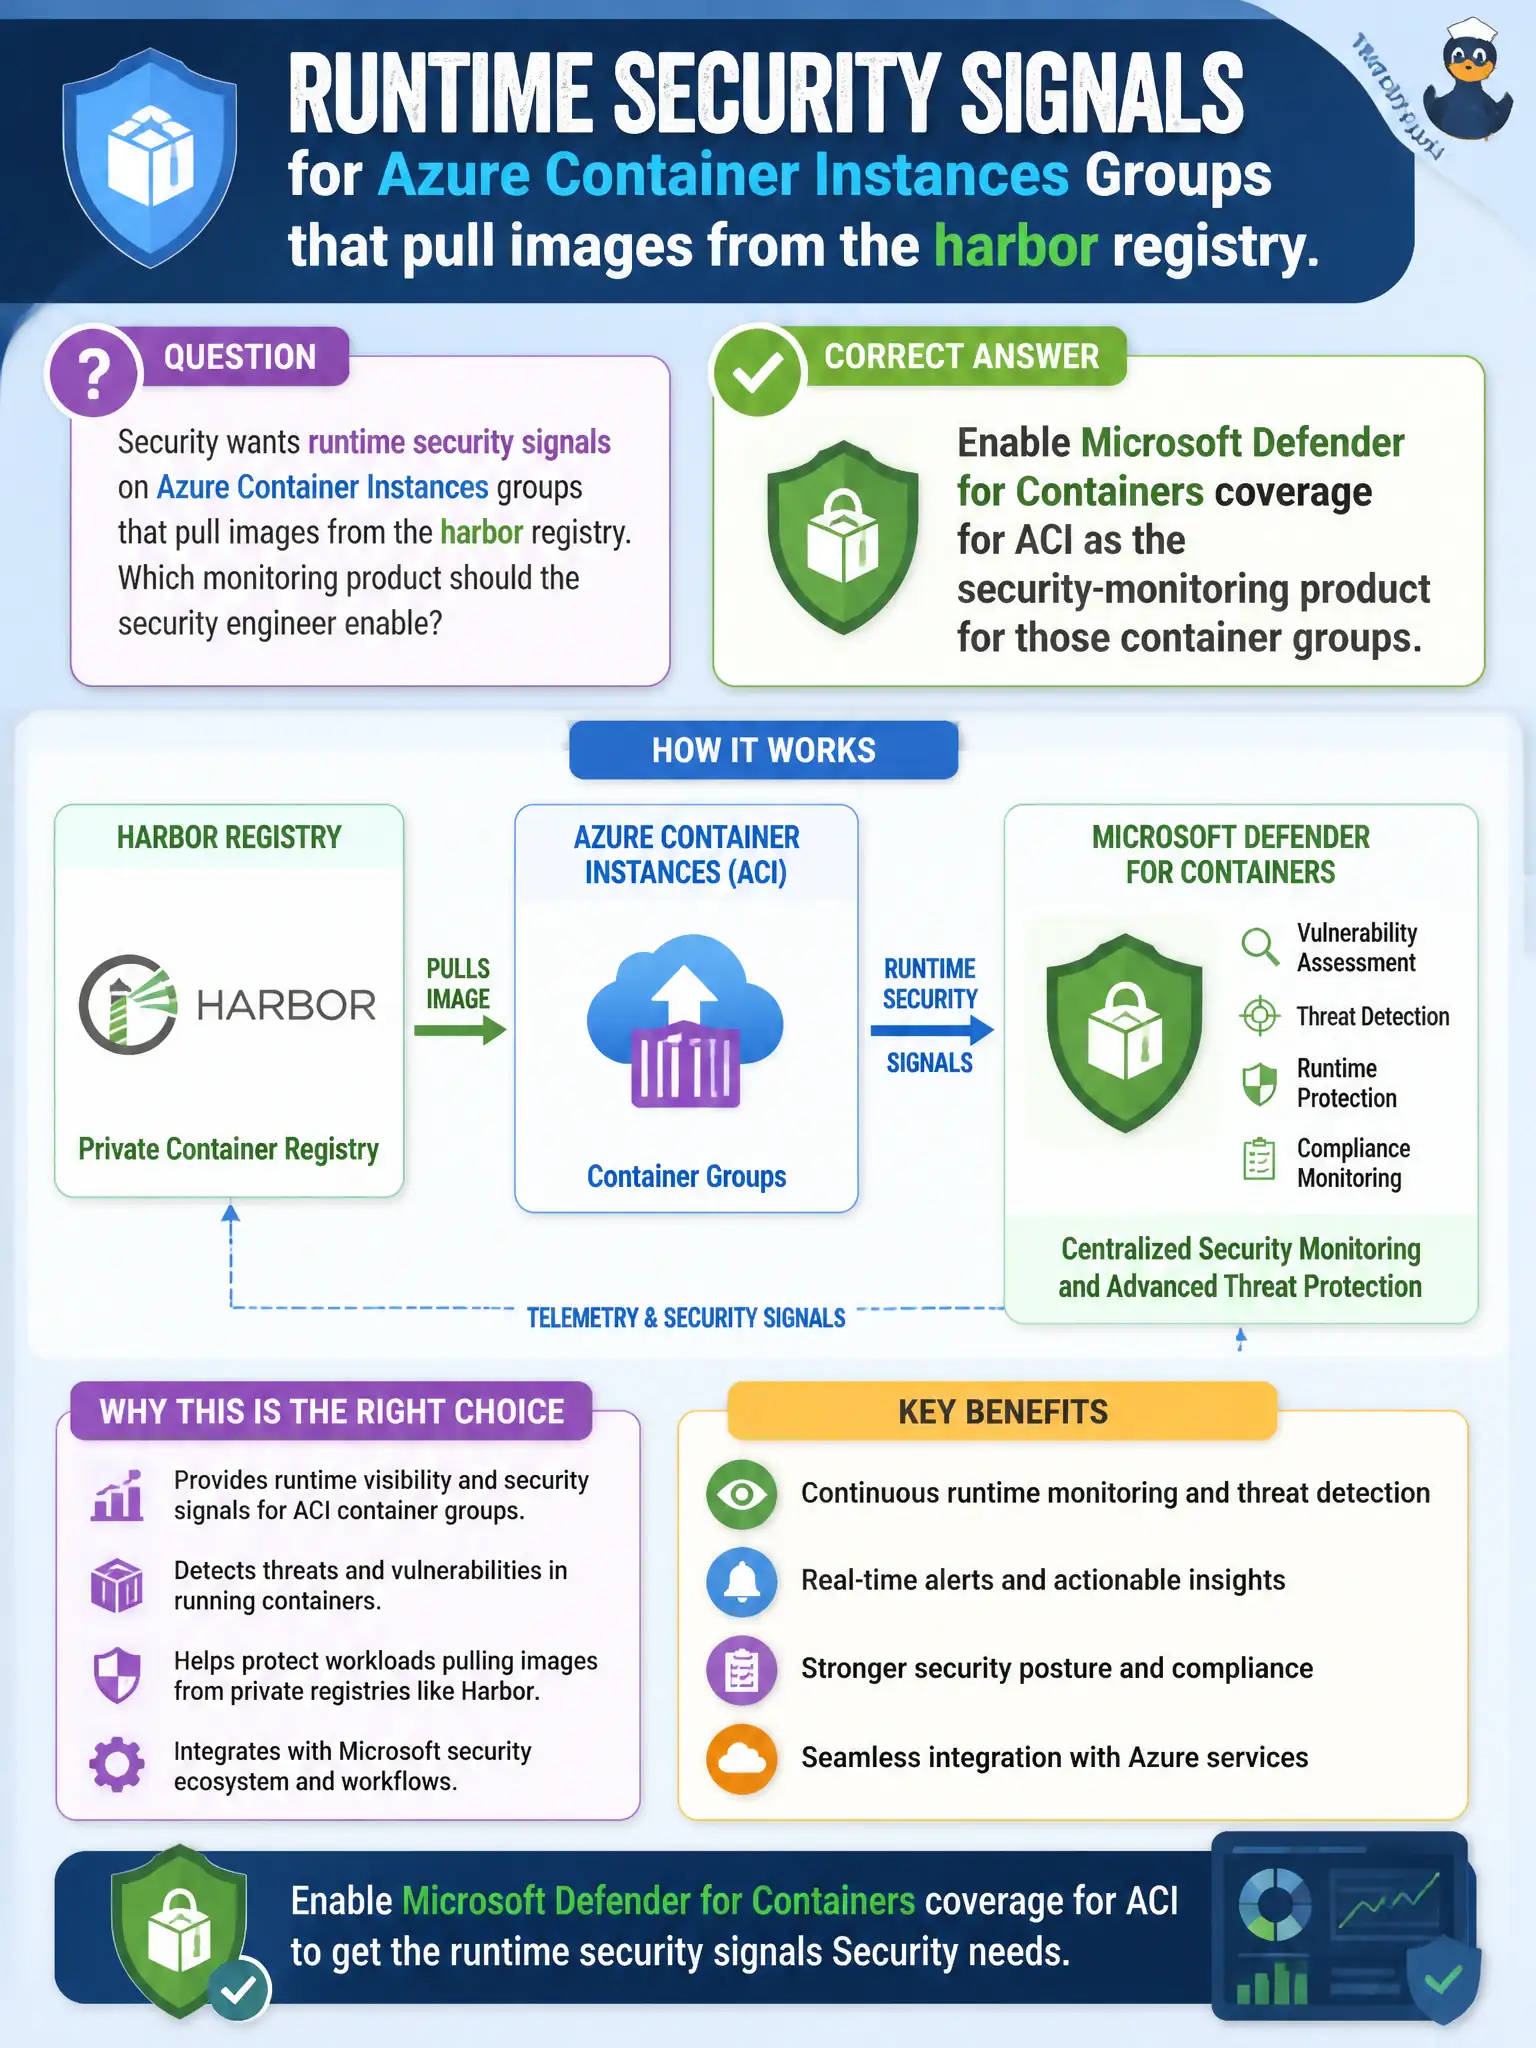
Security wants runtime security signals on Azure Container Instances groups that pull images from the harbor registry. Which monitoring product should the security engineer enable?
Select an answer to reveal the explanation.
Short Explanation
ACI pulling from the harbor registry still needs a security lookout. Turn on Defender for Containers for ACI—don’t pretend App Insights or a Servers plan on some VM covers those groups.
Full Explanation
Microsoft Defender for Containers coverage for Azure Container Instances is the security-monitoring product for ACI groups that pull images from the harbor registry. It supplies runtime security signals appropriate to those container groups rather than borrowing unrelated Defender plans or application-performance keys and calling that “ACI security monitoring.”
Enabling Defender for Servers catalog options on unrelated VMs fails by concept: Servers coverage on virtual machines is not ACI container security monitoring and does not watch those container groups. Adding an Application Insights instrumentation key to each ACI YAML as the primary security-monitoring control confuses application telemetry with Defender security signals. Authorizing only ACR admin credentials in ACI registry password fields and skipping runtime monitoring addresses pull authentication poorly and still leaves no runtime security product on the groups.
Exam caveat: Defender for Containers spans AKS and other container offerings including ACI where supported—enable the plan that actually covers the ACI resource type you run, not only Servers elsewhere in the subscription. Operational check: confirm Defender for Containers is enabled for the scope hosting the ACI groups, verify recommendations or alerts can surface for those groups, and move pulls off ACR admin passwords toward identity-based registry access.