
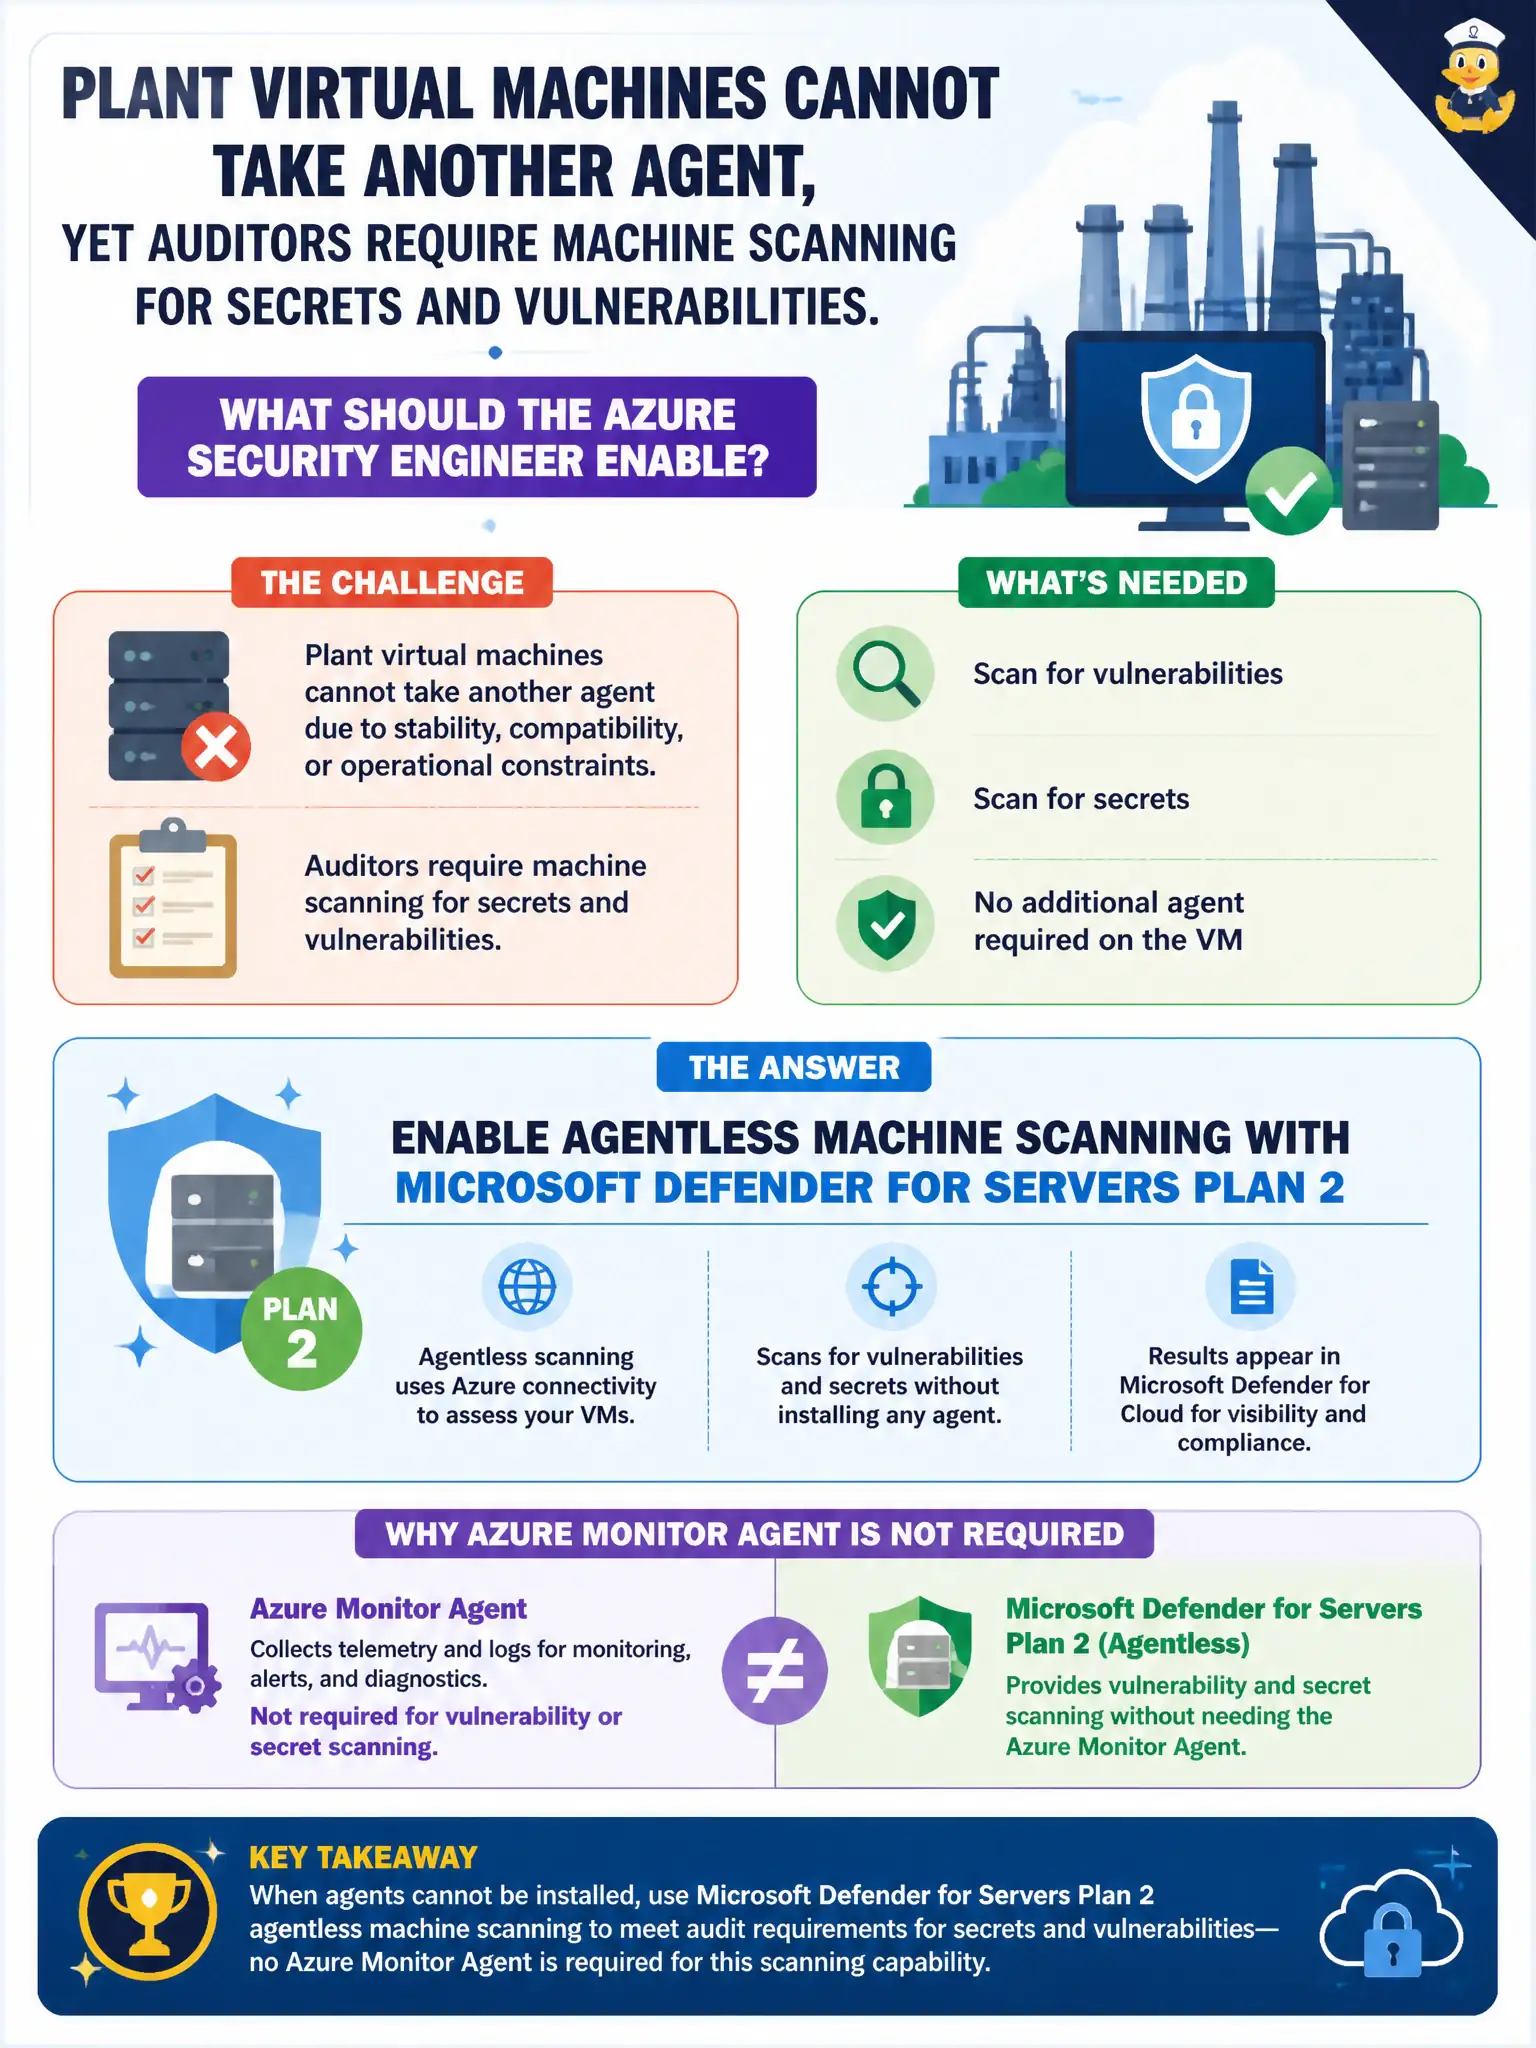
Plant virtual machines cannot take another agent, yet auditors require machine scanning for secrets and vulnerabilities. What should the Azure security engineer enable?
Select an answer to reveal the explanation.
Short Explanation
No room for another agent on the plant boxes? Plan 2 agentless scanning snapshots the disks—AMA is not the ticket for that feature. That’s the path when the guest can’t take more weight.
Full Explanation
Plant virtual machines that cannot take another agent still need machine scanning for secrets and vulnerabilities. Enable agentless machine scanning with Microsoft Defender for Servers Plan 2; Azure Monitor Agent is not required for that scan feature. Snapshot-based agentless analysis is the supported path when the guest cannot accept more agent weight.
Requiring only Azure Monitor Agent on every guest because agentless scanning supposedly does not exist on Plan 2 contradicts Plan 2’s agentless capability. Choosing Microsoft Defender for Servers Plan 1 exclusively for agentless disk snapshot scanning of secrets selects the wrong tier for that agentless feature set. Declaring a guest Qualys agent as the only supported path to agentless results invents a mandatory third-party agent where agentless Plan 2 scanning is the point.
Exam caveat: agentless scanning prerequisites and supported disks still apply; “agentless” means AMA is not required for that feature—it does not mean every powered-off or unsupported disk is scanned.
Operational check: enable Defender for Servers Plan 2 with agentless scanning for the plant machines, confirm AMA is not installed solely for this feature, and verify secrets and vulnerability results appear from agentless analysis for supported running machines.