
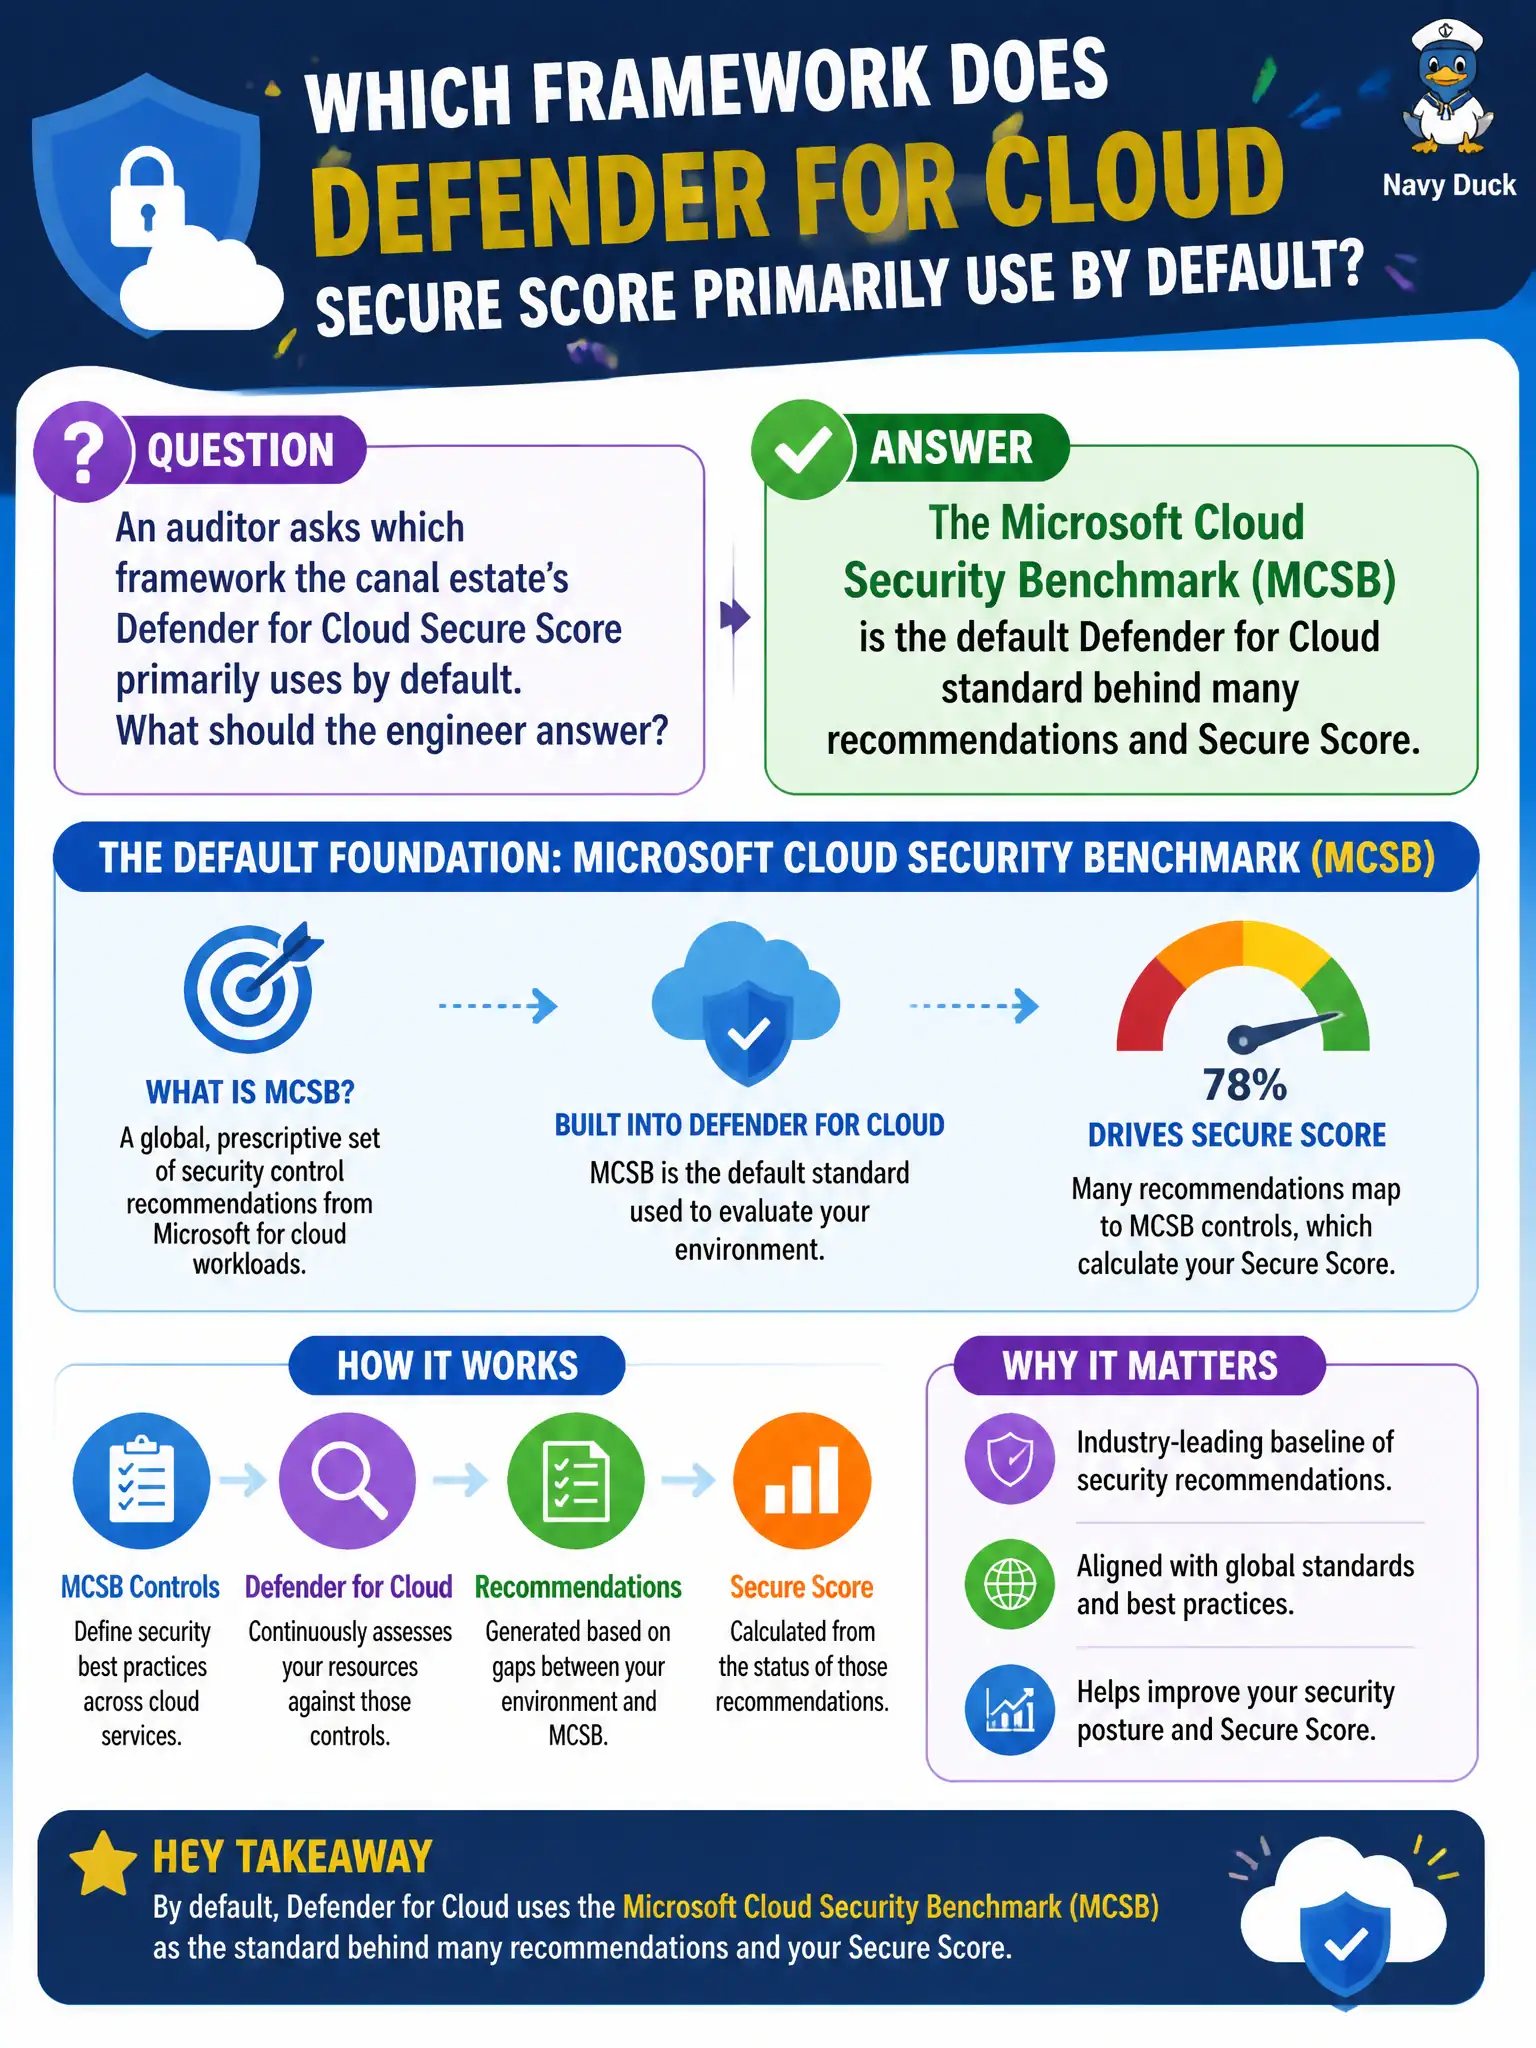
An auditor asks which framework the canal estate’s Defender for Cloud Secure Score primarily uses by default. What should the engineer answer?
Select an answer to reveal the explanation.
Short Explanation
When they ask “which rulebook is the score graded on,” the default answer is the Microsoft Cloud Security Benchmark—MCSB—not PCI-only, not Sentinel KQL, and not Azure Advisor’s cost tips.
Full Explanation
By default, many Microsoft Defender for Cloud recommendations and Secure Score calculations align to the Microsoft Cloud Security Benchmark (MCSB). When an auditor asks which framework the canal estate's Secure Score primarily uses by default, MCSB is the accurate answer—not a payment-card-only or Sentinel-driven model.
Claiming only PCI-DSS drives Secure Score while MCSB applies solely to AWS connectors is wrong on both counts: Secure Score is not PCI-exclusive, and MCSB is central to Azure posture as well as multi-cloud guidance. Saying Secure Score is driven exclusively by custom KQL analytics rules in Microsoft Sentinel confuses SOC detection engineering with CSPM scoring. Asserting Secure Score has no framework and is a random sample of Azure Advisor cost tips mixes cost optimization tips with security posture recommendations.
Exam caveat: you can enable additional regulatory standards (CIS, ISO, PCI, HIPAA, and others) for compliance dashboards; those complement MCSB reporting and do not redefine Secure Score as "PCI-only."
Operational check: open Defender for Cloud regulatory compliance / security standards for the canal subscriptions, confirm MCSB is present as the default posture standard, and show the auditor how Secure Score recommendations map to MCSB controls.