
An operator opens a Microsoft Sentinel incident for every Secure Score recommendation on the lock-lab subscription. What is the correct distinction?
Select an answer to reveal the explanation.
Short Explanation
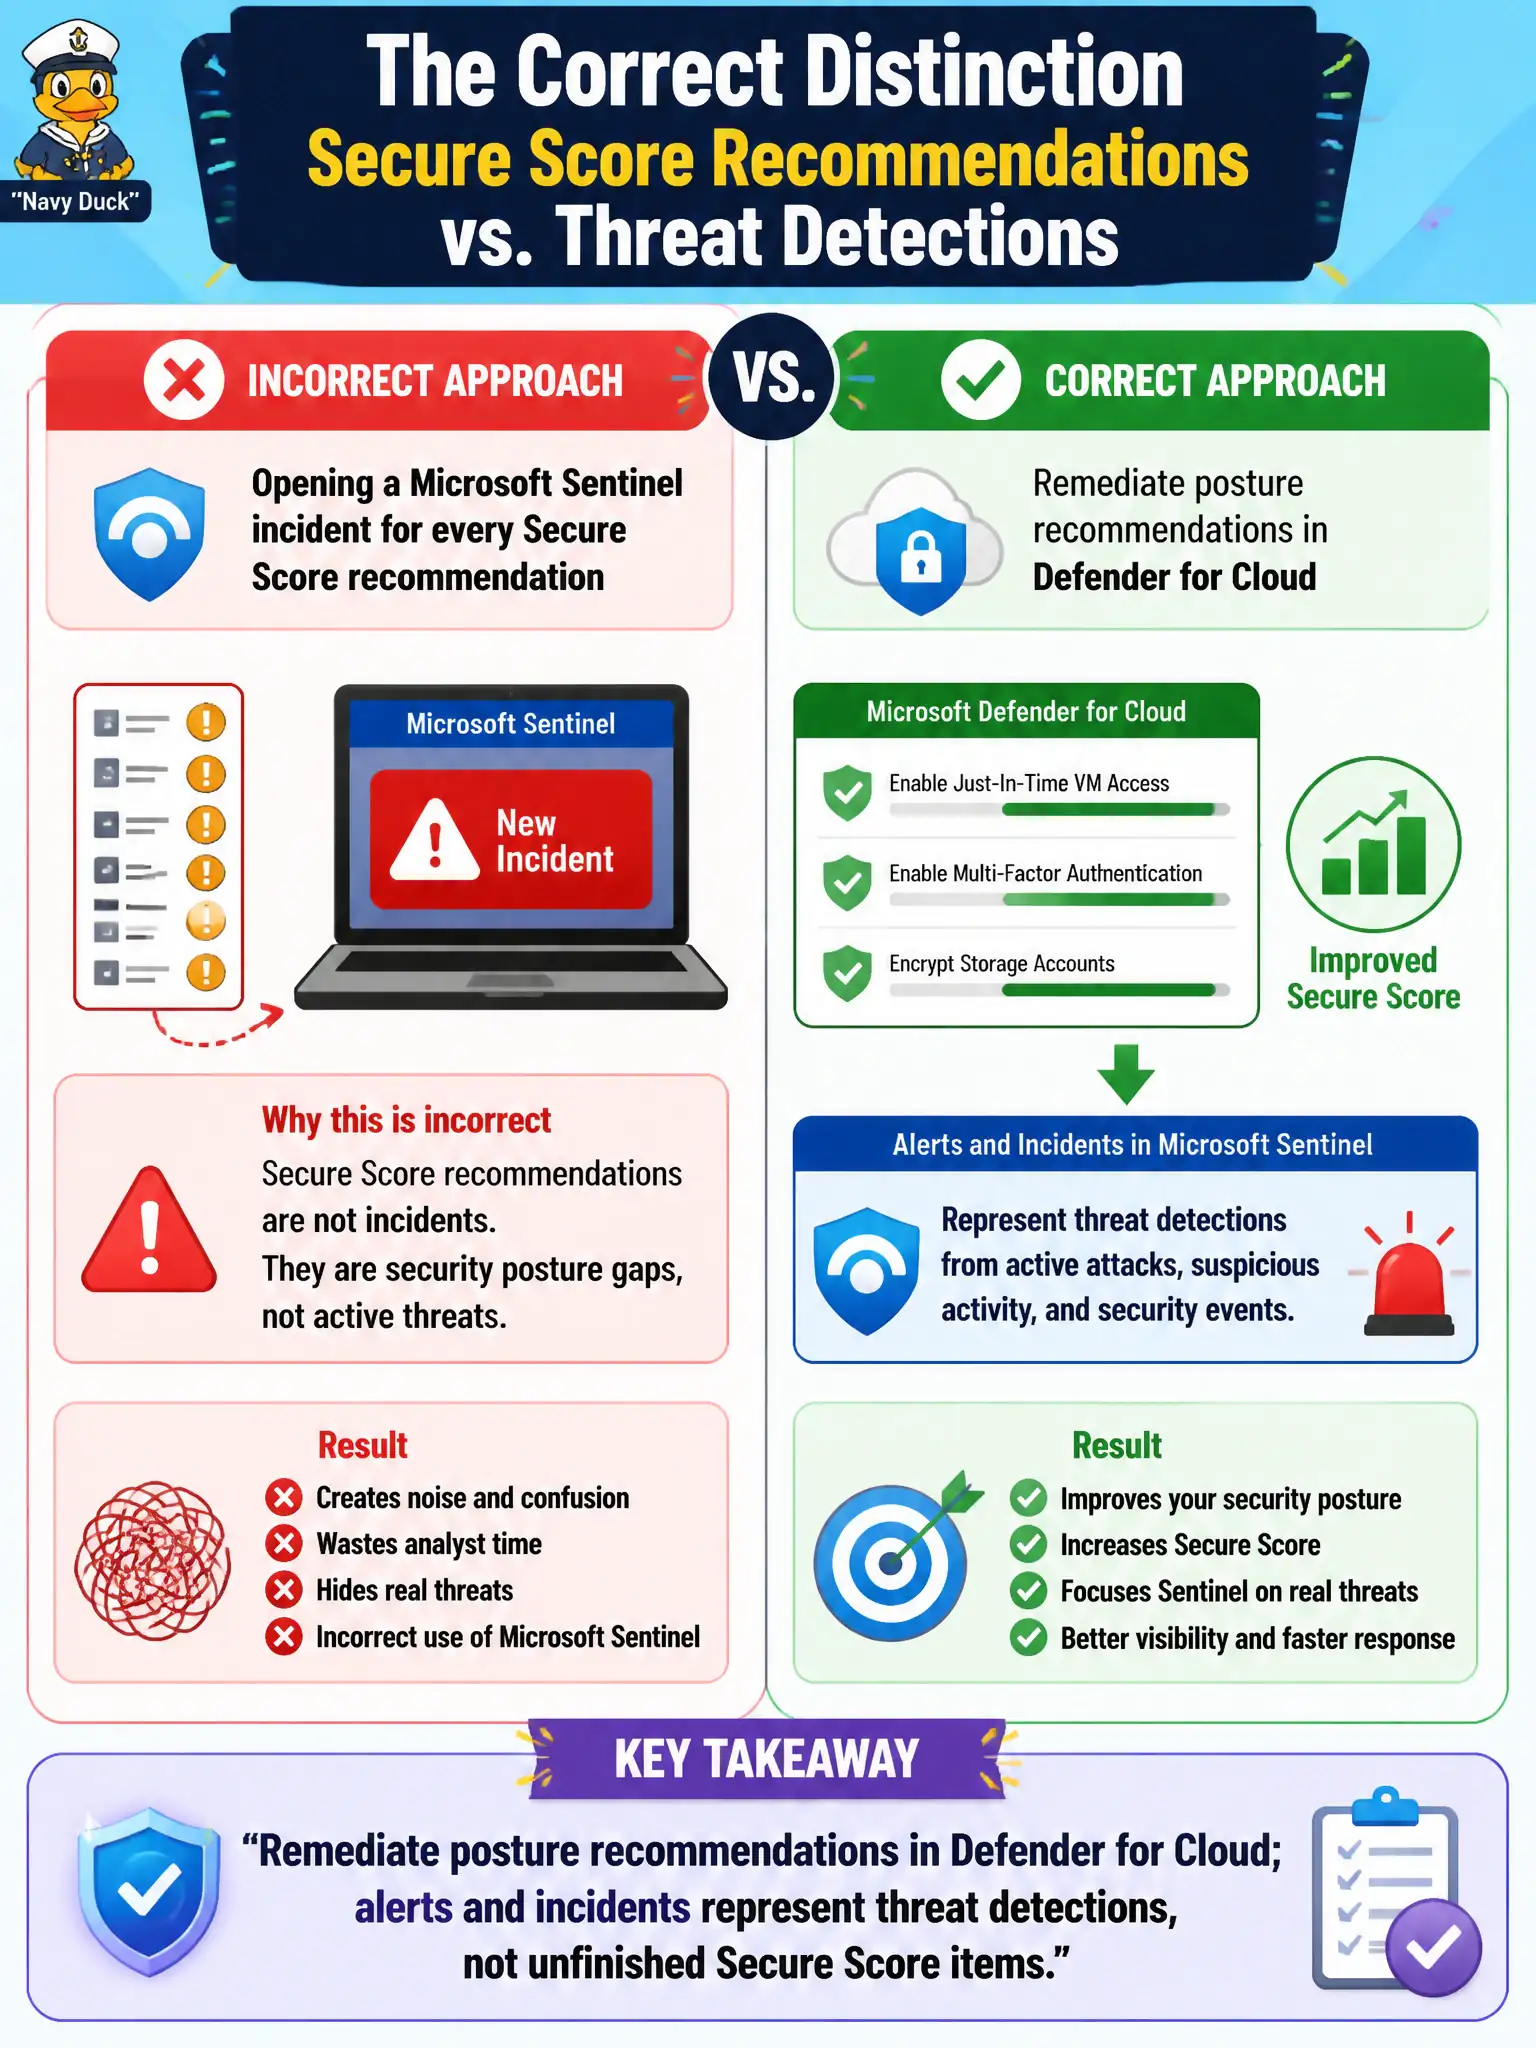
A recommendation is homework on the Secure Score report card. An alert or incident is the siren that something hostile might be happening—do not dump the homework pile into the SOC queue.
Full Explanation
Posture recommendations that drive Secure Score are remediation tasks in Microsoft Defender for Cloud; Microsoft Sentinel alerts and incidents represent threat detections and investigations. Opening a Sentinel incident for every Secure Score recommendation on the lock-lab subscription collapses two different workflows and floods the SOC with unfinished homework instead of hostile activity.
Treating every Secure Score recommendation as an automatic high-severity Sentinel incident by design is incorrect—recommendations are not incidents and severity models differ. Saying recommendations and alerts are identical with only the portal blade name different erases the posture-versus-threat distinction AZ-500 expects. Ignoring posture recommendations until an ISO auditor files a finding delays hardening and leaves Secure Score debt unaddressed between audits.
Exam caveat: some Defender for Cloud security alerts can be forwarded or triaged alongside Sentinel, but that integration path is still about detections—not bulk conversion of every Secure Score recommendation into an incident.
Operational check: keep recommendation remediation in Defender for Cloud (owners, due dates, exemptions), ensure Sentinel incidents map to analytics rules/alert products, and sample the lock-lab incident queue to confirm it is not filled with Secure Score line items.