
A brokerage keeps AWS Config exceptions on a spreadsheet and wants the same rules evaluated in every account. What should they deploy?
Select an answer to reveal the explanation.
Short Explanation
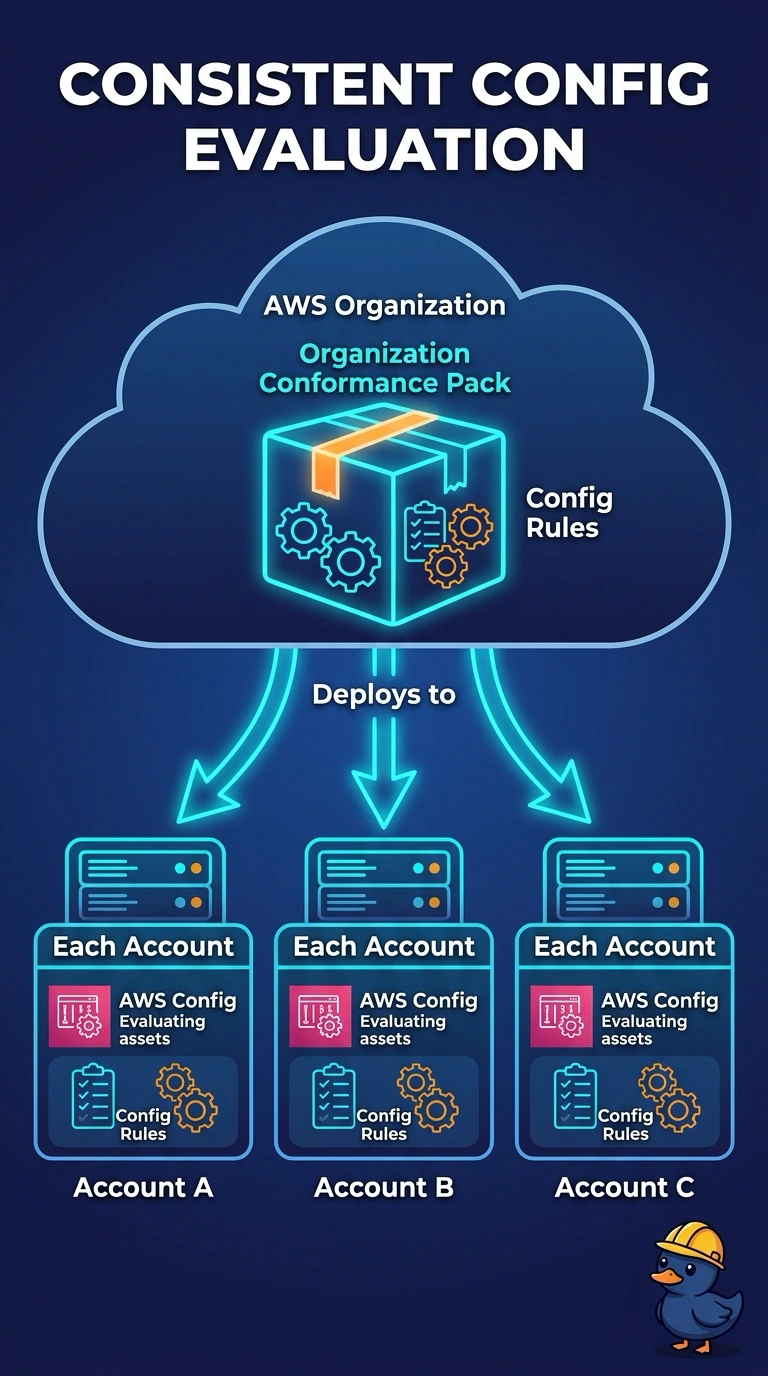
A spreadsheet is a diary, and a diary does not walk the building checking the locks. You want the same AWS Config rules evaluated in every account, and an organization conformance pack is what deploys that set. A deny policy or a single rule in one account does not do that job.
Full Explanation
An organization conformance pack packages AWS Config rules, and any remediation you attach, and deploys that package across accounts in the organization. Each account then evaluates its own resources and reports compliance, which is the evaluation a spreadsheet never performs. Config has to be recording in those member accounts, or the pack has no resource data to evaluate. A shared sheet can list exceptions and cannot detect a newly public bucket or an opened security group. One Config rule in a single account evaluates only that account, and a note to copy results does not create the rule anywhere else. A service control policy can deny an API at request time, and it is not a Config rule and does not evaluate resources that already exist. Caveat: the pack reports compliance and can start remediation you configured, and it does not by itself deny the API call the way a policy would. Operational check: after deployment, open a member account and confirm the pack's rules are present there and showing a compliance state, not only listed in the management account.