
A bank's EC2 Image Builder pipeline must download packages and reach Image Builder service endpoints without a path to the public internet. The build subnet is private. What should the network team add?
Select an answer to reveal the explanation.
Short Explanation
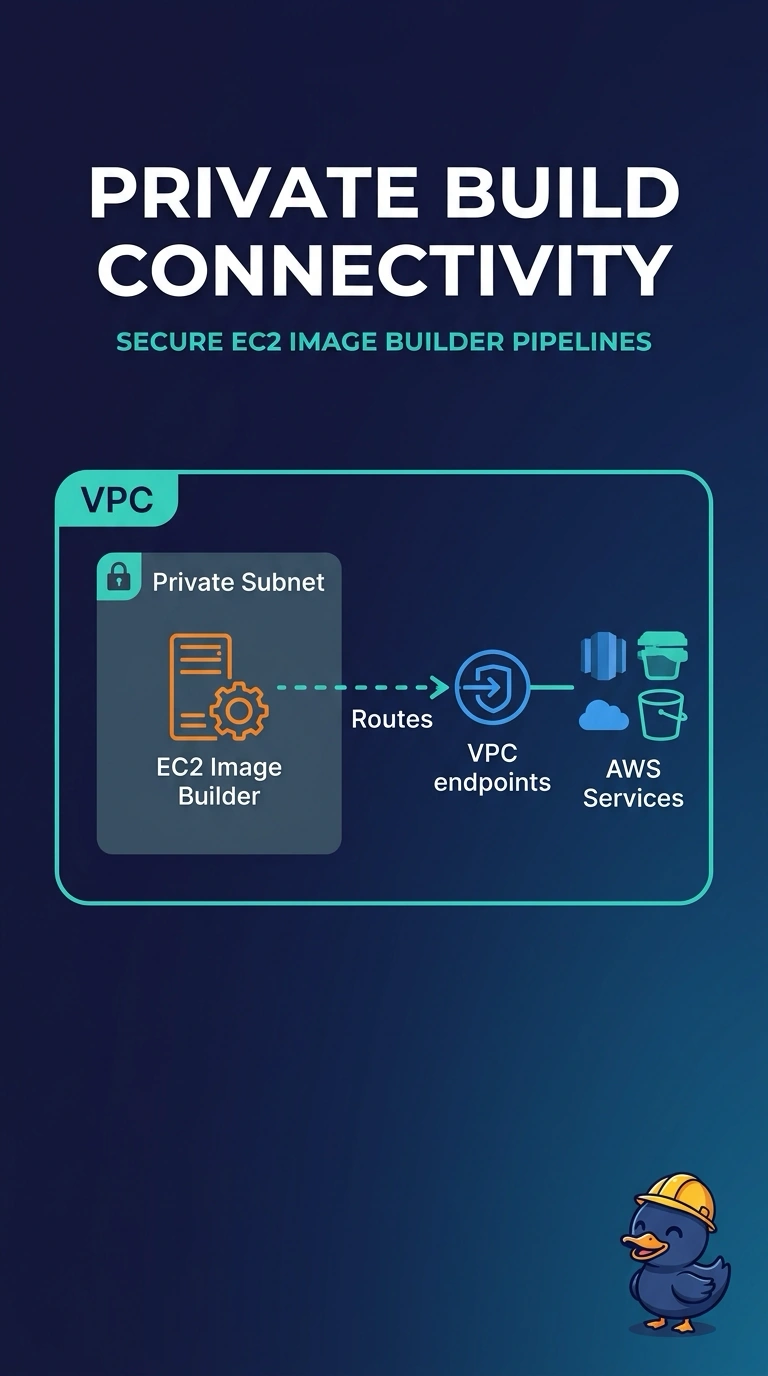
The build needs to talk to AWS, not to the whole internet. You give the private subnet VPC endpoints for the services the pipeline calls, and you route that traffic at the endpoints. A public address on the builder is the path the bank said not to open.
Full Explanation
A private build subnet can call AWS APIs through VPC endpoints, with routes that send that service traffic to the endpoints, and never needs a path onto the public internet. That is what lets the pipeline download its packages and reach the Image Builder service endpoints under the bank's constraint. A public IPv4 address plus a default route to an internet gateway is the public path the requirement rules out. A peering connection does not attach a VPC to the public internet, so it does not create the API path either. An inbound security group rule for port 80 from anywhere does not give the build instance a route to the service endpoints. Caveat: each endpoint's security group still has to allow the build instance, and the instance has to call the endpoint names, or the pipeline still fails with the endpoints in place. Operational check: with no default route to an internet gateway, run the pipeline and confirm the build reaches Image Builder and its package source through the endpoints.