
A regulated fintech operates 40 AWS accounts under AWS Organizations with a dedicated log archive account. Auditors require immutable API history for all Regions, centralized storage, and tamper detection. Which CloudTrail design should the security engineer deploy to meet centralized organization logging?
Select an answer to reveal the explanation.
Short Explanation
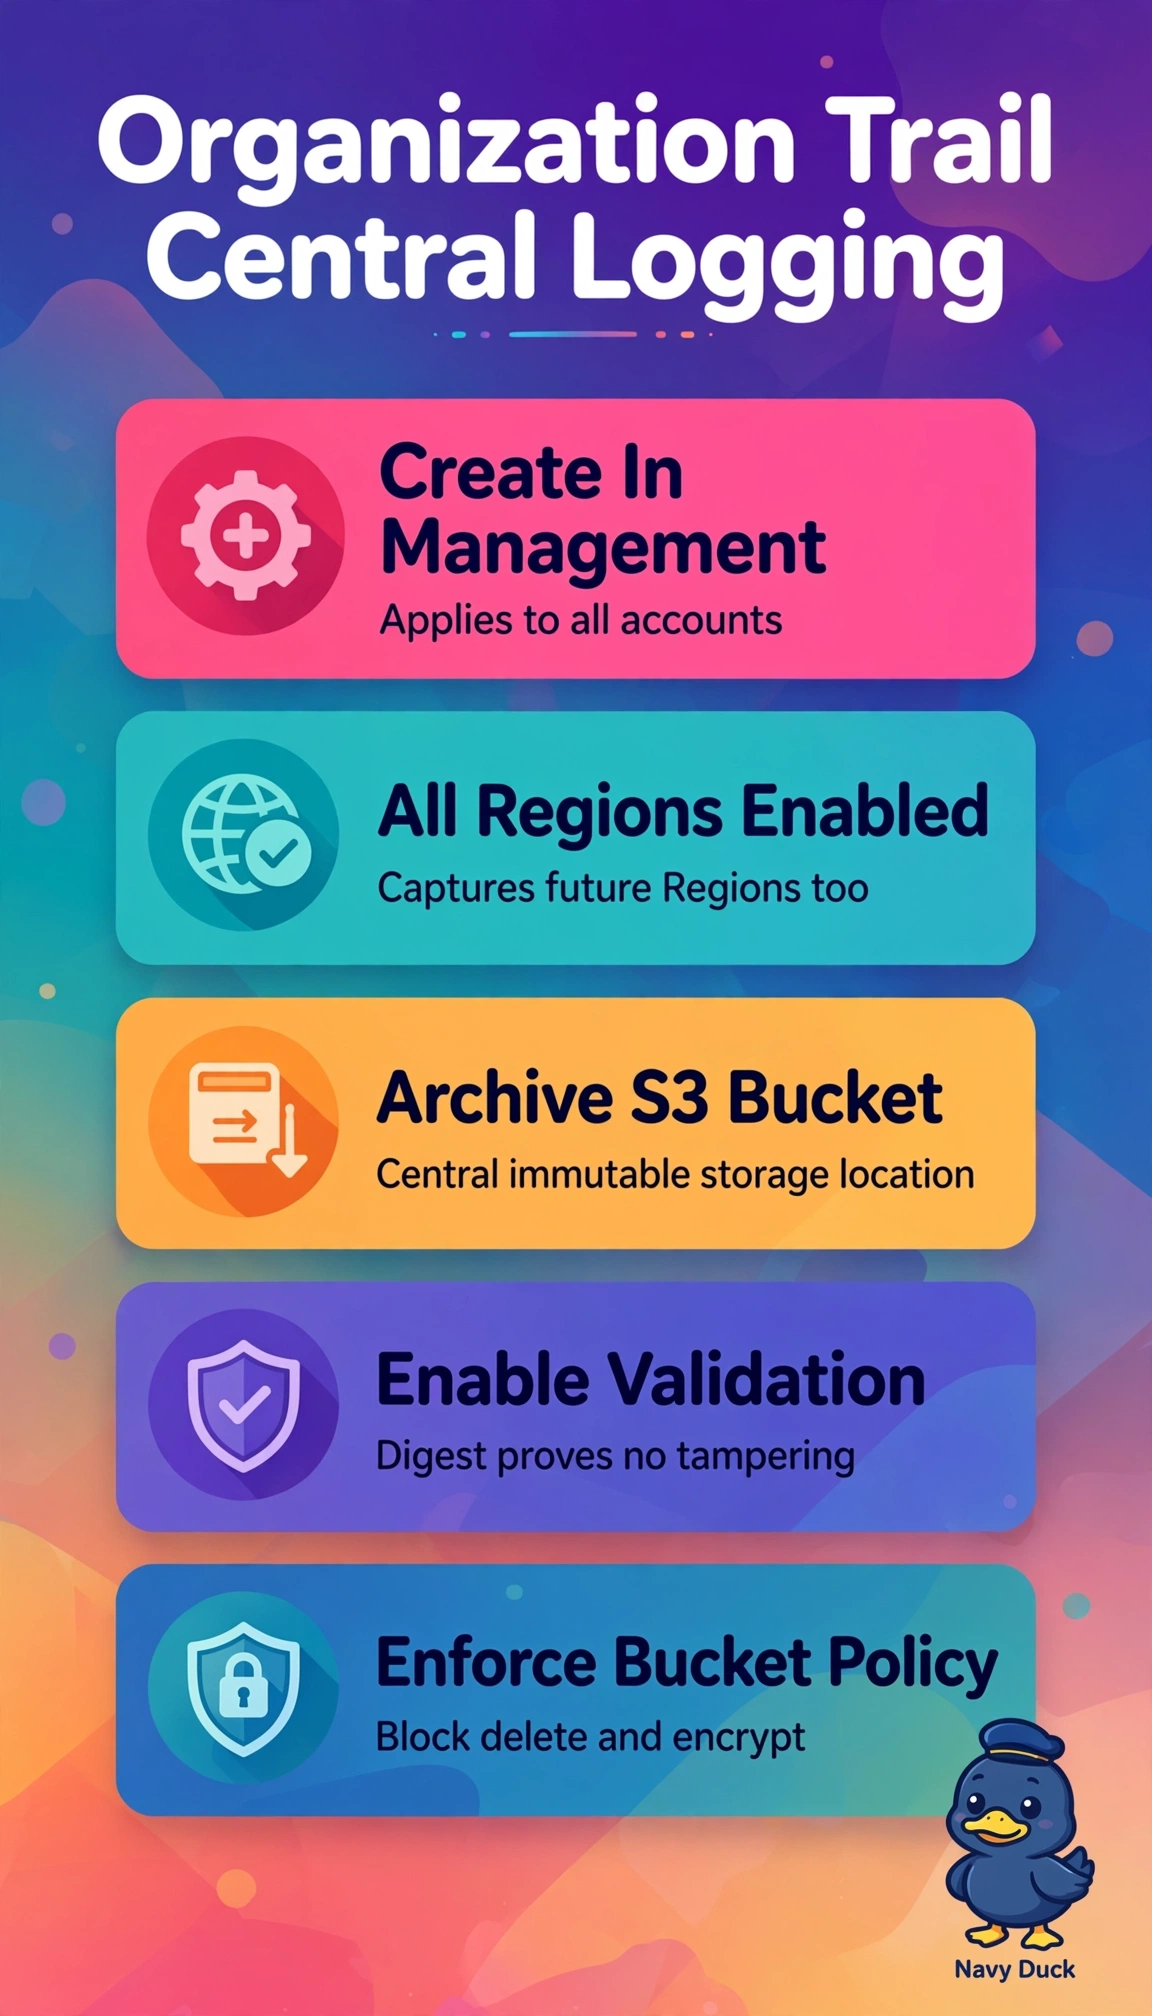
You're building one tamper-proof ledger for the whole company. Organization trails act like a central security camera covering every account and Region automatically.
Full Explanation
An organization trail created from the management or delegated administrator account automatically applies to all current and future member accounts and Regions, centralizing management activity in one S3 bucket in the log archive account, and enabling log file validation provides digest files that let you detect tampering. Account-level trails in each member account satisfy most centralization goals but miss the requirement for automatic coverage and single control because new accounts and Regions require manual setup and local buckets fragment storage. CloudTrail Insights with CloudWatch Logs only provides anomaly detection and short-term searchable logs but fails immutability and tamper detection because CloudWatch Logs alone lacks S3 Object Lock and log file validation digests. An organization trail in a member account without validation centralizes partially but misses governance and tamper detection because only the management account can create a true organization trail and disabled validation removes cryptographic integrity proof, plus auditors will flag it. Exam caveat: remember organization trails must originate from management or delegated admin, and always verify S3 bucket policy plus SSE-KMS and Object Lock for immutability.