
A retail company discovers an S3 bucket allows public reads due to an overly broad bucket policy and IAM role trust drift. The security team must find all unintended cross-account and public grants across IAM, S3, and KMS. Which service should the team use to investigate and correct the excessive privileges?
Select an answer to reveal the explanation.
Short Explanation
Overly generous policies are embarrassing but fixable. Analyzer flags what's actually exposed externally so you can tighten to least-privilege quickly.
Full Explanation
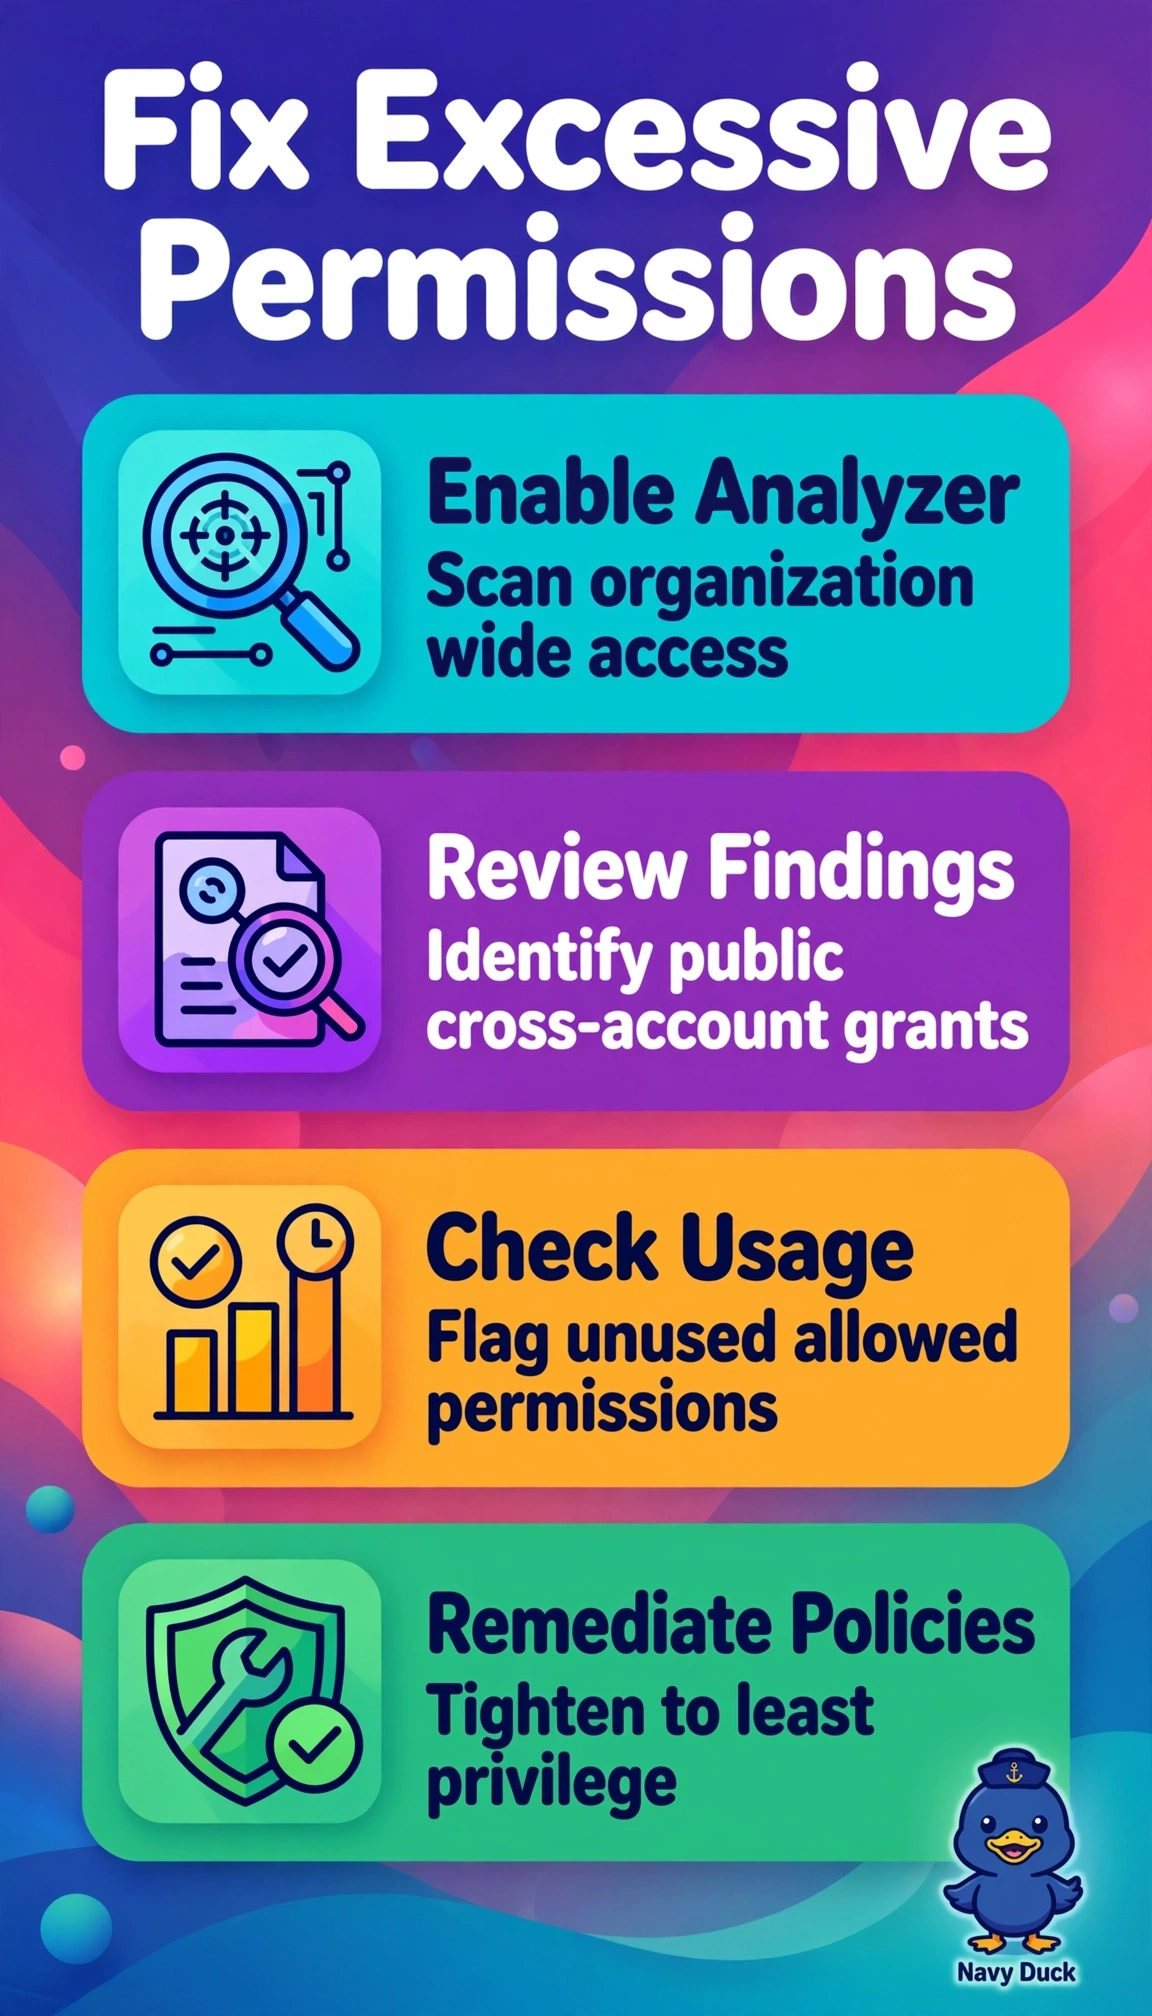
IAM Access Analyzer analyzes resource policies, trust policies, and IAM grants to identify external and public access, and unused access analysis highlights excessive permissions, enabling targeted policy tightening for S3, KMS, and IAM roles in one workflow. IAM Policy Simulator tests whether a specific principal can perform an action but does not inventory all public or cross-account exposure across services, so it cannot discover drift at scale. CloudTrail Insights detects unusual API activity patterns for operational anomalies but does not analyze policy effective permissions nor rewrite policies automatically. Amazon GuardDuty provides threat detection findings from logs and behavior, not comprehensive permission enumeration or policy remediation guidance. On the exam, select Access Analyzer for finding unintended access versus Simulator for testing a known call, and in practice enable organization-wide analyzer, archive intentional findings, and create EventBridge remediation for new public findings.