
A logistics firm with shared transit gateway and Route 53 Resolver sees data exfiltration via DNS tunneling and lateral movement between VPCs, but has only VPC flow logs centrally. Security wants hub-level visibility of routed inter-VPC traffic from the transit gateway itself rather than per-VPC logging. Which log-source design detects DNS tunneling and cross-VPC threats effectively?
Select an answer to reveal the explanation.
Short Explanation
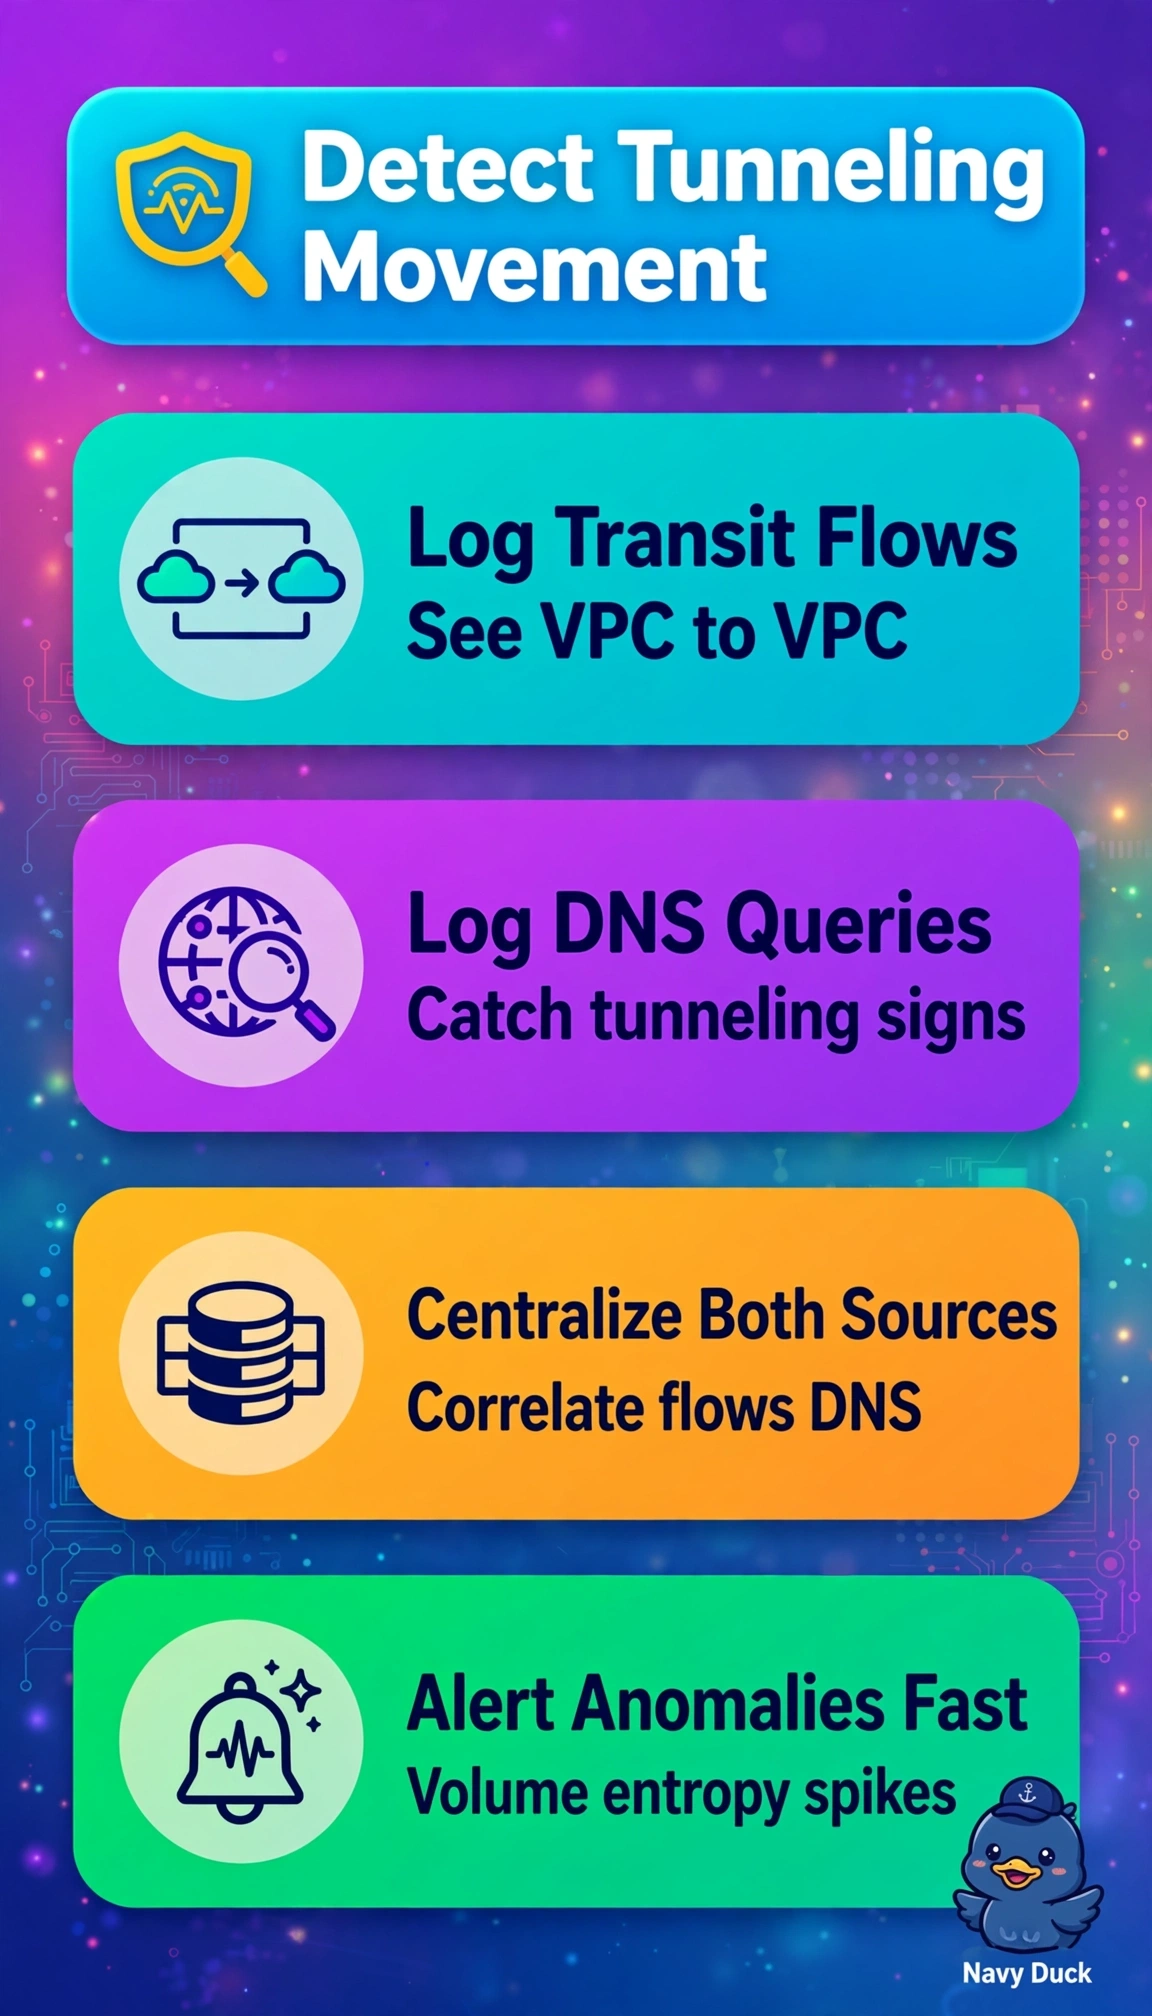
You're adding ears where the sneaky whispers travel. DNS plus transit logs expose tunneling queries and VPC-hopping flows that single VPC logs miss.
Full Explanation
The correct design succeeds because it pairs complementary telemetry at the shared transit choke point with central aggregation, providing both network and name-resolution visibility required for this threat model. Transit gateway flow logs give hub-level visibility into routed traffic between VPCs, which is essential for detecting lateral movement traversing the shared gateway that would be fragmented in per-interface logs, while Route 53 Resolver query logs expose queried names, volumes, and record types indicative of DNS tunneling that flow records with IPs and ports cannot reveal. Centralization enables correlation across accounts. By contrast, centralizing VPC flow logs with enhanced metadata is a standard method for east-west monitoring and lateral movement detection, yet it fails conceptually because flow records lack DNS query content and cannot distinguish tunneling from benign lookups. Forwarding Resolver logs centrally with analytics is also a widely used DNS security practice, but it fails because it provides no routed inter-VPC flow visibility and cannot trace movement through the transit gateway. Combining centralized VPC flow logs with Resolver logs is even closer and operationally common, but it still fails on the transit fact because only transit gateway flow logs natively capture transit-routed flows with gateway context, whereas VPC logs remain interface-centric and miss hub-level perspective. For exam precision, remember that VPC flow logs, transit gateway flow logs, and Resolver query logs are distinct sources and are not interchangeable despite overlapping network data. As a practical check, confirm both log types stream to a central data lake with normalized timestamps and validate with simulated tunneling queries plus cross-VPC scans to ensure both signals fire and correlate.