
A logistics company with 40 accounts needs weekly checks for public S3 buckets, unencrypted EBS volumes, and open security groups, auto-remediation for critical drifts, consolidated scores, and evidence for auditors. Which automation should the engineer deploy to perform regular assessments?
Select an answer to reveal the explanation.
Short Explanation
You need weekly report cards, not one-off spot checks across forty accounts. This continuous compliance combo grades everything like a strict teacher with auto detention slips.
Full Explanation
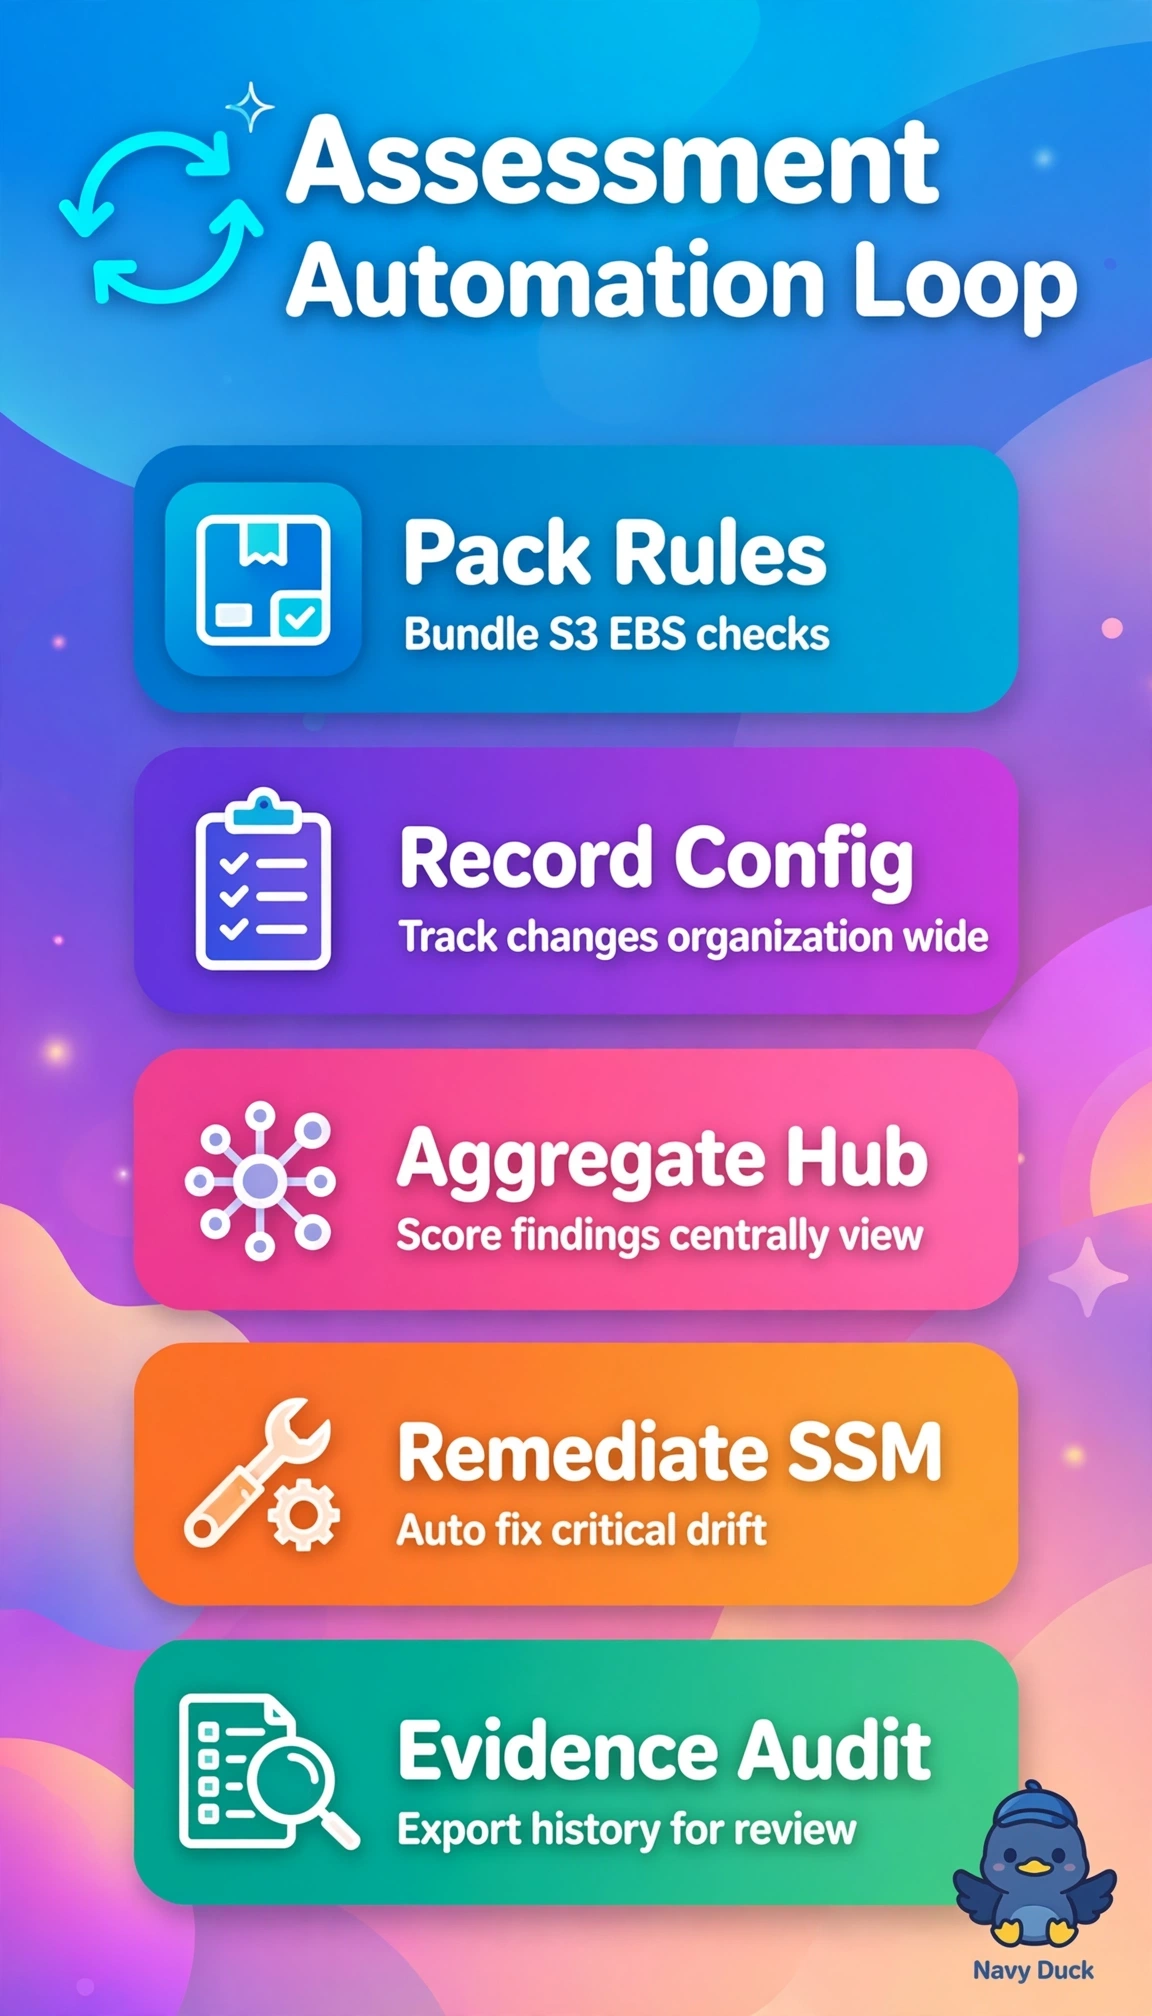
AWS Config conformance packs bundle managed rules for S3 public access, EBS encryption, and security group checks deployed via StackSets or Organizations, Security Hub aggregates findings into centralized compliance scores and dashboards, and Systems Manager Automation documents attached via Config remediation or Security Hub custom actions auto-remediate drift while preserving history for audit evidence. Inspector assesses EC2 and container vulnerabilities and exposures, not S3 bucket policies, EBS encryption configuration, or broad compliance scoring across services. CloudTrail Insights detects unusual API activity rather than evaluating configuration state against desired baselines, and manual review does not scale or provide scores and remediation. Custom Lambda inventory schedulers require maintaining code, rules, and reporting and lack managed rule coverage, centralized scoring, and native remediation integrations. For the exam, Config plus conformance packs equals configuration assessment while Security Hub equals aggregation, and in practice enable Config recording, verify pack deployment status, and test SSM remediation in nonproduction first.