
A SaaS team ships ECR container images weekly and runs Python Lambda functions processing payments. Leadership requires continuous known-vulnerability scanning for images and function code plus runtime threat detection for containers and functions, with AWS managing any agents. Which scanning control should the team implement for container and serverless compute security?
Select an answer to reveal the explanation.
Short Explanation
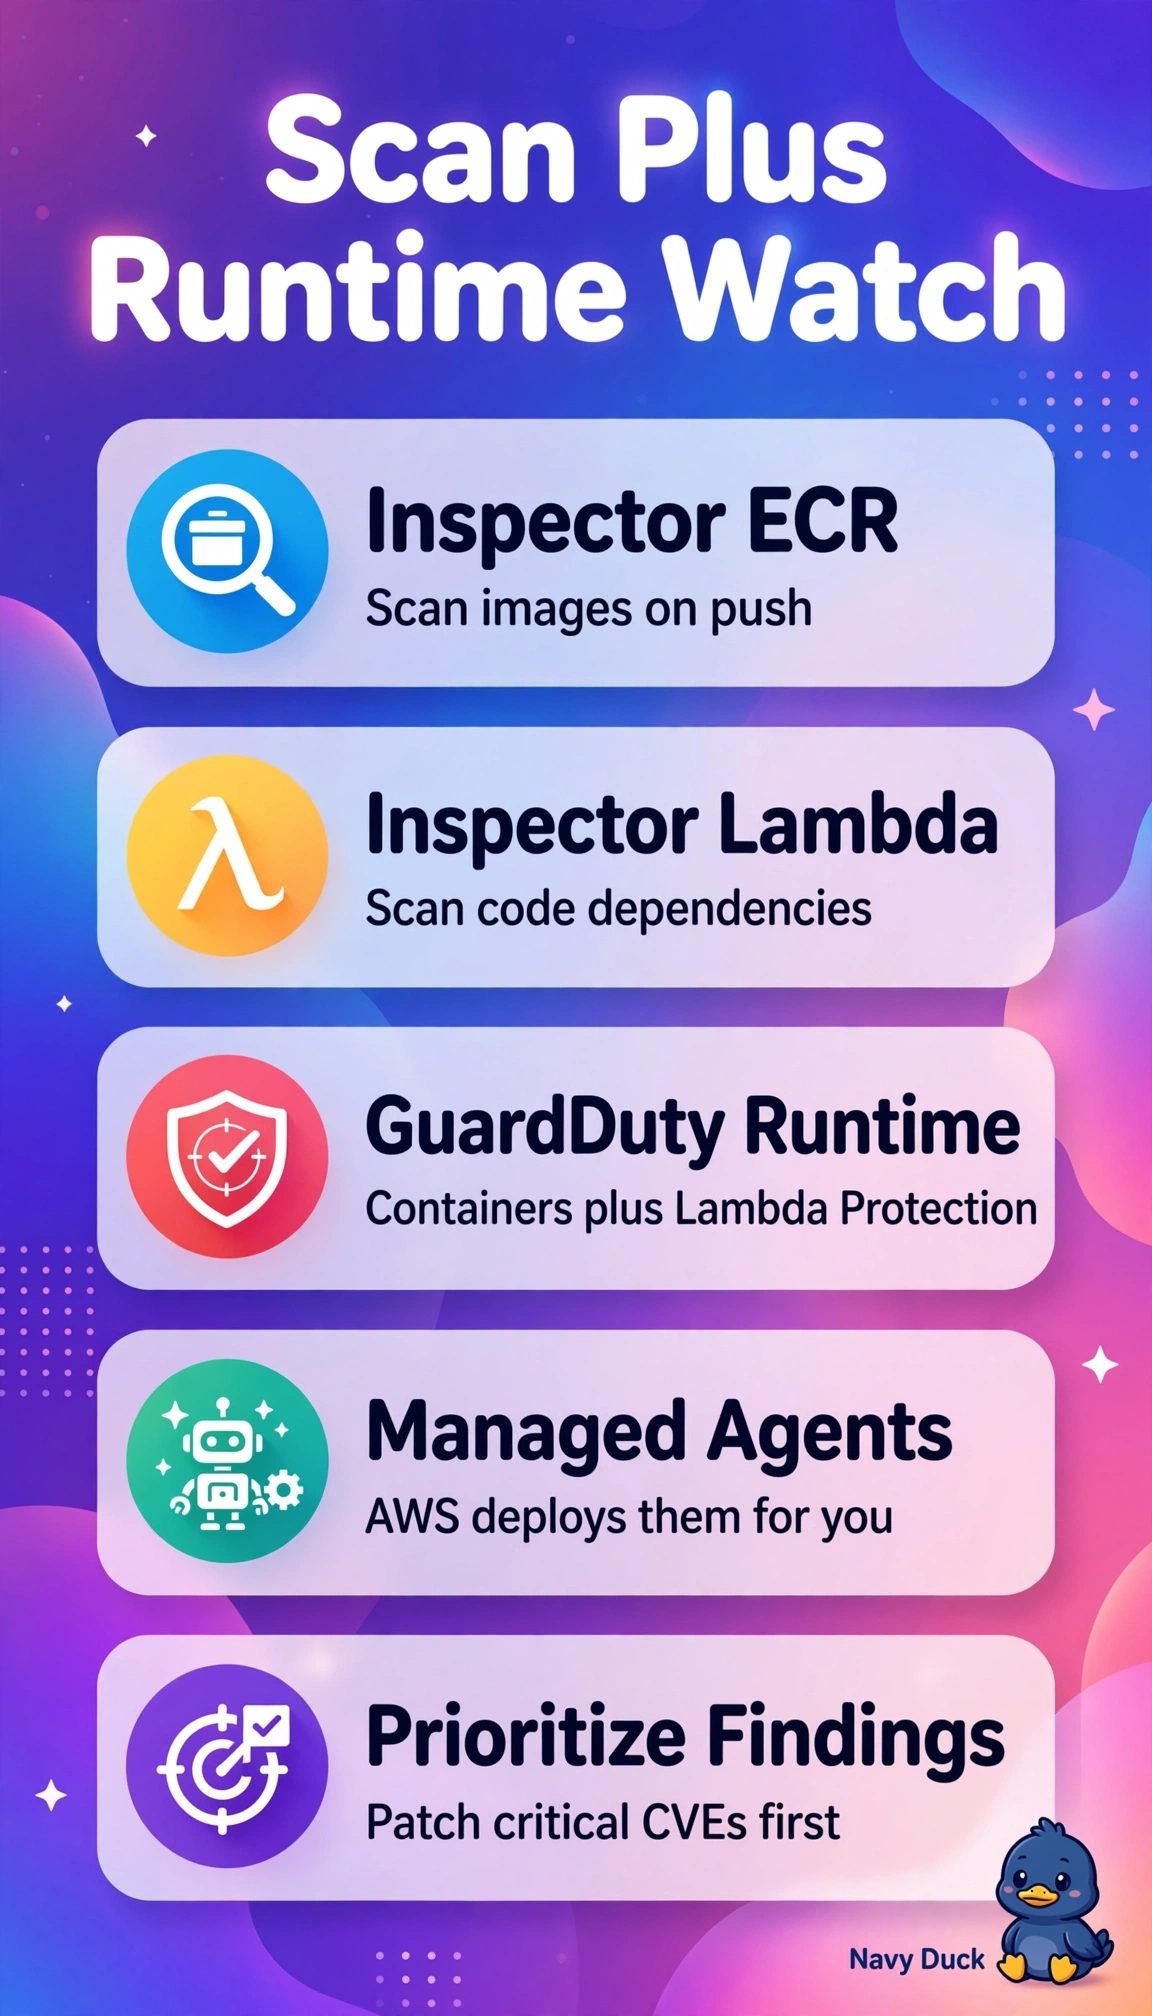
You're layering prevention and live watch together. Layering Inspector for build-time CVEs with GuardDuty for runtime behavior covers images and functions end to end.
Full Explanation
The correct control pairs continuous vulnerability assessment with managed runtime detection because Amazon Inspector provides automated CVE scanning for ECR image layers and Python Lambda code, while GuardDuty Runtime Monitoring with AWS-managed sensors covers ECS, Fargate and EKS and GuardDuty Lambda Protection analyzes function invocations and API activity for threats. One incorrect approach enables Inspector for both images and function code plus container runtime monitoring but omits Lambda Protection, leaving payment functions without serverless runtime detection despite otherwise complete coverage. Another incorrect approach combines continuous ECR scanning with both container and Lambda runtime protection but limits Inspector to images only, leaving Python dependencies and function packages unscanned for known vulnerabilities required by leadership. A third incorrect approach names the right services but requires manually installed and team-managed runtime agents, violating the AWS-managed requirement and creating overhead and gaps especially on Fargate and Lambda where self-management is impractical. Exam caveat: separate assessment from detection, as Inspector finds known weaknesses before exploitation and GuardDuty detects malicious behavior during execution, so scenarios demanding both need both services. Practical check: confirm Inspector enhanced ECR scanning and Lambda scanning are active, GuardDuty shows healthy runtime coverage for clusters, and Lambda Protection lists payment functions as protected with findings routed for remediation.