
GuardDuty reports cryptocurrency mining on an EC2 instance and Security Hub shows an associated IAM credential leak, but the owner claims both are test activity. Which validation workflow best assesses the true scope and impact of the security event?
Select an answer to reveal the explanation.
Short Explanation
Alerts tell you where smoke might be, but you still check the rooms. Validation by pivoting to raw logs and snapshots proves real scope before you act.
Full Explanation
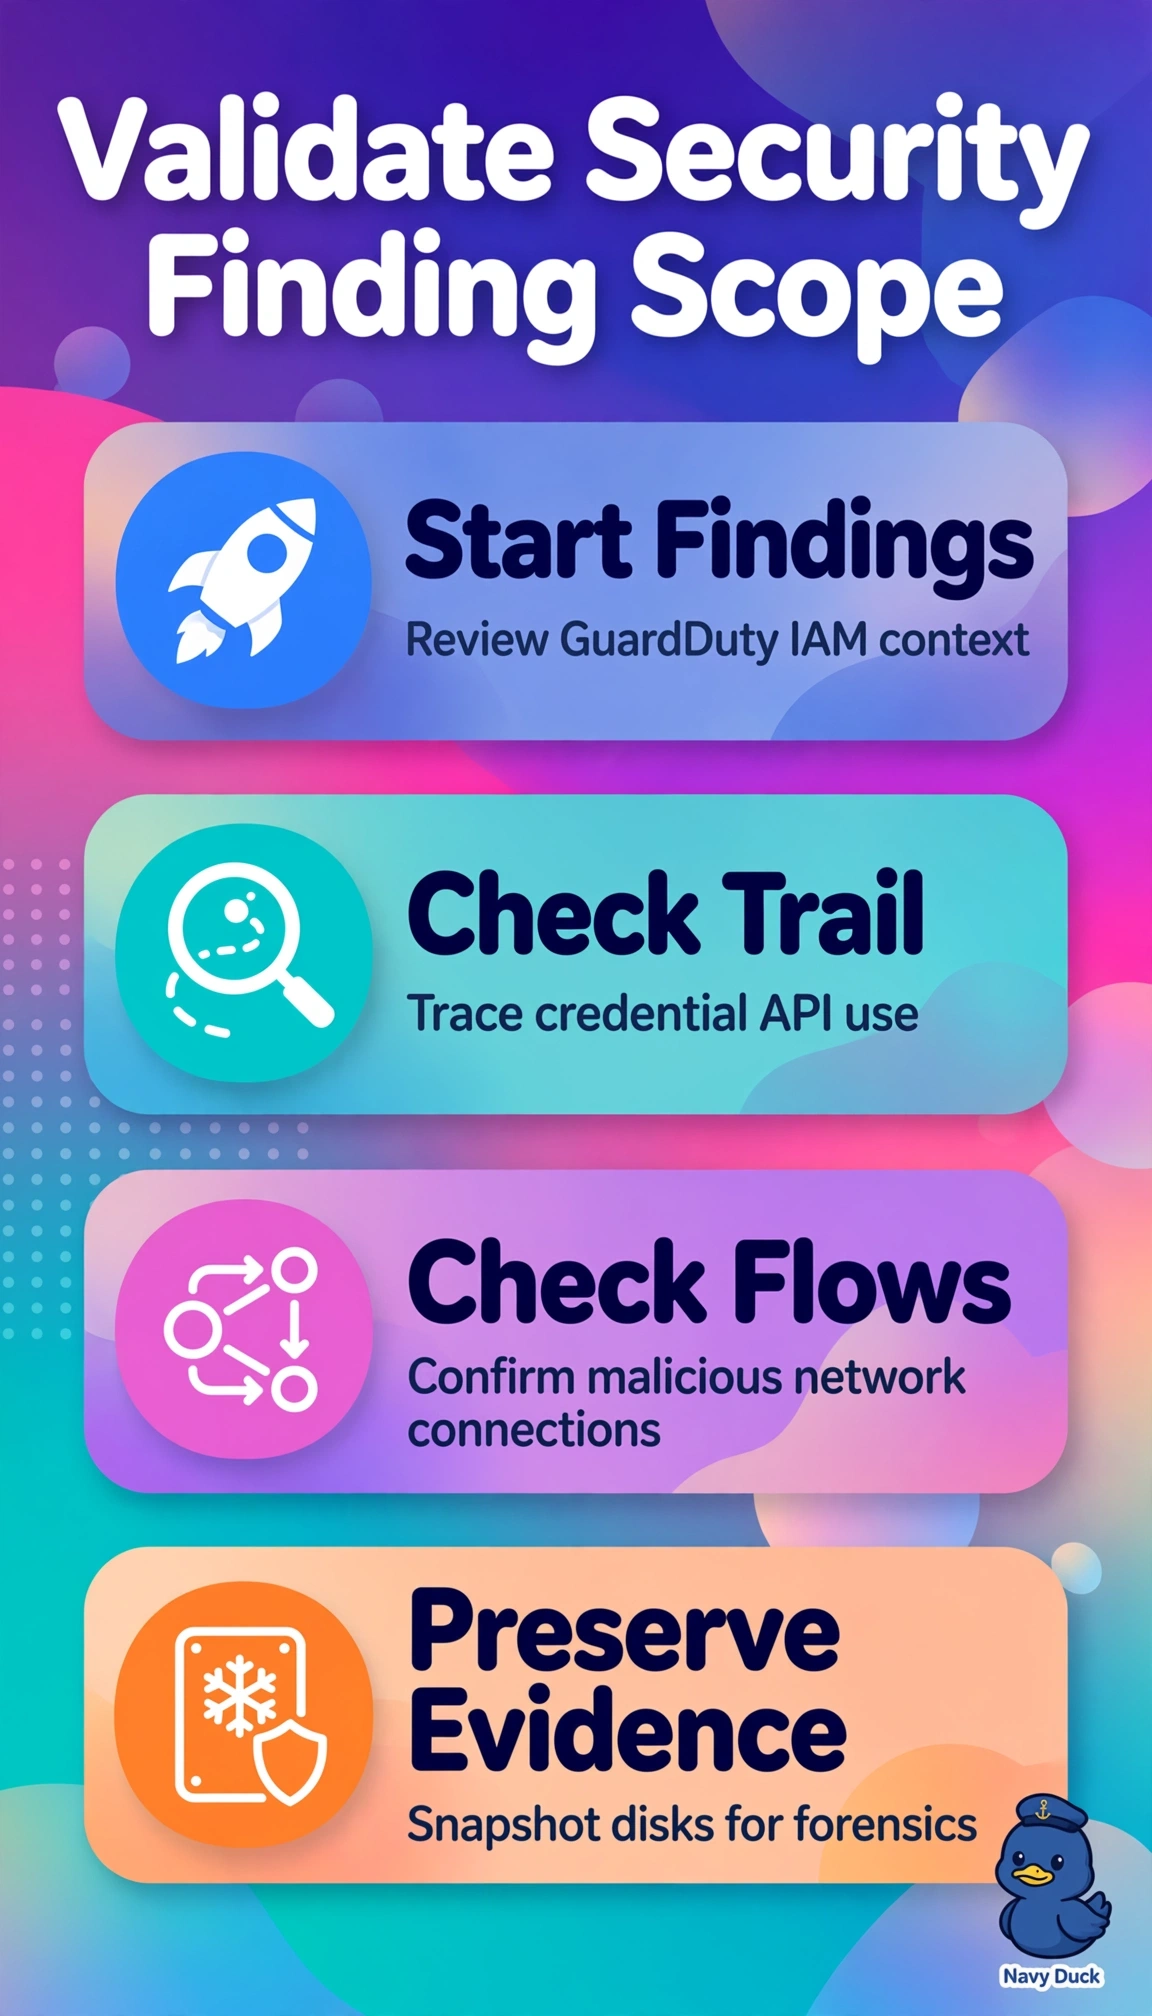
The correct workflow is right because neither a GuardDuty crypto-mining alert nor a correlated IAM credential leak can be dispositioned on owner assertion alone, so true scope requires pivoting from both detective signals to authoritative evidence across identity, network, and host domains, with CloudTrail establishing who used the leaked credentials, what APIs were called and when relative to any claimed test window, VPC Flow Logs establishing mining pool destinations, beaconing, data transfer volume and lateral movement to other instances, and EBS snapshots preserving host artifacts for persistence mechanisms, malware binaries, and timeline reconstruction without destroying evidence. Correlating only CloudTrail and VPC Flow Logs fails on the host-forensics concept because without EBS snapshot analysis persistence via cron, systemd, user-data, or rootkits remains unproven and scope cannot be closed. Pivoting only to CloudTrail and EBS snapshots fails on the network-telemetry concept because without VPC Flow Logs the external impact, command-and-control, pool communication, and east-west spread are invisible, leaving blast-radius incomplete. Using full telemetry merely to validate the claimed testing window for closure fails on the independent-verification concept because it introduces confirmation bias by presuming benign intent instead of testing malicious hypotheses against tags, change records, and anomalous behavior. For exams, distinguish scoping and impact assessment from containment or credential rotation, which preserve safety but do not prove scope and can destroy ordering if done first. Practically, snapshot EBS before isolation, query CloudTrail for IAM usage outside the claimed window and for persistence actions, and match VPC destinations against known mining pools while verifying tags and approvals independently.