
A media site on CloudFront and ALB origin faces SQL injection, XSS, and bot-driven credential stuffing during launches, with legitimate global traffic spikes. The team must filter OWASP Top 10 threats at the edge without building custom proxies. Which network edge protection control blocks these application-layer attacks?
Select an answer to reveal the explanation.
Short Explanation
You need a bouncer at the global door, not at the back hallway. Managed rules spot those nasty payloads before they ever reach your origin.
Full Explanation
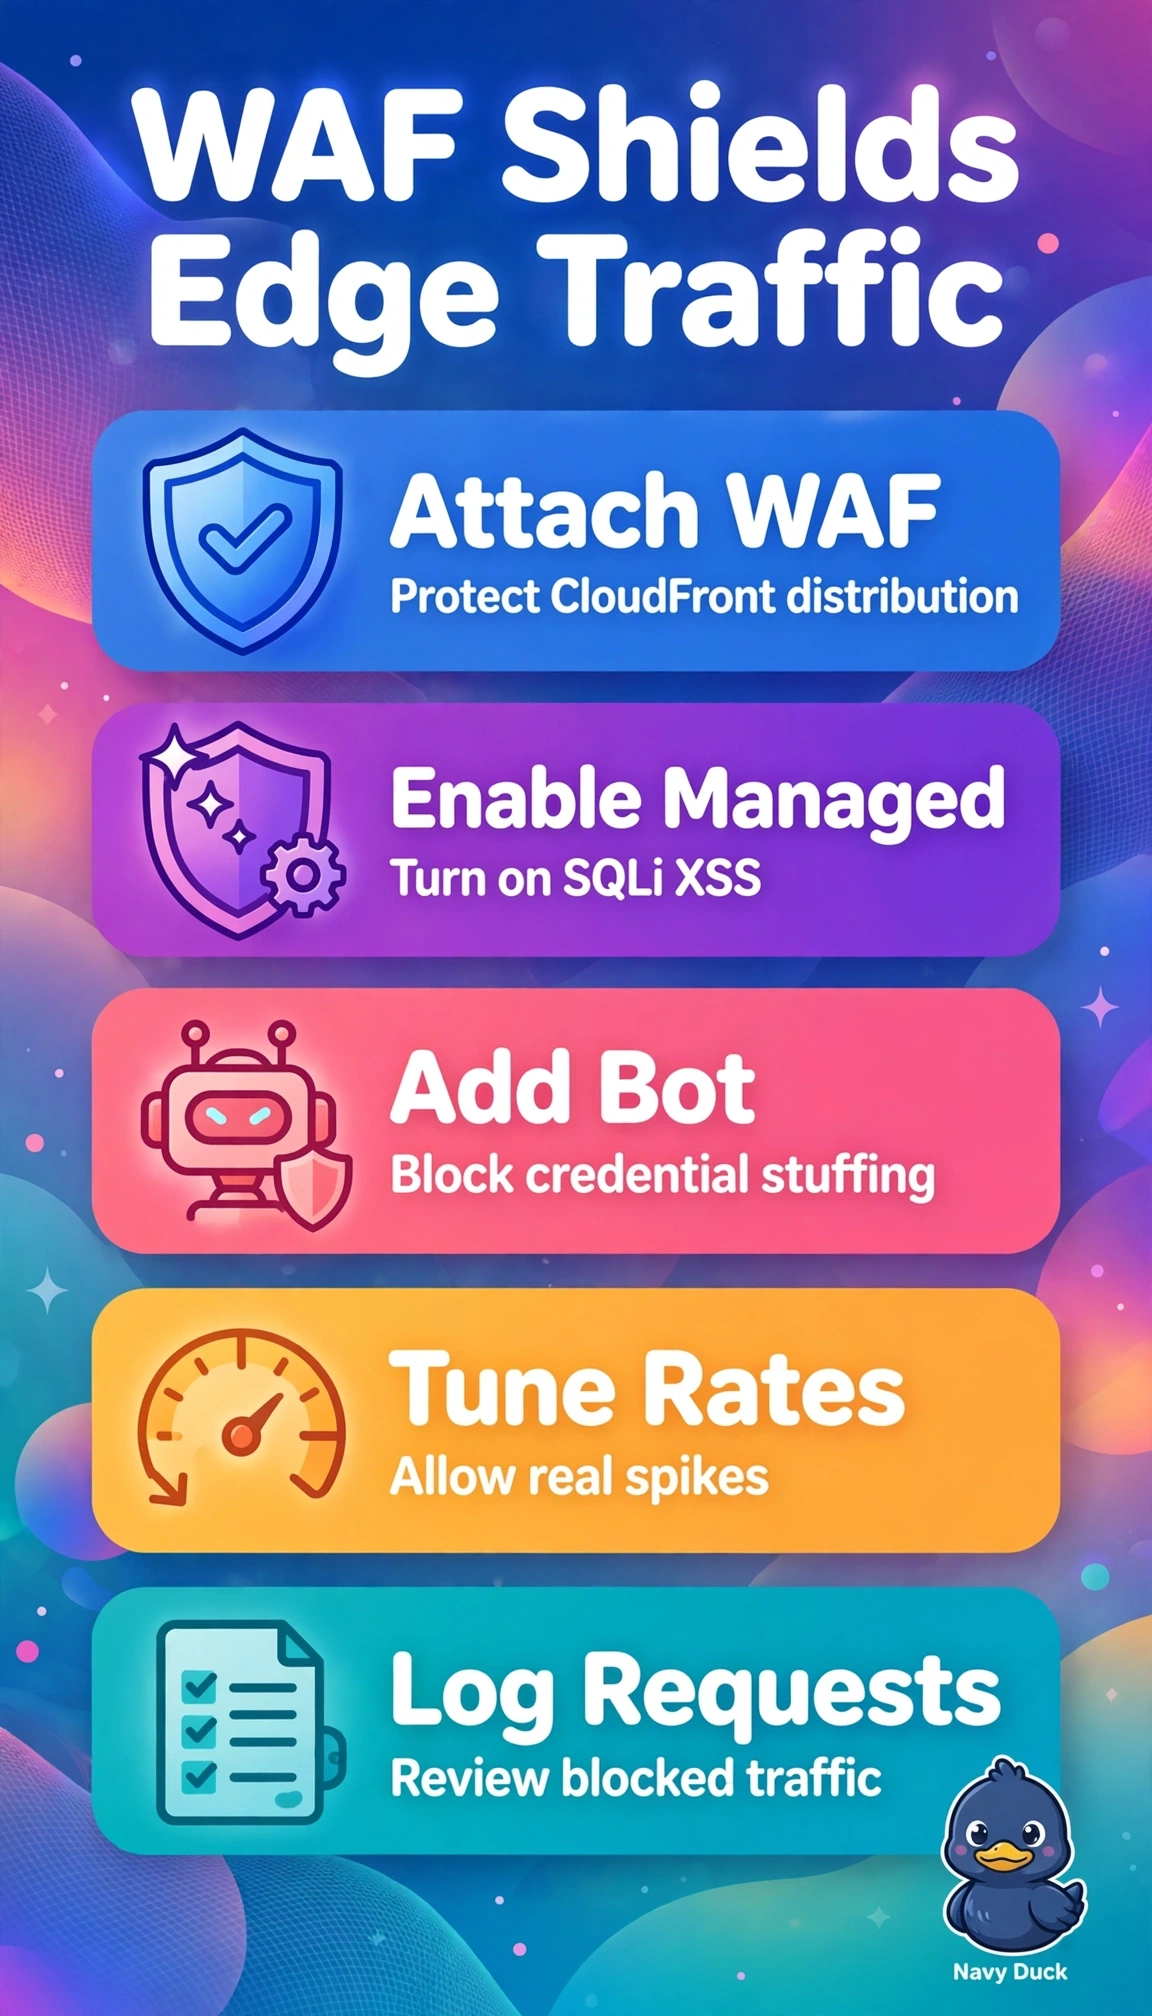
The correct control is right because AWS WAF operates at Layer 7 and integrates natively with CloudFront to inspect URLs, headers, bodies, and cookies at global edge locations using managed rule groups for SQL injection, cross-site scripting, and bot control, which directly addresses OWASP Top 10 filtering and credential stuffing without custom proxy code while AWS Bot Control distinguishes malicious automation from legitimate launch spikes. Shield Advanced fails by concept because it provides network-layer volumetric DDoS absorption and edge availability protection but does not parse application payloads for injection signatures. Attaching WAF to the ALB fails by placement because although inspection logic is correct, enforcement occurs at the regional origin after traffic has traversed the internet to the load balancer, leaving the edge requirement unmet and exposing origin capacity. CloudFront throttling with geo restriction fails by granularity because rate limits and country blocks can reduce brute-force volume but cannot detect SQL syntax or script payloads in otherwise normal-rate requests. Exam caveat: distinguish Shield versus WAF and CloudFront versus ALB attachment points, as stems emphasizing edge plus injection point to CloudFront WAF. Practical check: verify in the console that the web ACL is associated to the distribution, that SQLi, XSS core rules and Bot Control are in block or challenge mode, and that WAF logs show blocked XSS and SQLi samples during load testing.