
A SaaS team builds containers in CodePipeline across dev and prod accounts, must block images with critical CVEs from being promoted, sign images for admission, and track findings centrally. Which pipeline security scanning and signing design satisfies these controls?
Select an answer to reveal the explanation.
Short Explanation
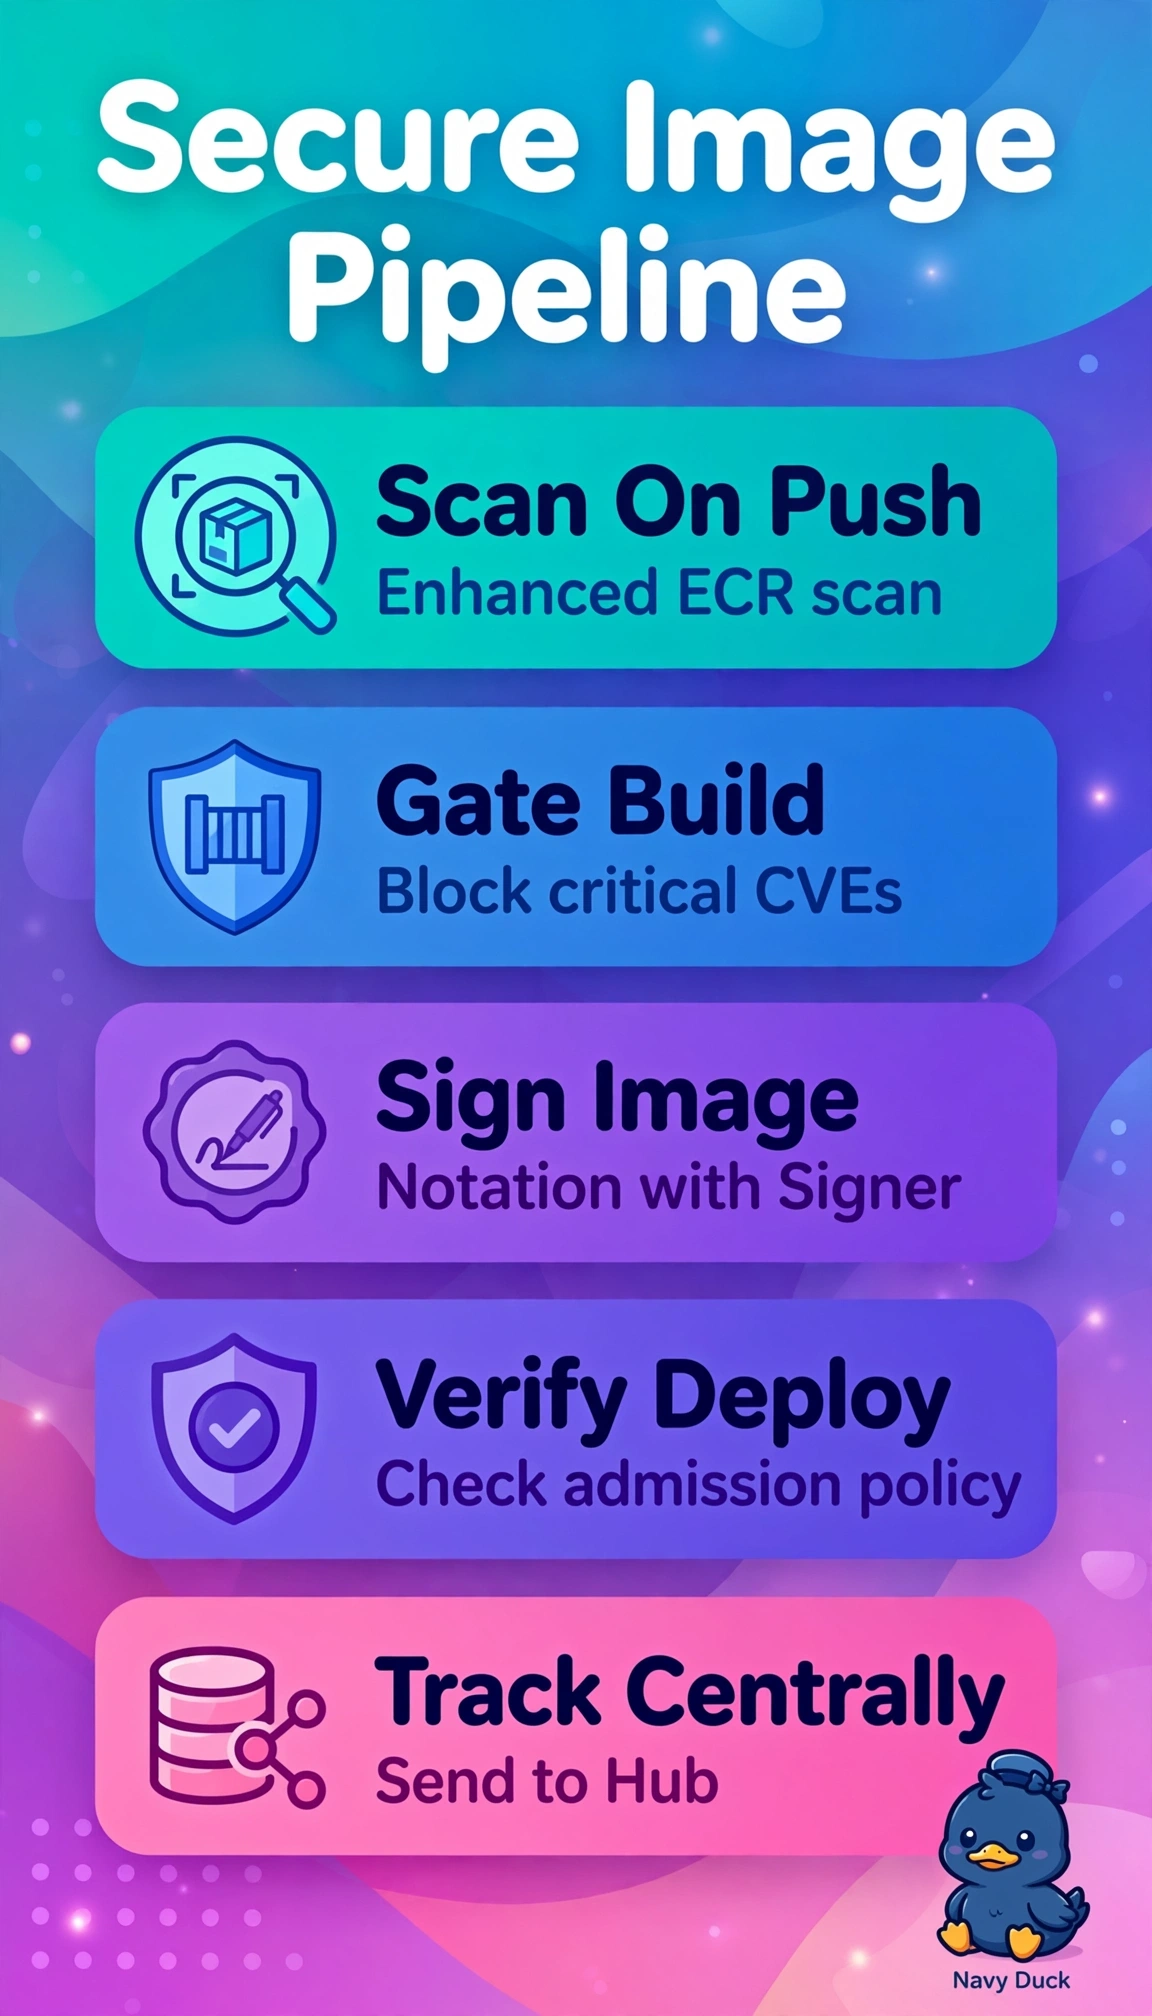
You can catch risky images early with ECR enhanced scanning on each push and block promotion when critical findings appear. Notation signatures then give admission controllers a way to verify trusted images before they enter production.
Full Explanation
The design with ECR enhanced scanning on push, a promotion gate, Notation signing, and Security Hub tracking satisfies all four controls. Enhanced scanning, backed by Inspector, evaluates OS and language packages on push and continuously; Security Hub provides centralized multi-account visibility, and CodePipeline can block promotion when critical CVEs are found. Notation signing provides verifiable artifact integrity that Kubernetes admission controllers can enforce. The design with enhanced scanning, gating, and Security Hub tracking covers scanning and central tracking but omits signing, so admission control requiring signed provenance cannot be satisfied. The design with scanning, cross-account replication, and Notation signing preserves provenance and distribution but omits the findings-based promotion gate, allowing images with critical CVEs to advance; replication is not a preventive security gate. The design with basic scanning, gating, and Notation signing supports push-time blocking and admission checks, but lacks Inspector’s enhanced scanning depth and continuous, centralized findings coverage across dev and prod. Exam caveat: distinguish scan timing and depth; basic or on-pull scanning may sound sufficient but does not meet on-push blocking and multi-account centralization. Practical check: verify Inspector delegated administrator and ECR enhanced scanning settings, test that a critical CVE fails the pipeline, validate Notation verification logs at admission, and confirm matching finding IDs in Security Hub.