
A global gaming studio runs 30 AWS accounts for matchmaking and live events, generating high-volume VPC flow and application logs that security must search within seconds while finance requires low-cost seven-year retention for compliance. Which centralized logging design delivers near-real-time analysis with durable tiered archiving?
Select an answer to reveal the explanation.
Short Explanation
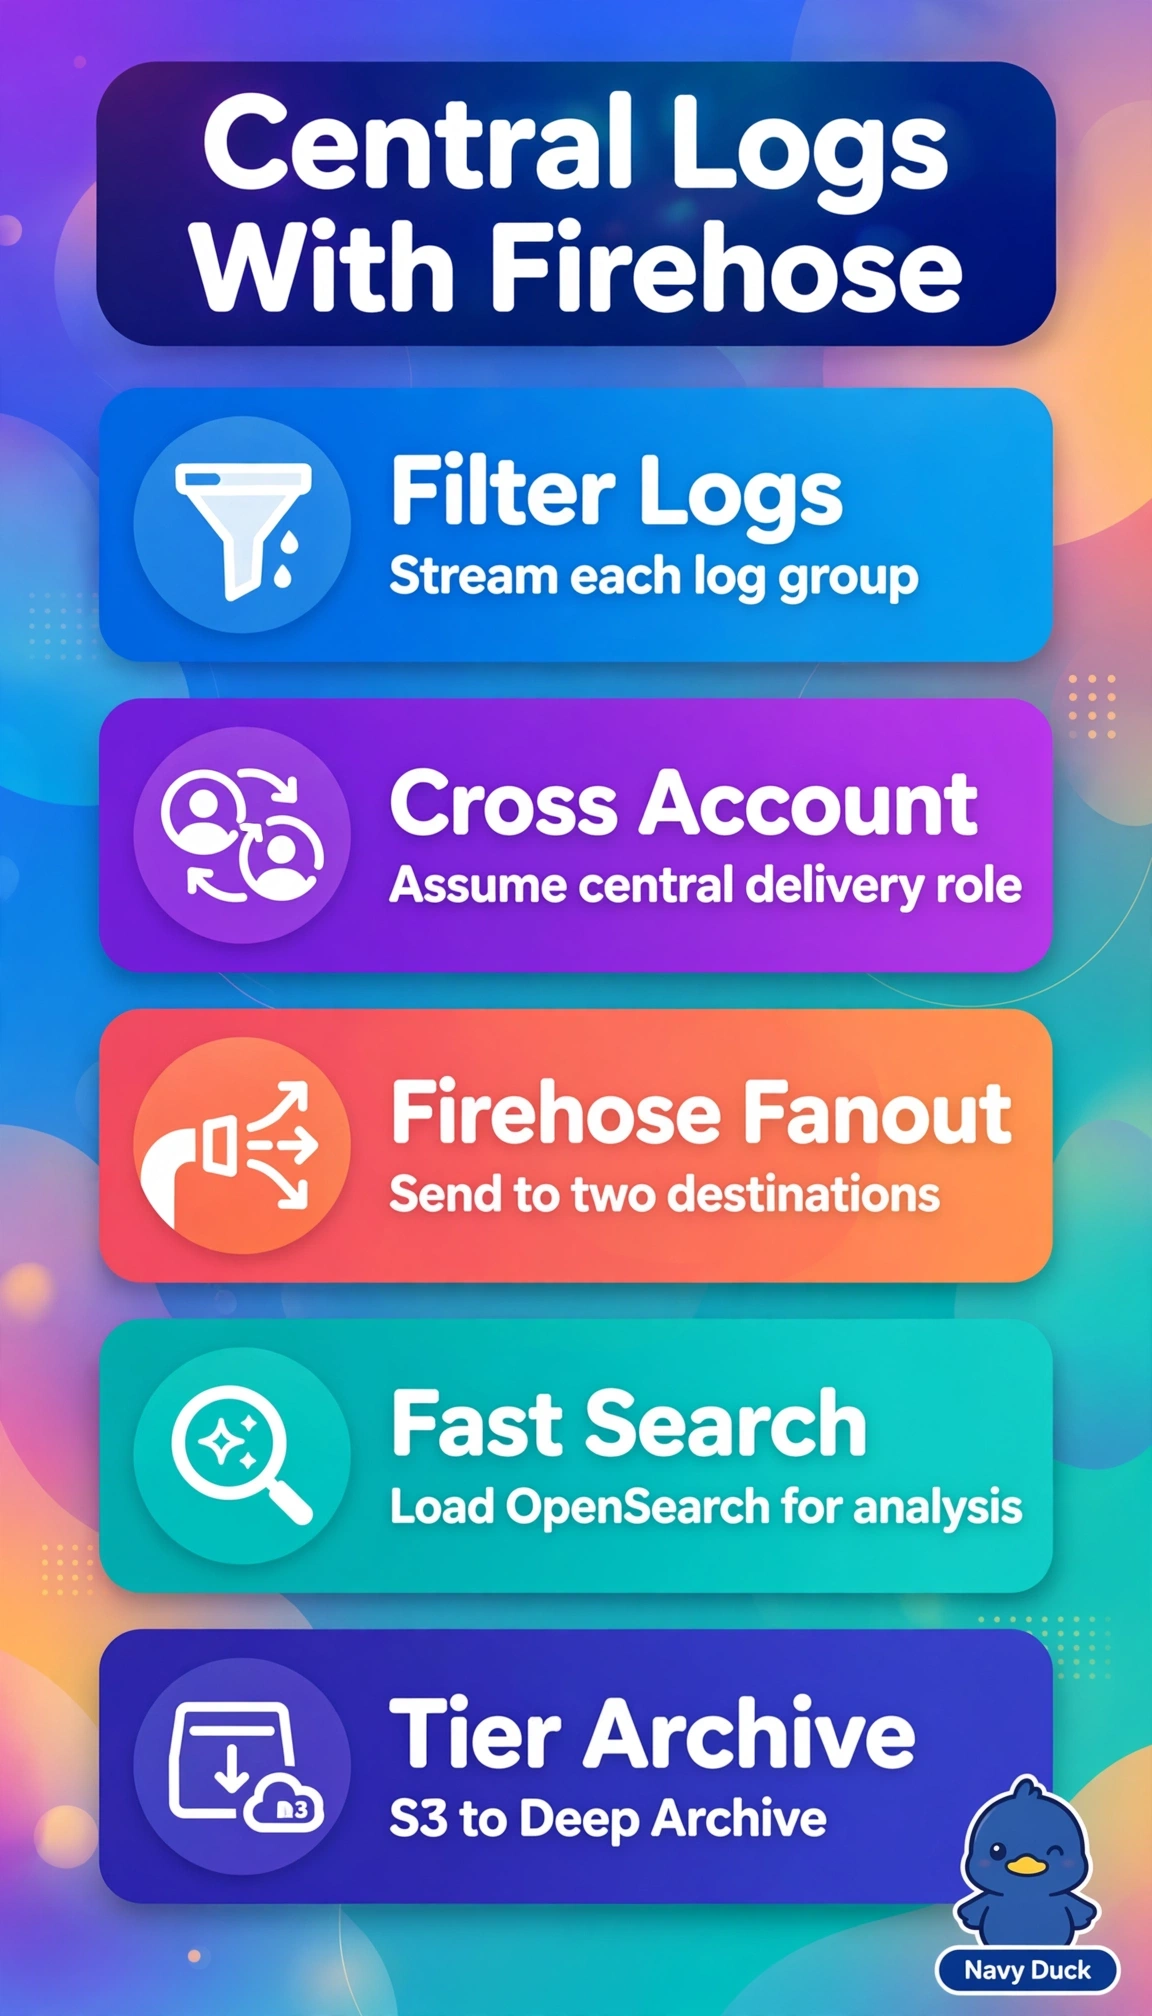
You've got both speed and thrift covered with streaming plus cheap deep storage. Subscription filters act like conveyor belts feeding Firehose, which sorts fresh logs for search while dropping a copy into S3 for years.
Full Explanation
The correct approach works because CloudWatch Logs subscription filters provide continuous, near-real-time streaming from each member account to a central destination using cross-account IAM roles, and Amazon Data Firehose fans that stream out to both an analytics endpoint such as Amazon OpenSearch Service for seconds-latency search and to a central S3 bucket where lifecycle policies transition objects to S3 Glacier Deep Archive for seven-year low-cost retention with Object Lock and versioning for immutability. The organization CloudTrail trail approach fails by concept because CloudTrail records only API activity and cannot stream VPC or application logs from CloudWatch Logs, so it misses the security search requirement despite offering central S3 archiving. The scheduled hourly S3 export approach fails by concept because batch exports are periodic and Athena queries are retrospective, so they cannot satisfy the seconds-latency detection need even though they provide cheap archival. The central Amazon MSK approach fails by concept because MSK is a streaming bus, not a tiered archive, and retaining seven years in Kafka and OpenSearch is costly and operationally heavy compared with S3 storage tiers. Exam caveat: choose subscription plus Firehose to S3 plus search when you see both real-time and multi-year retention in one stem. Practical check: verify destination Firehose resource policy allows logs.amazonaws.com AssumeRole and test S3 lifecycle transitions with Object Lock enabled.