
A biotech enterprise stores genomic data in S3 and must prove no external network path or permissive policy allows exfiltration, while partners access dashboards through identity-aware private entry. Which combination enforces this data perimeter?
Select an answer to reveal the explanation.
Short Explanation
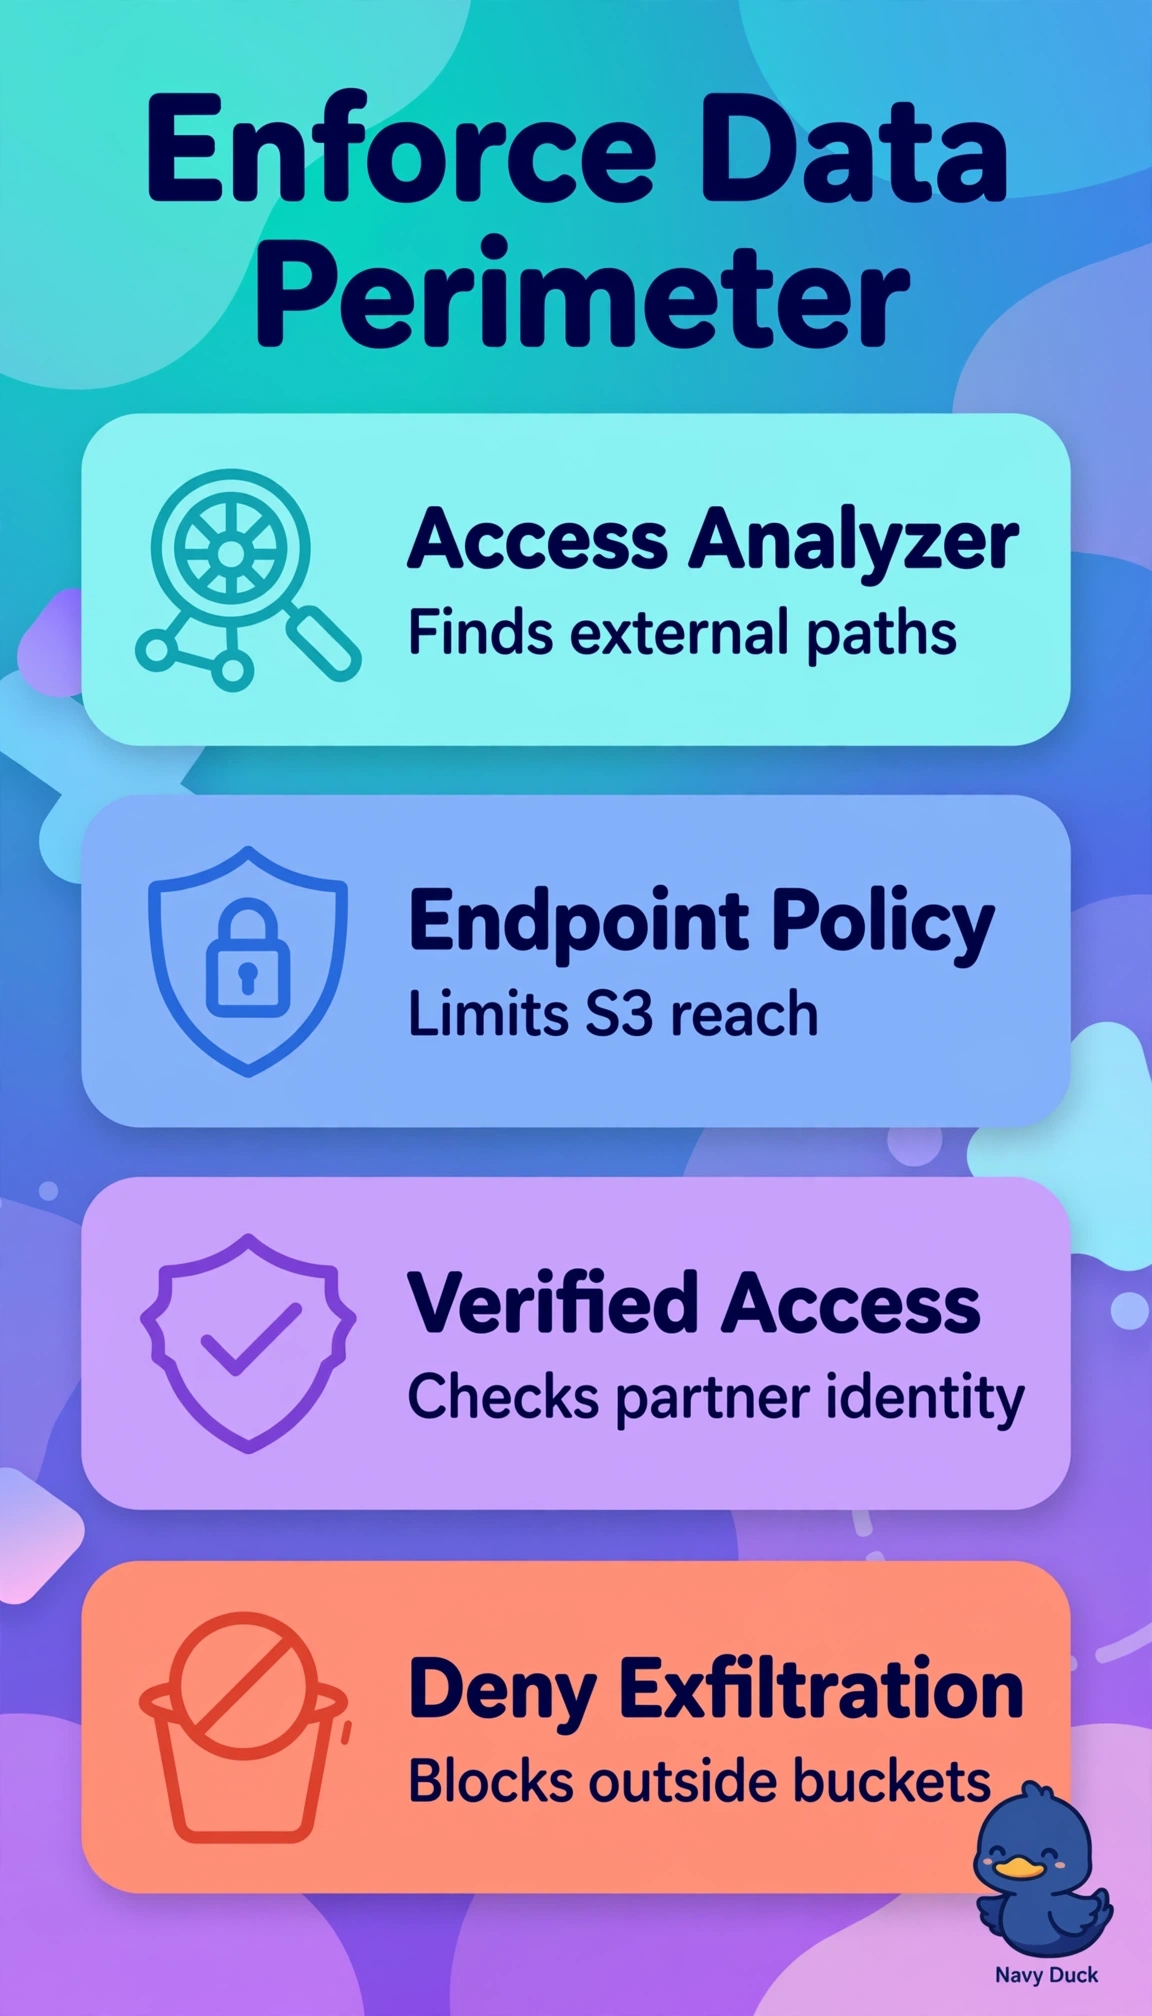
Genomes can't leak, period. You're building a tight data perimeter where Analyzer proves no escape and private endpoints enforce every request.
Full Explanation
The correct combination establishes a verifiable data perimeter because IAM Access Analyzer proves that no S3 bucket policy, access point, or IAM grant allows external or cross-account exfiltration, restrictive VPC endpoint policies ensure S3 is reachable only from approved VPCs and principals with conditions like aws:SourceVpce and aws:PrincipalOrgID while denying internet paths, and Verified Access provides identity-aware private entry to dashboards with per-request evaluation of user identity, device posture, and IdP groups without inbound ports. The internet-facing ALB approach fails on network containment because it reintroduces a public ingress path for partner dashboards even though analyzer validation and endpoint restriction are correctly applied, violating the no external path mandate. The client VPN approach fails on identity-aware access because VPN grants broad network-layer connectivity authenticated at tunnel setup rather than continuous application-layer evaluation of identity and device health. The PrivateLink without validation approach fails on policy assurance because interface endpoints alone cannot remediate permissive S3 resource policies, and without analyzer findings review undetected external allowances remain provable during audit. An exam caveat is that Verified Access, PrivateLink, VPN, and endpoint policies all sound private, so distinguish designs that prove no permissive policy with analyzer evidence and enforce per-identity app access from those that only provide private routing. A practical check is to clear Access Analyzer external-access findings to zero, test endpoint policies with IAM Policy Simulator for a foreign principal, and confirm Verified Access logs deny non-compliant devices before production release.