
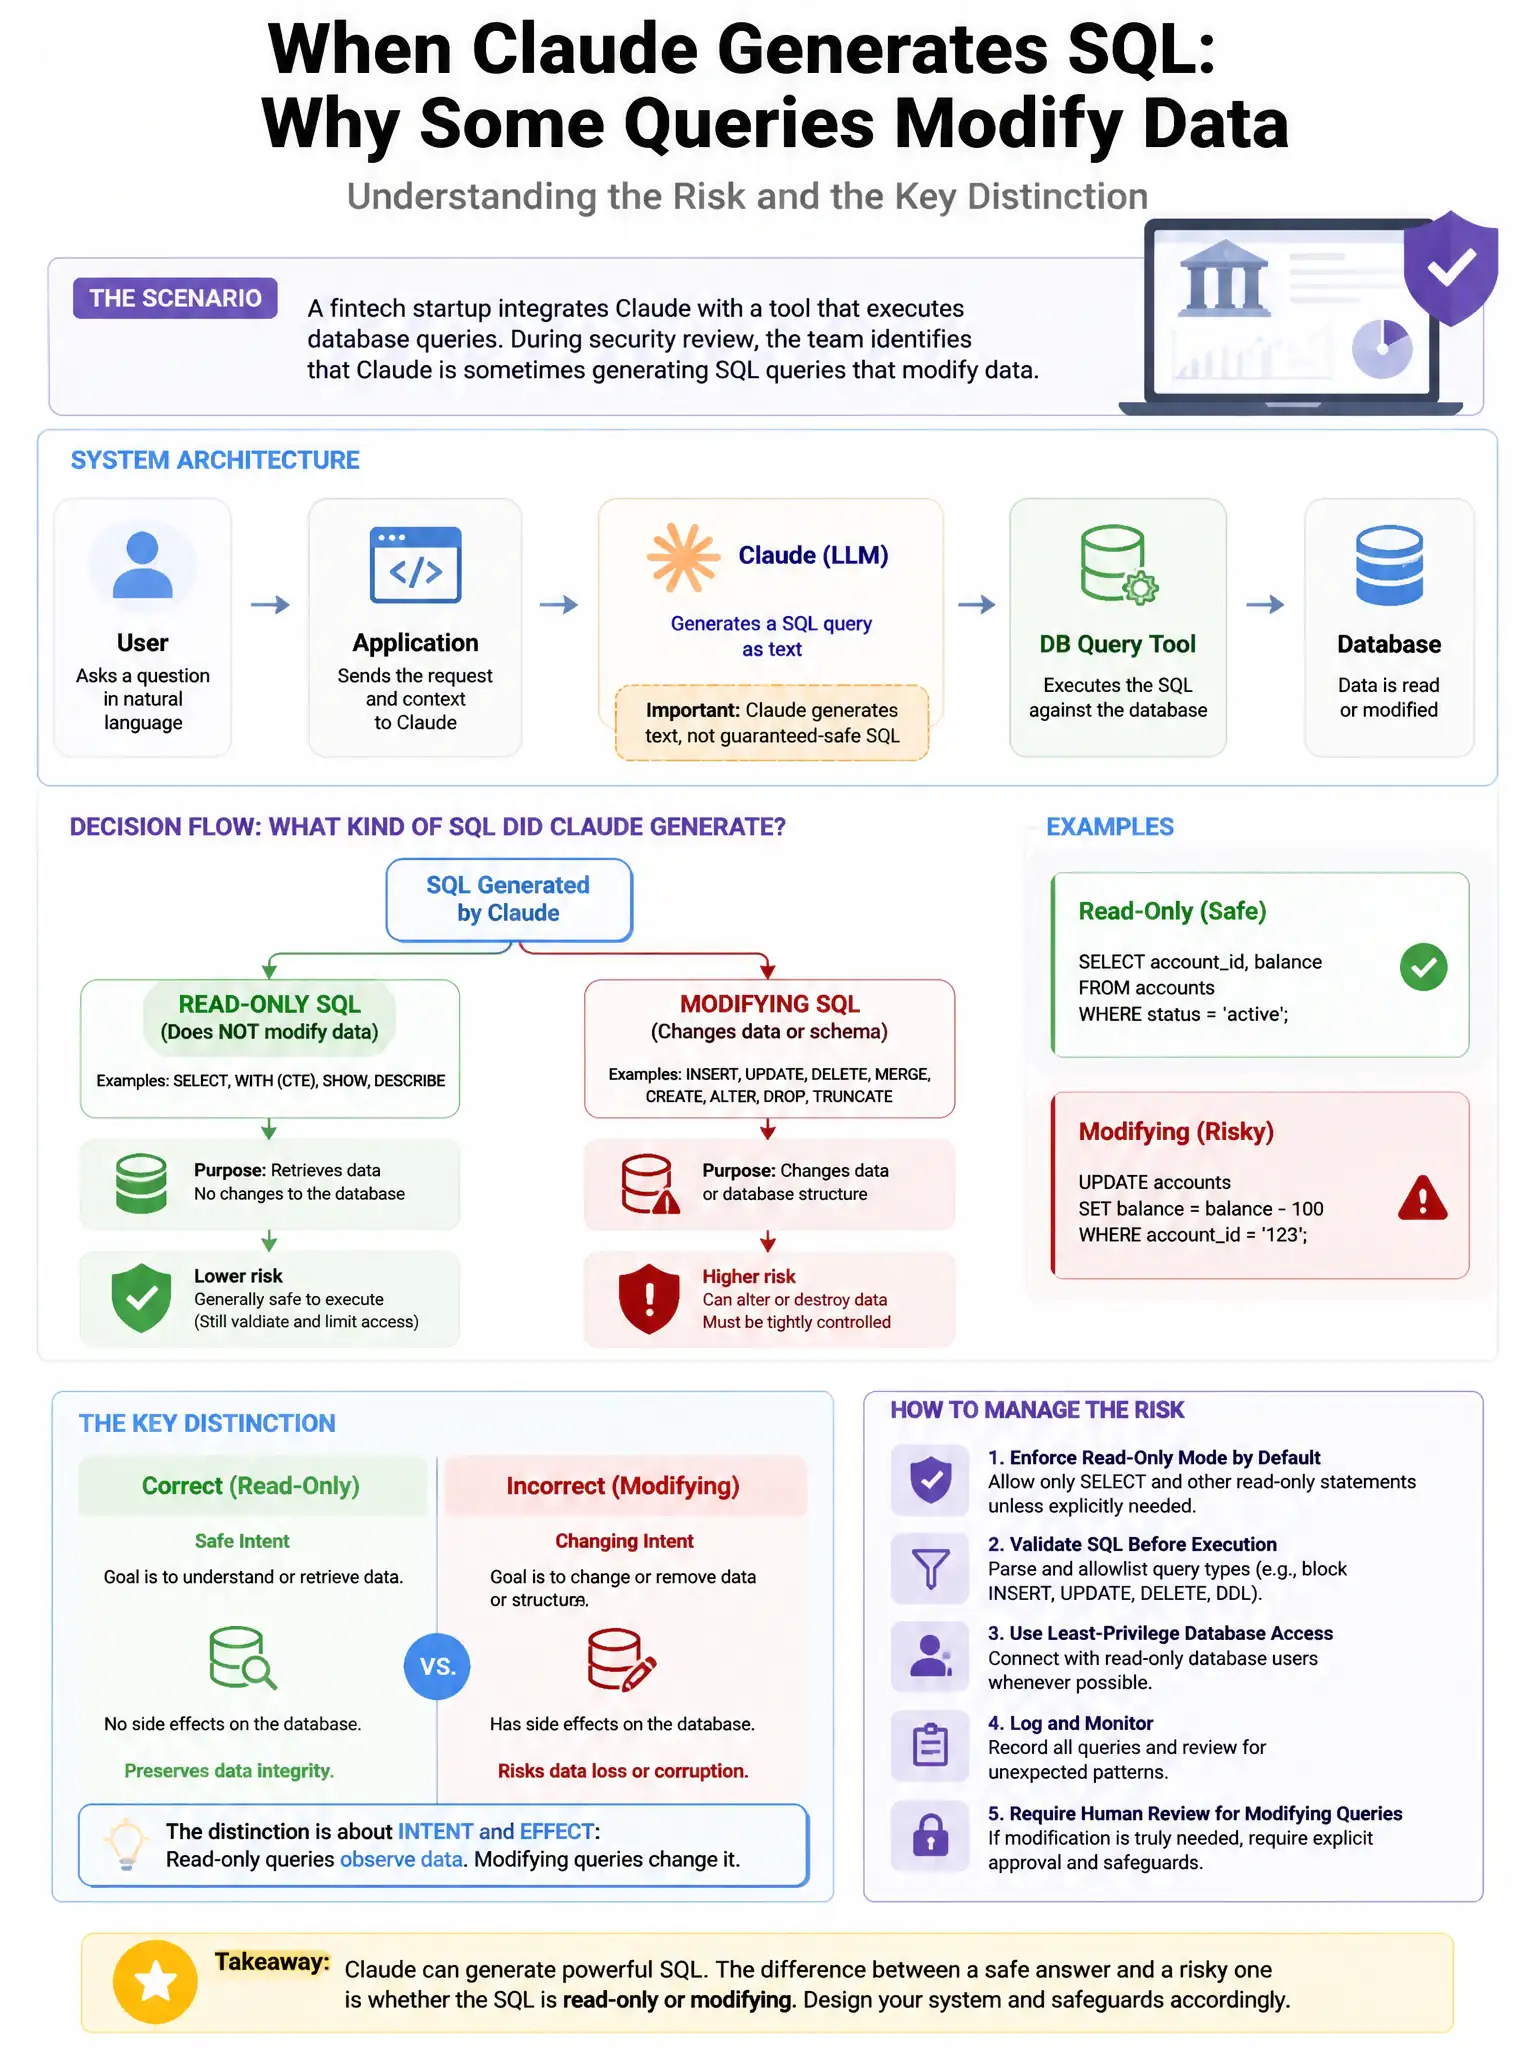
A fintech startup integrates Claude with a tool that executes database queries. During security review, the team identifies that Claude is sometimes generating SQL queries that modify data (UPDATE, DELETE) when the tool schema description says 'query the transaction database.' The security team wants a design in which Claude cannot produce SQL write statements at all, not one that only blocks them after they are generated. The current tool schema description reads: 'Query the transactions database to retrieve customer transaction data.' What is the most robust architectural solution?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need to switch to a parameterized query tool that accepts filter parameters instead of raw SQL. If Claude can't send SQL, it can't send write SQL. That removes the attack surface instead of hoping the model behaves.
Full Explanation
The parameterized query tool that accepts filter parameters such as customer_id, date_range, and transaction_type instead of raw SQL is the most robust architectural solution. It eliminates the attack surface entirely: if the tool interface accepts structured filter parameters rather than a SQL string, there is no SQL string for Claude to generate, so write operations become architecturally impossible through the tool interface. This is the principle of least privilege applied to tool design. The other approaches are defense-in-depth layers, but they don't remove the dangerous capability from the interface. The server-side SQL validation layer that rejects any non-SELECT statements before database execution, returning a tool error, is essential as a defense layer, but it is not the most robust architectural solution because it assumes Claude always produces parseable SQL that the validator can intercept, and validation logic has its own bugs. The tool description constraint that says only SELECT statements are permitted and never UPDATE, DELETE, INSERT, or DDL statements is prompt guidance that Claude may not reliably follow, especially under adversarial prompting or unusual edge cases. The system prompt instruction that says Claude must never generate SQL statements that modify data and all database queries must be read-only SELECT statements has the same weakness as the tool description constraint: it is guidance, not enforcement. The correct security architecture eliminates the dangerous capability from the tool interface rather than relying on model compliance.