
A municipal pump-out dock agent must book a slot on an outside calendar without a volunteer pasting an API key into the prompt or the repo. Which control obtains those credentials safely?
Select an answer to reveal the explanation.
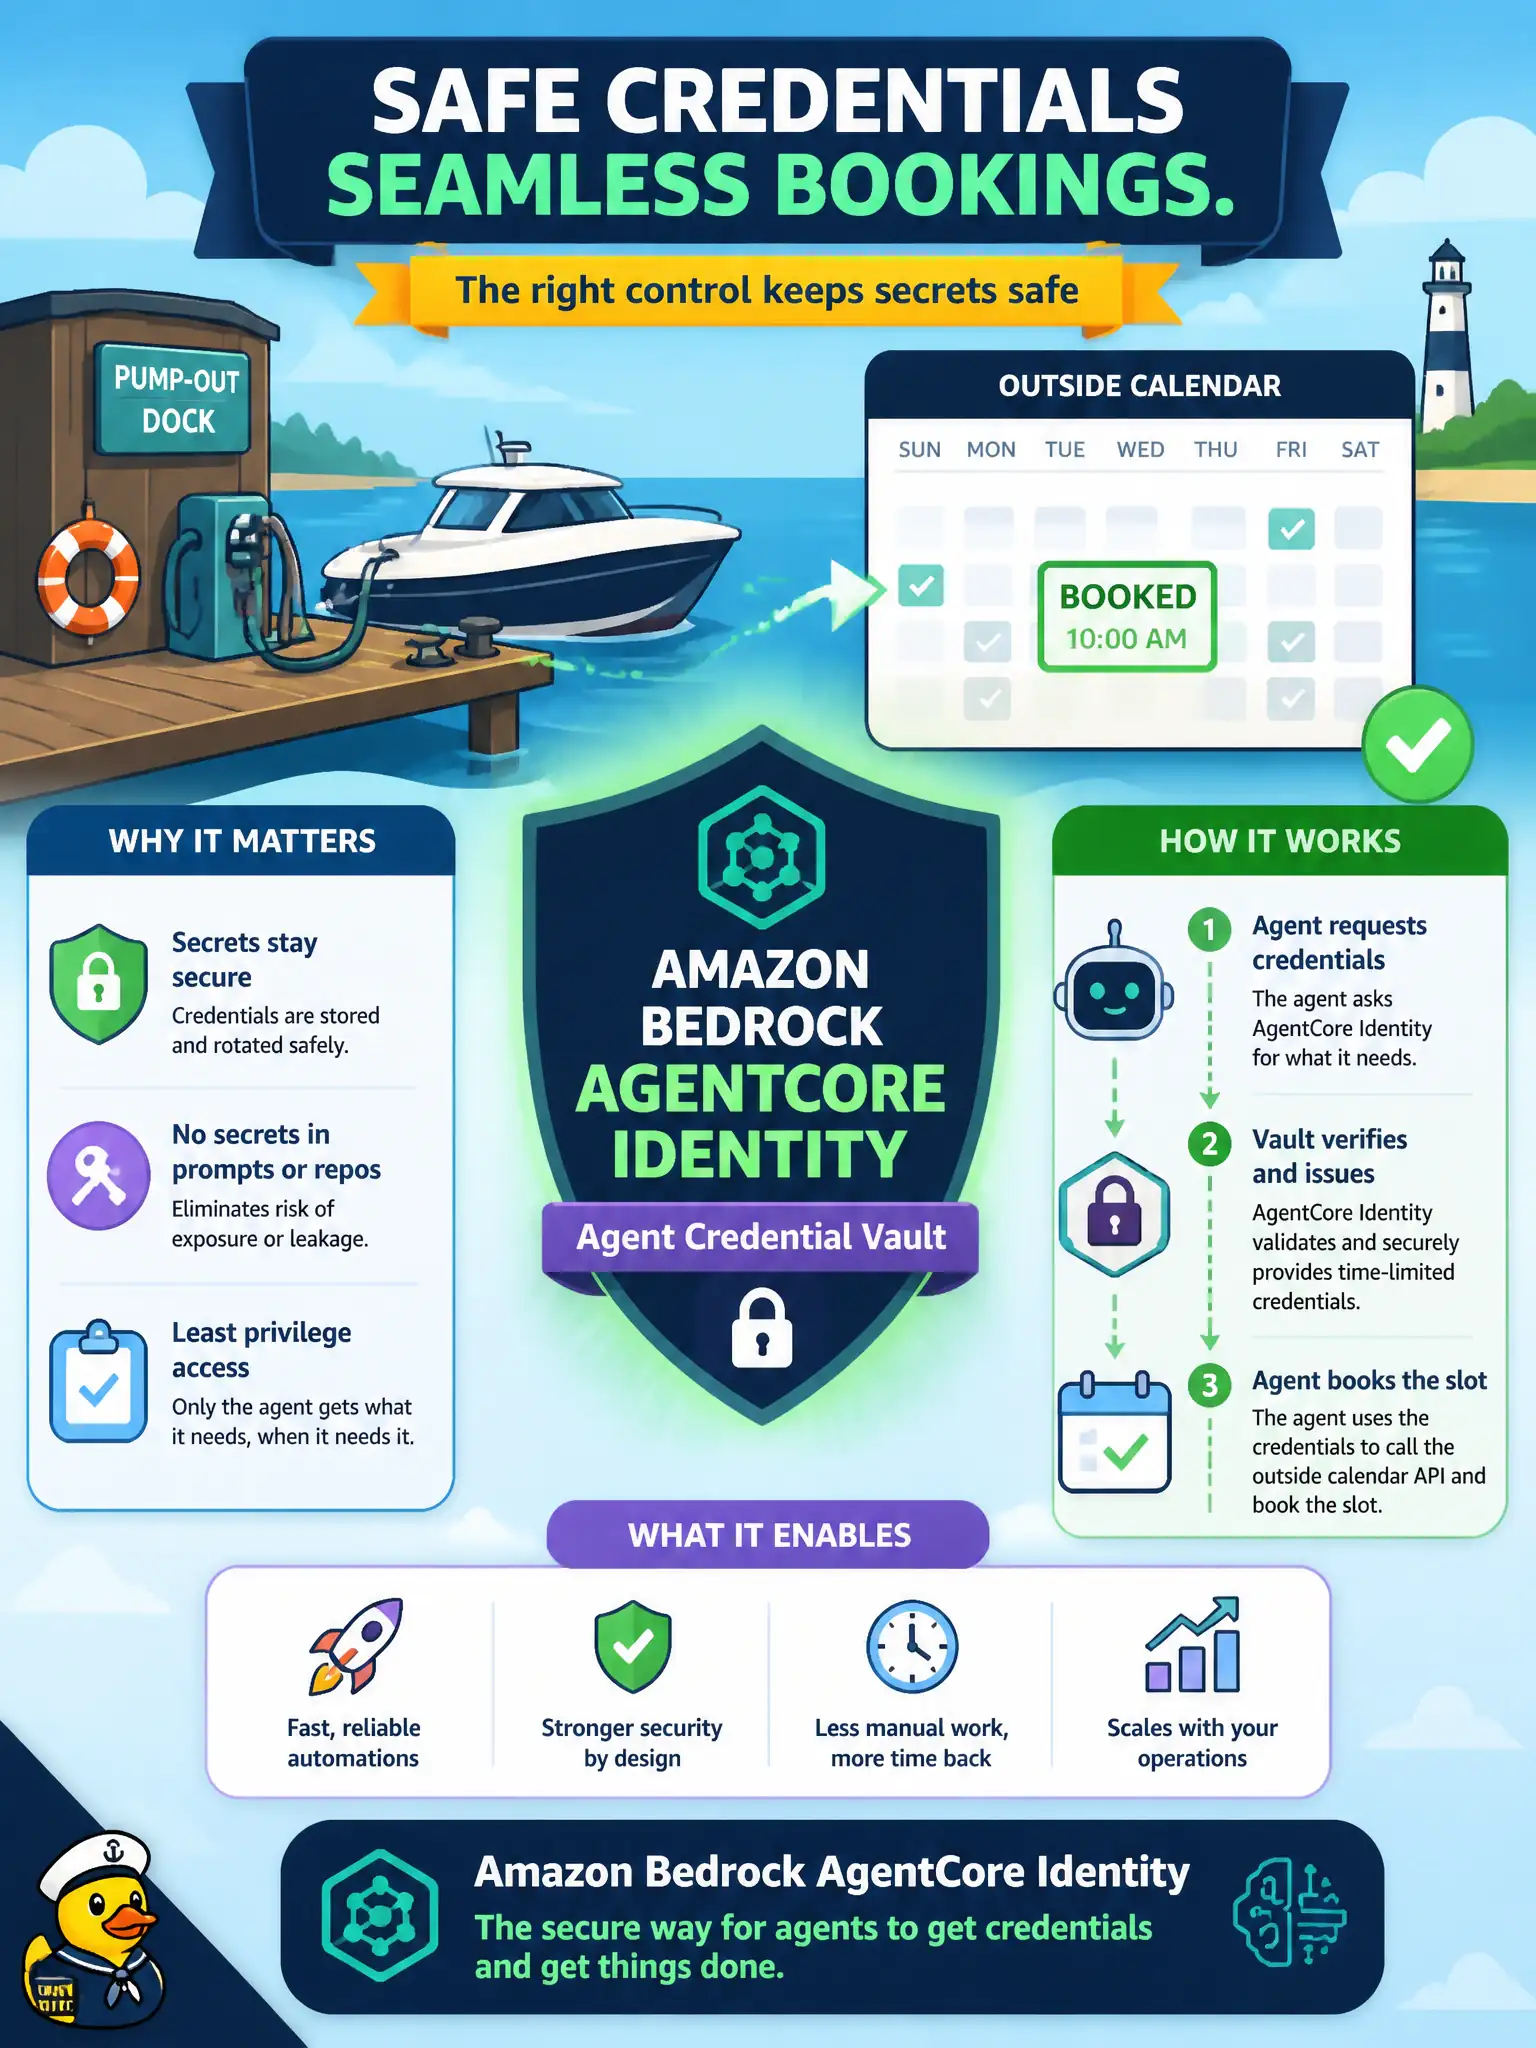
Short Explanation
Think of booking an outside calendar without pasting an API key into the prompt or the repo. Amazon Bedrock AgentCore Identity, or an equivalent vault. A git file is not a credential store.
Full Explanation
The municipal pump-out dock agent must book an outside calendar without volunteers pasting an API key into the prompt or the repository. Amazon Bedrock AgentCore Identity, or an equivalent agent credential vault, obtains and injects those third-party credentials safely at runtime. Secrets stay out of prompts, chat logs, and source control while the agent still performs the booking action on behalf of the dock.
Pasting the calendar key into the system prompt fails because prompts are visible to operators, often logged, and easy to exfiltrate via injection or casual screenshot sharing. Committing the key to the repo fails because git history spreads long-lived secrets across clones, forks, and backups. Amazon Polly fails because speech synthesis is not a credential vault for third-party API keys.
Exam caveat: a vault solves storage and injection; the agent still needs least-privilege scopes on the calendar integration and auditing of booking actions so a stolen runtime session cannot do more than schedule slots. Operational check: store the calendar secret in AgentCore Identity or a secrets manager, grant only the dock agent role retrieve-on-use access, scan the repo and prompt templates for leftover keys, and rotate any key that was ever pasted or committed.