
A community tool-barn agent can look up hours but must never email a refund or open the door controller. Which control limits those actions?
Select an answer to reveal the explanation.
Short Explanation
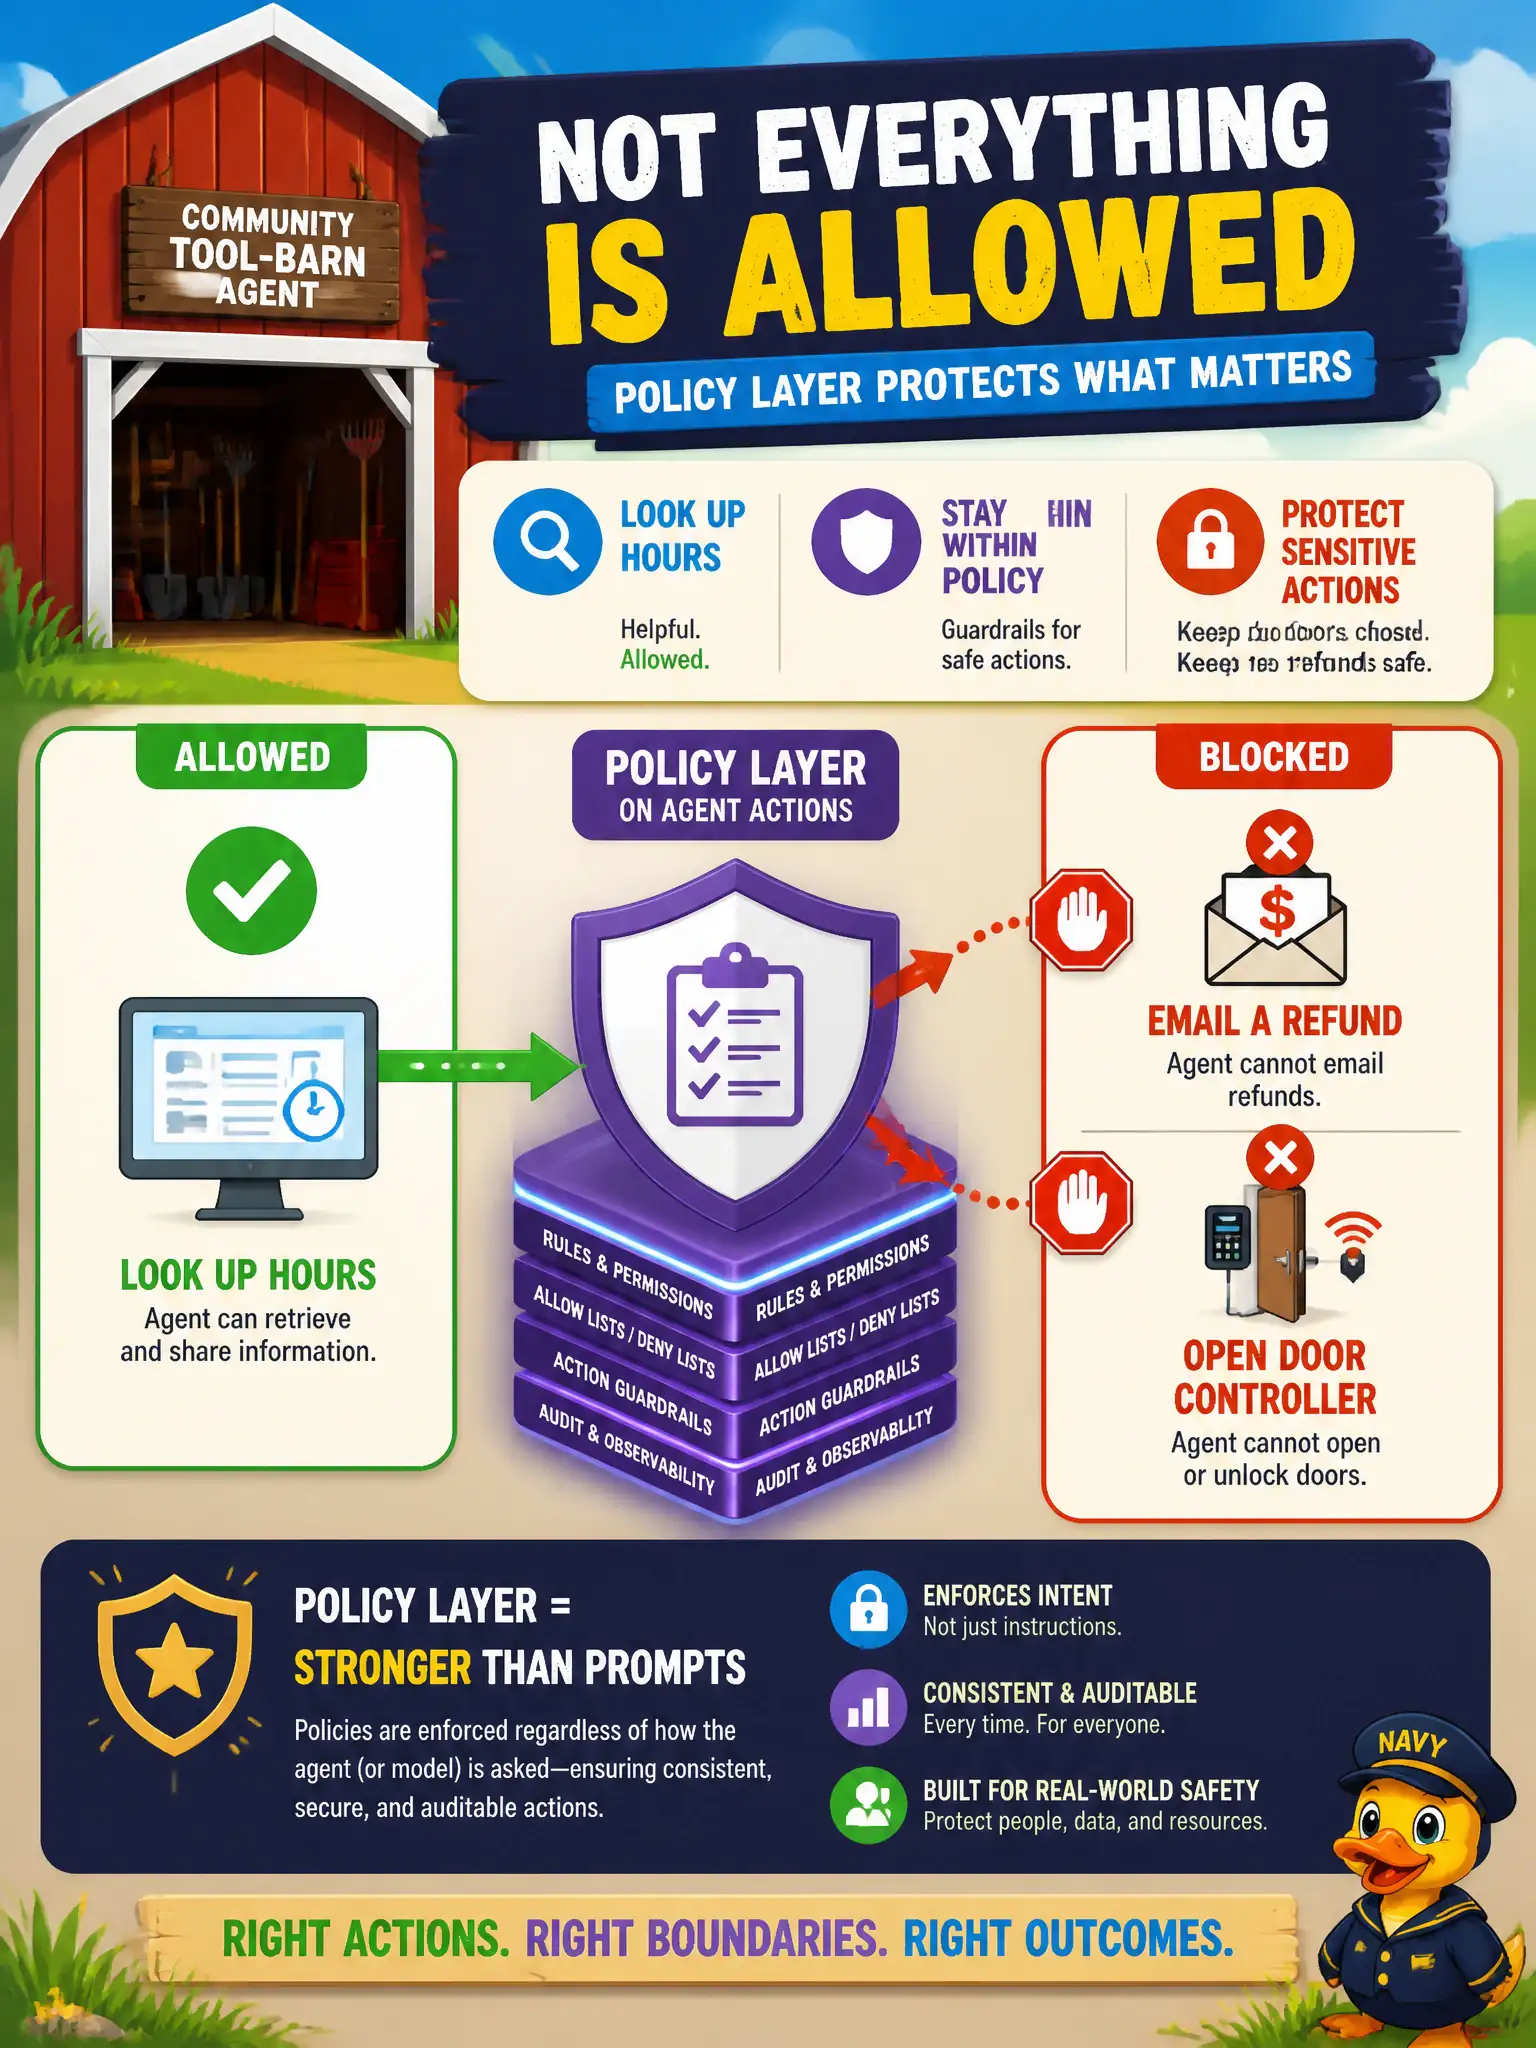
Think of a tool-barn agent that can look up hours but must never email a refund or open the door. Put a policy layer on those actions, such as Policy in AgentCore. Asking nicely in the prompt is not a lock.
Full Explanation
The community tool-barn agent may look up hours but must never email a refund or open the door controller. That requires a policy layer on agent actions—such as Policy in Amazon Bedrock AgentCore—not merely asking the model nicely in the prompt. Hard authorization on tools enforces allow/deny regardless of how cleverly a caller phrases a request to the barn assistant.
Relying on prompt wording alone fails because polite instructions are not a security boundary; models can be jailbroken or confused into attempting disallowed tools. Raising temperature so refund emails stop themselves fails because decoding randomness does not enforce tool policy or disable mailers. A dashboard title fails because charts do not lock door controllers or prevent refund mailers from sending.
Exam caveat: if a disallowed tool remains attached to the agent with only prompt guidance, the control is incomplete—deny at the policy/tool gateway and omit unused high-risk tools from the agent's tool list entirely. Operational check: configure an explicit allow-list for hours lookup, deny refund email and door-open actions in the policy layer, run red-team prompts that attempt those actions, and confirm the gateway blocks them even when the model tries to call the tools.