
A creamery already has approved AWS identity, logging, and regional controls and wants its GenAI helper to inherit those instead of a shadow laptop stack. Which Domain 2 advantage is this?
Select an answer to reveal the explanation.
Short Explanation
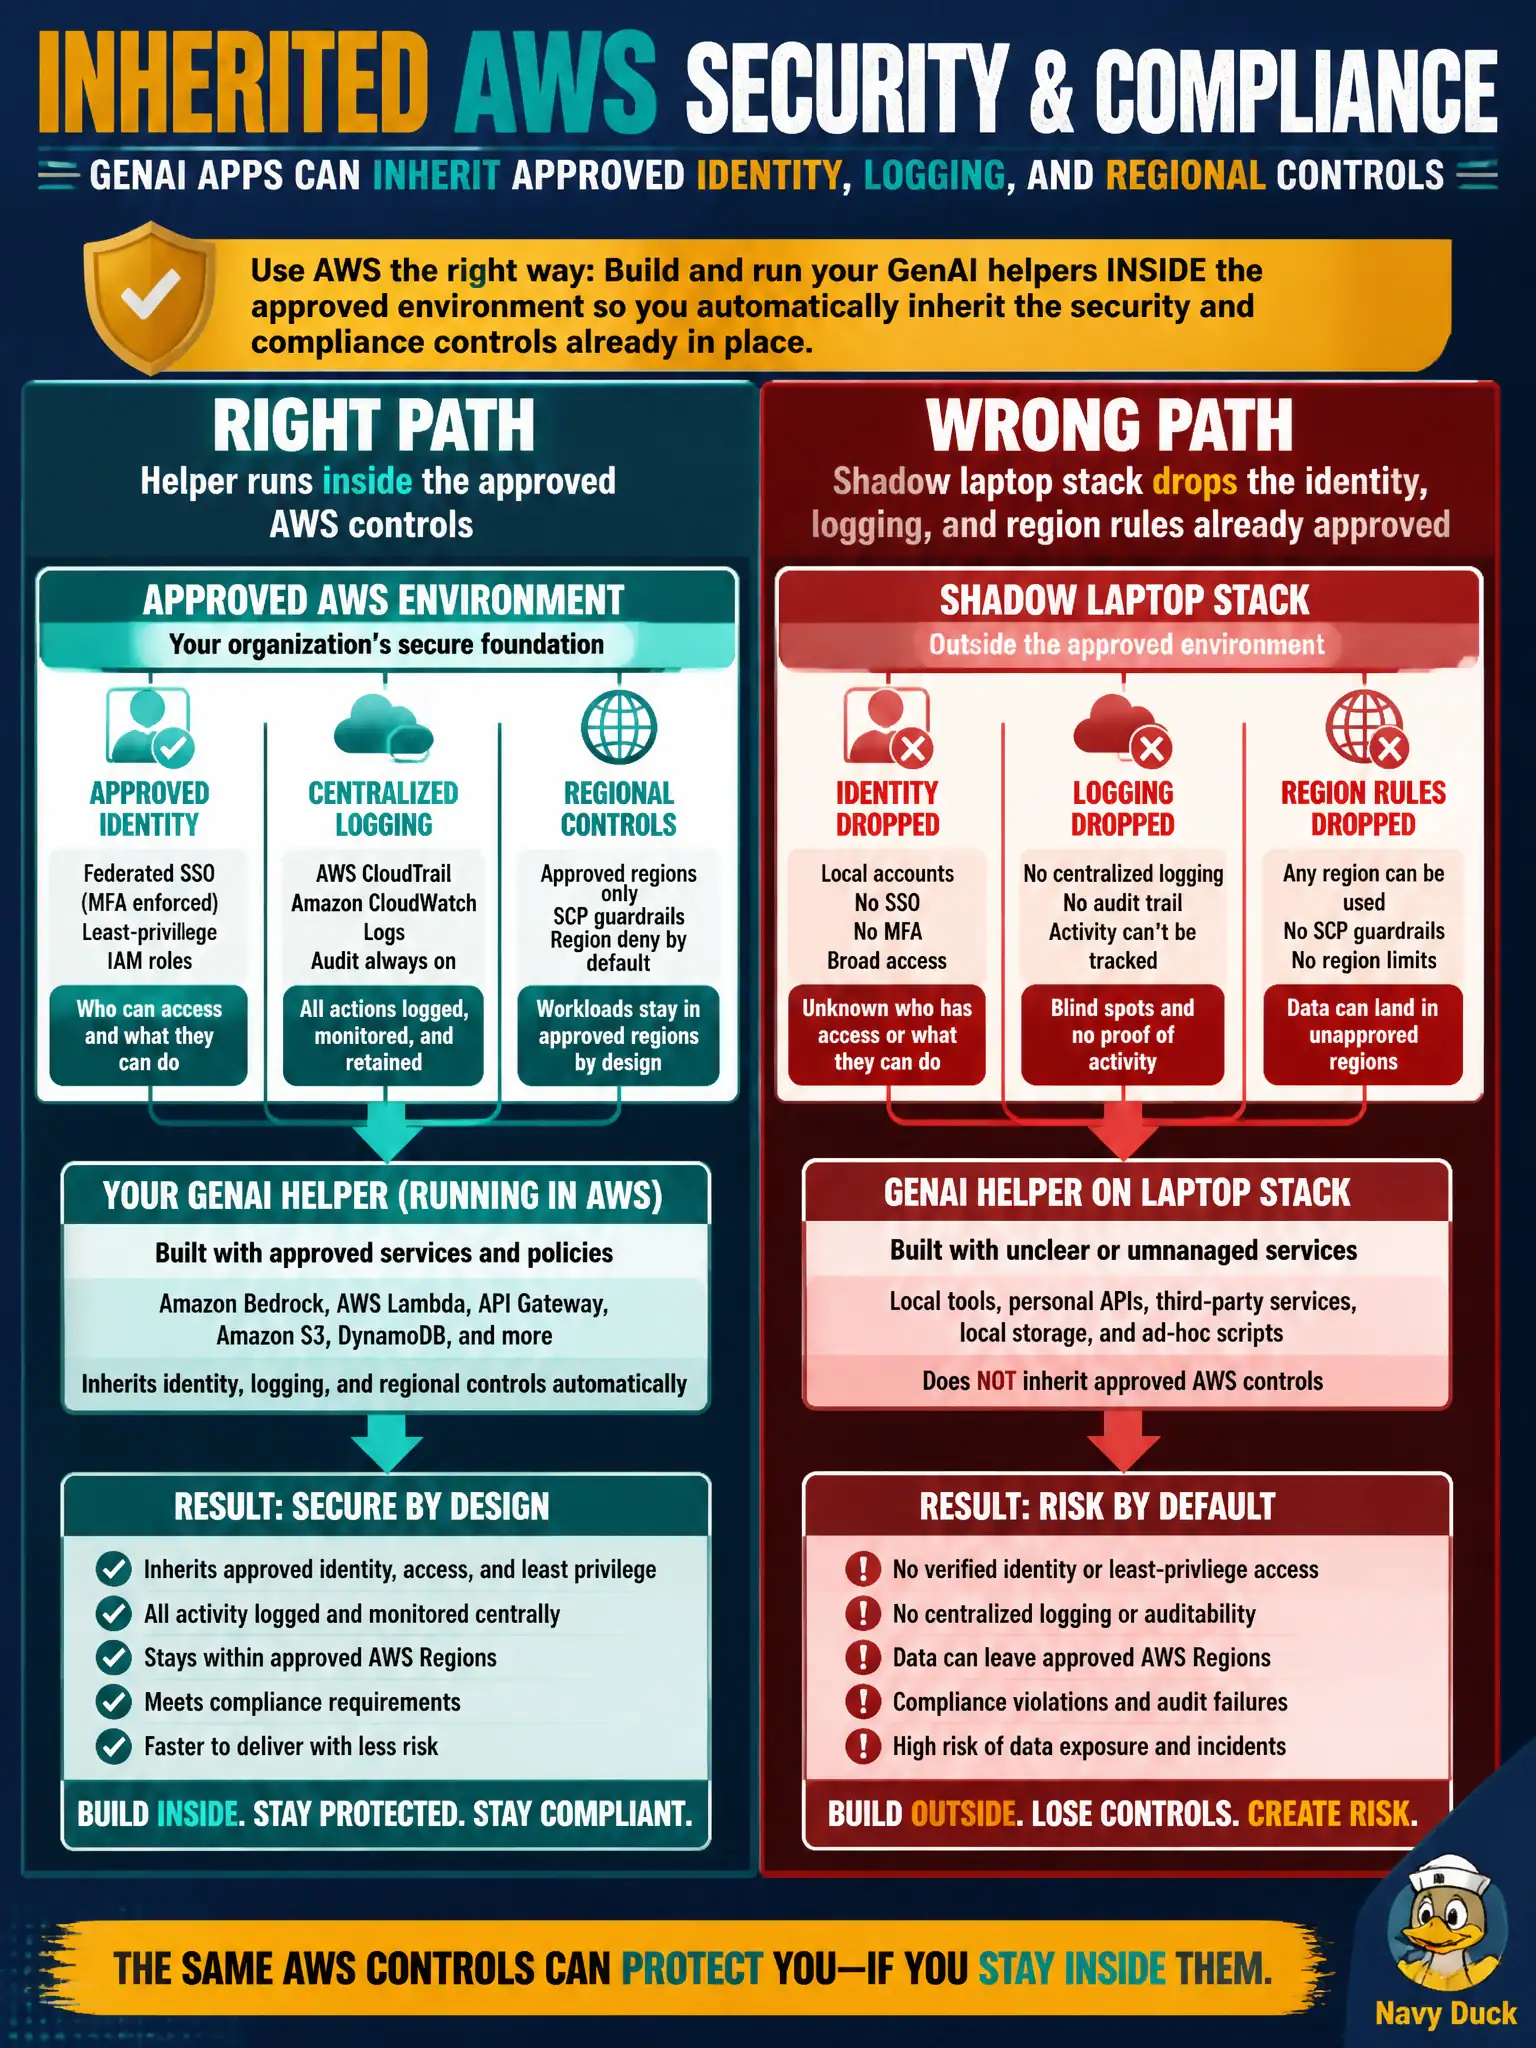
Think of hanging the helper on the same approved AWS identity, logging, and region rules the creamery already has. Inherit those controls. A shadow laptop stack drops them, and this is not a Domain 5 essay.
Full Explanation
Security and compliance of AWS infrastructure that the app can inherit is the Domain 2 advantage when a creamery already has approved identity, logging, and regional controls and wants its GenAI helper on that path instead of a shadow laptop stack. Building on the same governed cloud footprint reuses controls the organization already trusts and keeps the helper inside the approved boundary.
Standing up a shadow stack outside approved controls drops the inheritance benefit and creates an unmanaged twin that auditors will not treat as equivalent. Writing a Domain 5 shared-responsibility essay is not what this item asks; the question targets the Domain 2 benefit of inheriting infrastructure controls. A Guardrails how-to that lists every filter rule is a content-filter configuration deep-dive, not the inheritance advantage described here.
Exam caveat: inheriting account controls does not automatically classify prompts or redact sensitive dairy-customer data—you still design application-layer protections. Operational check: deploy the helper into the approved account and region, verify logging coverage for invocations, reject any laptop-side production path that bypasses corporate IAM, and confirm regional residency matches creamery policy.