
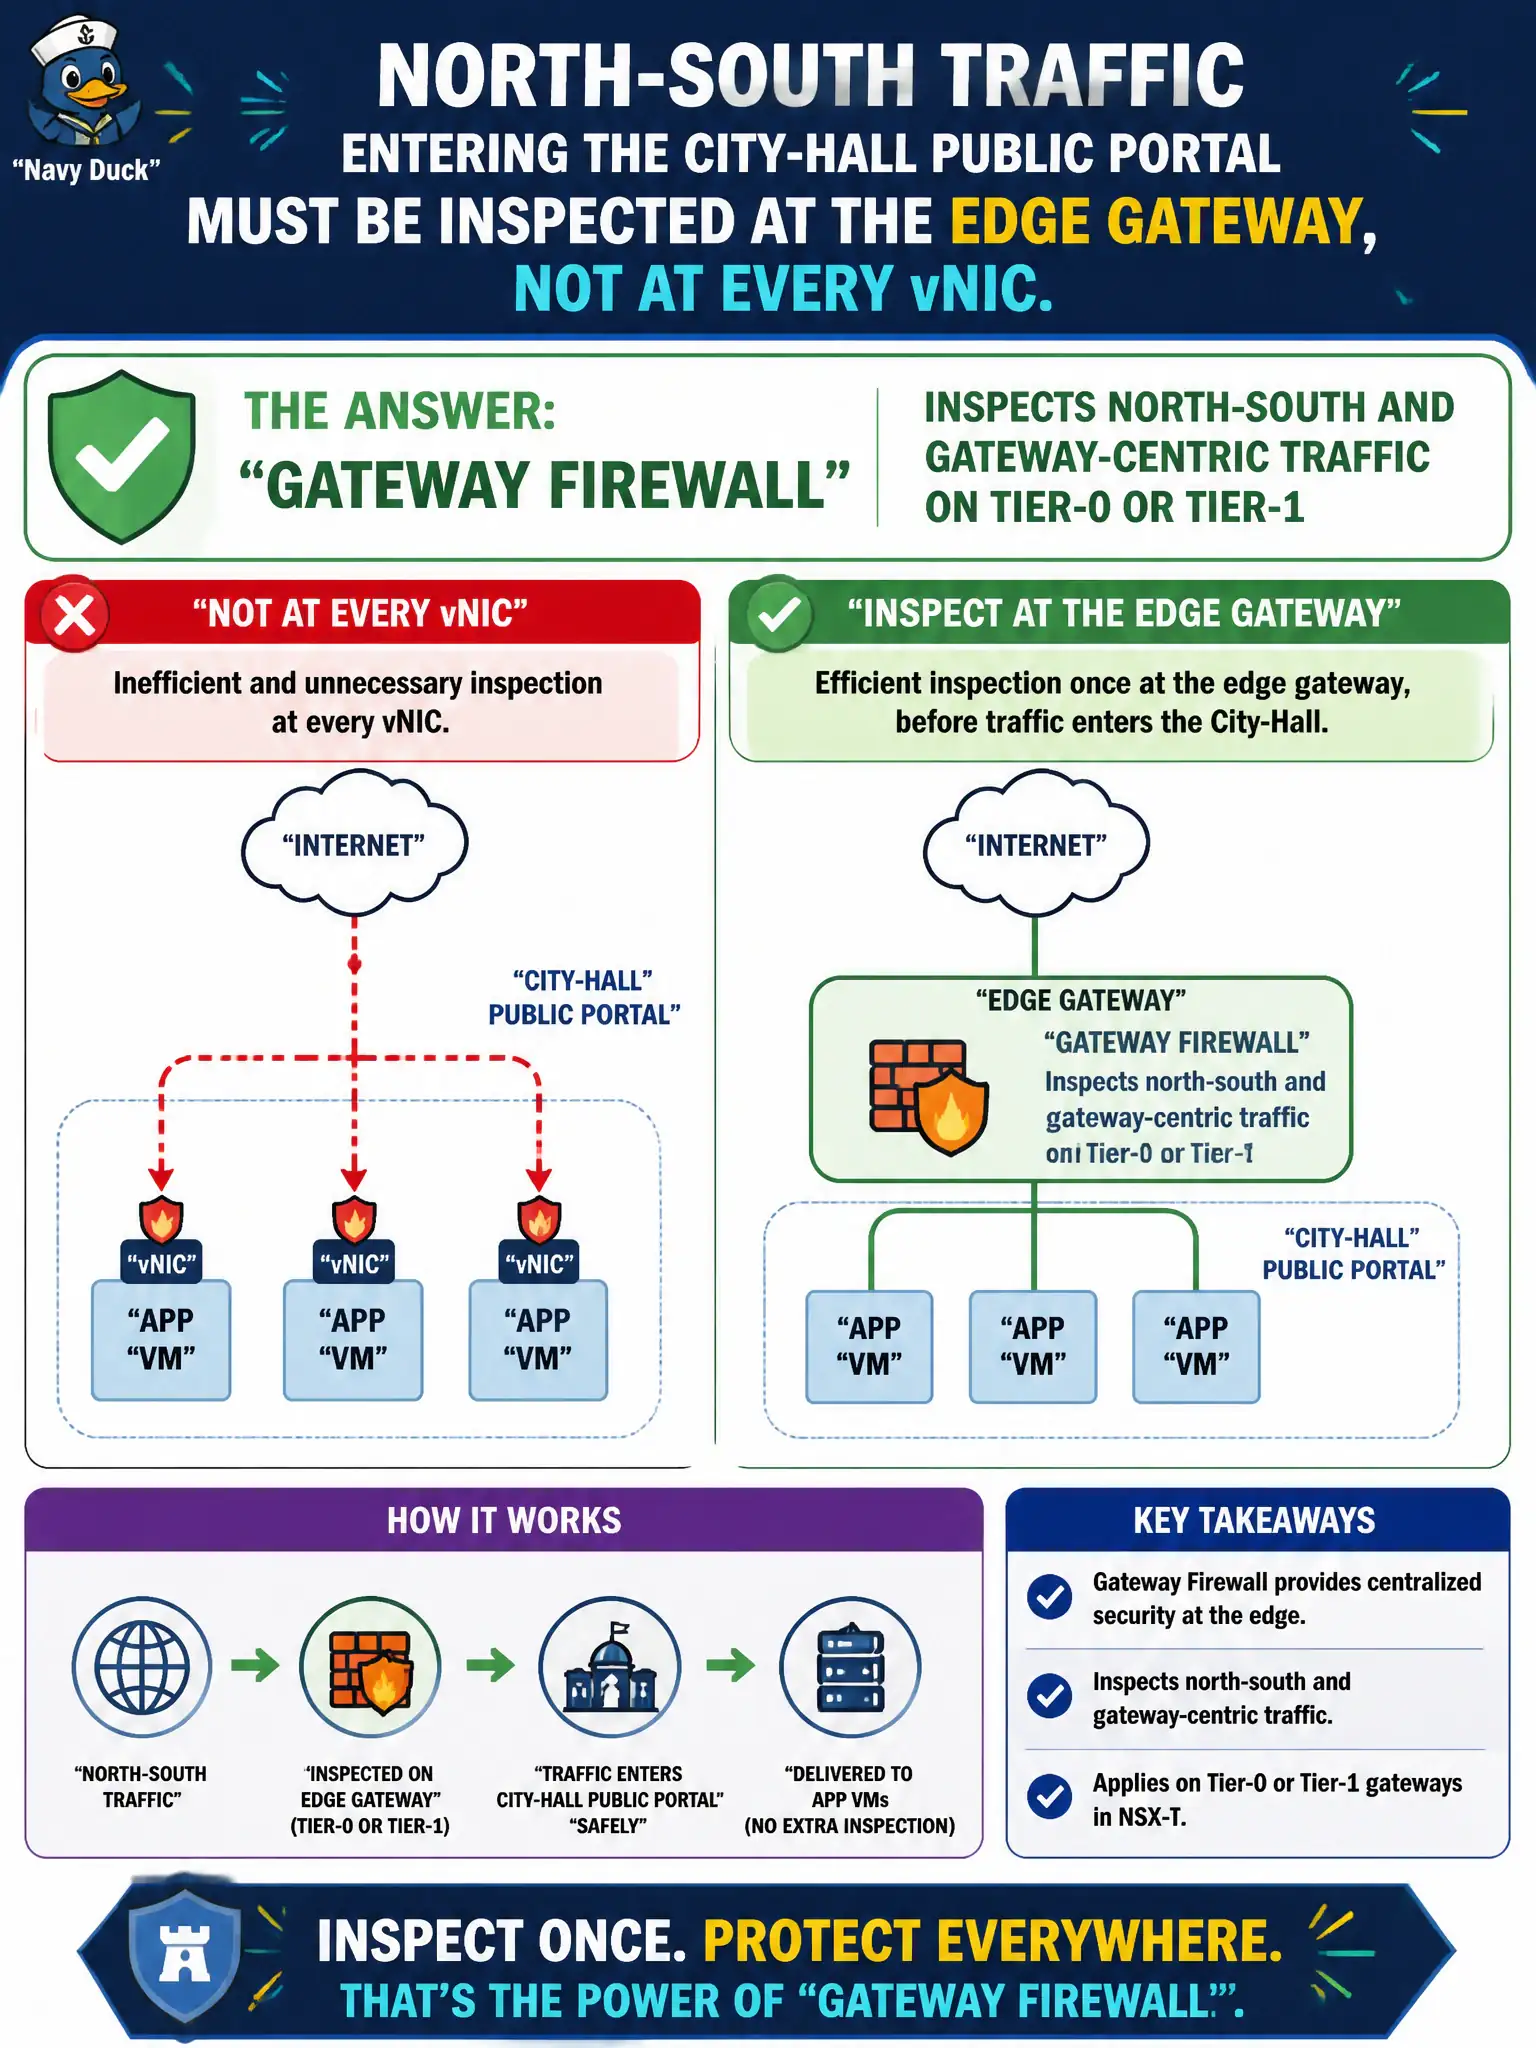
North-south traffic entering the city-hall public portal must be inspected at the edge gateway, not at every vNIC. Which NSX-T feature is that?
Select an answer to reveal the explanation.
Short Explanation
Think of gateway firewall as the city-hall front door and Distributed Firewall as the locks on each office. North-south inspection at the edge is the front door. DRS and vCenter HA do not filter those packets.
Full Explanation
Gateway firewall inspects north-south and other gateway-centric traffic on Tier-0 or Tier-1, which is distinct from Distributed Firewall at the vNIC. Think of gateway firewall as the city-hall front door and Distributed Firewall as the locks on each office—north-south inspection for the public portal is the front door. Distributed Firewall is the east-west micro-segmentation engine and is not the only north-south gateway inspector for this item. vSphere DRS balances compute placement and is not a packet filter. vCenter HA restarts VMs and is not an edge firewall. Exam caveat: many designs use both DFW and gateway firewall; when the stem says inspect at the edge gateway rather than at every vNIC, the feature is gateway firewall. Operational check: apply a gateway firewall rule on the relevant Tier-0 or Tier-1 for portal north-south traffic, confirm hits on that path, and ensure DRS and vCenter HA were not named as the inspector. Document the civic rationale in the change record so the next operator can restate why the correct control matches the agency outcome, why each distractor fails by concept, and which NSX Manager view confirms the result after publish. Document the civic rationale in the change record so the next operator can restate why the correct control matches the agency outcome, why each distractor fails by concept, and which NSX Manager view confirms the result after publish.