
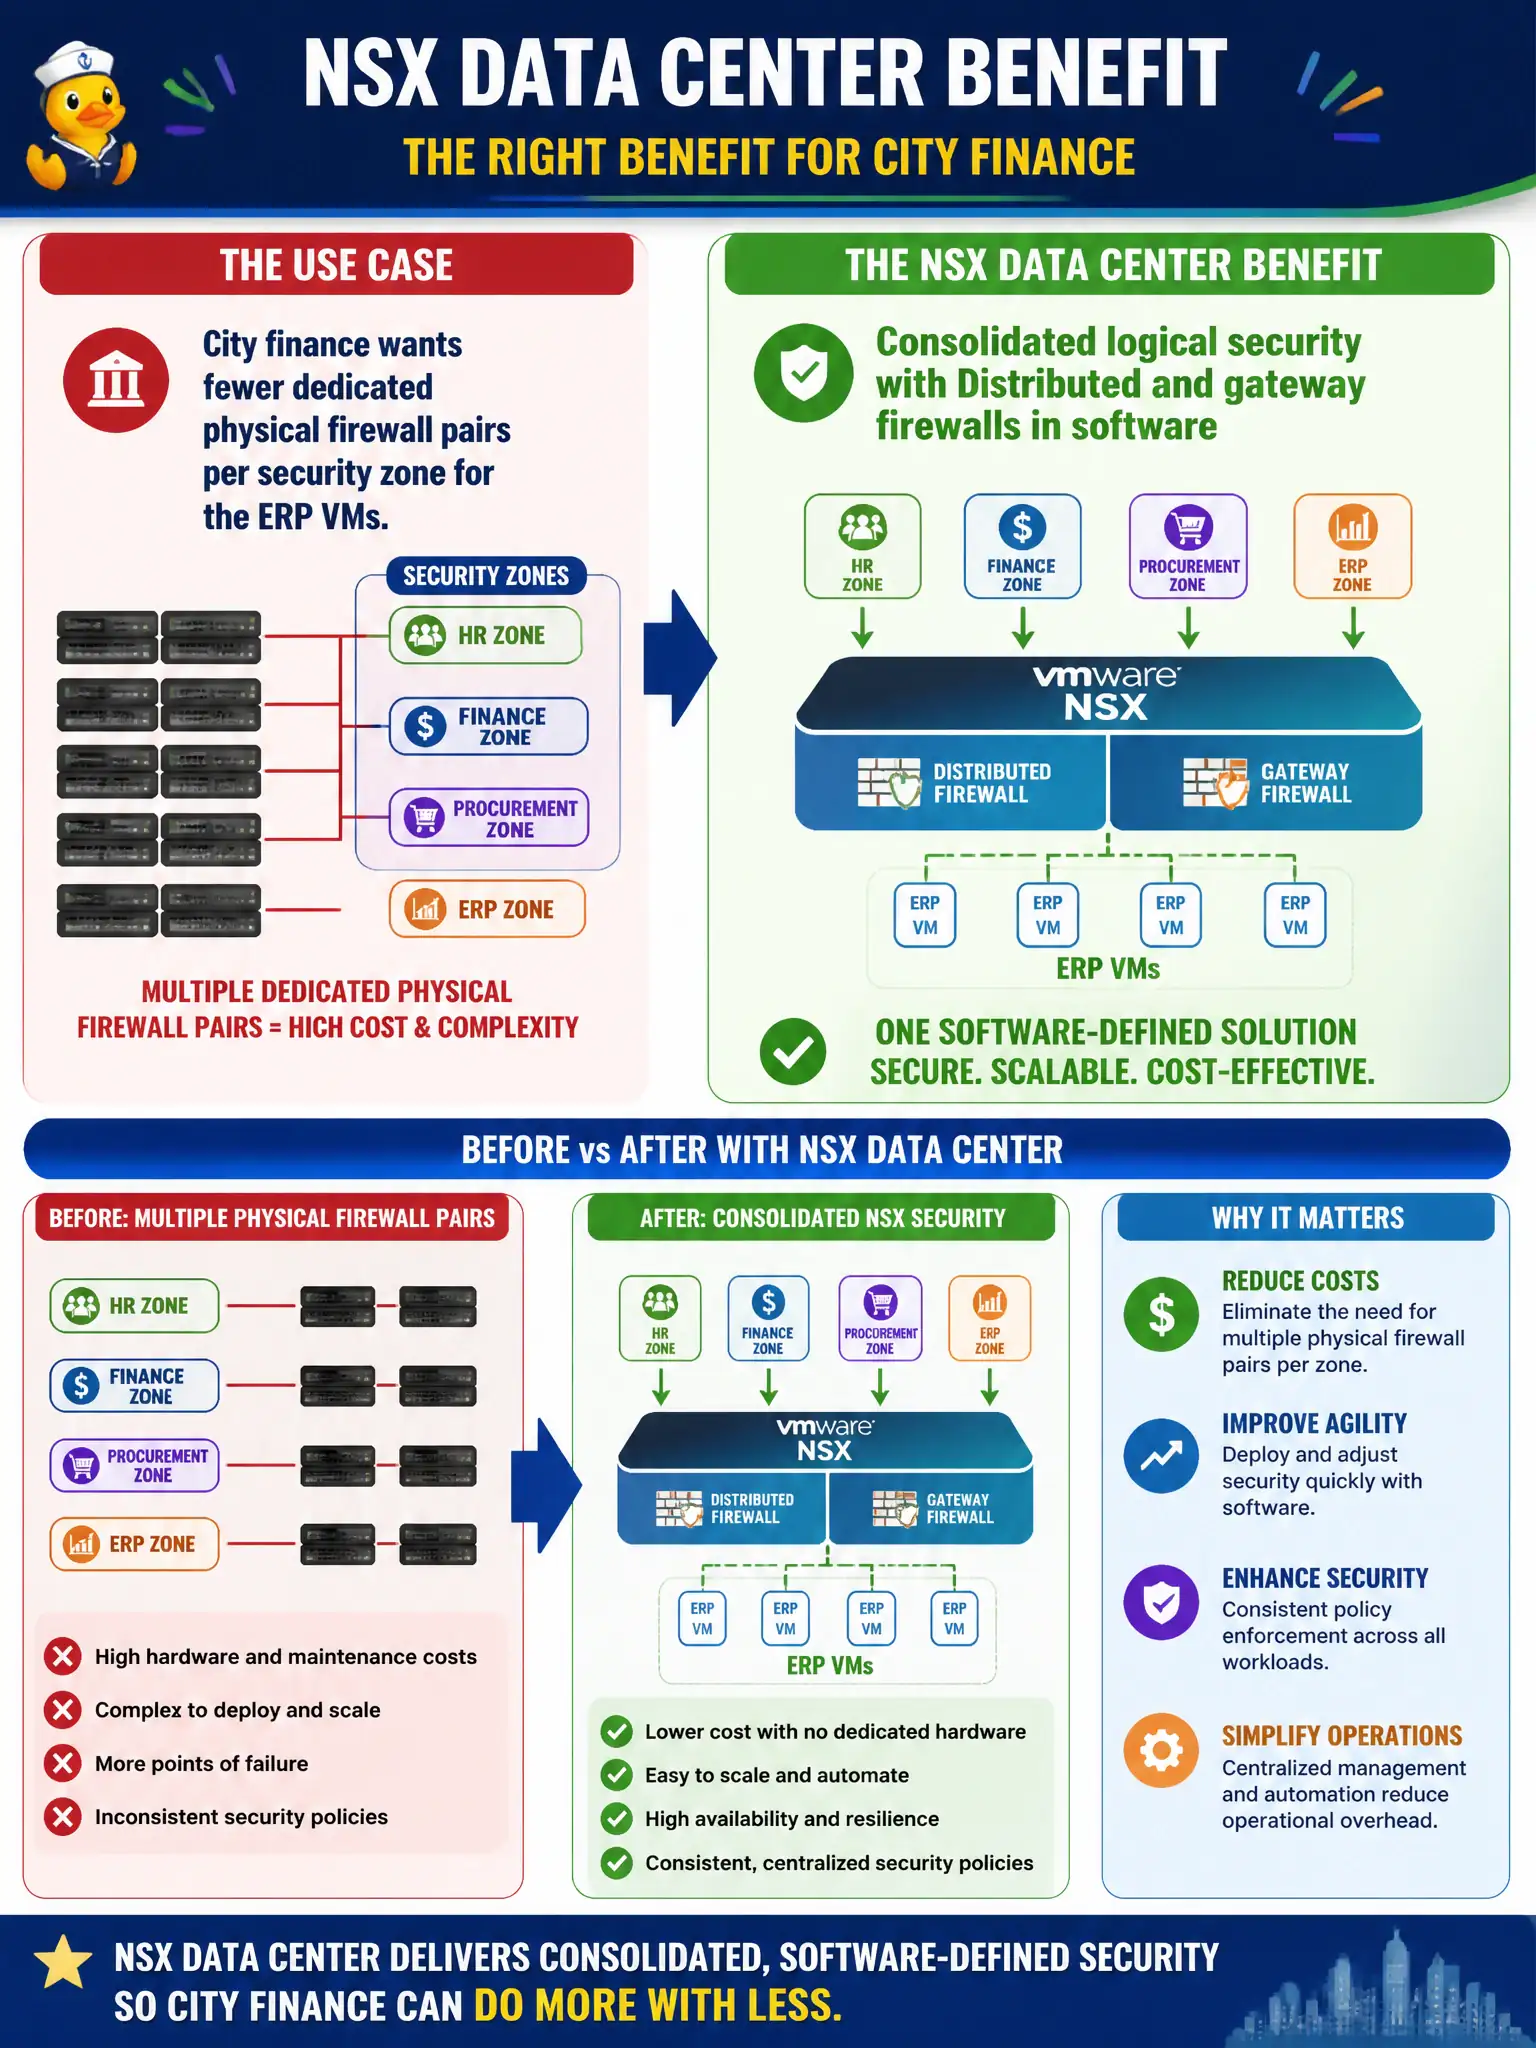
City finance wants fewer dedicated physical firewall pairs per security zone for the ERP VMs. Which NSX Data Center benefit matches that use case?
Select an answer to reveal the explanation.
Short Explanation
Fewer hardware firewall pairs does not mean no security. NSX folds zone controls into software at the vNIC and gateway. vSAN checksums are storage integrity, not a firewall.
Full Explanation
Reducing dedicated physical firewall pairs per security zone for ERP VMs aligns with consolidated logical security using Distributed and gateway firewalls in software. NSX can enforce east-west and selected north-south policy without buying a new hardware pair for every zone carve-out in city finance. Removing all security inspection from the civic data center is not a benefit; it is a control failure. Buying one extra hardware firewall pair for every new ERP VM scales cost and operational burden the wrong way. Using vSAN checksums as an east-west firewall confuses storage integrity with packet filtering. Exam caveat: consolidation does not mean zero firewalls; it means policy is expressed as NSX objects while retaining a selective hardware perimeter where compliance still requires it. Operational check: map ERP tiers to NSX groups, migrate east-west rules from a hairpinned hardware pair onto DFW, keep Tier-0 or Tier-1 gateway firewall for north-south, and measure whether hairpin traffic volume drops without widening allow-any posture before presenting diagrams to the civic CAB. In municipal operations, record the chosen control and the rejected distractors in the change ticket so future on-call staff understand which failure modes would affect city services. Re-validate after the next maintenance window that the same design still holds for the current NSX build and the agency workloads that depend on it.