
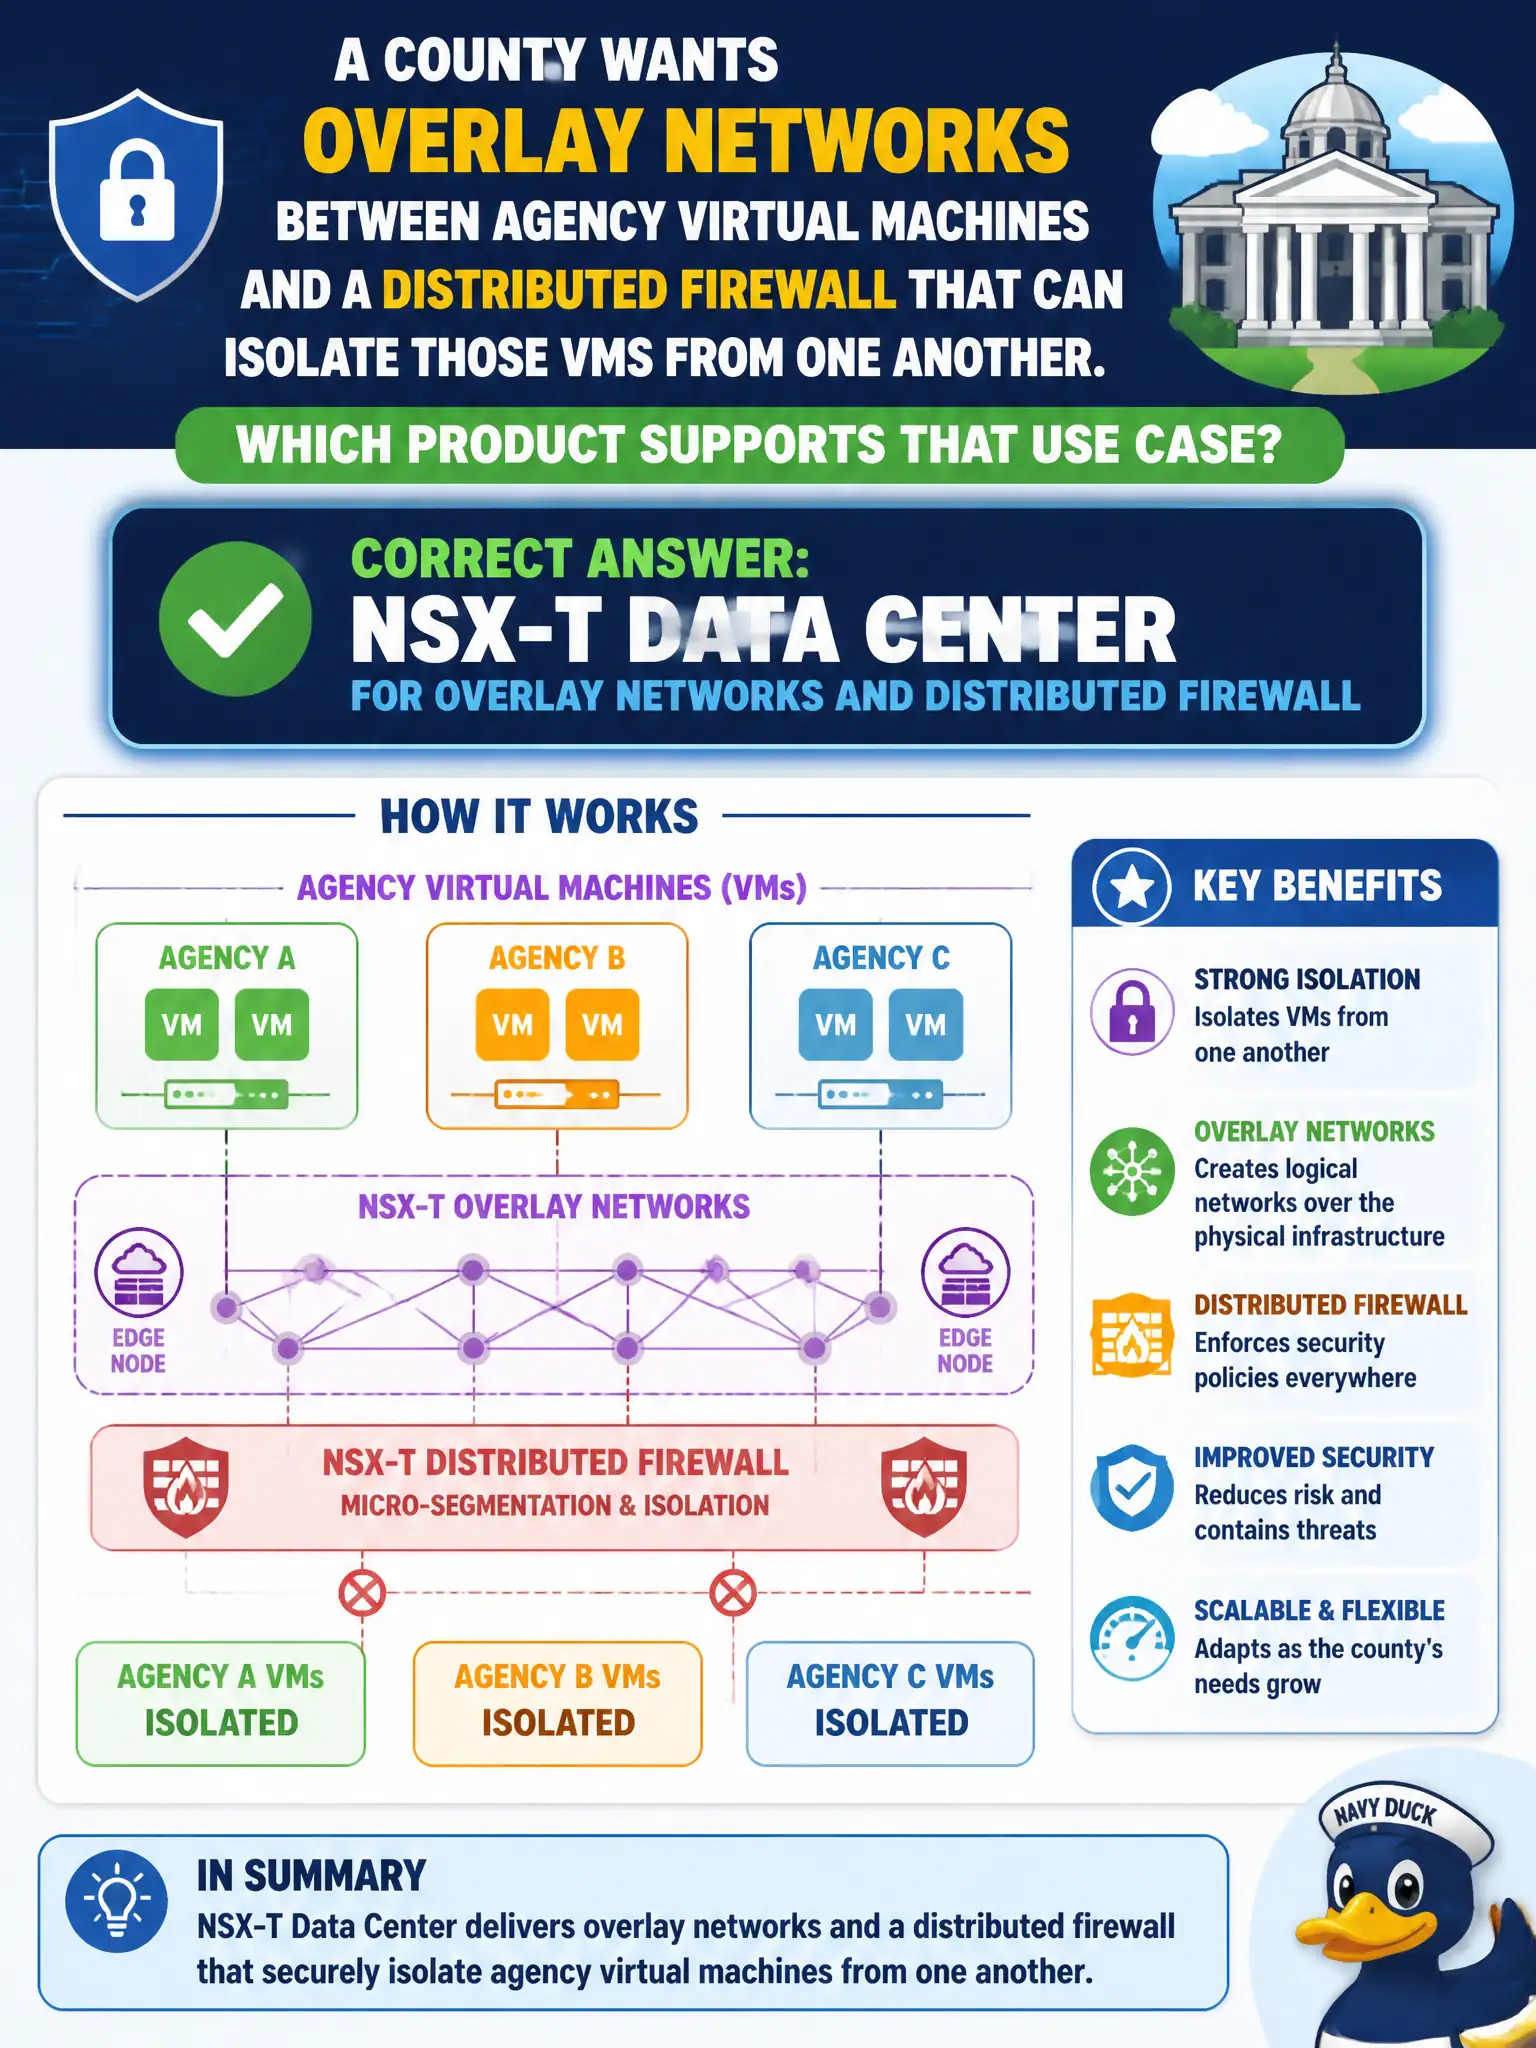
A county wants overlay networks between agency virtual machines and a distributed firewall that can isolate those VMs from one another. Which product supports that use case?
Select an answer to reveal the explanation.
Short Explanation
Overlay plus east-west firewall between agency VMs is the NSX-T job. vSAN is storage and Horizon is desktops. A standard-switch VLAN can tag a port group, but it is not the county's overlay and Distributed Firewall product.
Full Explanation
A county that wants overlay networks between agency virtual machines and a distributed firewall that can isolate those VMs from one another needs NSX-T Data Center for overlay networks and Distributed Firewall. Overlay plus east-west firewall between agency VMs is the NSX-T job in the civic security and network design. vSAN as the overlay and distributed-firewall fabric is wrong—vSAN is software-defined storage and does not implement Geneve segments or DFW. Horizon as the network-virtualization platform is wrong—Horizon is end-user computing for desktops and apps. vSphere Standard Switch VLAN tagging as the only required product can separate port groups with VLANs but is not the county’s overlay-plus-Distributed-Firewall platform for micro-segmentation at scale. Exam caveat: VLAN isolation on a VSS/VDS is still useful underlay hygiene; it does not equal Geneve overlay micro-segmentation with NSX DFW. Associate questions often pair overlay and DFW as the signature NSX use case. Operational check: prepare agency hosts as transport nodes, attach agency VMs to overlay segments, and enforce Distributed Firewall rules that deny unnecessary east-west paths while allowing required application flows; validate with a deliberate deny test between two agency tiers.