
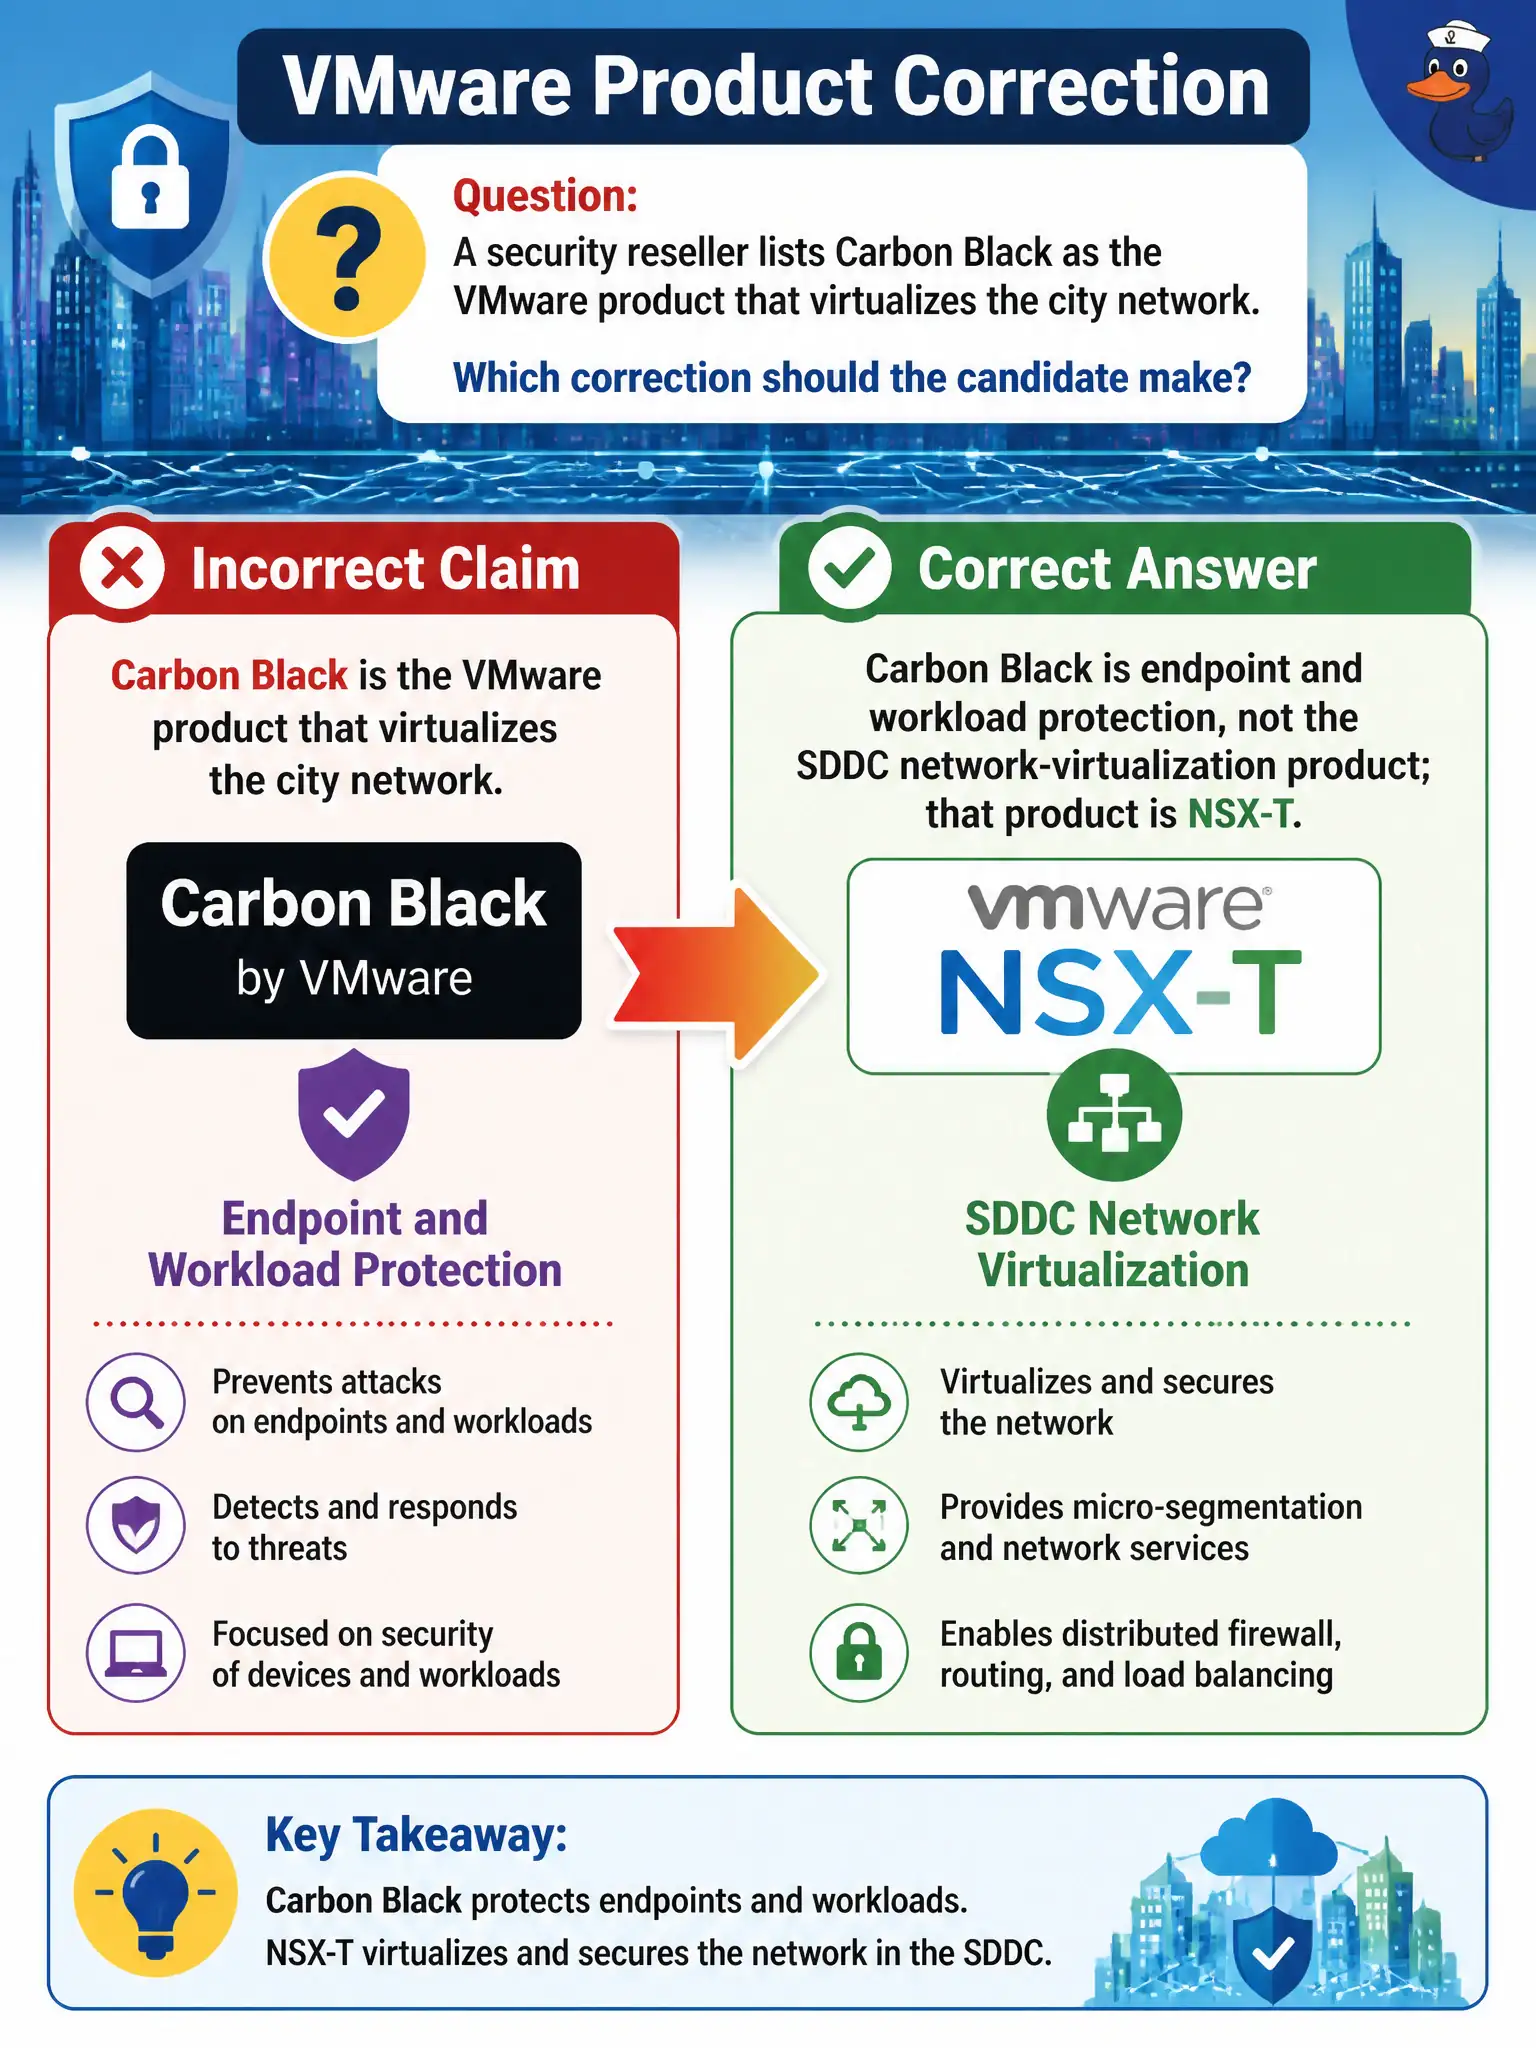
A security reseller lists Carbon Black as the VMware product that virtualizes the city network. Which correction should the candidate make?
Select an answer to reveal the explanation.
Short Explanation
Carbon Black watches laptops and workloads for malware. It does not virtualize the civic network. The network pillar is NSX-T. Carbon Black is not a VDS, a vSAN engine, or Geneve.
Full Explanation
When a security reseller lists Carbon Black as the VMware product that virtualizes the city network, the candidate must correct the product role: Carbon Black is endpoint and workload protection, not the SDDC network-virtualization product; that product is NSX-T. Carbon Black watches laptops and workloads for malware and attack behavior; it does not create overlay segments, Tier gateways, or Distributed Firewall sections for the civic fabric. Carbon Black is not the vSphere Distributed Switch, not the vSAN storage-policy engine, and not the NSX overlay encapsulation format. Those mislabels mix endpoint security with vSphere networking, storage policy, and Geneve tunneling. Exam caveat: Carbon Black and NSX can both appear in a secure civic design—one for endpoint/workload protection, one for network virtualization and micro-segmentation—but they are not interchangeable logos on an SDDC network pillar slide. Associate items often plant familiar security brands as distractors. Operational check: review the security architecture and ensure Carbon Black sensors and consoles are scoped to endpoint protection use cases, while NSX Manager owns segments, gateways, and Distributed Firewall; remove any diagram arrow that claims Carbon Black “is” the virtual network before the architecture board meets. Capture the corrected diagram in the security architecture repo so reseller slides cannot relabel Carbon Black as the civic virtual network again.