
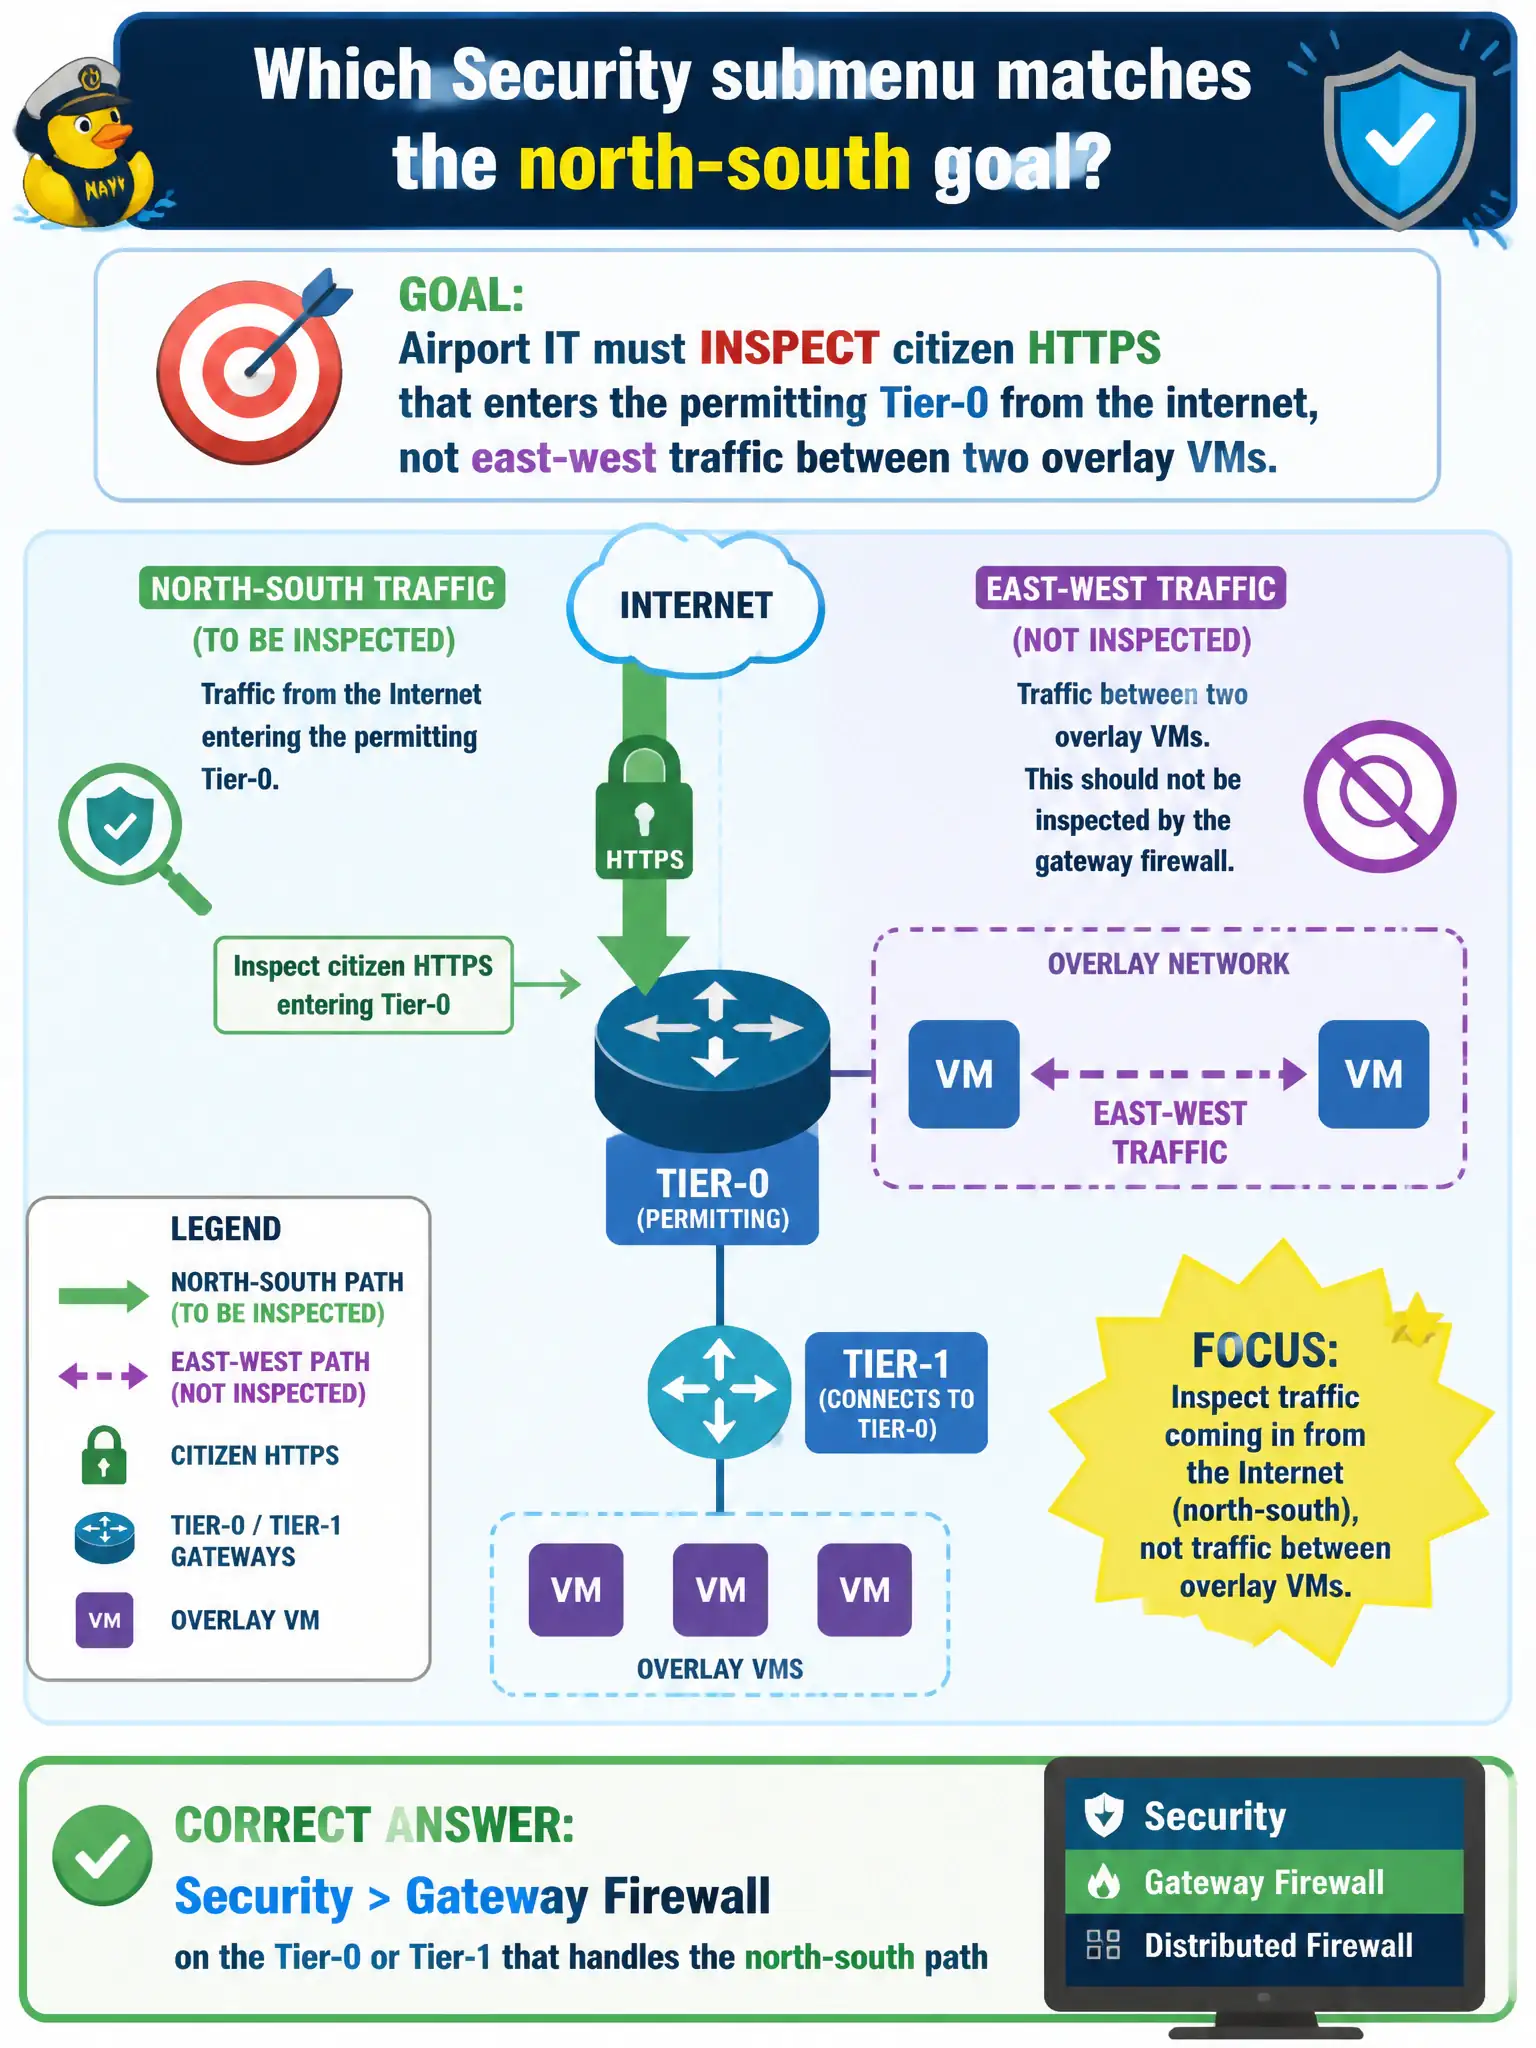
Airport IT must inspect citizen HTTPS that enters the permitting Tier-0 from the internet, not east-west traffic between two overlay VMs. Which Security submenu matches that north-south goal?
Select an answer to reveal the explanation.
Short Explanation
Citizens walking in from the street hit the front door, not the hallway cameras. North-south on the Tier-0 is Gateway Firewall; hallway (VM-to-VM) is Distributed Firewall.
Full Explanation
Airport IT must inspect citizen HTTPS entering the permitting path from the internet—that is north-south traffic on the Tier-0 or Tier-1 gateway path. Security > Gateway Firewall on the Tier-0 or Tier-1 that handles that path is the correct Security submenu for centralized north-south inspection, as opposed to east-west DFW between overlay VMs. Using Distributed Firewall only is conceptually wrong for “all internet is east-west at the vNIC”: inbound internet to the civic VIP/path is north-south through the gateway/Edge services plane; DFW alone does not replace Gateway Firewall for that edge inspection goal. Inventory > Tags are grouping metadata, not the north-south inspection feature. System > Fabric > Nodes lists transport nodes; Gateway Firewall is not merely an Edge VM display name. Exam caveat: Gateway Firewall and Distributed Firewall are complementary—north-south citizen HTTPS and east-west micro-segmentation are different enforcement points; exam items often test which menu matches the traffic direction. Operational check: open Gateway Firewall on the permitting Tier-0/Tier-1, confirm HTTPS rules and logging for the internet-facing path, test from an external probe approved by airport change control, and attach rule hit counts to the security ticket.