
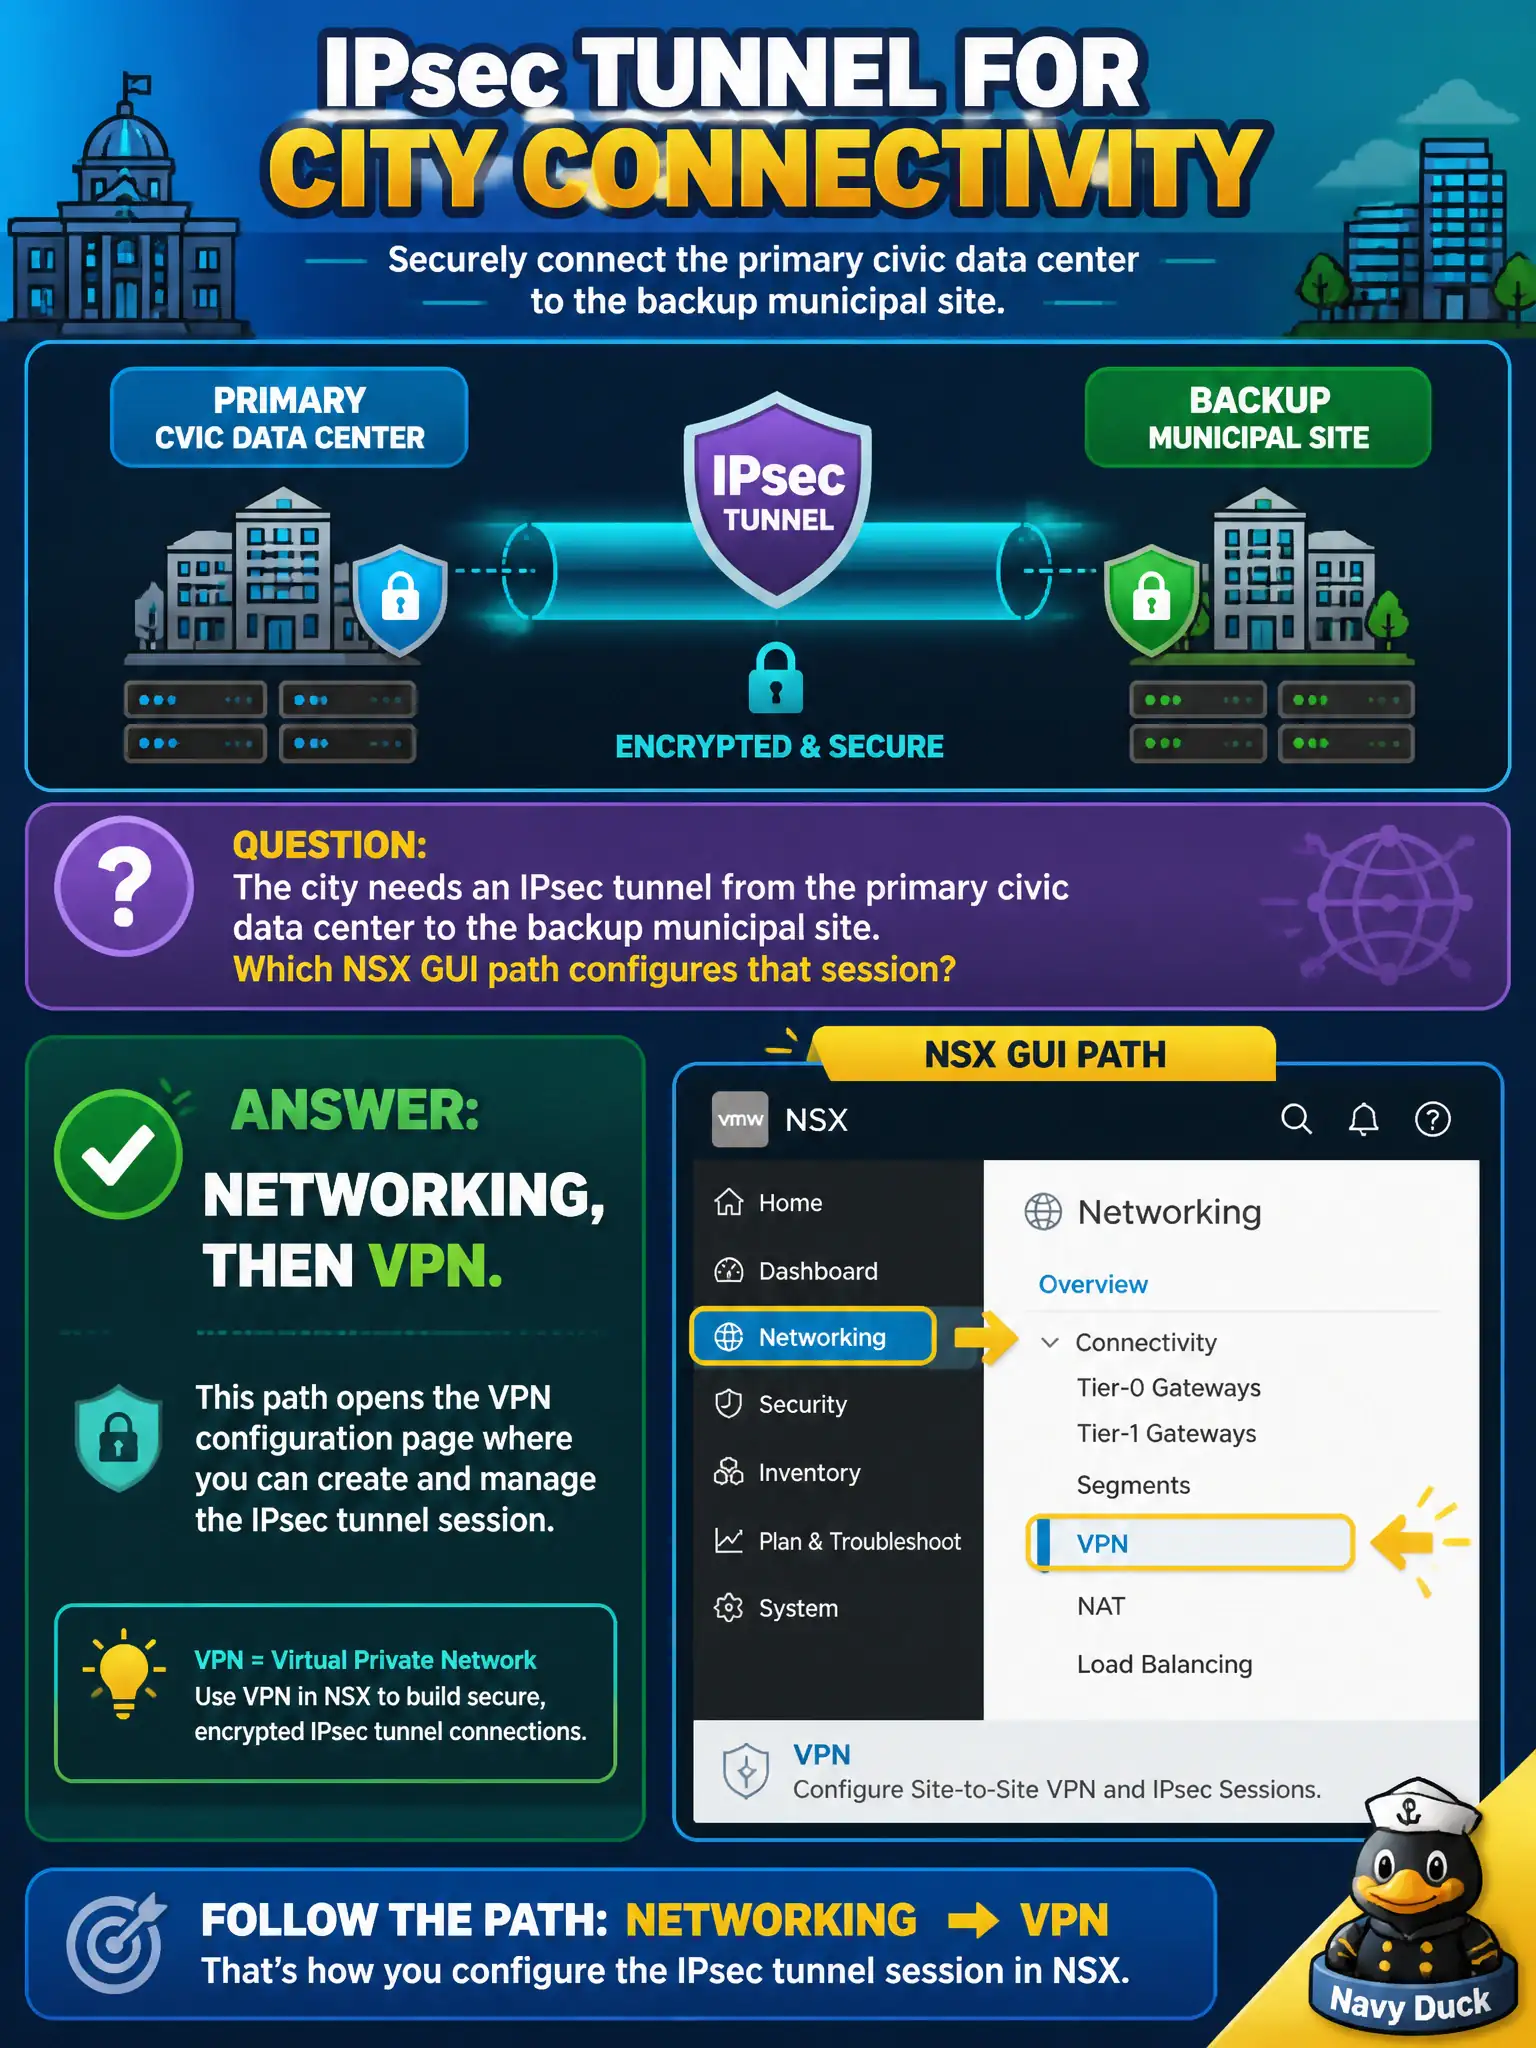
The city needs an IPsec tunnel from the primary civic data center to the backup municipal site. Which NSX GUI path configures that session?
Select an answer to reveal the explanation.
Short Explanation
A sealed road between two civic halls is a VPN session, and NSX keeps that under Networking, then VPN. DFW has no IPsec category, and Horizon or Carbon Black is the wrong office.
Full Explanation
Policy-mode IPsec and related VPN sessions are configured under Networking, then VPN, typically on a Tier-0 that has Edge services, for the tunnel from the primary civic data center to the backup municipal site. A sealed road between two civic halls is a VPN session kept under Networking VPN. Distributed Firewall has no IPsec category. Unified Access Gateway may terminate EUC remote access, but it is not the NSX site-to-site VPN GUI. Carbon Black Network Isolation is an endpoint control, not NSX VPN. Exam caveat: VPN is an Edge-centralized service; do not look under DFW categories for IPsec site-to-site. Operational check: open Networking VPN, configure the IPsec session toward the backup site, bring the tunnel up, pass a test flow, and reject DFW IPsec categories, Horizon UAG, and Carbon Black as the configure path. Document the civic rationale in the change record so the next operator can restate why the correct control matches the agency outcome, why each distractor fails by concept, and which NSX Manager view confirms the result after publish. Document the civic rationale in the change record so the next operator can restate why the correct control matches the agency outcome, why each distractor fails by concept, and which NSX Manager view confirms the result after publish.