
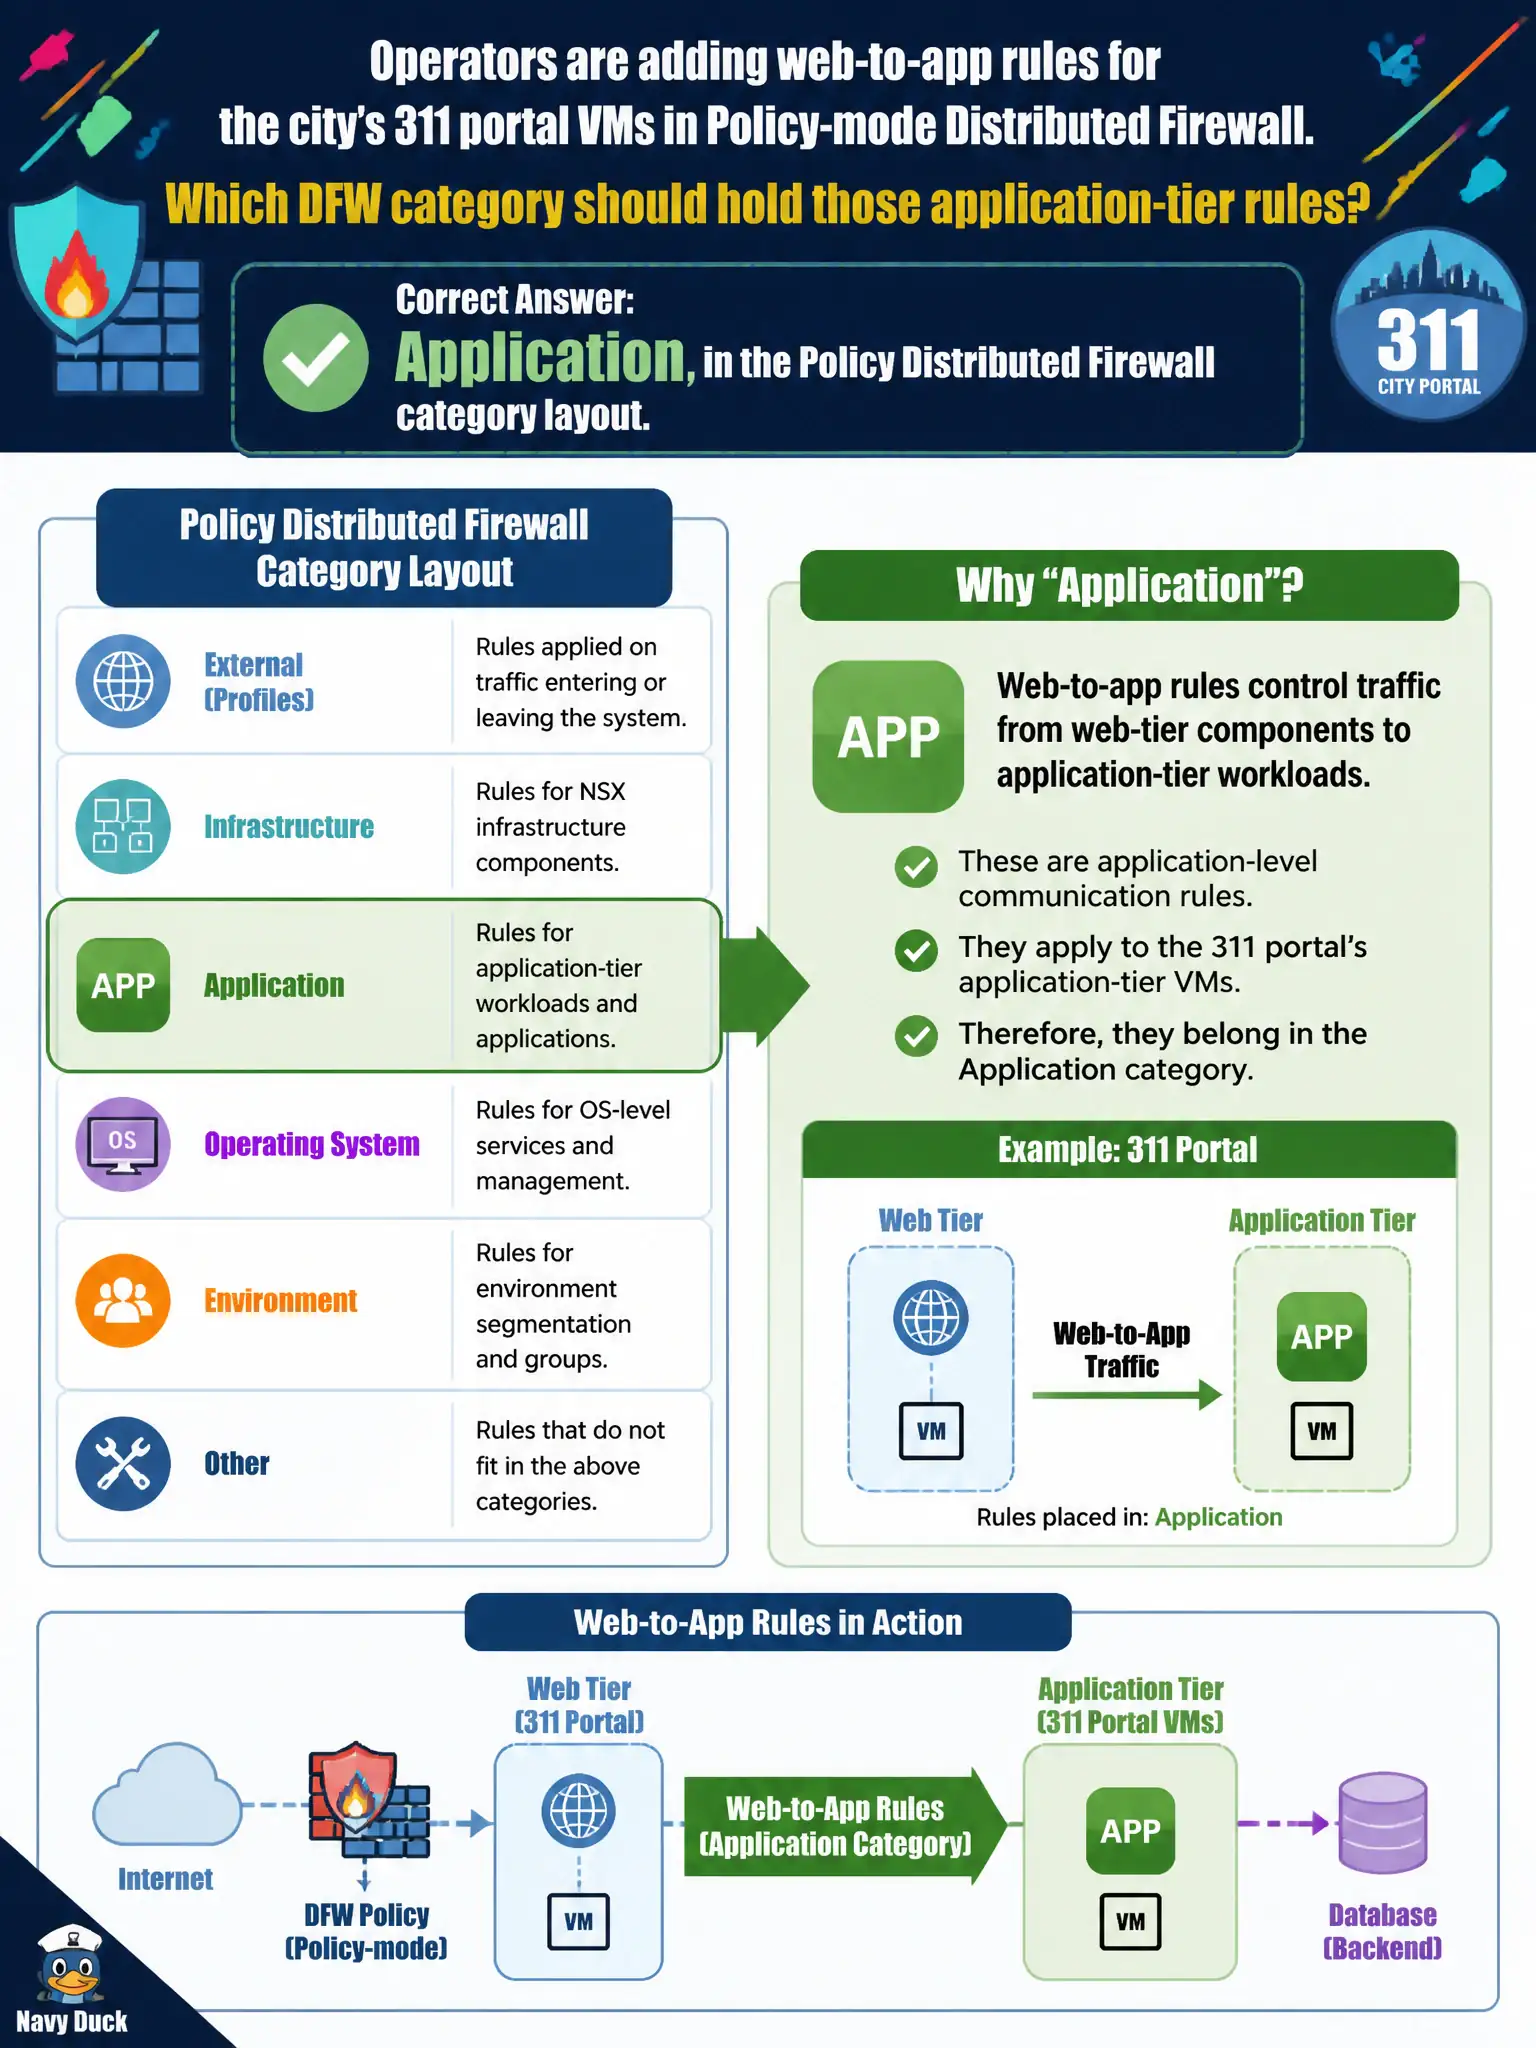
Operators are adding web-to-app rules for the city's 311 portal VMs in Policy-mode Distributed Firewall. Which DFW category should hold those application-tier rules?
Select an answer to reveal the explanation.
Short Explanation
Web-to-app for 311 is the application conversation, so it goes in the Application drawer. Ethernet is L2, Emergency is the break-glass stack, and Gateway Firewall is a different product surface.
Full Explanation
Policy-mode Distributed Firewall organizes policies into Ethernet, Emergency, Infrastructure, Environment, and Application categories. Web-to-app rules for the city's 311 portal belong in Application—the application conversation drawer. Ethernet is for Layer 2 rules, not the only place HTTP can match. Gateway Firewall Infrastructure is not a DFW category for east-west application tiers. Emergency is reserved for preempting policies and should not hold every civic application rule. Exam caveat: category order and precedence matter in Policy DFW; putting app-tier rules in Emergency or Ethernet is a common distractor. Operational check: add the 311 web-to-app rules in the Application category, publish, confirm hits on application flows, and verify they were not placed under Ethernet, Emergency-only, or Gateway Firewall Infrastructure. Document the civic rationale in the change record so the next operator can restate why the correct control matches the agency outcome, why each distractor fails by concept, and which NSX Manager view confirms the result after publish. Document the civic rationale in the change record so the next operator can restate why the correct control matches the agency outcome, why each distractor fails by concept, and which NSX Manager view confirms the result after publish.