
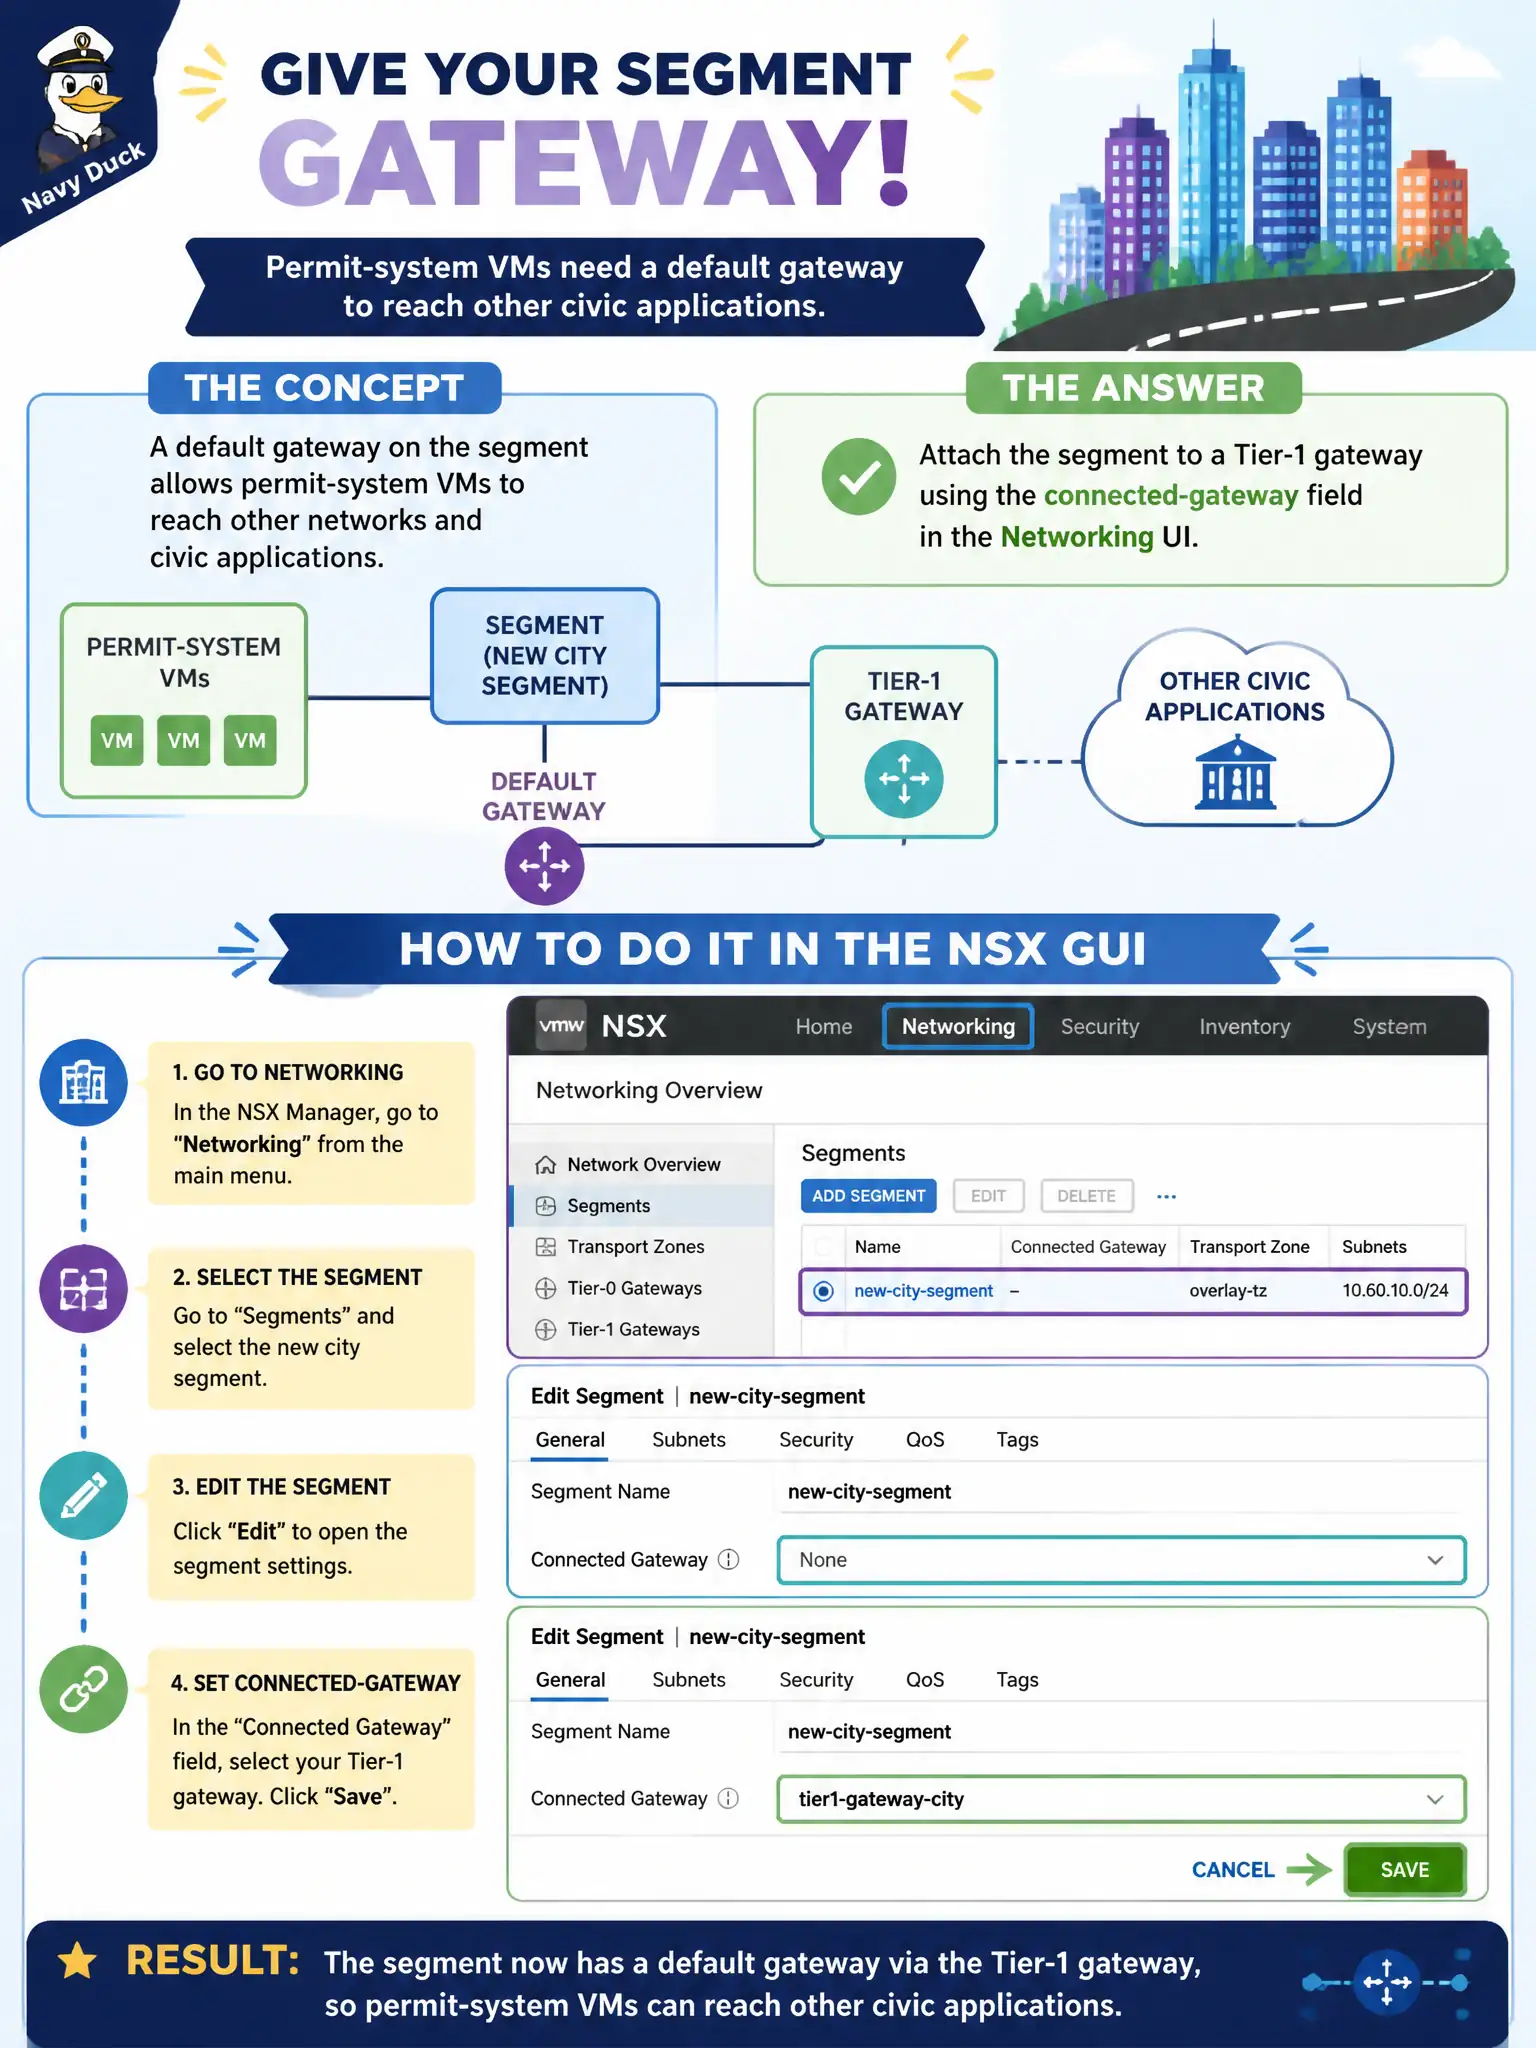
Permit-system VMs on a new city segment need a default gateway so they can reach other civic applications. How should the operator give that segment a gateway in the NSX GUI?
Select an answer to reveal the explanation.
Short Explanation
Those permit VMs need a software on-ramp, not a midnight SSH to a physical core. Hook the segment to a Tier-1 in the Networking UI. A vSAN policy or a DFW allow rule is not a default gateway.
Full Explanation
In the Policy Networking UI, a segment receives a gateway by connecting to a Tier-1, or to a Tier-0 in a single-tier design, through the connected-gateway field. Permit-system VMs need that software on-ramp so they can reach other civic applications—not a midnight SSH to a physical core hoping NSX discovers a static route. Physical-router CLI is not the NSX method. vSAN storage policies do not route packets. Distributed Firewall Emergency rules filter traffic; they do not provide a default gateway. Exam caveat: connected-gateway on the segment is the Policy association; ensure the Tier-1 or Tier-0 already exists and is healthy before expecting VM default-gateway reachability. Operational check: set the permit segment's connected gateway to the intended Tier-1, boot a test VM with the gateway address, confirm northbound reachability, and verify physical CLI, vSAN policies, and DFW Emergency rules were not used as the gateway. Document the civic rationale in the change record so the next operator can restate why the correct control matches the agency outcome, why each distractor fails by concept, and which NSX Manager view confirms the result after publish. Document the civic rationale in the change record so the next operator can restate why the correct control matches the agency outcome, why each distractor fails by concept, and which NSX Manager view confirms the result after publish.