
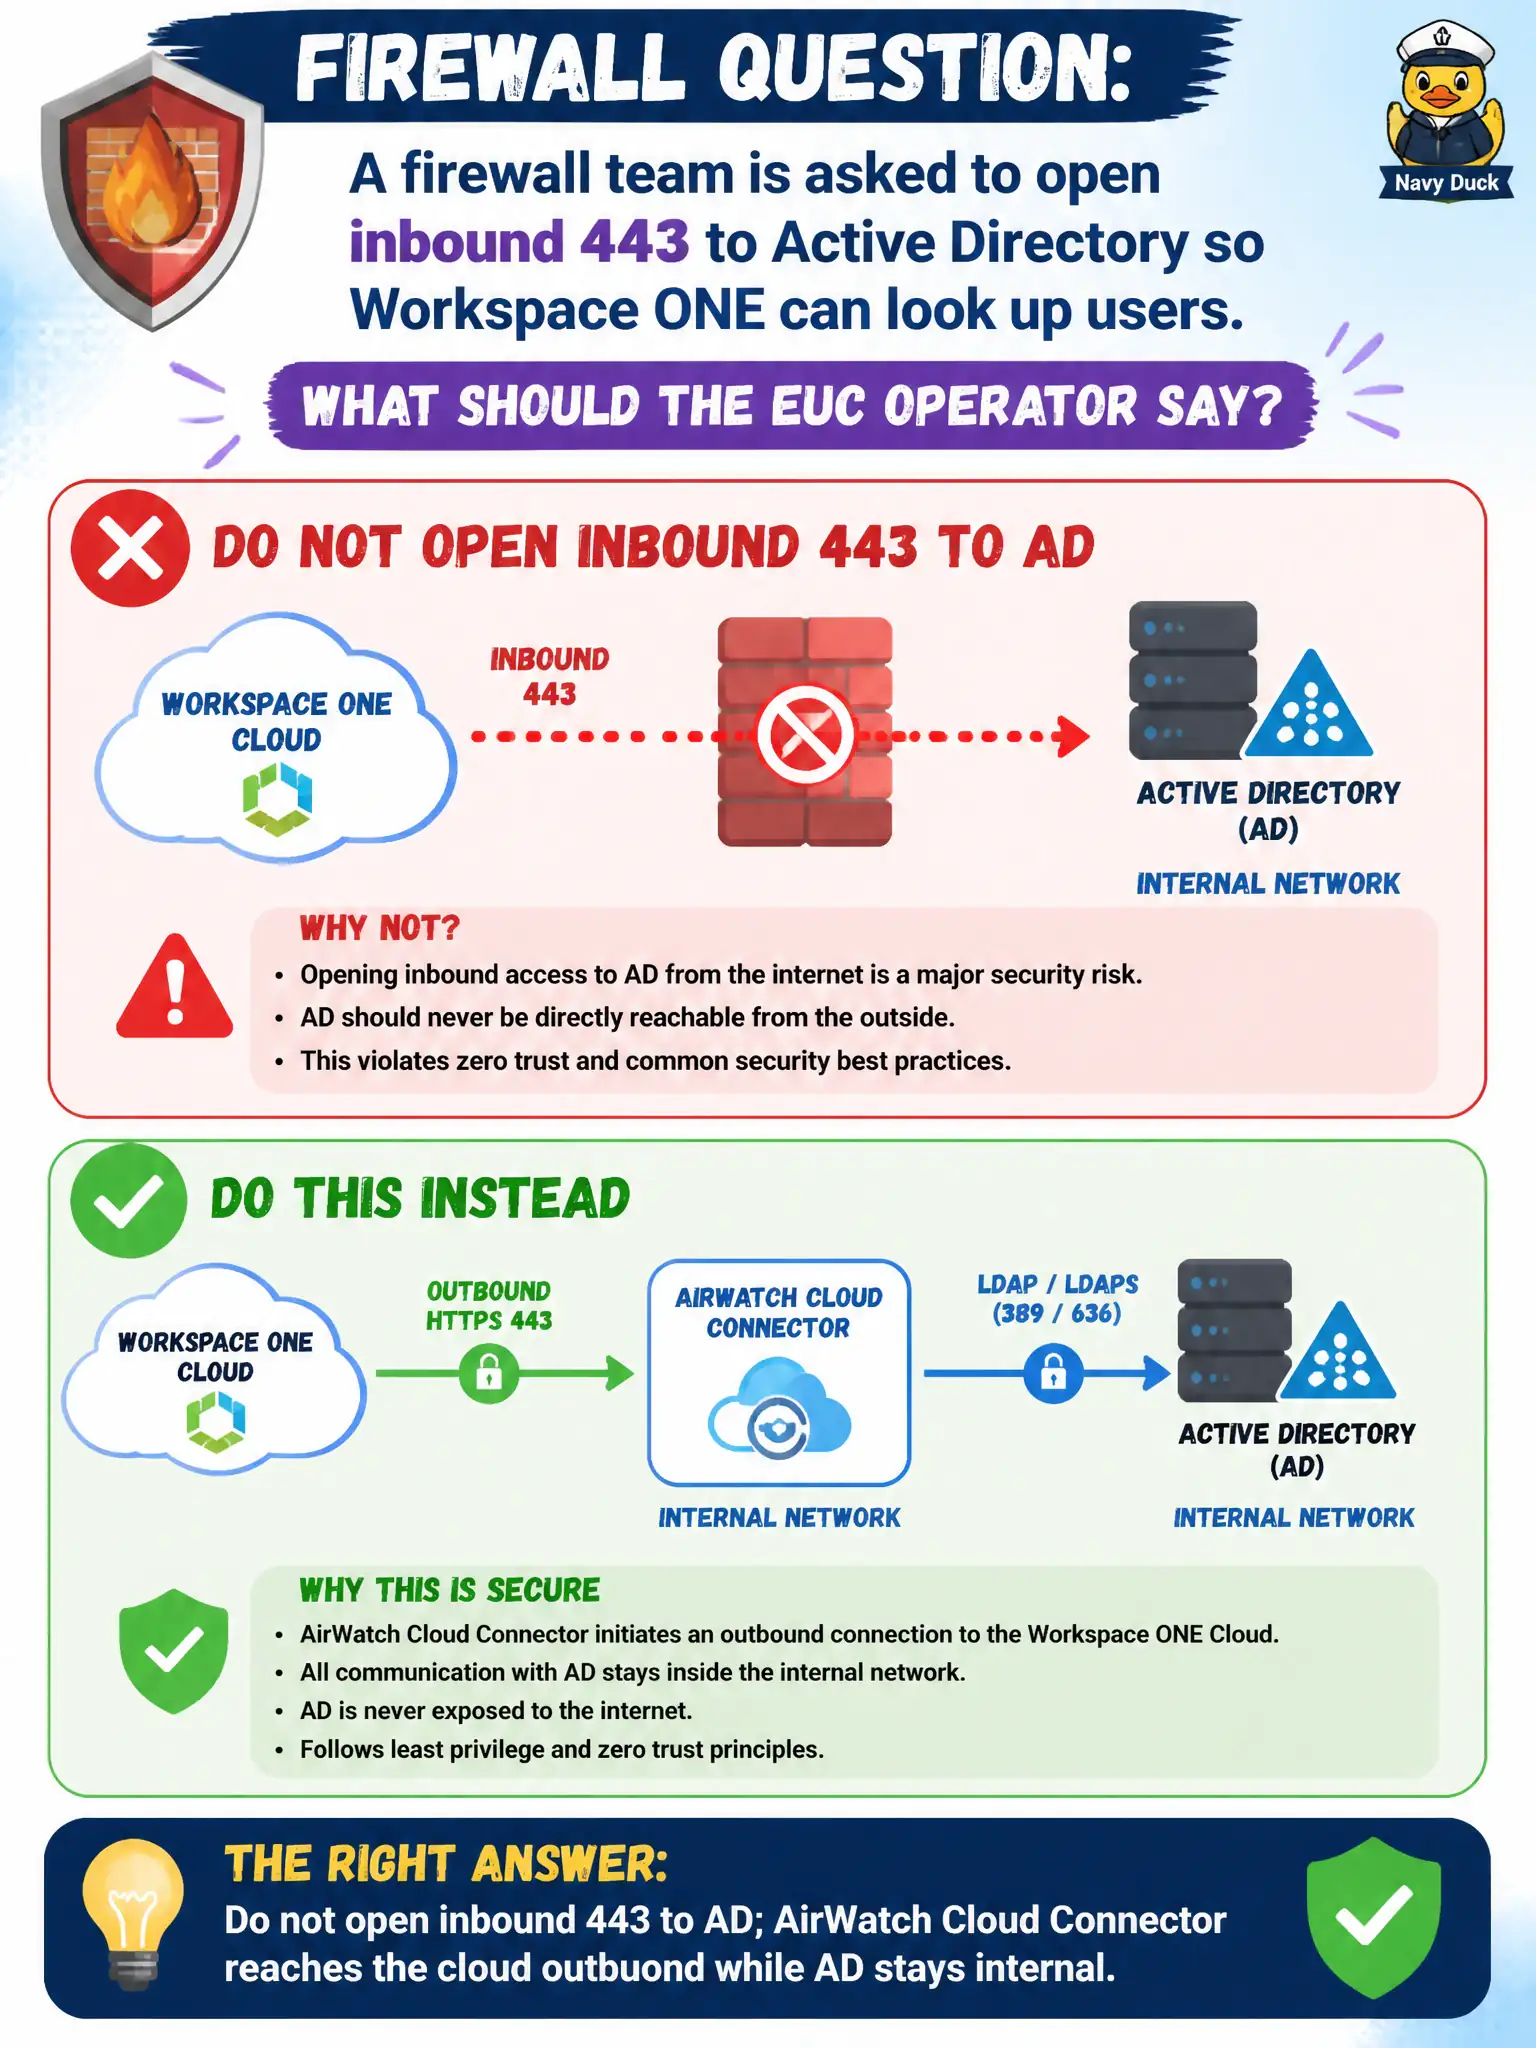
A firewall team is asked to open inbound 443 to Active Directory so Workspace ONE can look up users. What should the EUC operator say?
Select an answer to reveal the explanation.
Short Explanation
Do not cut a new street from the internet into the AD vault. The courier is Cloud Connector walking outbound; AD stays inside. NSX DFW and Connection Server are not that courier.
Full Explanation
When a firewall team is asked to open inbound 443 to Active Directory so Workspace ONE can look up users, the EUC operator should refuse that path: do not open inbound 443 to AD. AirWatch Cloud Connector reaches SaaS UEM outbound from the civic data center while Active Directory stays on the internal network. That outbound-initiated model is the associate-depth answer for protecting municipal directory servers. Opening inbound 443 from the internet to every domain controller exposes the identity vault and is the wrong design. Putting NSX Distributed Firewall in front of AD and skipping Cloud Connector does not create the SaaS UEM directory integration by itself. Publishing Connection Server as an LDAP proxy for UEM confuses the Horizon broker with the UEM Cloud Connector role. Exam caveat: outbound allow-lists for Cloud Connector hosts are still required; “no inbound to AD” does not mean “no firewall rules at all.” Operational check: review firewall policy for no internet-sourced paths to domain controllers, confirm Cloud Connector outbound URLs or IPs are permitted, sync a test civic OU into SaaS UEM, and re-check that AD listening ports remain unreachable from untrusted networks.