
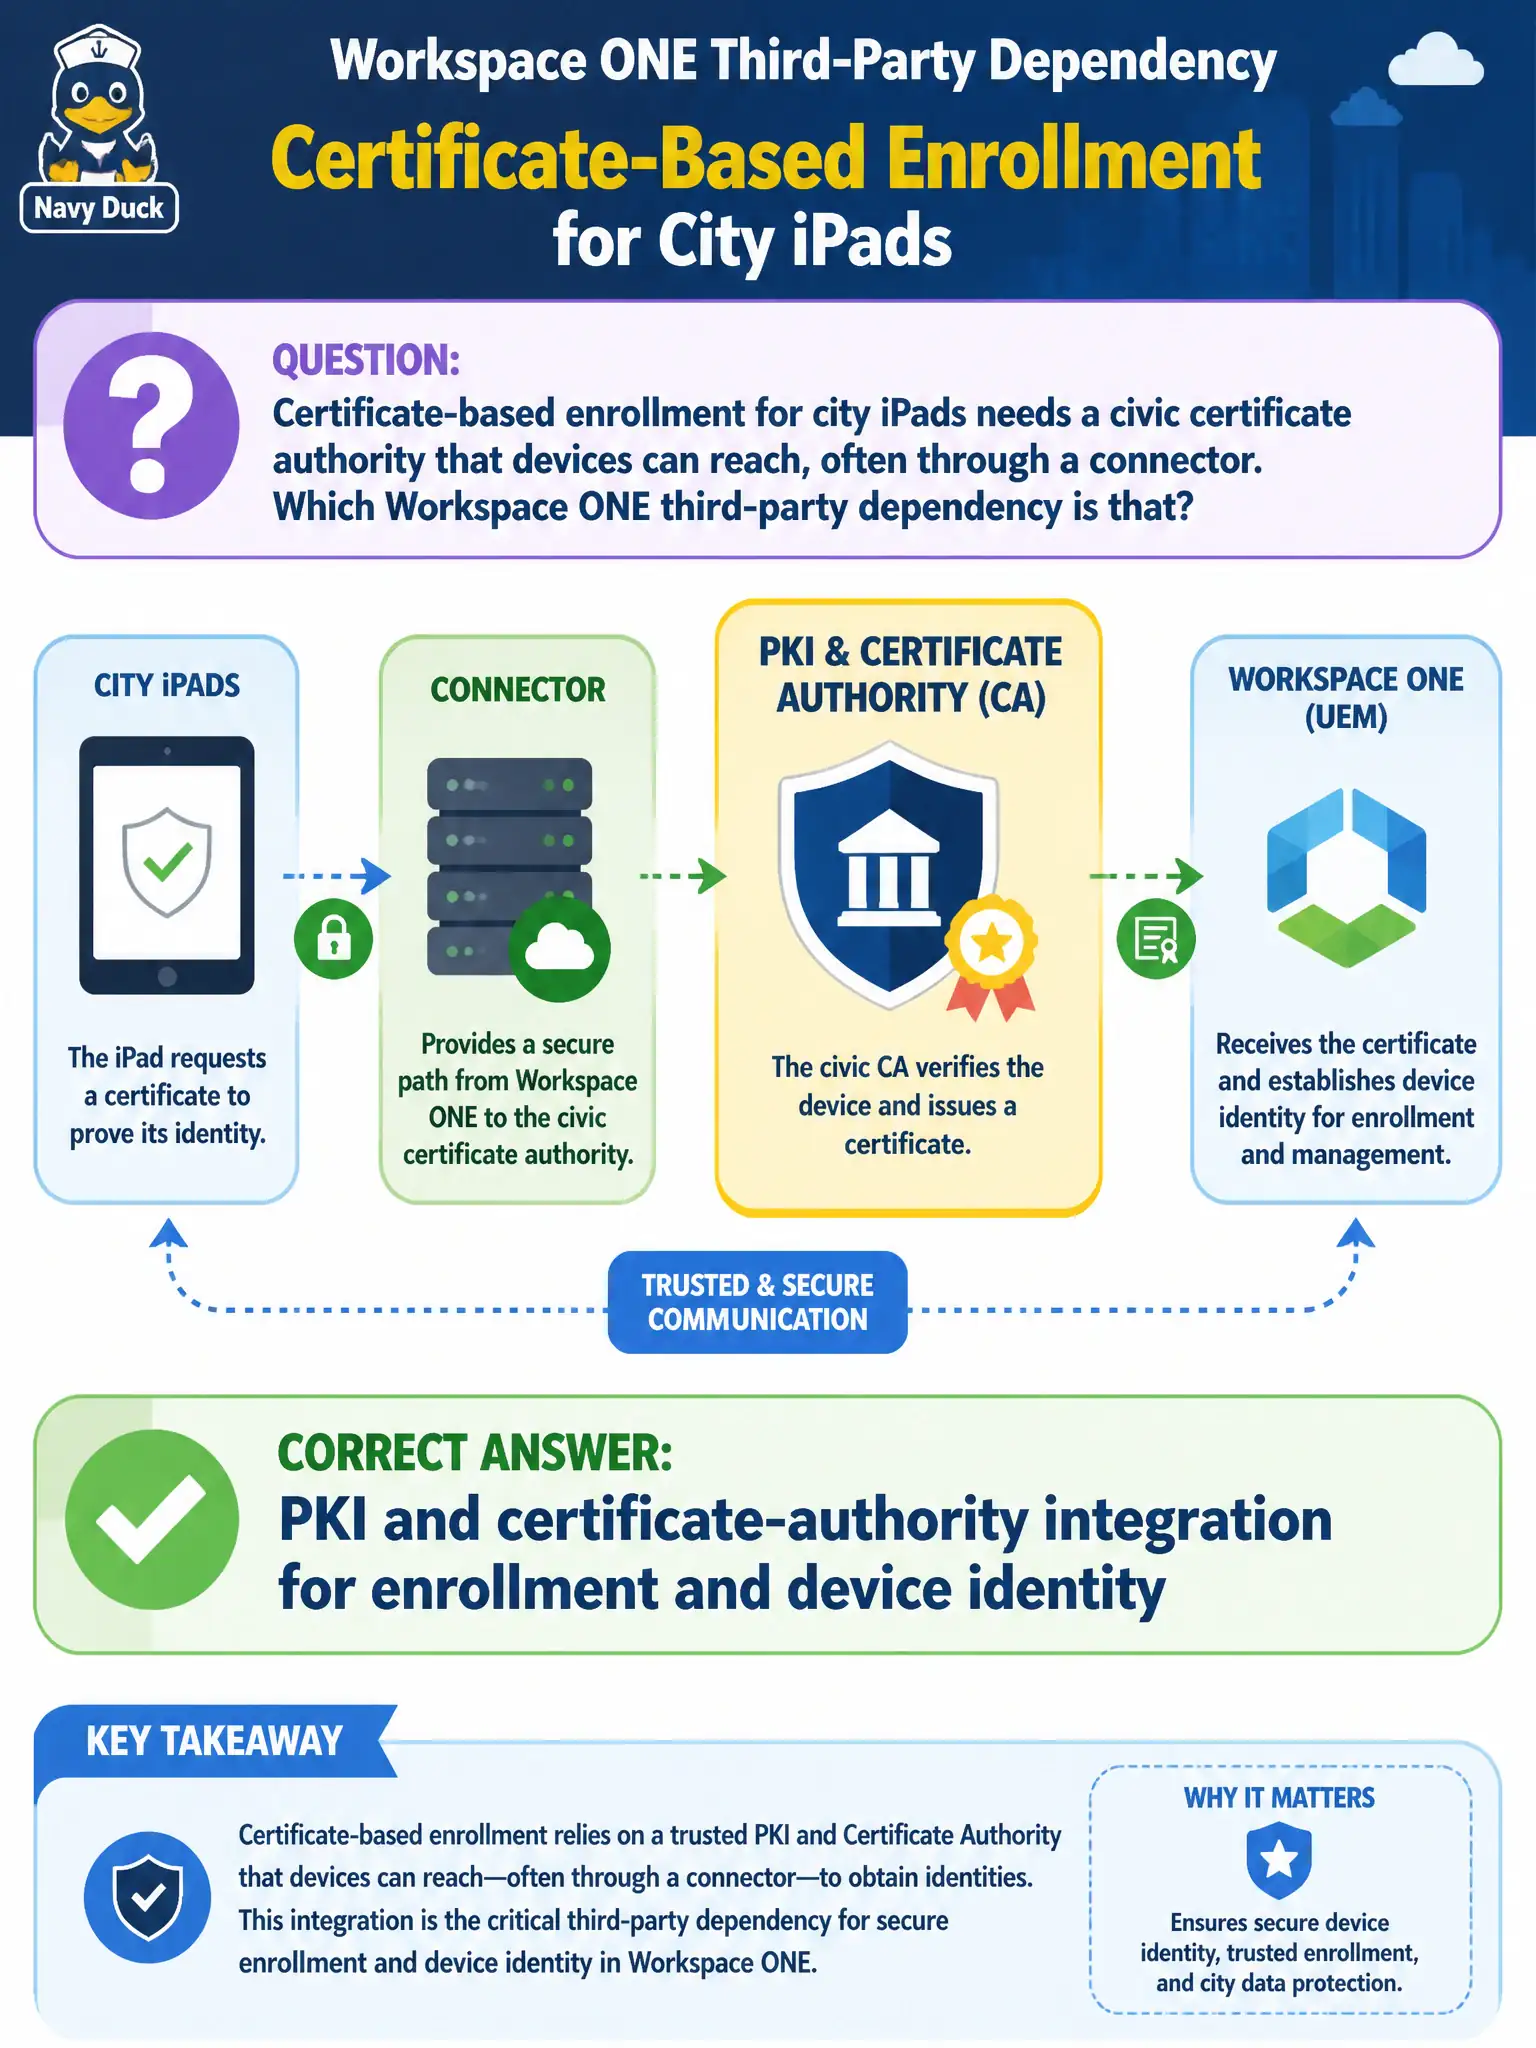
Certificate-based enrollment for city iPads needs a civic certificate authority that devices can reach, often through a connector. Which Workspace ONE third-party dependency is that?
Select an answer to reveal the explanation.
Short Explanation
Those iPads need a city-issued badge, not a Horizon SQL table. PKI and the civic CA (often via connector) are the Workspace ONE dependency for certificate enrollment. App Volumes and DRS live on the VDI/hypervisor side.
Full Explanation
Certificate-based enrollment for city iPads depends on PKI and certificate-authority integration that devices can reach, often through a connector. In municipal EUC terms, treat the endpoint as a window into city systems when the architecture says so, not as the system of record for the files or apps in the stem. Distractor concept: Horizon events SQL Server is not the enrollment CA dependency. Distractor concept: App Volumes writable volumes are unrelated to iPad cert enrollment. Distractor concept: vSphere DRS affinity rules are not the Workspace ONE cert dependency. Exam caveat: Cert enrollment → PKI/CA reachability (often via connector), not SQL/App Volumes/DRS. Operational check: Confirm devices can obtain/renew civic certs for enrollment and that connector/CA paths are monitored. Record the chosen control and the rejected failure modes in the civic change ticket or runbook so on-call staff and auditors share the same rationale after the next maintenance window. Re-validate after personnel or image changes that the same control still meets the city's continuity, security, and support expectations for this service. Helpdesk coaching tip aligned to the conversational brief: Those iPads need a city-issued badge, not a Horizon SQL table. PKI and the civic CA (often via connector) are the Workspace ONE dependency for certificate enrollment. App Volumes and DRS live on the VDI/hypervisor side.