
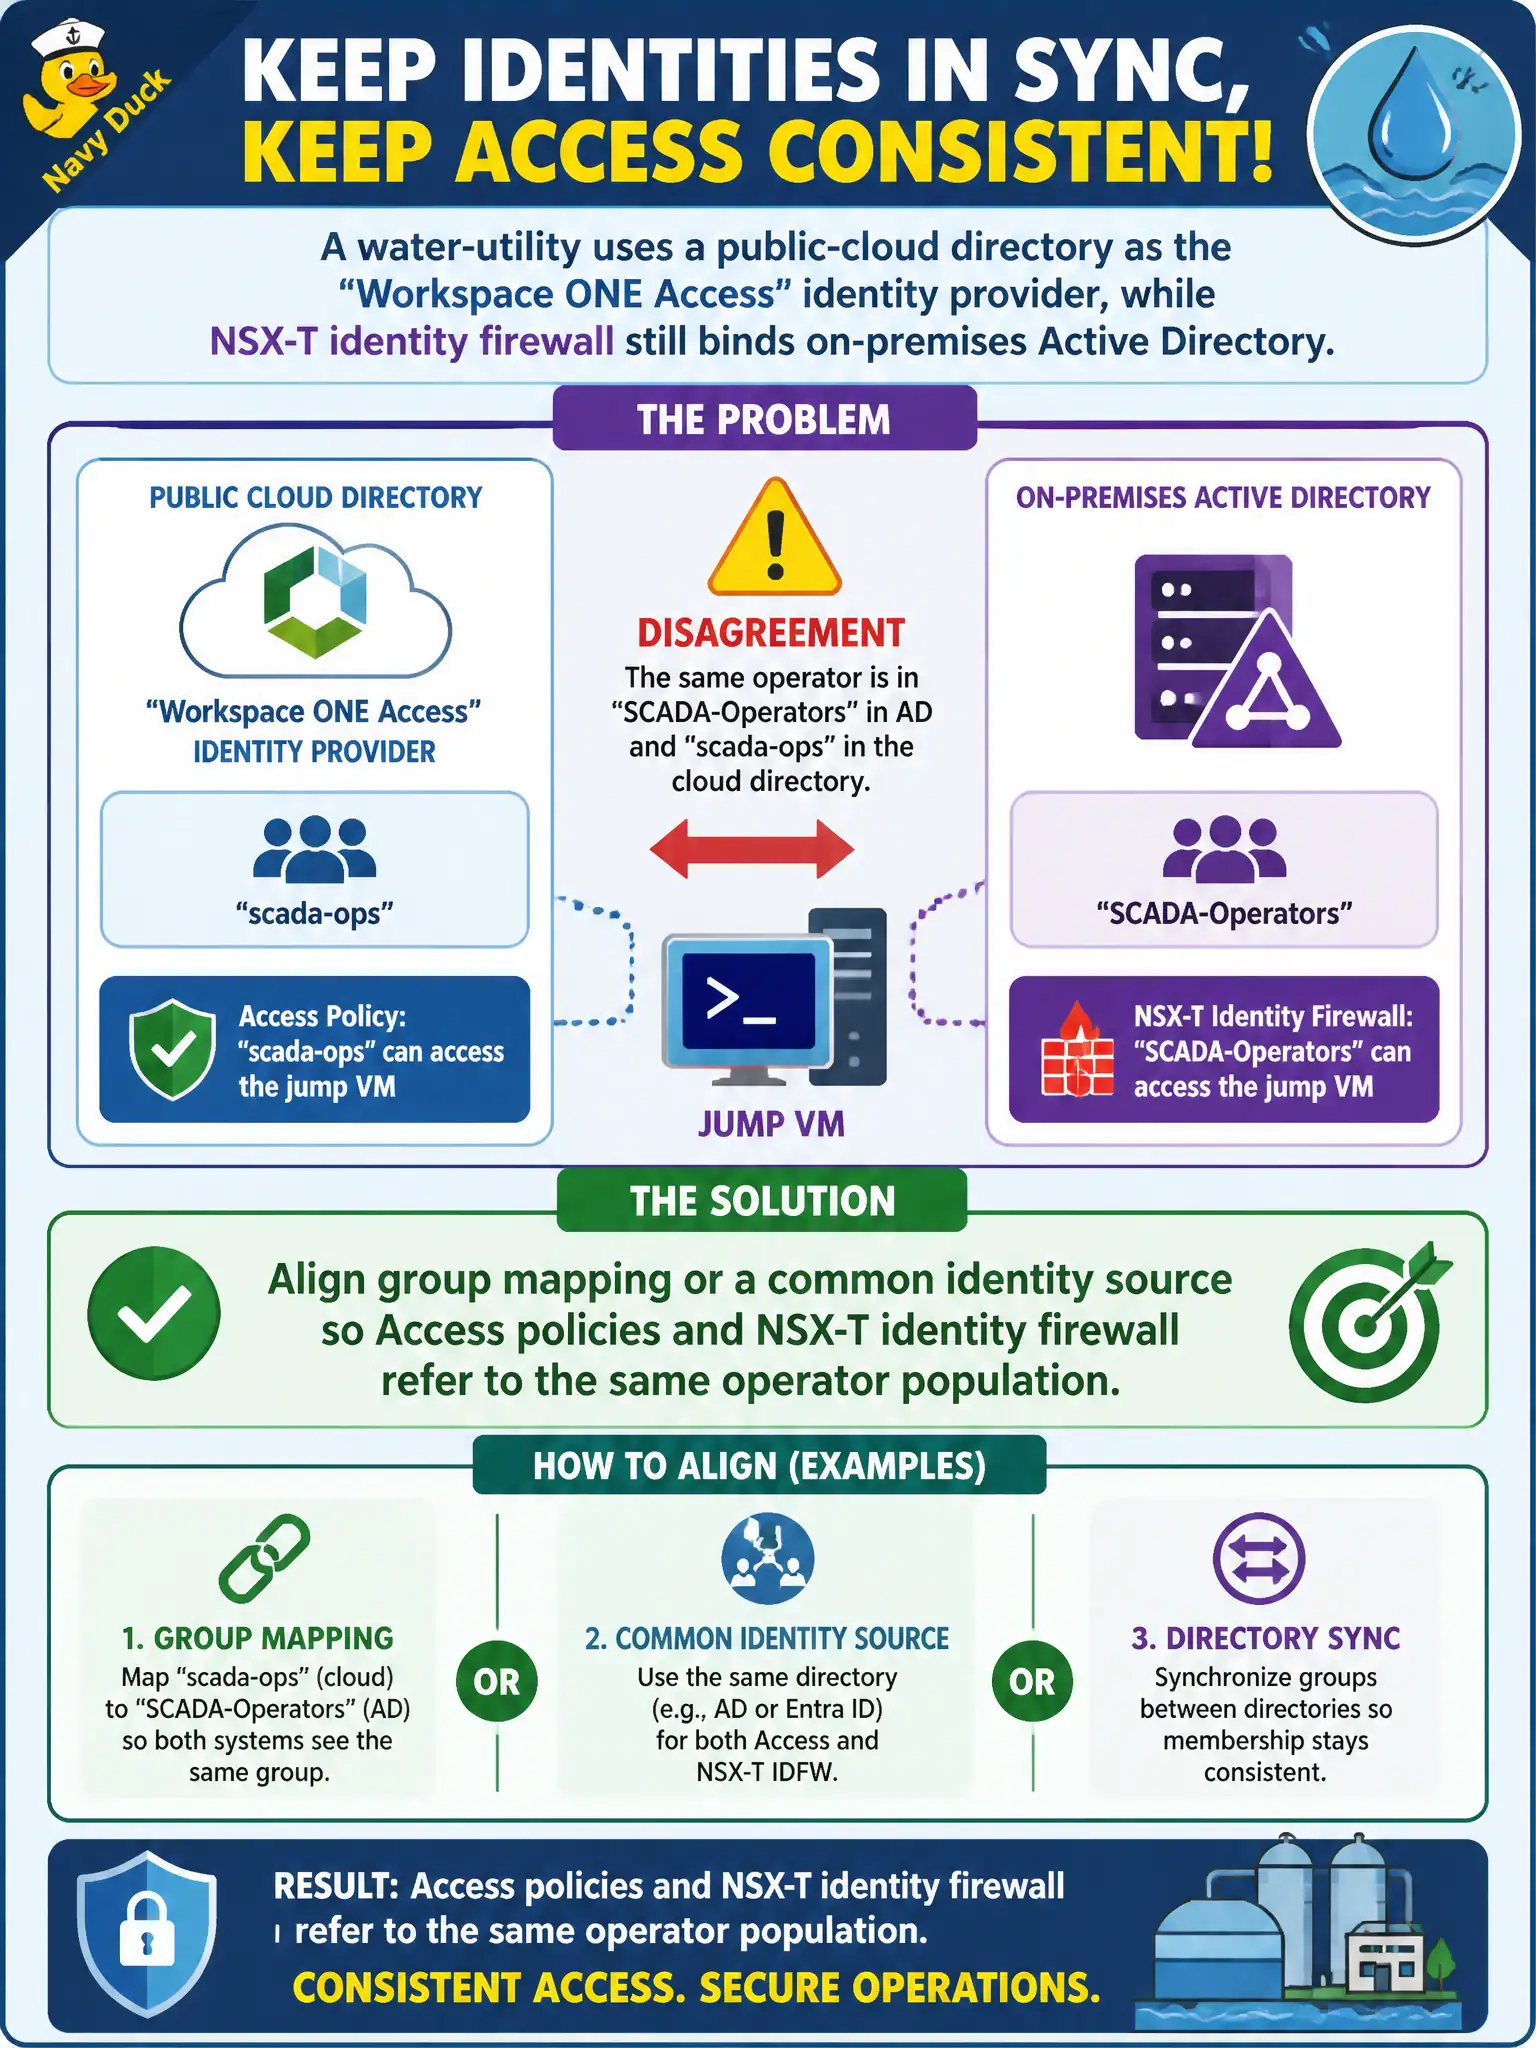
A water-utility uses a public-cloud directory as the Workspace ONE Access identity provider, while NSX-T identity firewall still binds on-premises Active Directory. The same operator is in SCADA-Operators in AD and scada-ops in the cloud directory, so Access and IDFW disagree on who may reach a jump VM. What should the administrator do?
Select an answer to reveal the explanation.
Short Explanation
Two directories with two spellings of the same crew is a split nametag. Access and IDFW will never agree until someone maps those groups or uses one source of truth. Don't pick a winner or expect Geneve to merge identity.
Full Explanation
When a water-utility uses a public-cloud directory as the Workspace ONE Access identity provider while NSX-T identity firewall still binds on-premises Active Directory, and the same operator is in SCADA-Operators in AD and scada-ops in the cloud directory so Access and IDFW disagree on who may reach a jump VM, align group mapping or a common identity source so Access policies and NSX-T identity firewall refer to the same operator population. Split directories with divergent group names produce conflicting allow decisions for civic SCADA jump access. Harmonizing identity mapping restores consistent authorization. Disabling identity firewall and relying on Carbon Black Cloud to interpret both directories as one group fails by concept because CBC does not merge Access and IDFW directory groups into one network identity firewall decision. Declaring Access wrong and rewriting only IDFW, because on-premises AD is always authoritative for SaaS, fails by concept because cloud-directory Access and on-prem IDFW both matter; unilaterally ignoring Access breaks the IdP design. Stretching on-premises NSX-T overlay into the public-cloud directory using Geneve so group names merge automatically fails by concept because Geneve overlay stretch does not merge cloud directory and AD group namespaces. Exam caveat: hybrid IdP plus on-prem IDFW requires explicit group alignment—do not disable IDFW for CBC, ignore Access, or expect Geneve to merge directories. Operational check: map SCADA-Operators and scada-ops to one authorized population, test Access and IDFW decisions for the jump VM, document the identity source of truth, and update the water-utility hybrid identity matrix for municipal OT access control.