
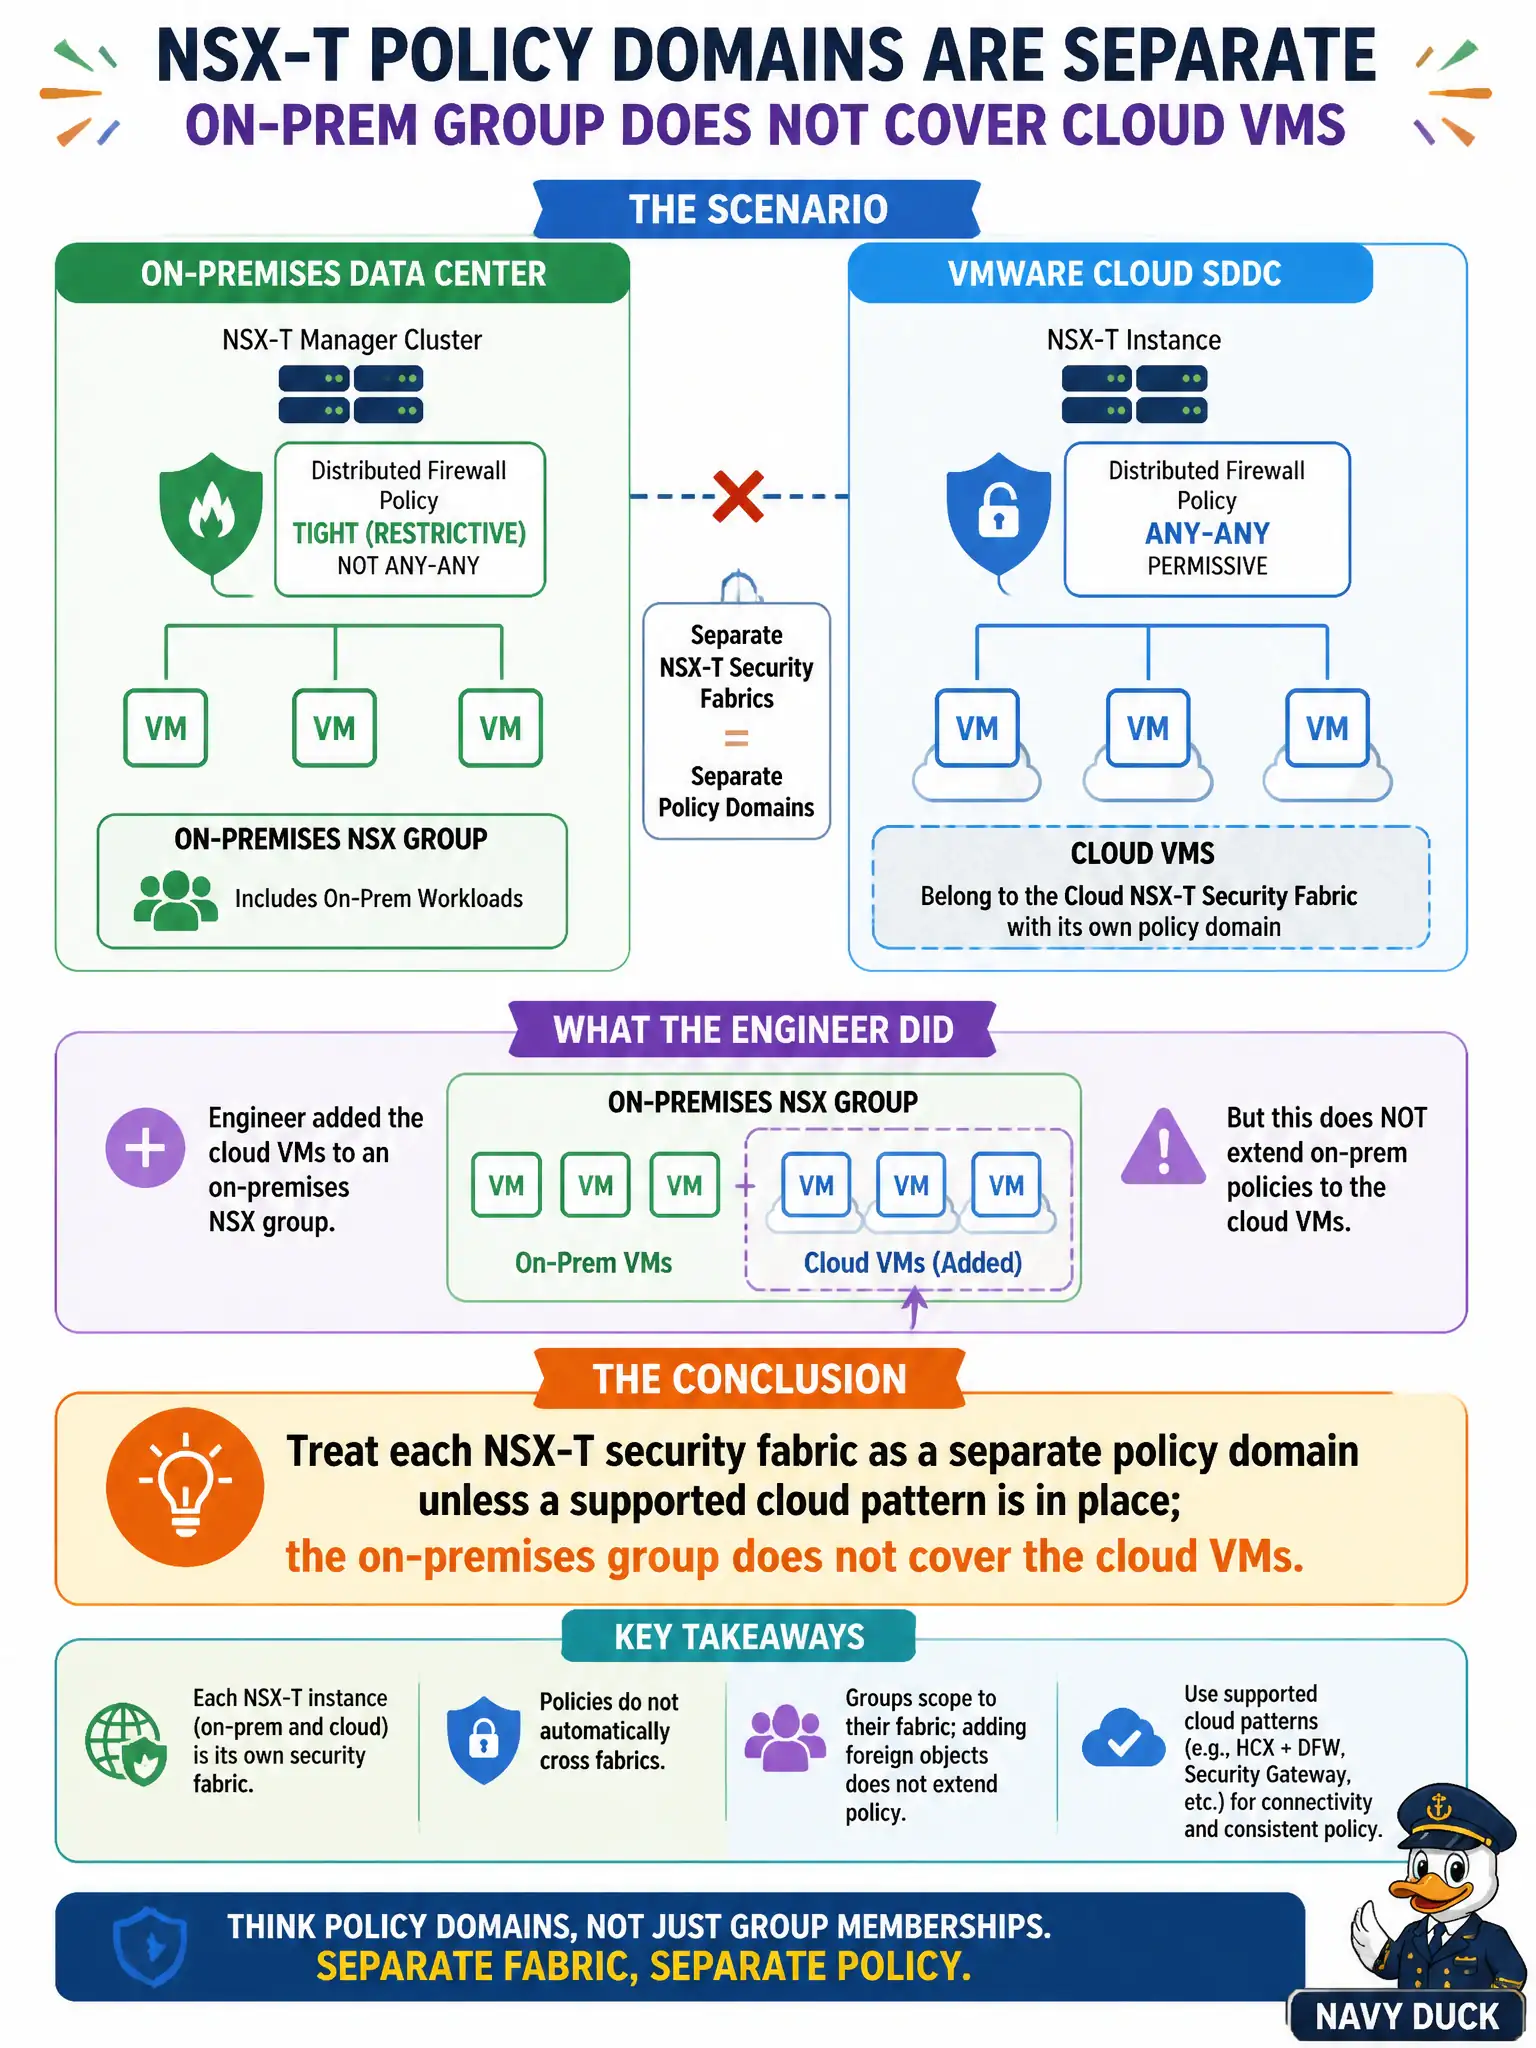
A county on-premises NSX-T Manager cluster has tight Distributed Firewall policy. Workloads in a VMware Cloud SDDC with its own NSX-T instance remain any-any. An engineer added those cloud VMs to an on-premises NSX group. What should the administrator conclude?
Select an answer to reveal the explanation.
Short Explanation
Each NSX Manager cluster is its own security city. Dropping a cloud VM name into an on-prem group does not teleport DFW across the WAN. Fix or duplicate policy in the cloud fabric — don't assume one on-prem group covers VMC.
Full Explanation
When a county on-premises NSX-T Manager cluster has tight Distributed Firewall policy but workloads in a VMware Cloud SDDC with its own NSX-T instance remain any-any, and an engineer added those cloud VMs to an on-premises NSX group, conclude that each NSX-T security fabric is a separate policy domain unless a supported cloud pattern is in place; the on-premises group does not cover the cloud VMs. On-premises groups do not magically stretch DFW into another SDDC's NSX instance. Civic cloud workloads need policy in their own fabric or a supported multi-cloud pattern. On-premises groups automatically stretch Distributed Firewall into every cloud SDDC that uses Geneve fails by concept because Geneve encapsulation does not auto-stretch on-prem DFW policy domains into remote SDDC NSX instances. Identity firewall on the on-premises Manager will enforce the same rules in the cloud SDDC after AD sync fails by concept because on-prem IDFW does not enforce in a separate cloud NSX-T fabric via AD sync alone. Carbon Black Cloud sensor groups on the on-premises org will push NSX Distributed Firewall into the cloud SDDC fails by concept because CBC groups do not push NSX DFW policy into a remote SDDC. Exam caveat: separate NSX-T fabrics are separate policy domains—on-prem groups, IDFW, or CBC do not silently cover cloud SDDC any-any. Operational check: implement equivalent DFW in the cloud SDDC or a supported federation/cloud pattern, remove the false assumption that on-prem groups cover cloud VMs, and update the county multi-cloud security architecture for municipal hybrid governance.