
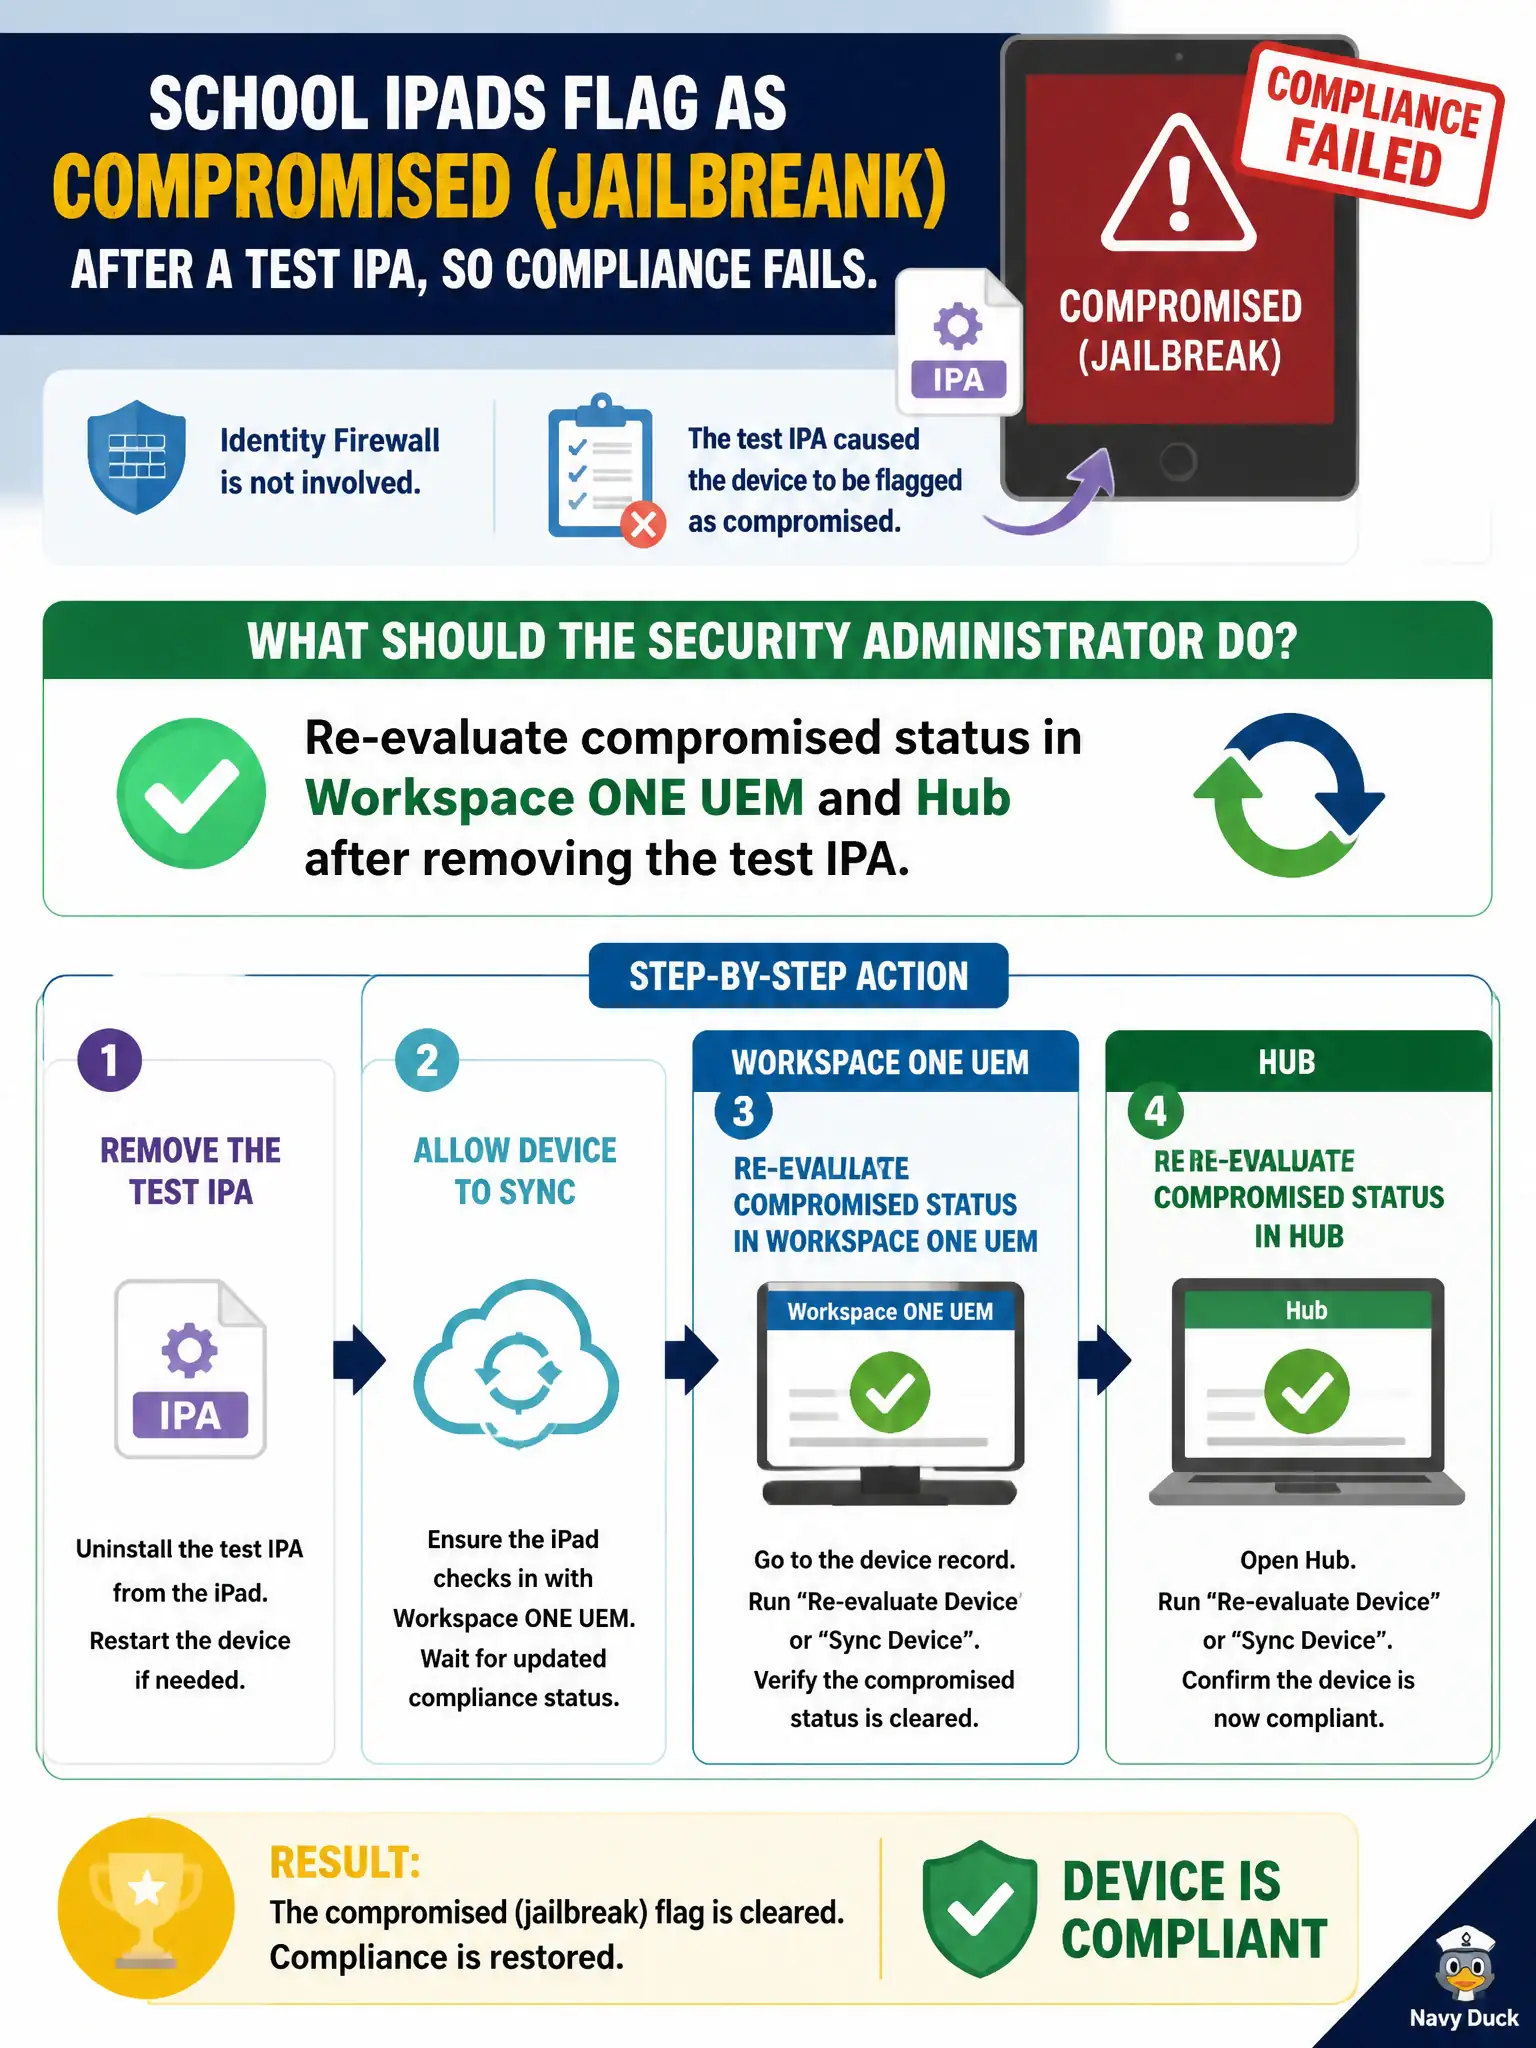
School iPads flag as compromised (jailbreak) after a test IPA, so compliance fails. Identity Firewall is not involved. What should the security administrator do?
Select an answer to reveal the explanation.
Short Explanation
Hub yelled jailbreak after a test IPA, not because NSX saw a user. Pull the test package and re-run the compromised check in Workspace ONE UEM.
Full Explanation
When school iPads flag as compromised (jailbreak) after a test IPA so compliance fails and Identity Firewall is not involved, re-evaluate compromised status in Workspace ONE UEM and Hub after removing the test IPA. Jailbreak/compromise detection can stick after lab testing until UEM/Hub re-evaluate posture; removing the test IPA and refreshing status restores legitimate civic classroom devices. Creating an NSX-T Identity Firewall rule that ignores jailbreak state fails by concept because Identity Firewall is not involved and cannot clear UEM compromised device compliance. Unenrolling every iPad from UEM and switching to Carbon Black Cloud only fails by concept because mass unenrollment destroys MDM control and CBC does not manage iOS compliance the same way. Disabling Intelligent Hub permanently so compromise checks stop fails by concept because that removes the managed client and weakens ongoing posture assessment. Exam caveat: post-lab compromised flags need IPA removal and UEM/Hub re-evaluation—not IDFW exceptions, mass unenrollment, or Hub disable. Operational check: remove the test IPA, trigger compliance re-evaluation in UEM/Hub, confirm compromised status clears, restore app access, and keep lab IPAs off production school profiles for civic education device integrity.