
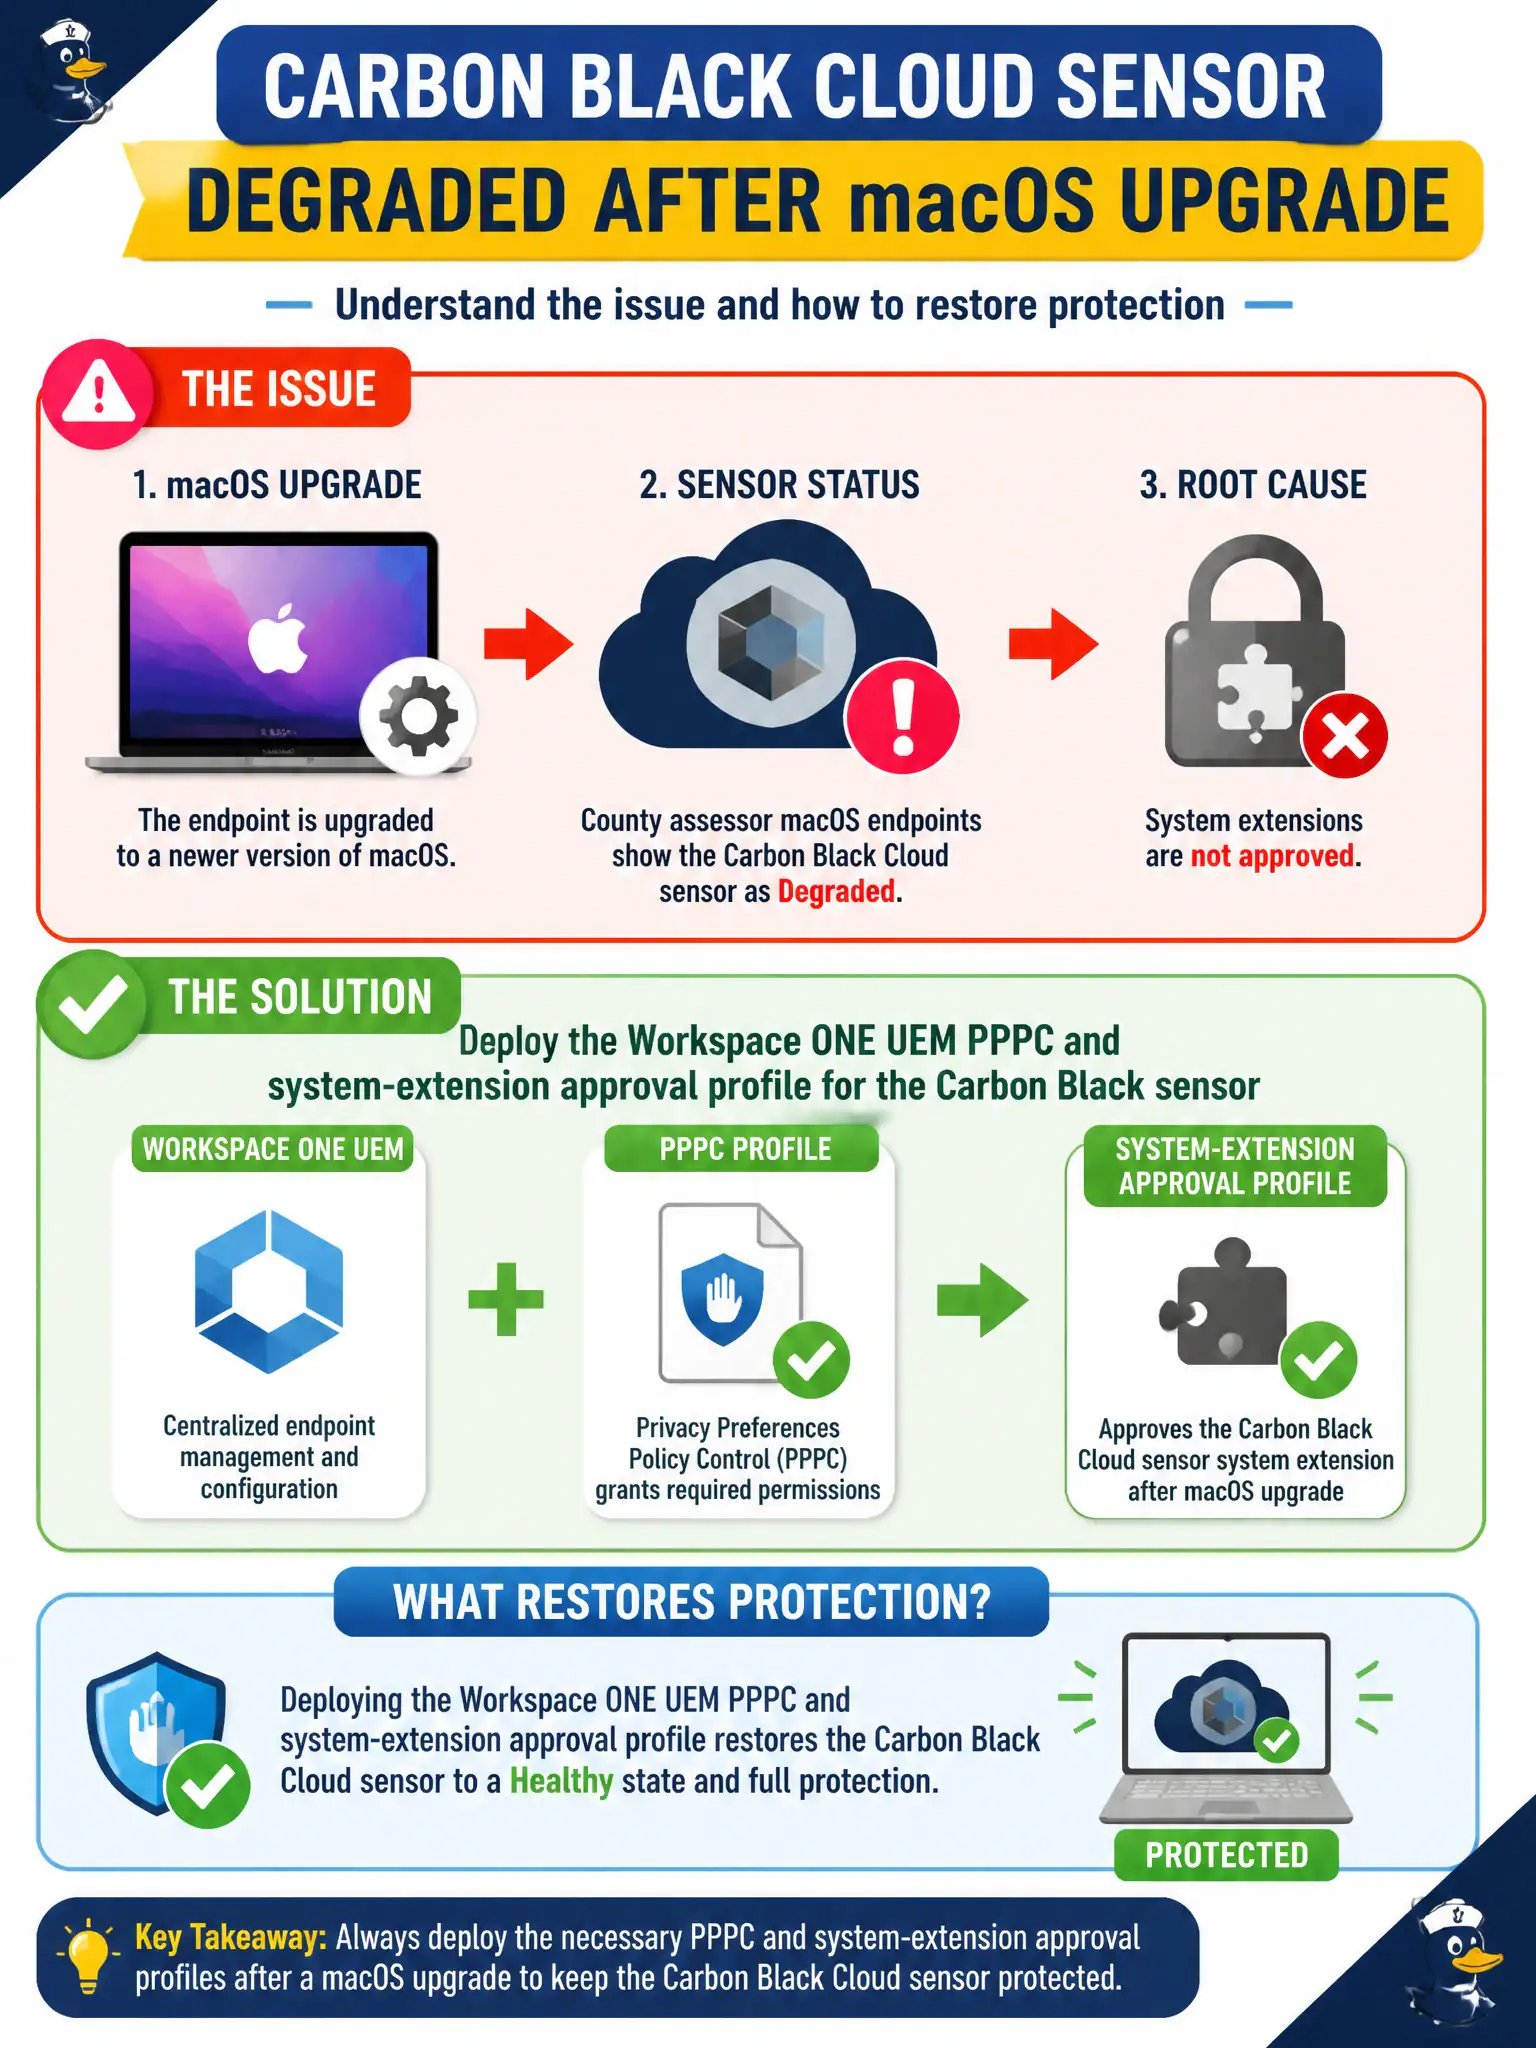
County assessor macOS endpoints show the Carbon Black Cloud sensor as Degraded after a macOS upgrade. System extensions are not approved. What restores protection?
Select an answer to reveal the explanation.
Short Explanation
A Degraded Mac sensor is usually a missing hall pass from MDM, not a broken NSX fabric. Approve the Carbon Black system extension and PPPC from Workspace ONE UEM so the sensor can load again.
Full Explanation
When county assessor macOS endpoints show the Carbon Black Cloud sensor as Degraded after a macOS upgrade because system extensions are not approved, deploy the Workspace ONE UEM PPPC and system-extension approval profile for the Carbon Black sensor. Modern macOS requires Privacy Preferences Policy Control and system-extension approvals for the sensor to load fully; without them protection degrades after upgrades. UEM profiles restore civic assessor endpoint protection the supported way. Enabling NSX-T Identity Firewall on the Mac VLAN so login events replace the sensor fails by concept because IDFW is network identity firewalling, not a replacement for a degraded CBC macOS sensor. Disabling System Integrity Protection on each Mac so the sensor can load unsigned kernel extensions fails by concept because disabling SIP is unsafe and is not the supported approval path for CBC on modern macOS. Registering each Mac as an NSX-T Guest Introspection service virtual machine fails by concept because Guest Introspection SVMs are datacenter partner VMs, not macOS endpoint sensors. Exam caveat: macOS CBC Degraded after upgrade usually means missing PPPC/system-extension approvals via UEM—not SIP disable, IDFW, or GI SVM registration. Operational check: push PPPC and system-extension approval profiles from UEM, confirm sensors leave Degraded, verify prevention on a pilot assessor Mac, and record the profile baseline in the county macOS hardening standard for civic endpoints.